
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
46 results
iCSeeU preview

iCSeeU

GitHublr-m/icseeu

This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!

binary-exploitationctfdebuggers+9
31 year ago
secbox preview

secbox

GitHubyv1ing/secbox

Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.

binary-exploitationctfdebuggers+9
7 days ago
bba preview

bba

GitHubopenbba0/bba

Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
android-securitybinary-analysisdebuggers+7
286 days ago
gdbfuzz preview
Archived

gdbfuzz

GitHubboschresearch/gdbfuzz

Fuzzing Embedded Systems using Hardware Breakpoints

binary-analysisdebuggerseducation+6
1972 years ago
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
gdb-dashboard preview

gdb-dashboard

GitHubcyrus-and/gdb-dashboard

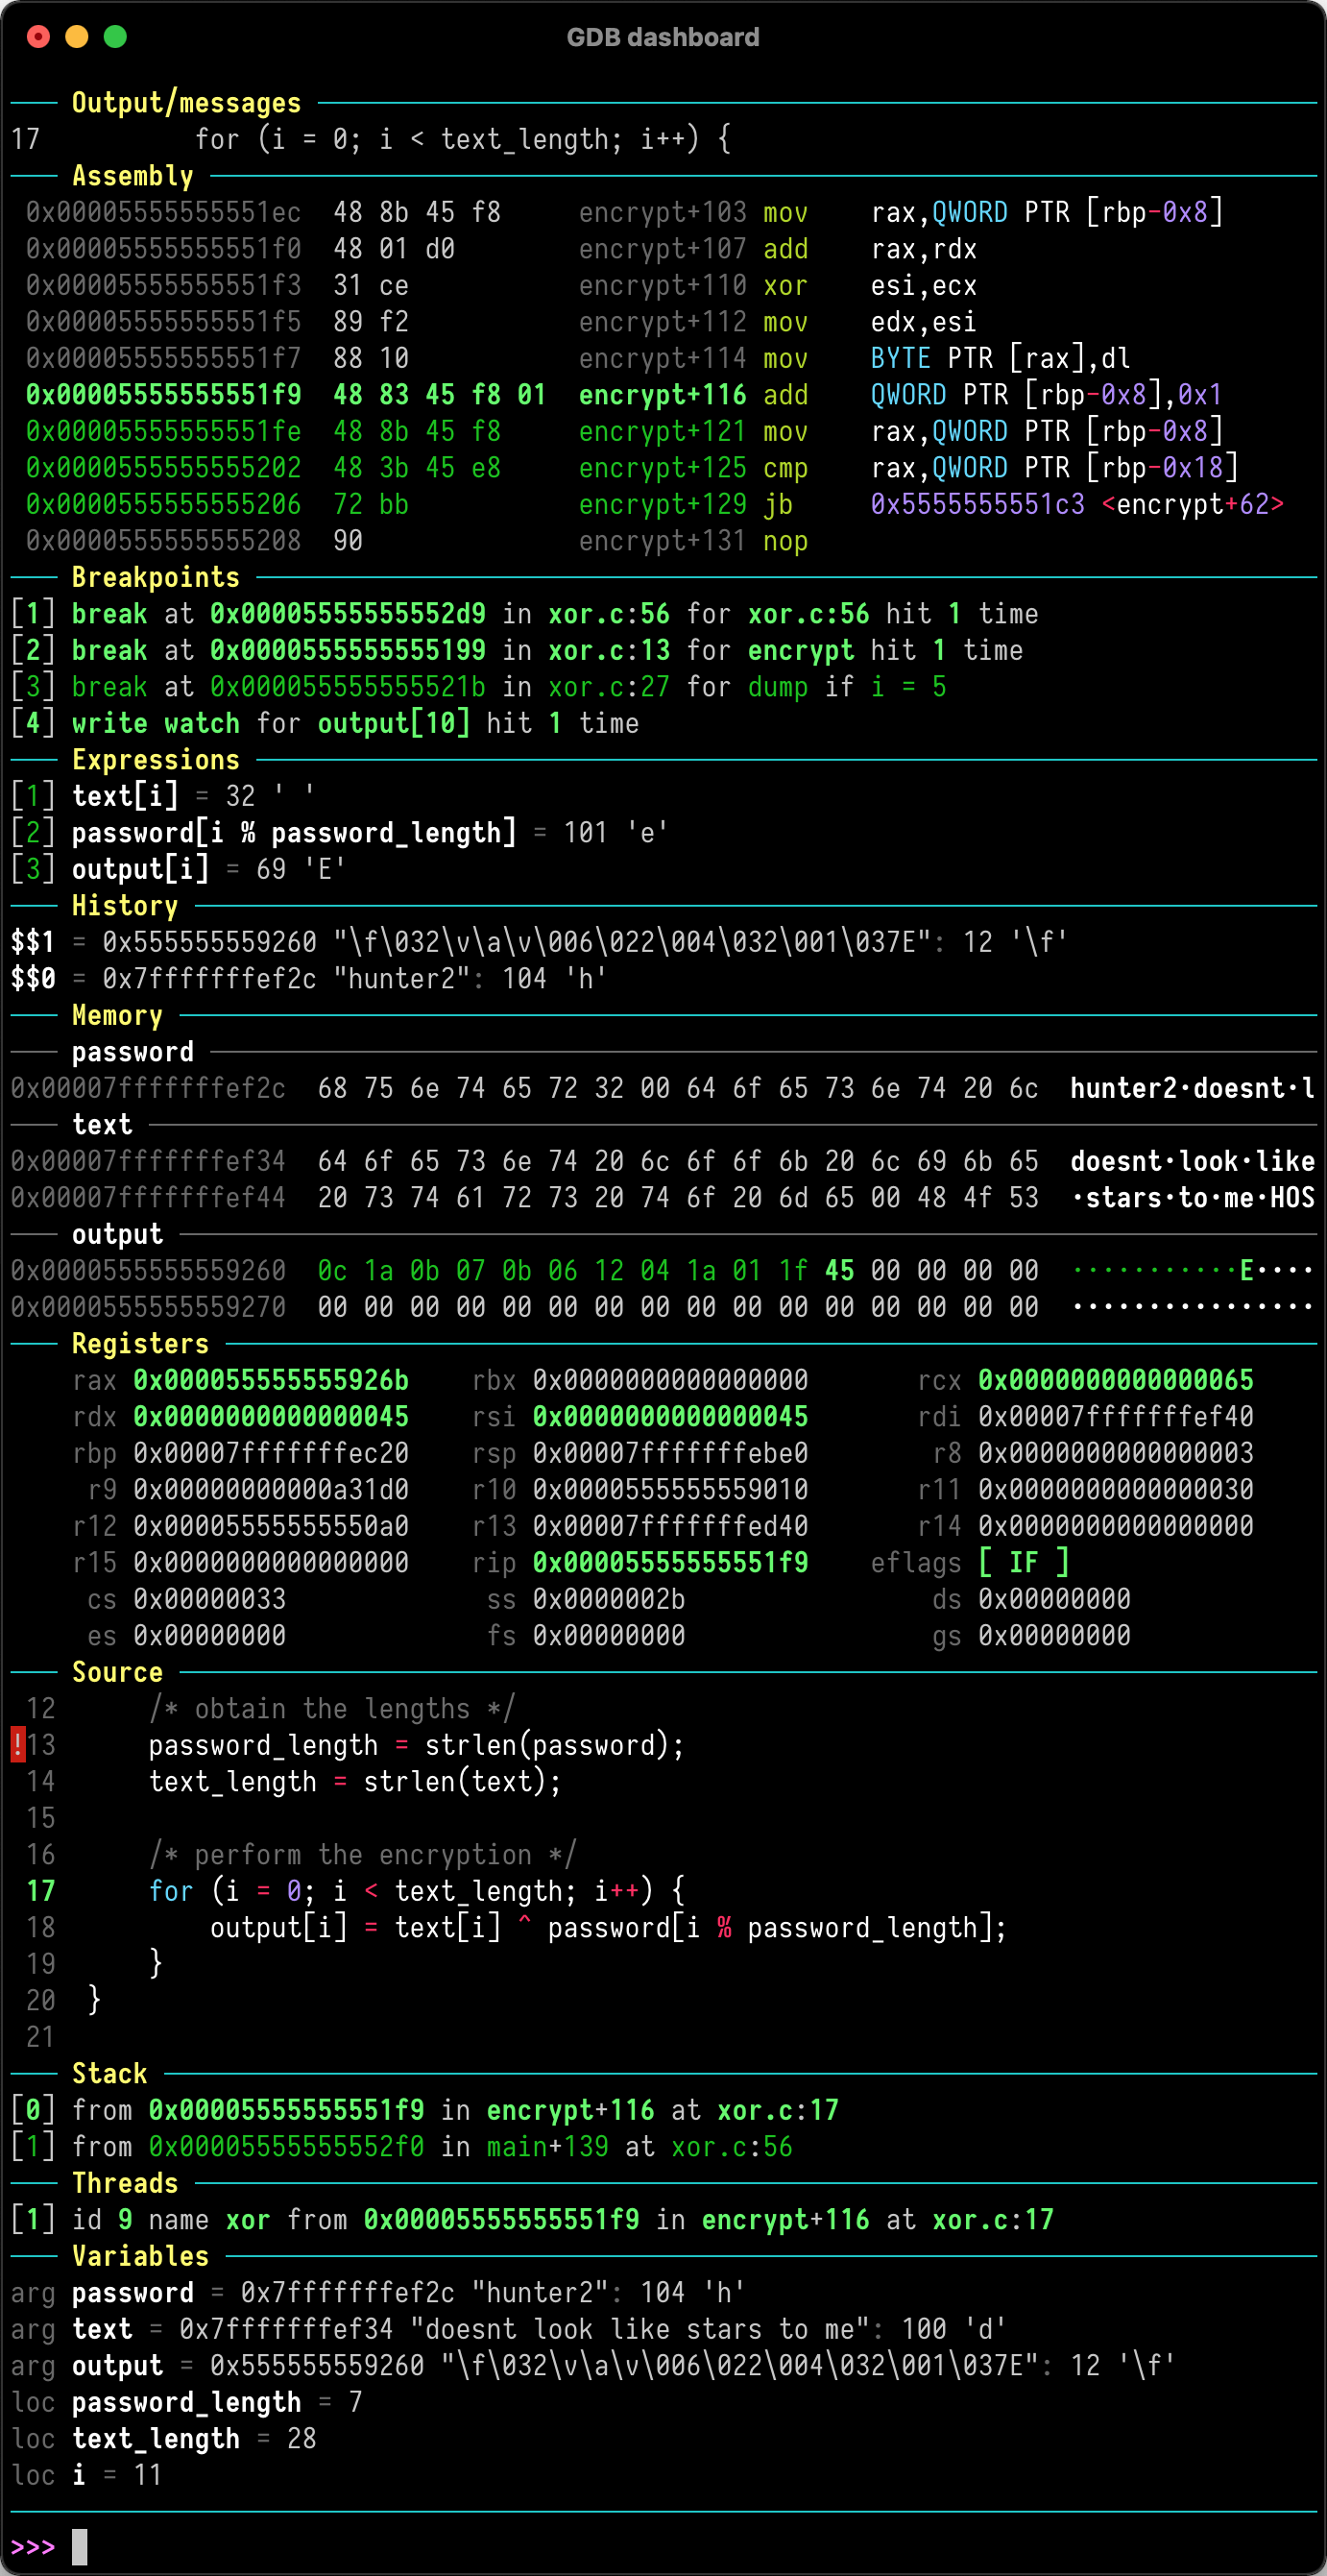
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…

binary-analysisdebuggersreverse-engineering+1
12.3k3 months ago
r2frida preview

r2frida

GitHubnowsecure/r2frida

Radare2 and Frida better together.
android-securitybinary-analysisdebuggers+8
1.5k4 days ago
auto_re preview

auto_re

GitHuba1ext/auto_re

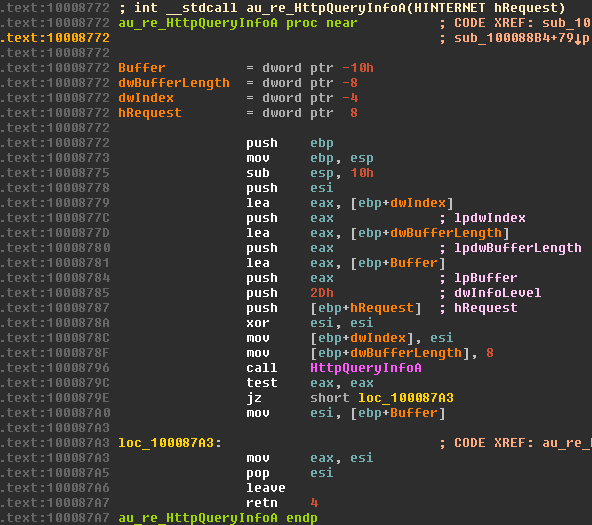
IDA PRO auto-renaming plugin with tagging support
binary-analysisdebuggersreverse-engineering+1
7932 months ago
threadtear preview

threadtear

GitHubloerting/threadtear

Multifunctional java deobfuscation tool suite
binary-analysiscode-analysisdebuggers+3
9845 years ago
ttddbg preview

ttddbg

GitHubairbus-cert/ttddbg

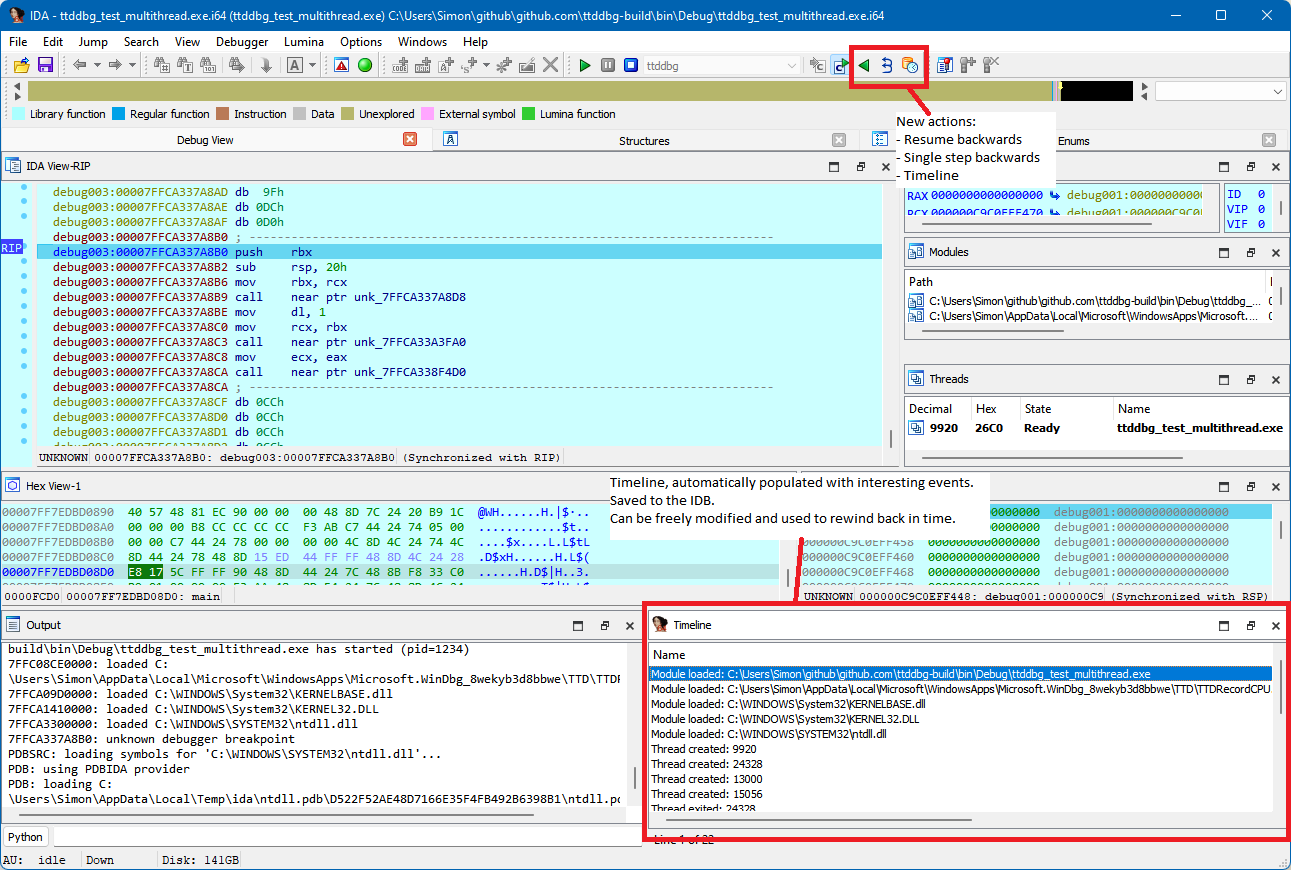
Time Travel Debugging IDA plugin
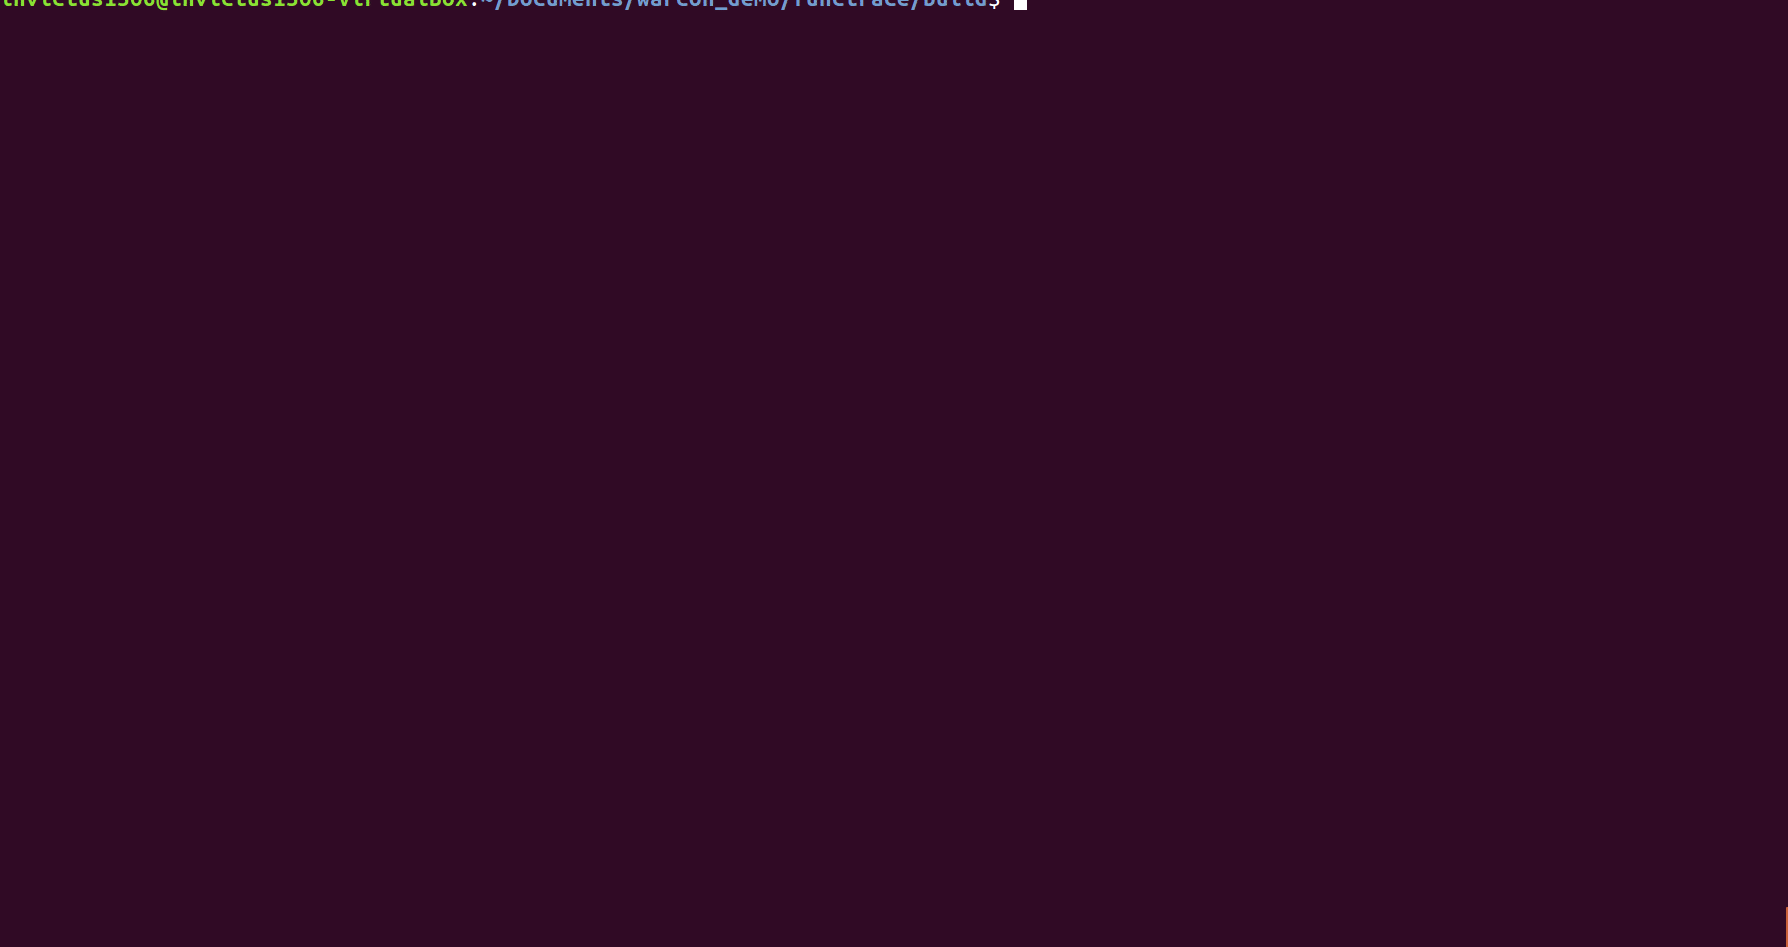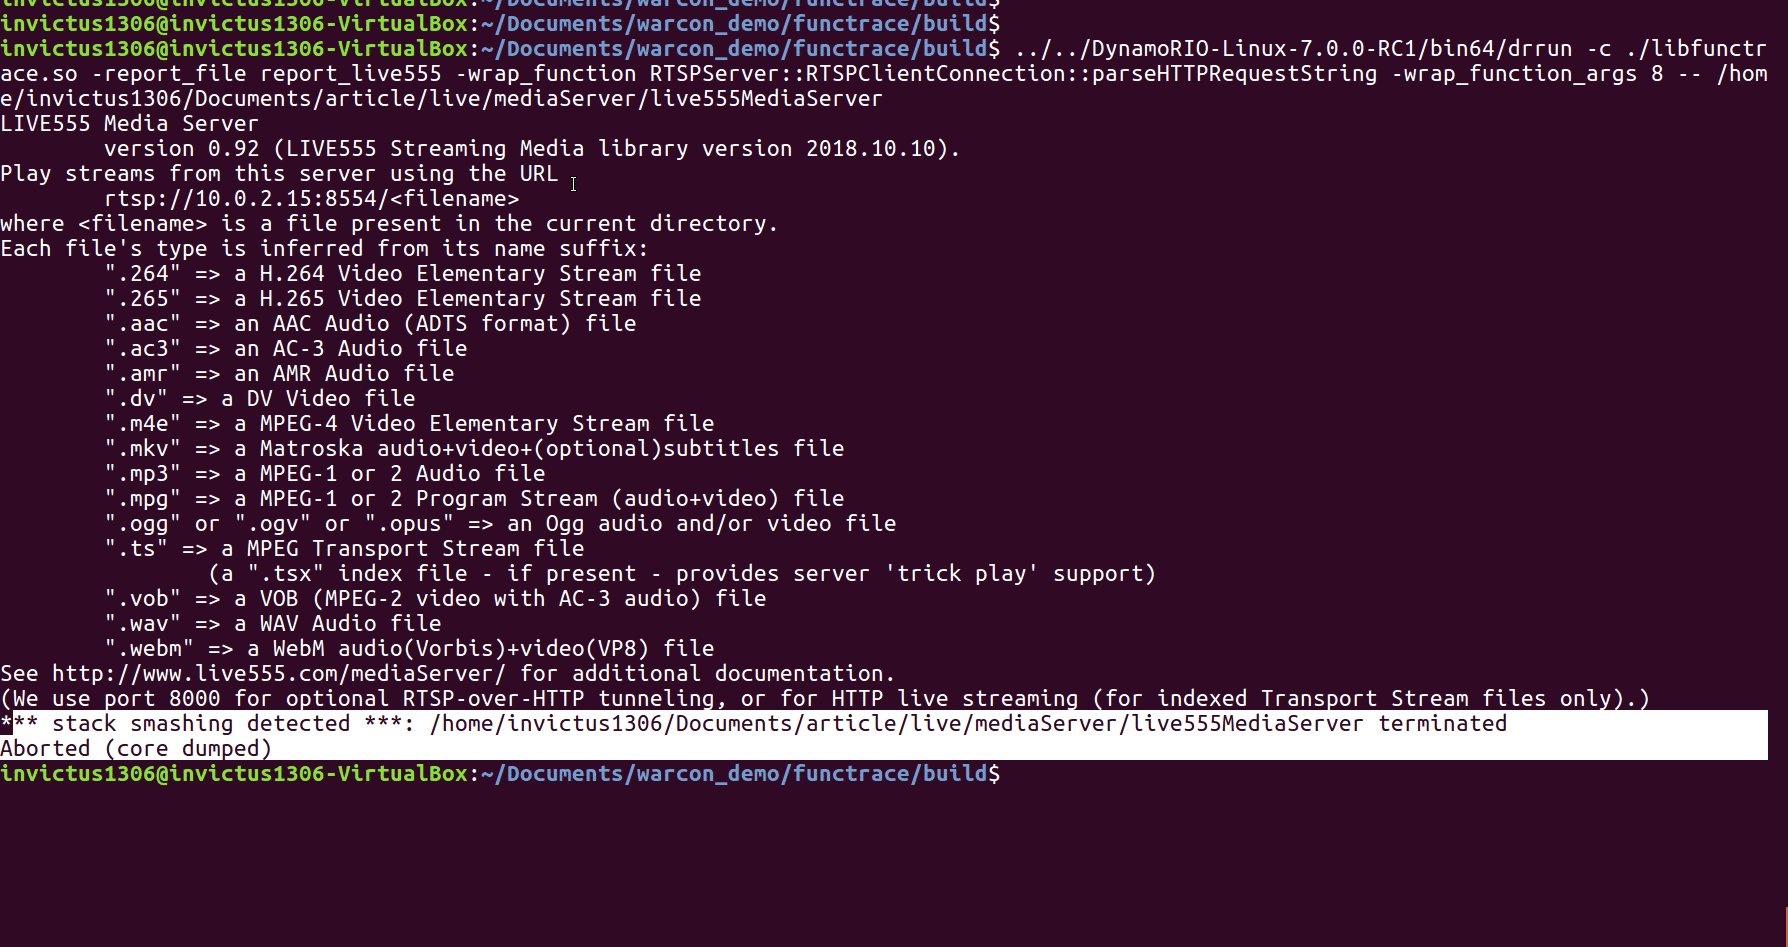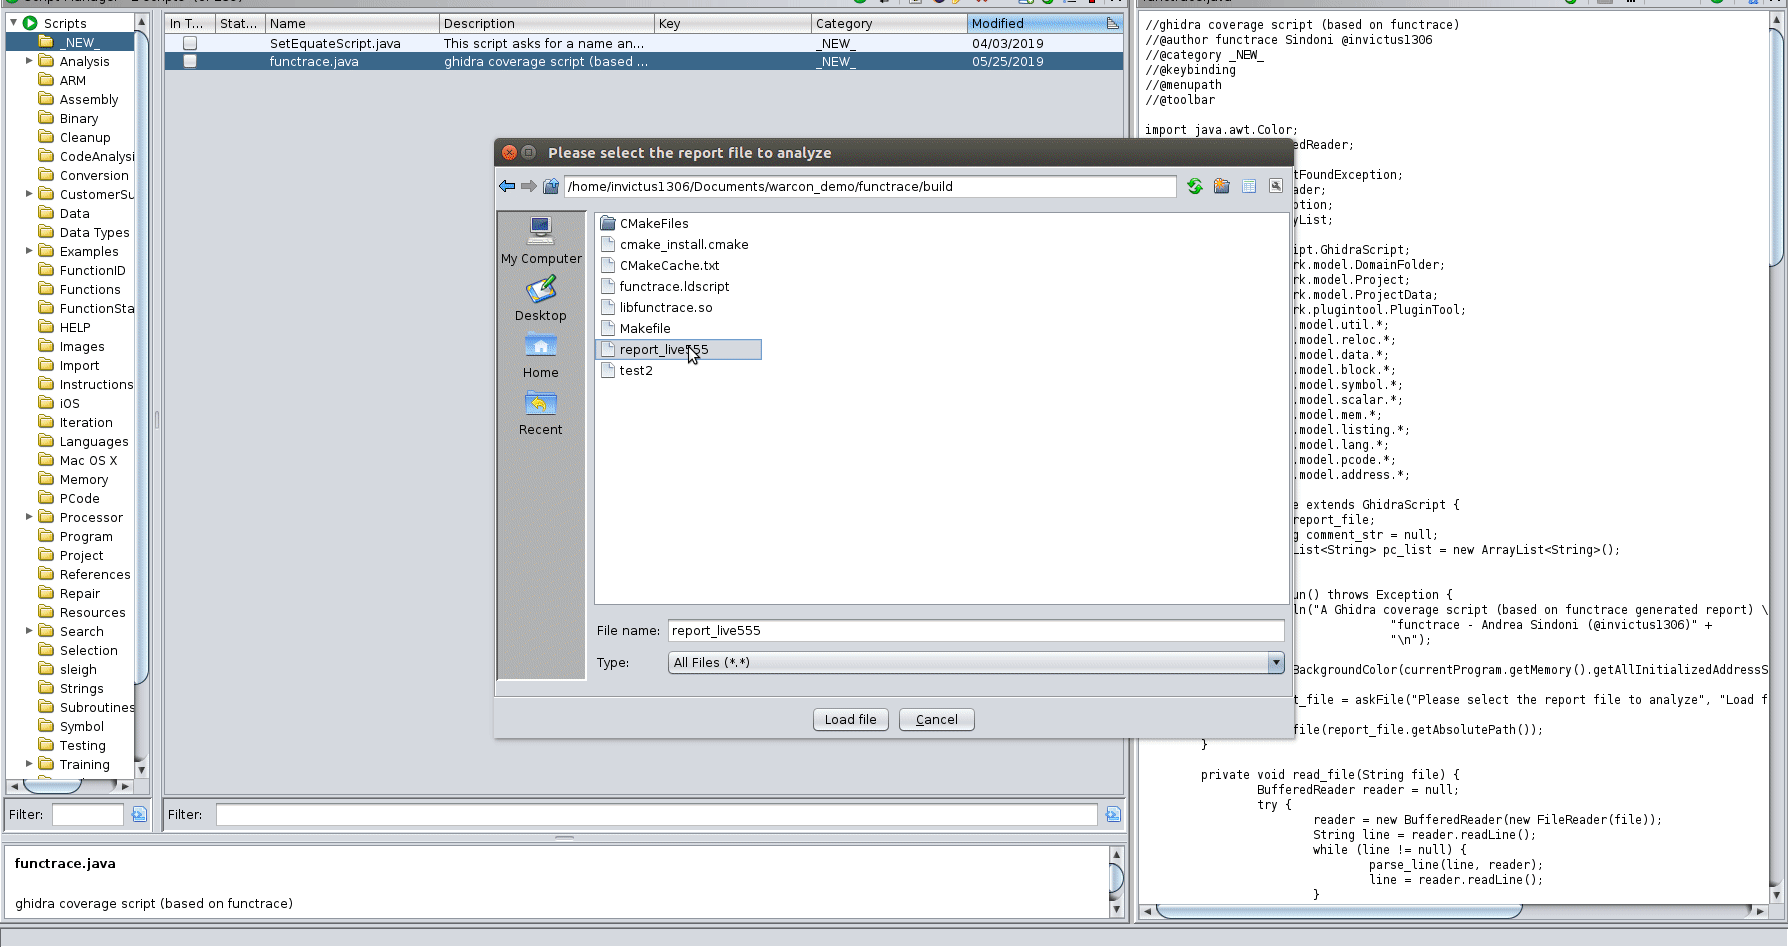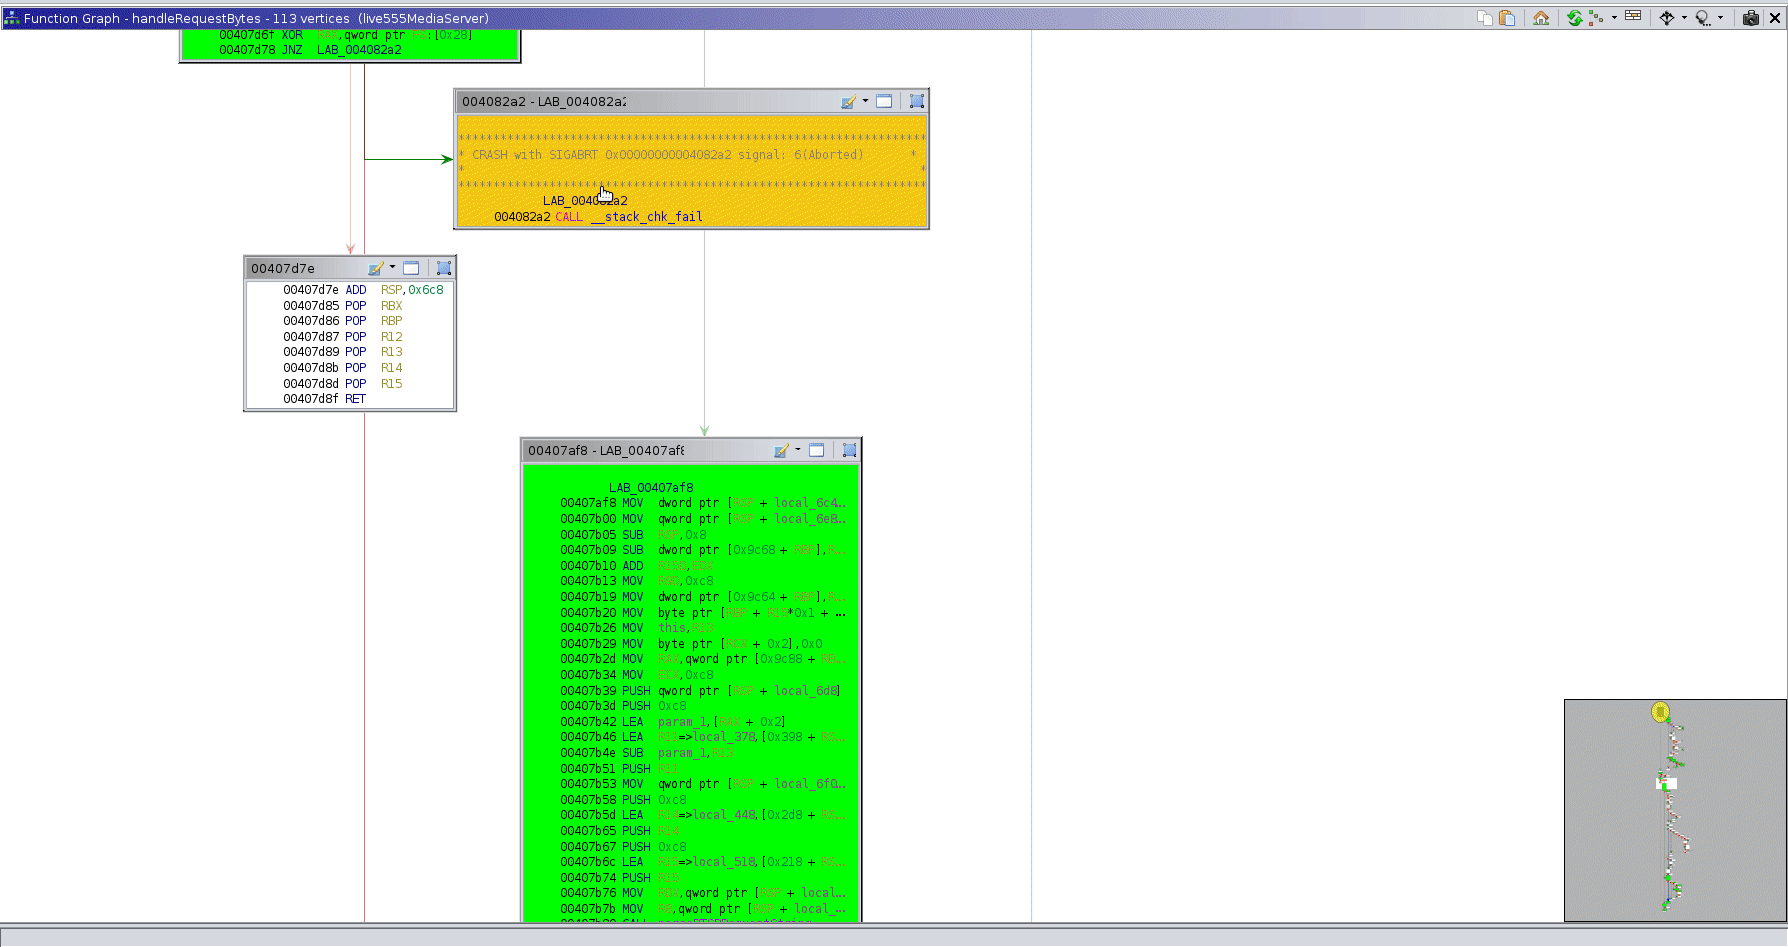
binary-analysisdebuggersdynamic-code-analysis+1
5982 years ago
functrace preview

functrace

GitHubinvictus1306/functrace

A function tracer
binary-analysisdebuggersdynamic-analysis-sandboxing+2
927 years ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux

android-securitybinary-exploitationdebuggers+5
197 years ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k3 days ago
super-tart-vphone-writeup preview

super-tart-vphone-writeup

GitHubwh1te4ever/super-tart-vphone-writeup

Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…

binary-exploitationdebuggersexploitation+7
1.3k7 months ago
snapchange preview

snapchange

GitHubawslabs/snapchange

Lightweight fuzzing of a memory snapshot using KVM
debuggersdynamic-analysis-sandboxingdynamic-code-analysis+3
4722 years ago
r0ak preview

r0ak

GitHubharryanon/r0ak

Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
binary-exploitationdebuggersexploitation+5
1088 years ago
sigwire preview

sigwire

GitHubyeet-src/sigwire

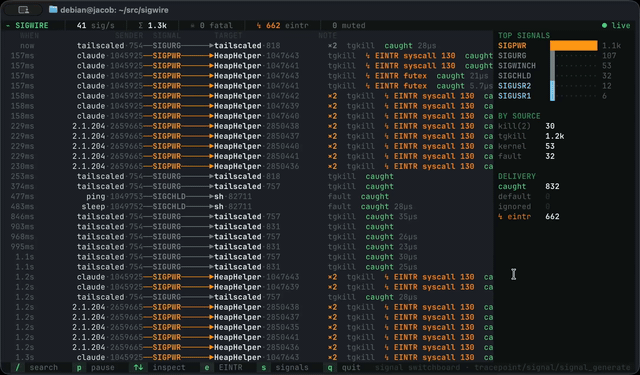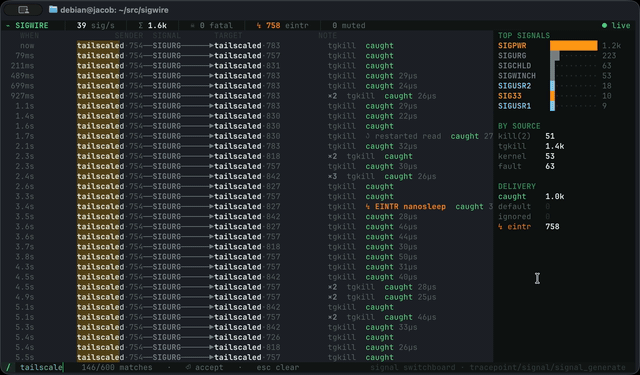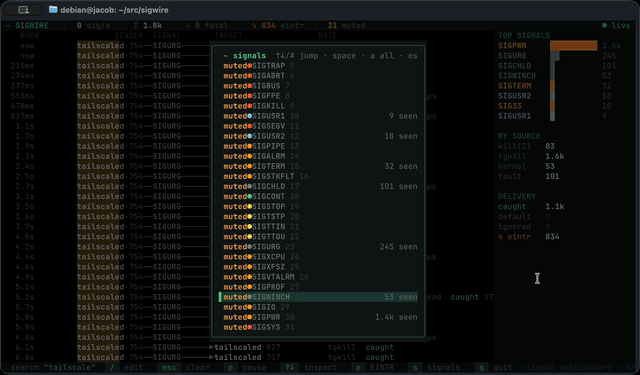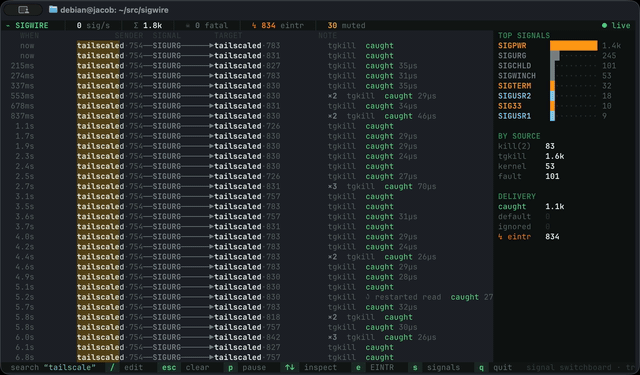
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
debuggersdynamic-analysis-sandboxingforensics+2
1602 months ago
ebpfmon preview

ebpfmon

GitHubredcanaryco/ebpfmon

Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…

debuggersdynamic-analysis-sandboxingutilities-frameworks
903 years ago
Previous123Next