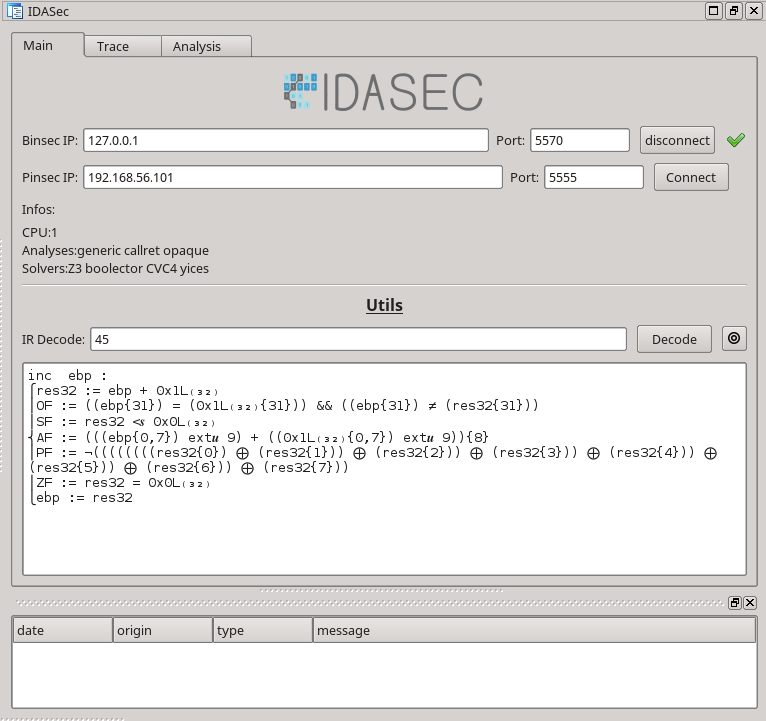
idasec
 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1178 years ago
robindavid/idasecIDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
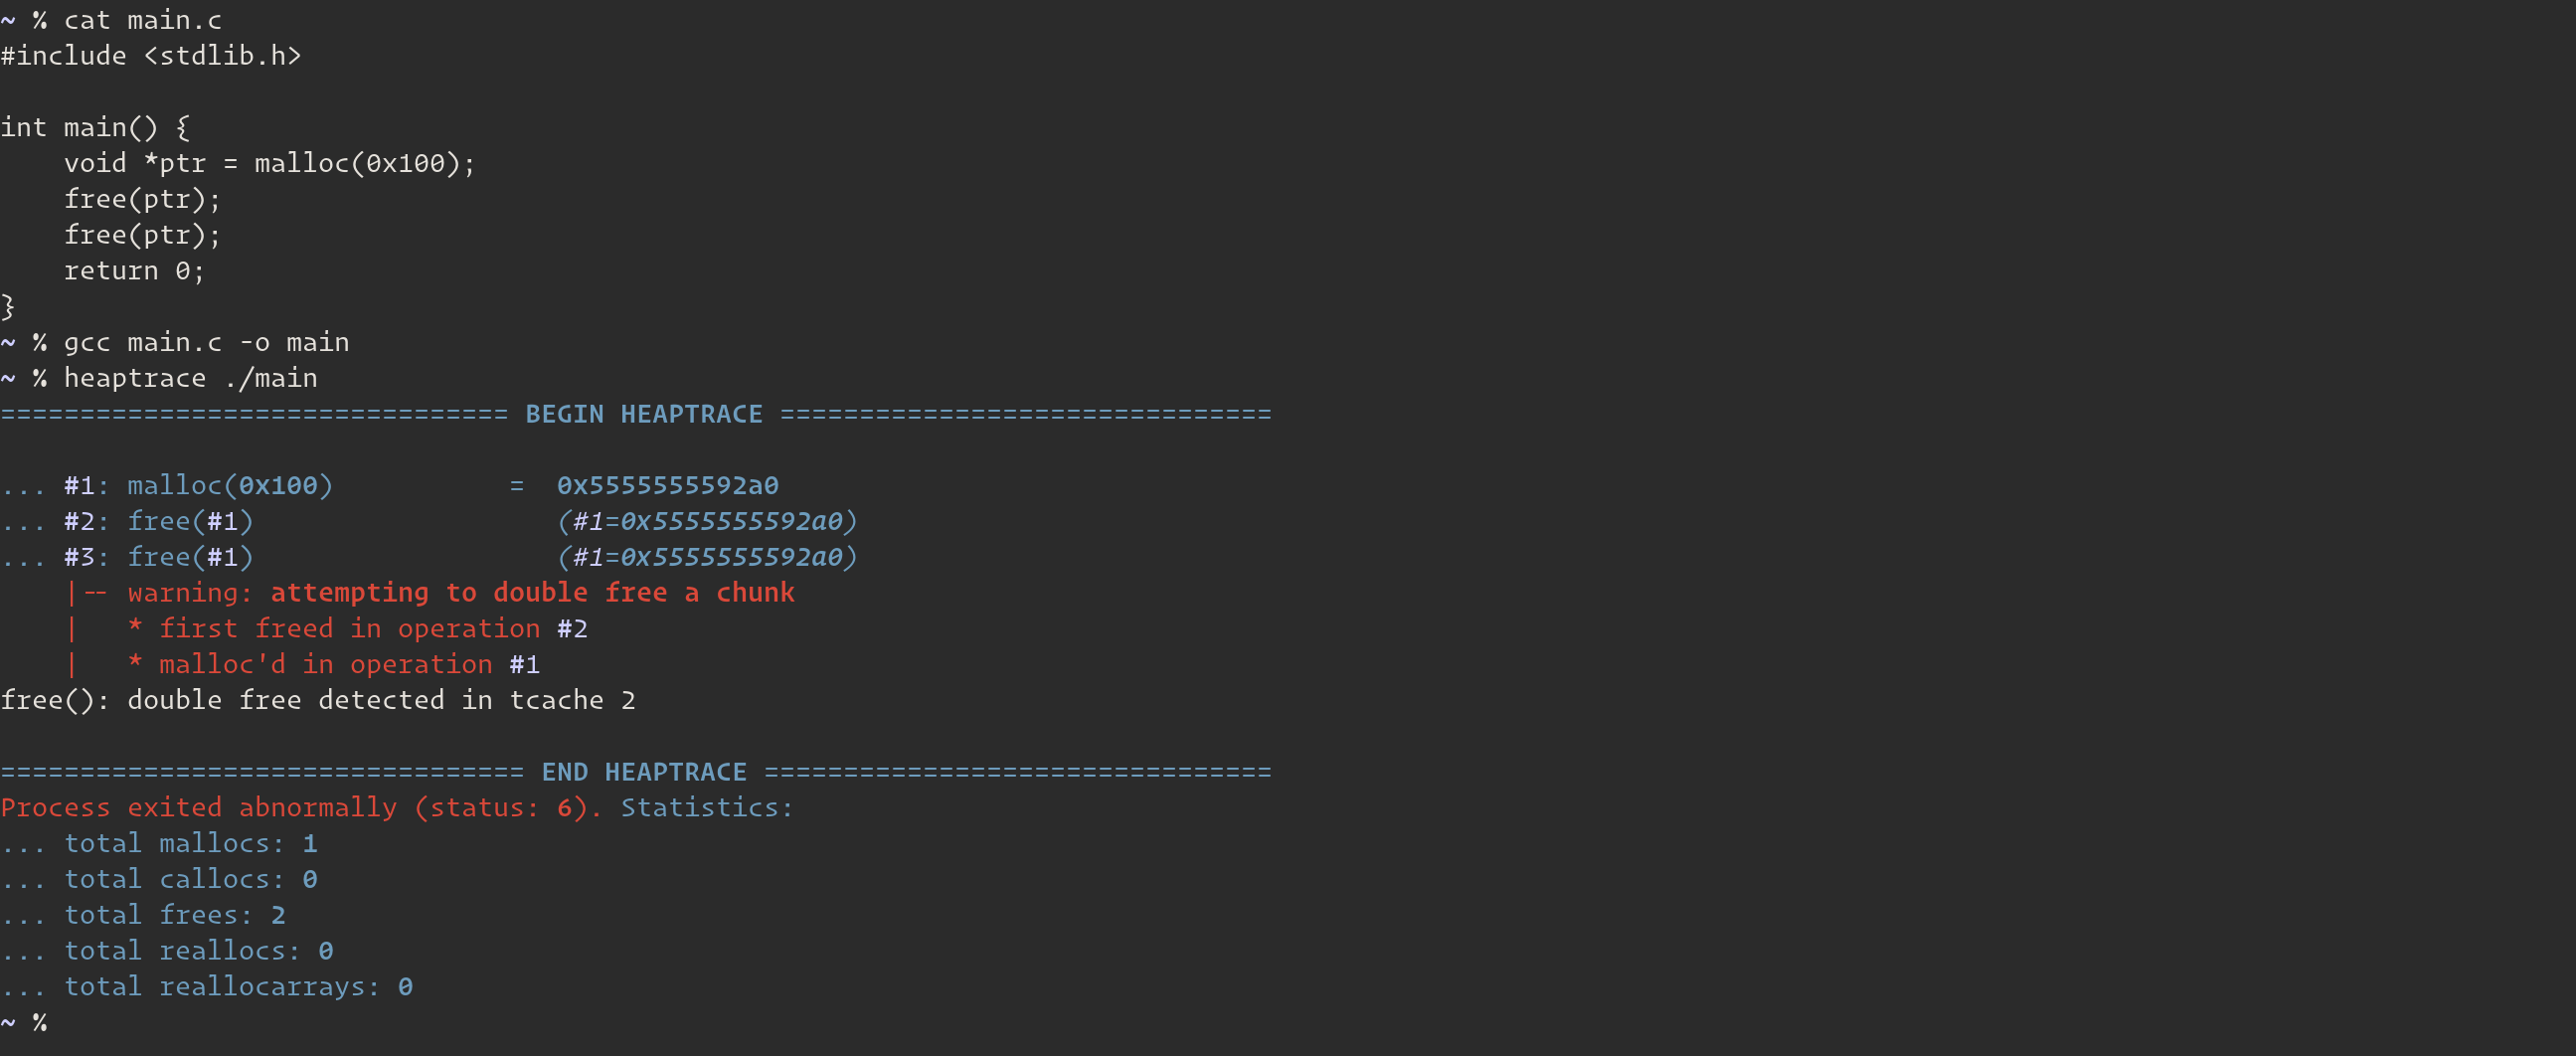 arinerron/heaptrace
helps visualize heap operations for pwn and debugging
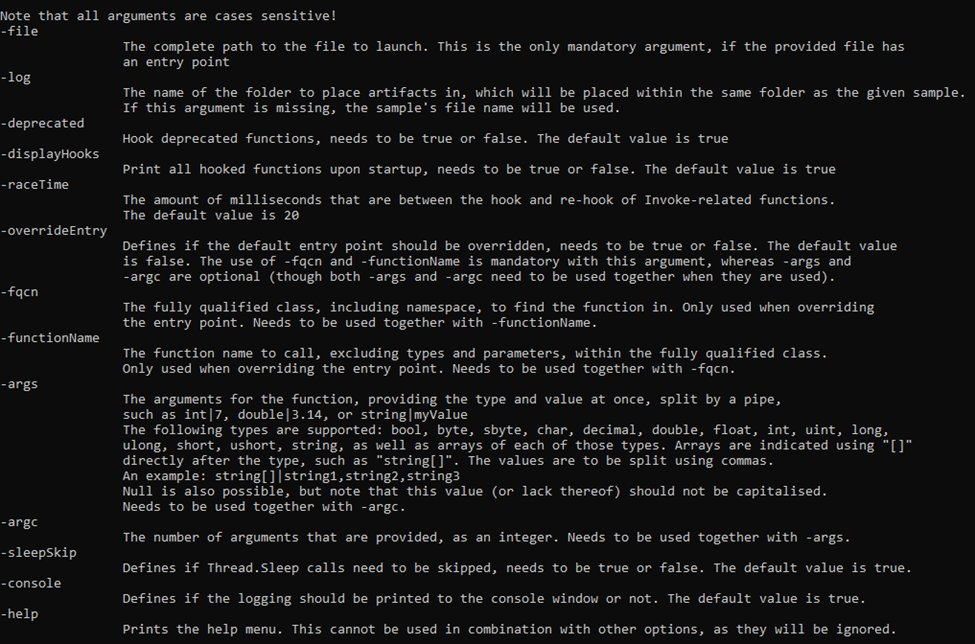 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
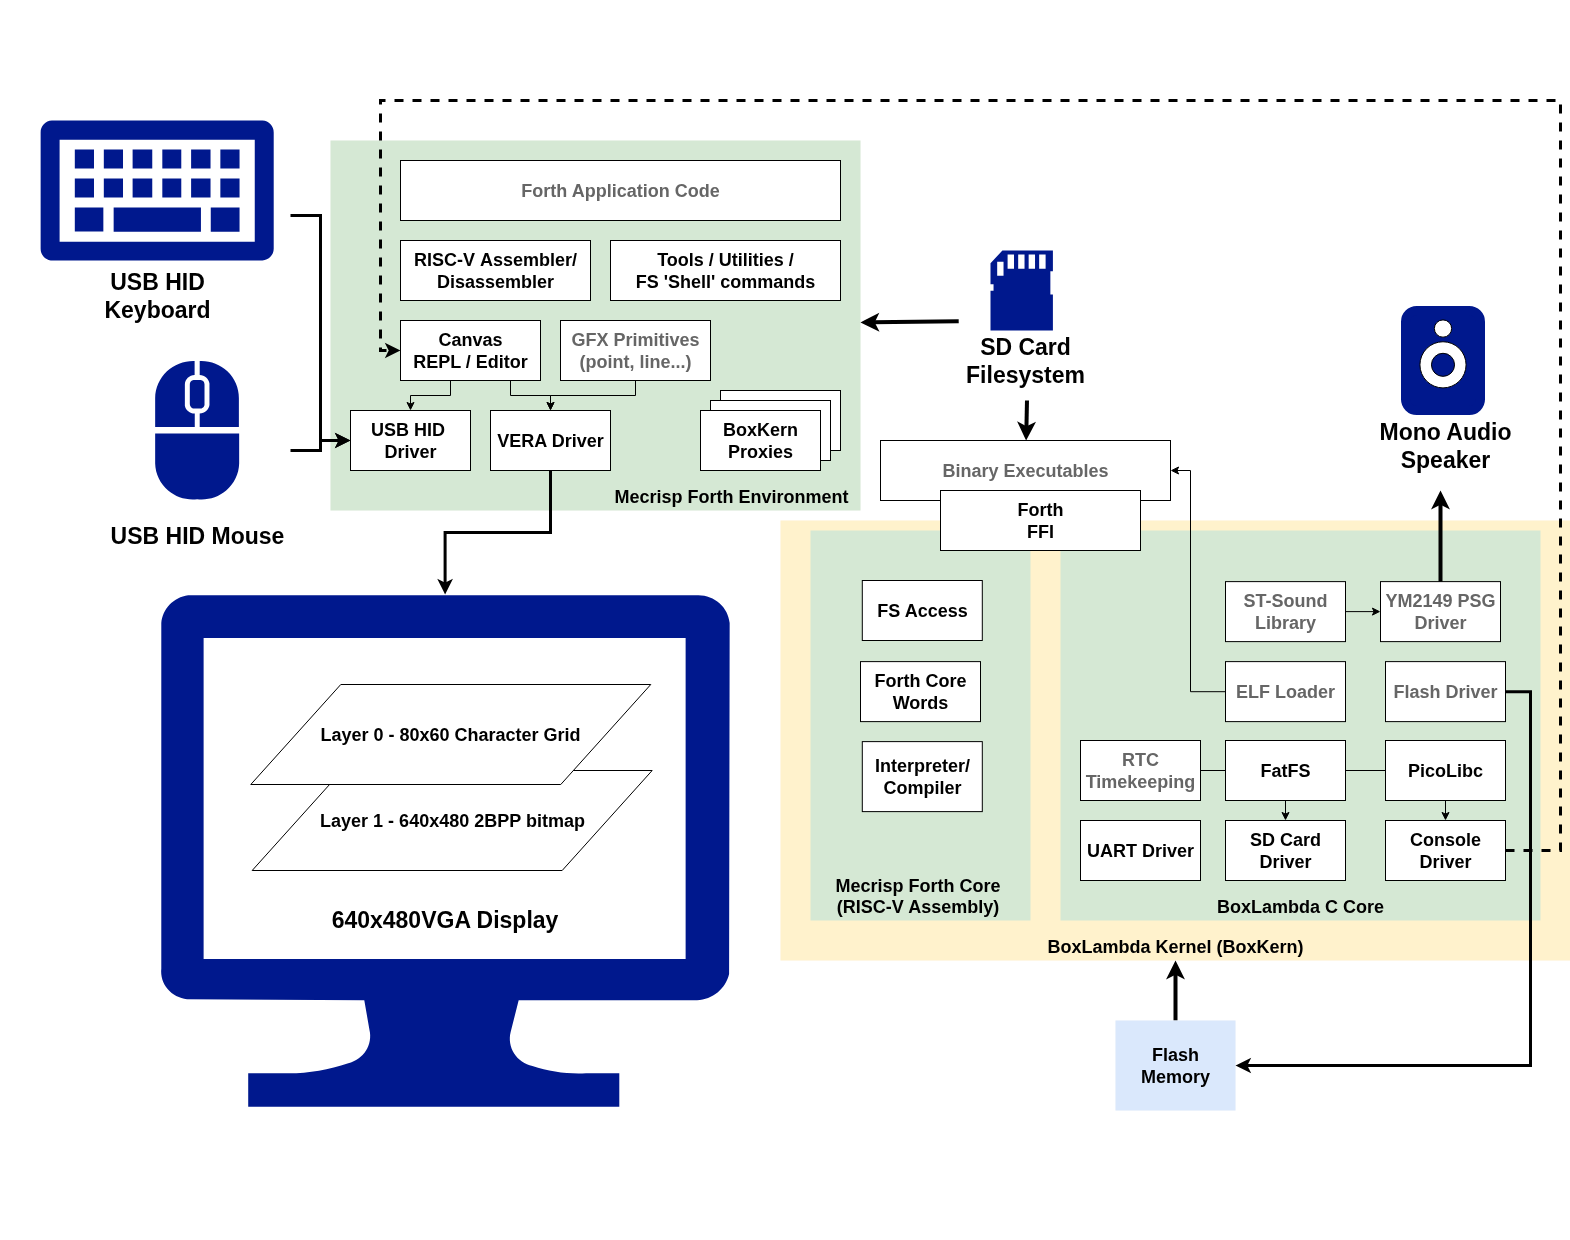 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
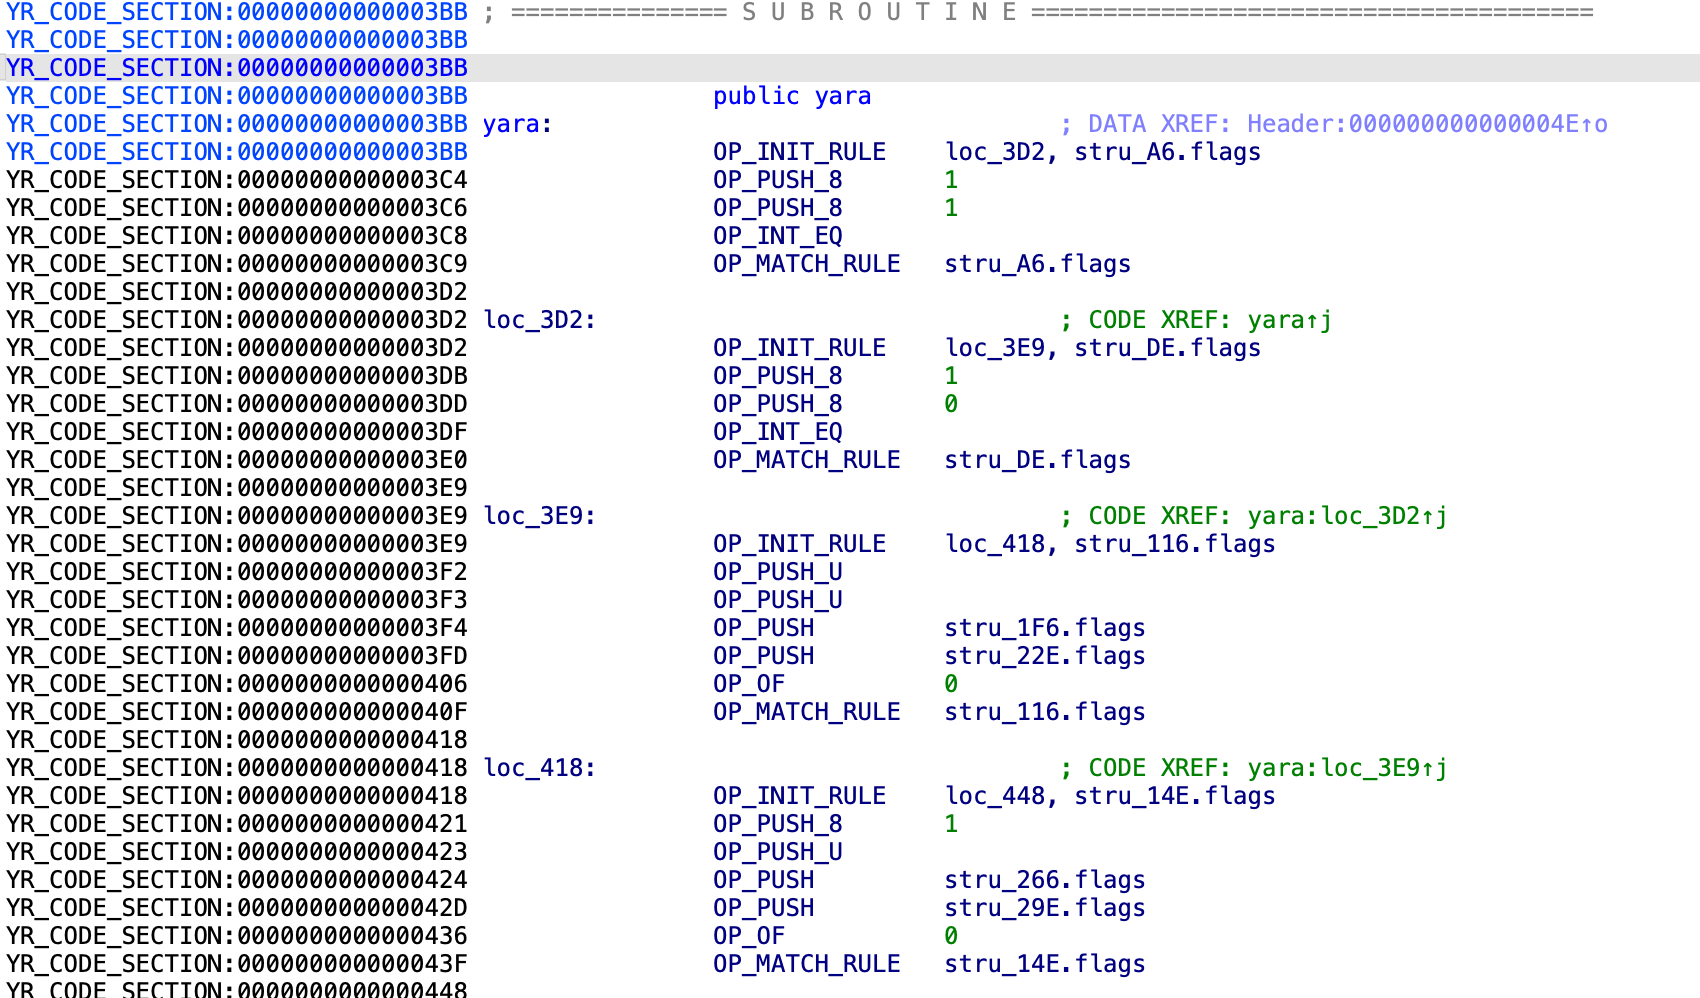 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
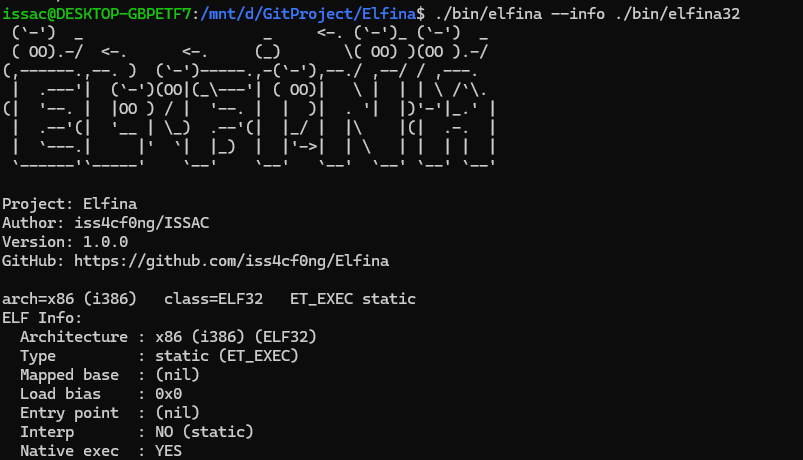 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 halcy0nic/cve-2023-40294-and-cve-2023-40295
Proof of concept for CVE-2023-40294 and CVE-2023-40295
 gmh5225/ida-sdk
Official IDA Pro SDK headers and libraries for building plugins that disassemble, decompile, and analyze binaries within the IDA reverse engineering…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 luisyapura/analisis-y-explotacion-de-cve-2025-5548
Educational lab for analyzing and exploiting CVE-2025-5548 (FreeFloat FTP Server buffer overflow) with step-by-step guides, debugger setup, and…
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…
 beraphin/cve-2017-16943
Technical analysis and proof-of-concept for CVE-2017-16943, a use-after-free in Exim's receive_msg function, demonstrating heap manipulation and RIP…