
AIDebug
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
ai-securitybinary-analysisdebuggers+7
12
anpa1200/aidebugEvidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
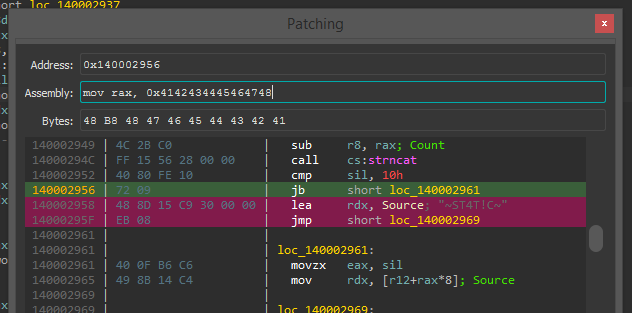 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
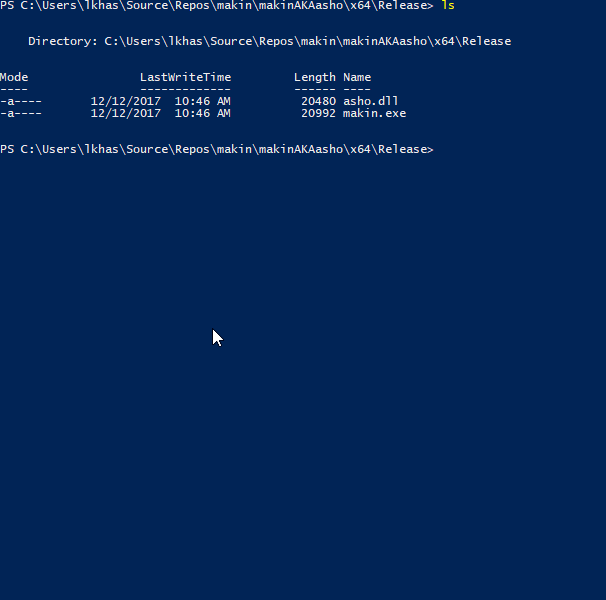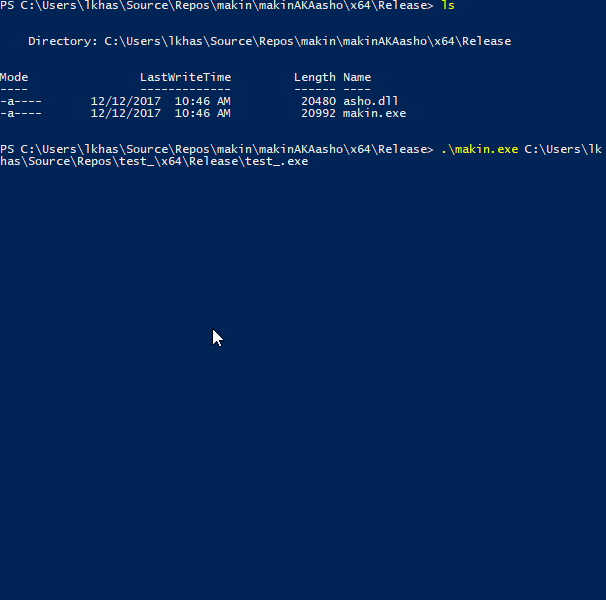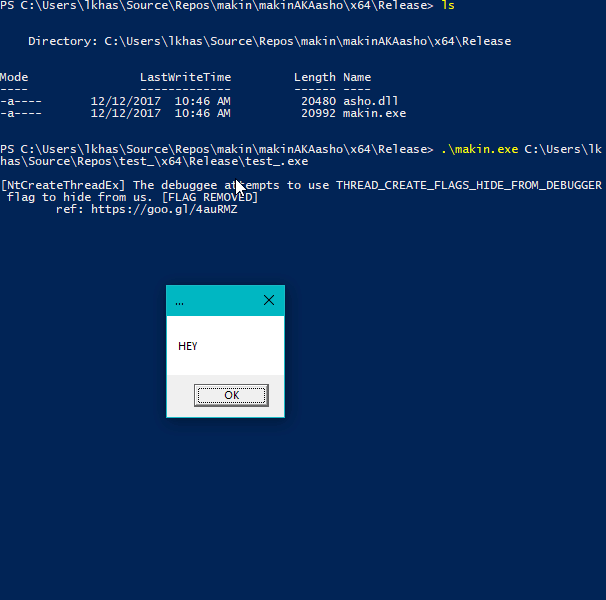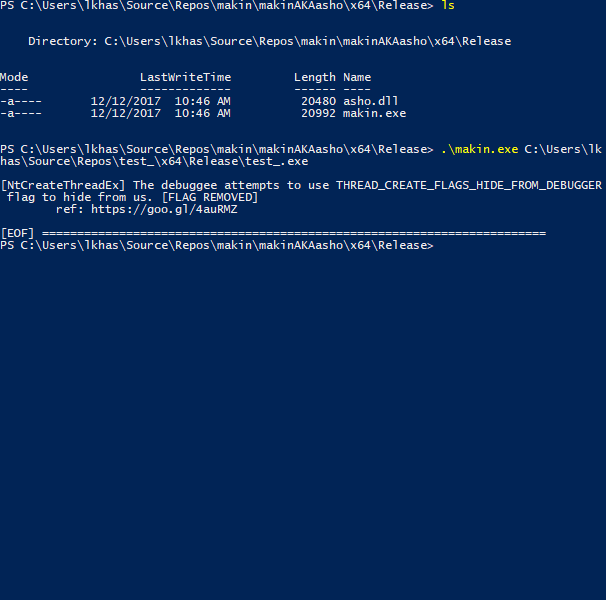 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
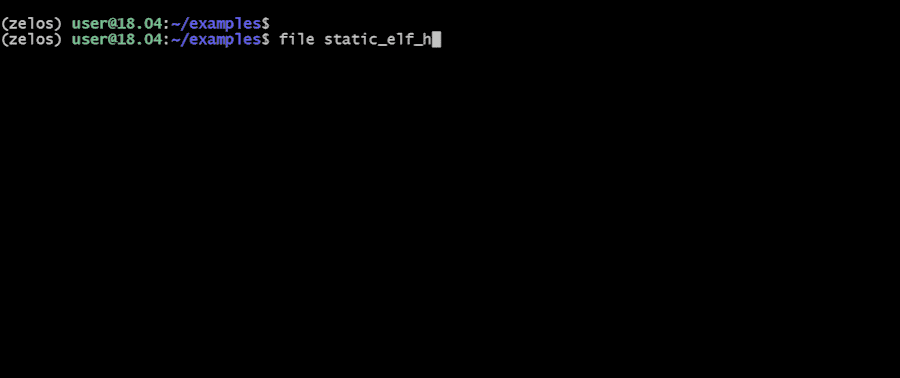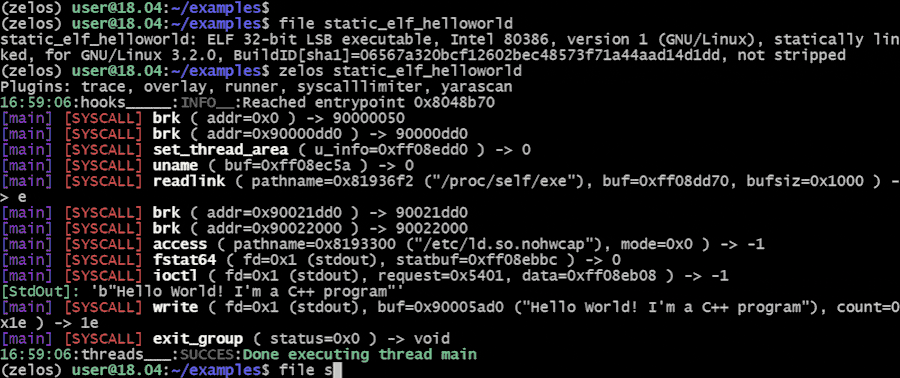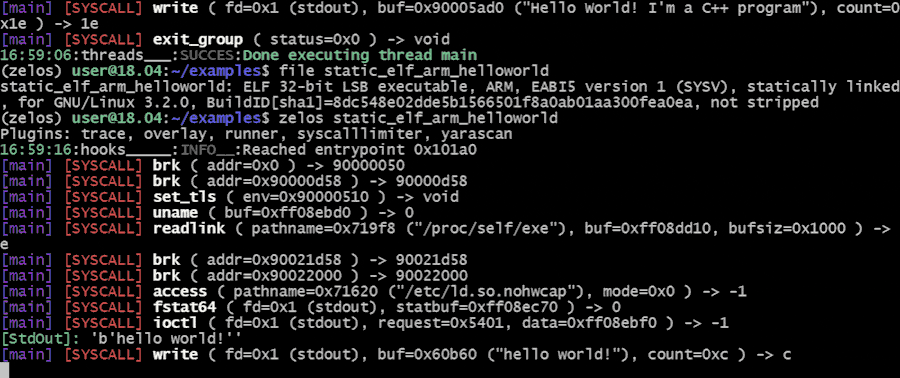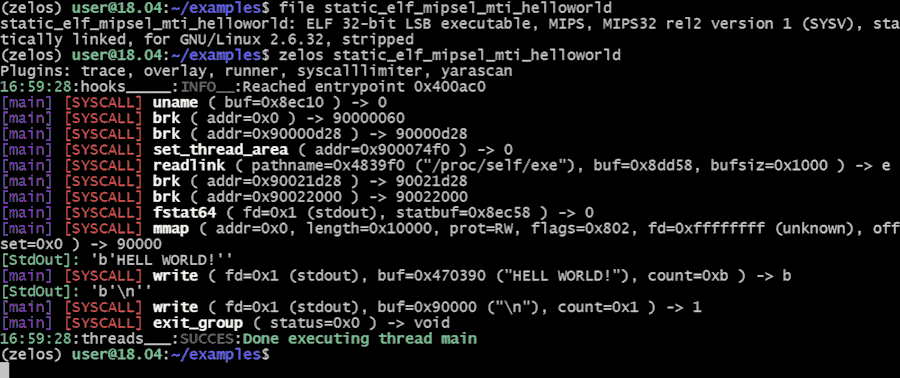 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]
 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
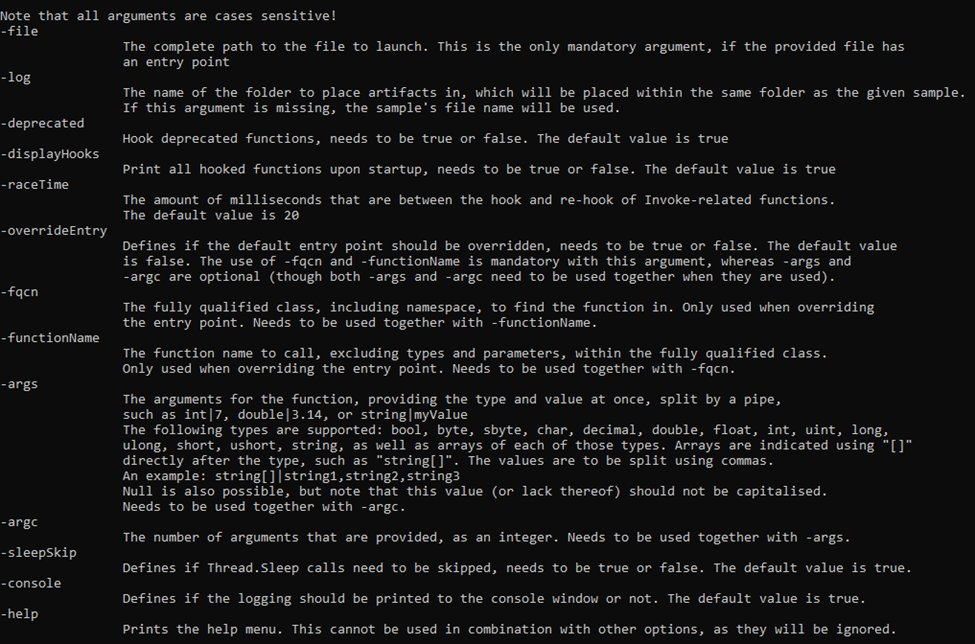 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
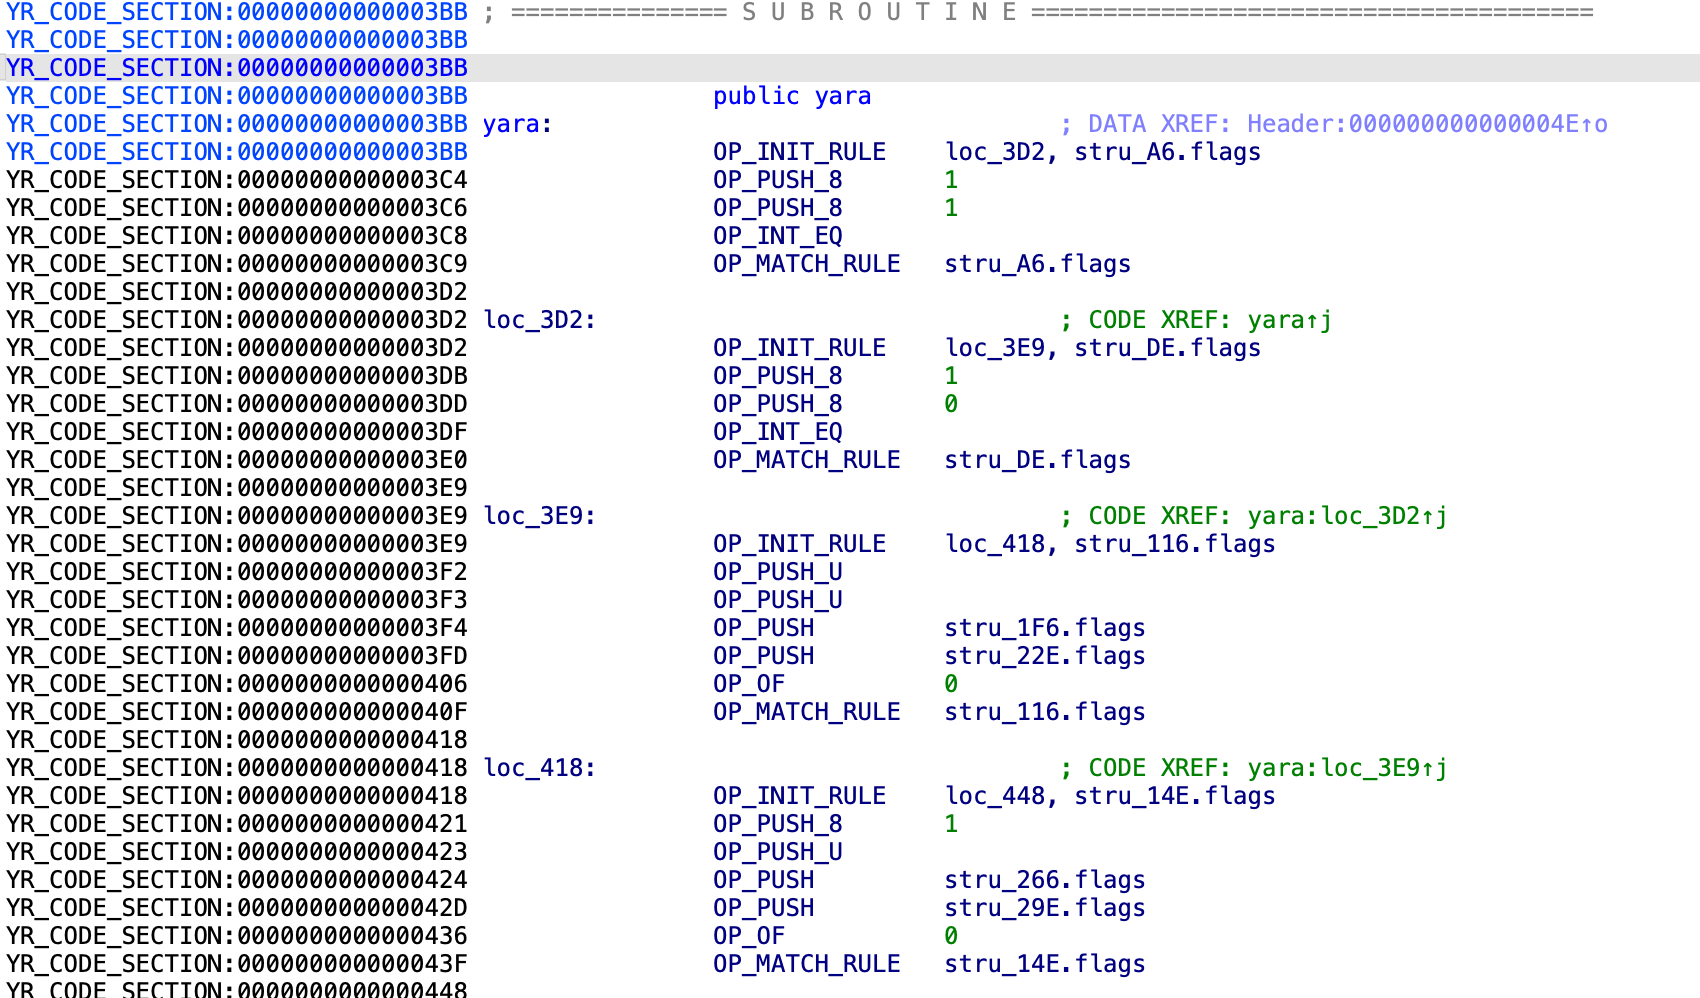 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset