
Archived
gdbfuzz
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
binary-analysisdebuggerseducation+6
196
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 frida/frida
Main repo for hosting release binaries
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
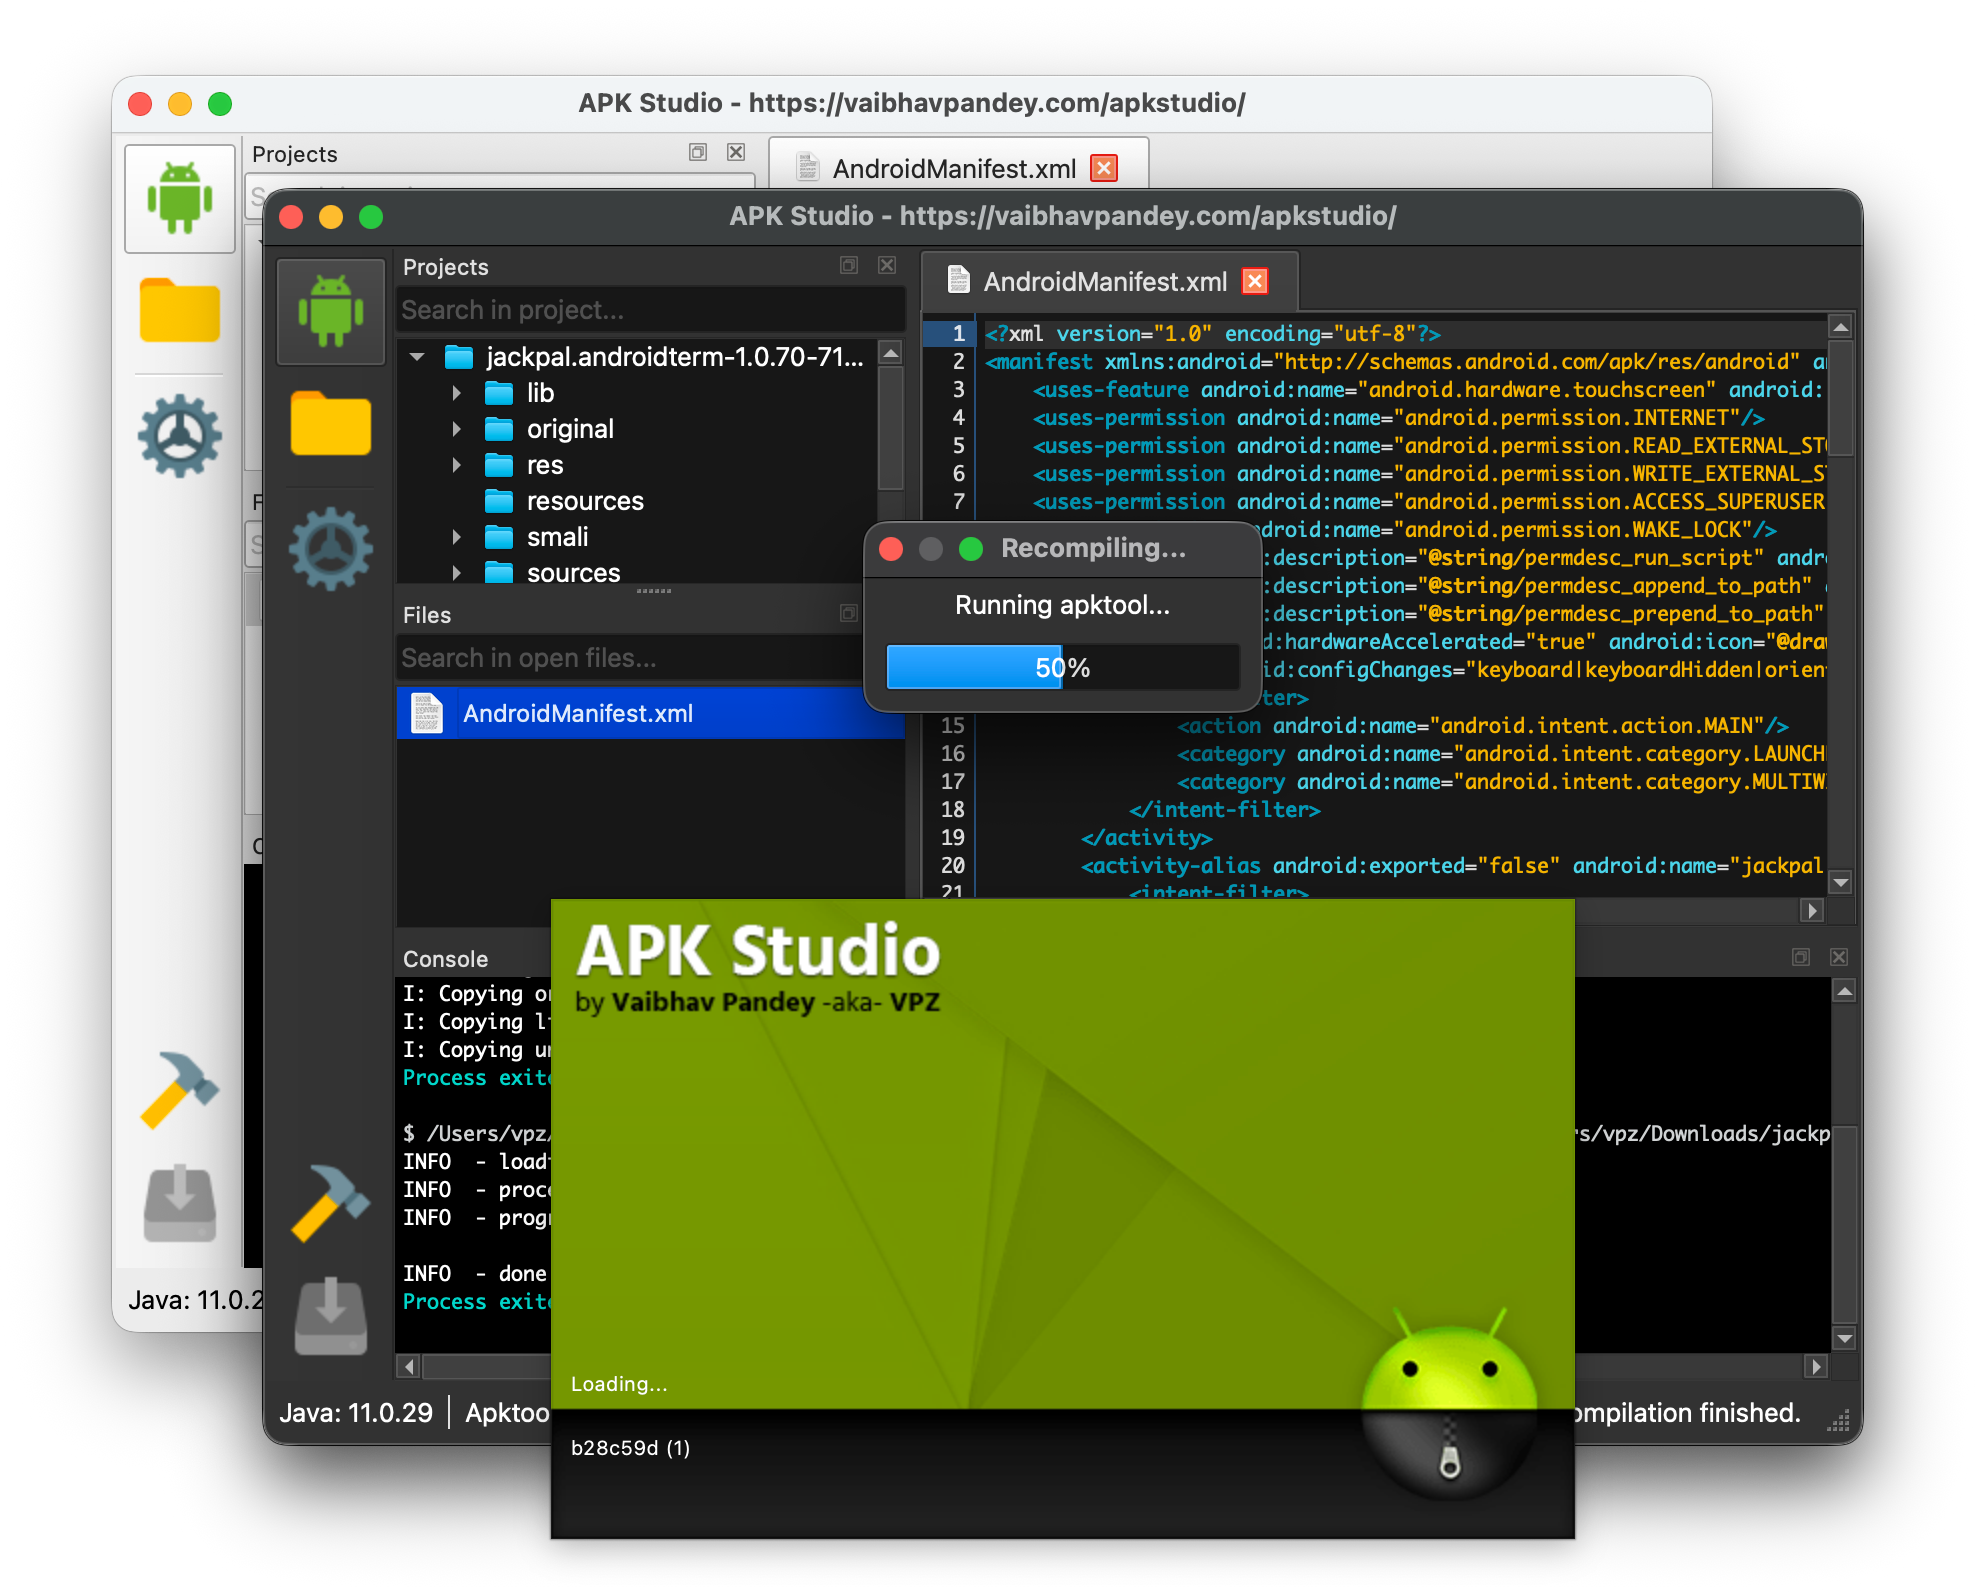 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
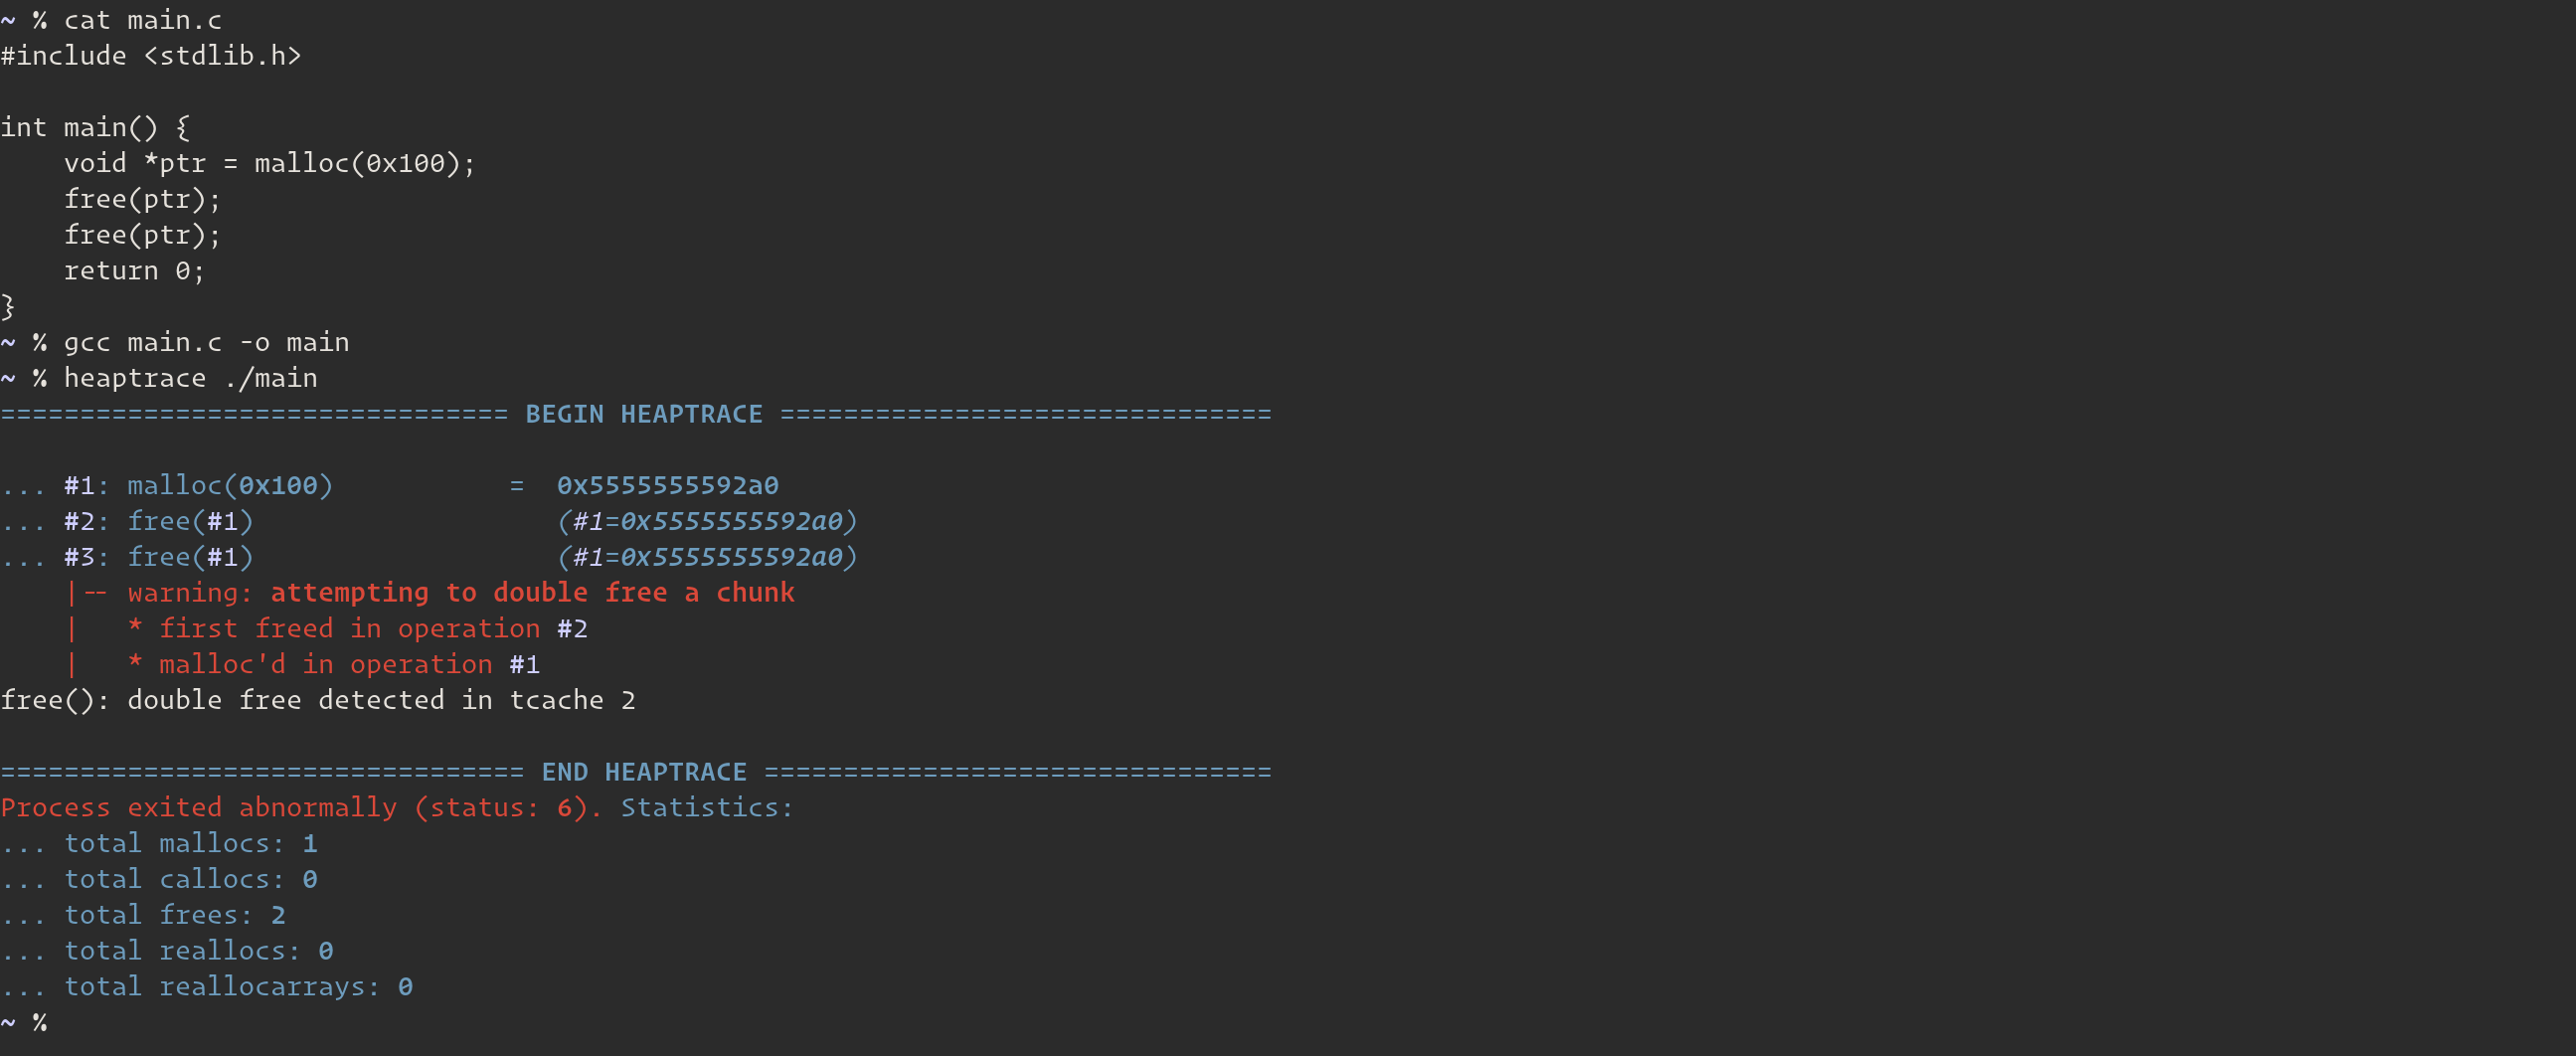 arinerron/heaptrace
helps visualize heap operations for pwn and debugging
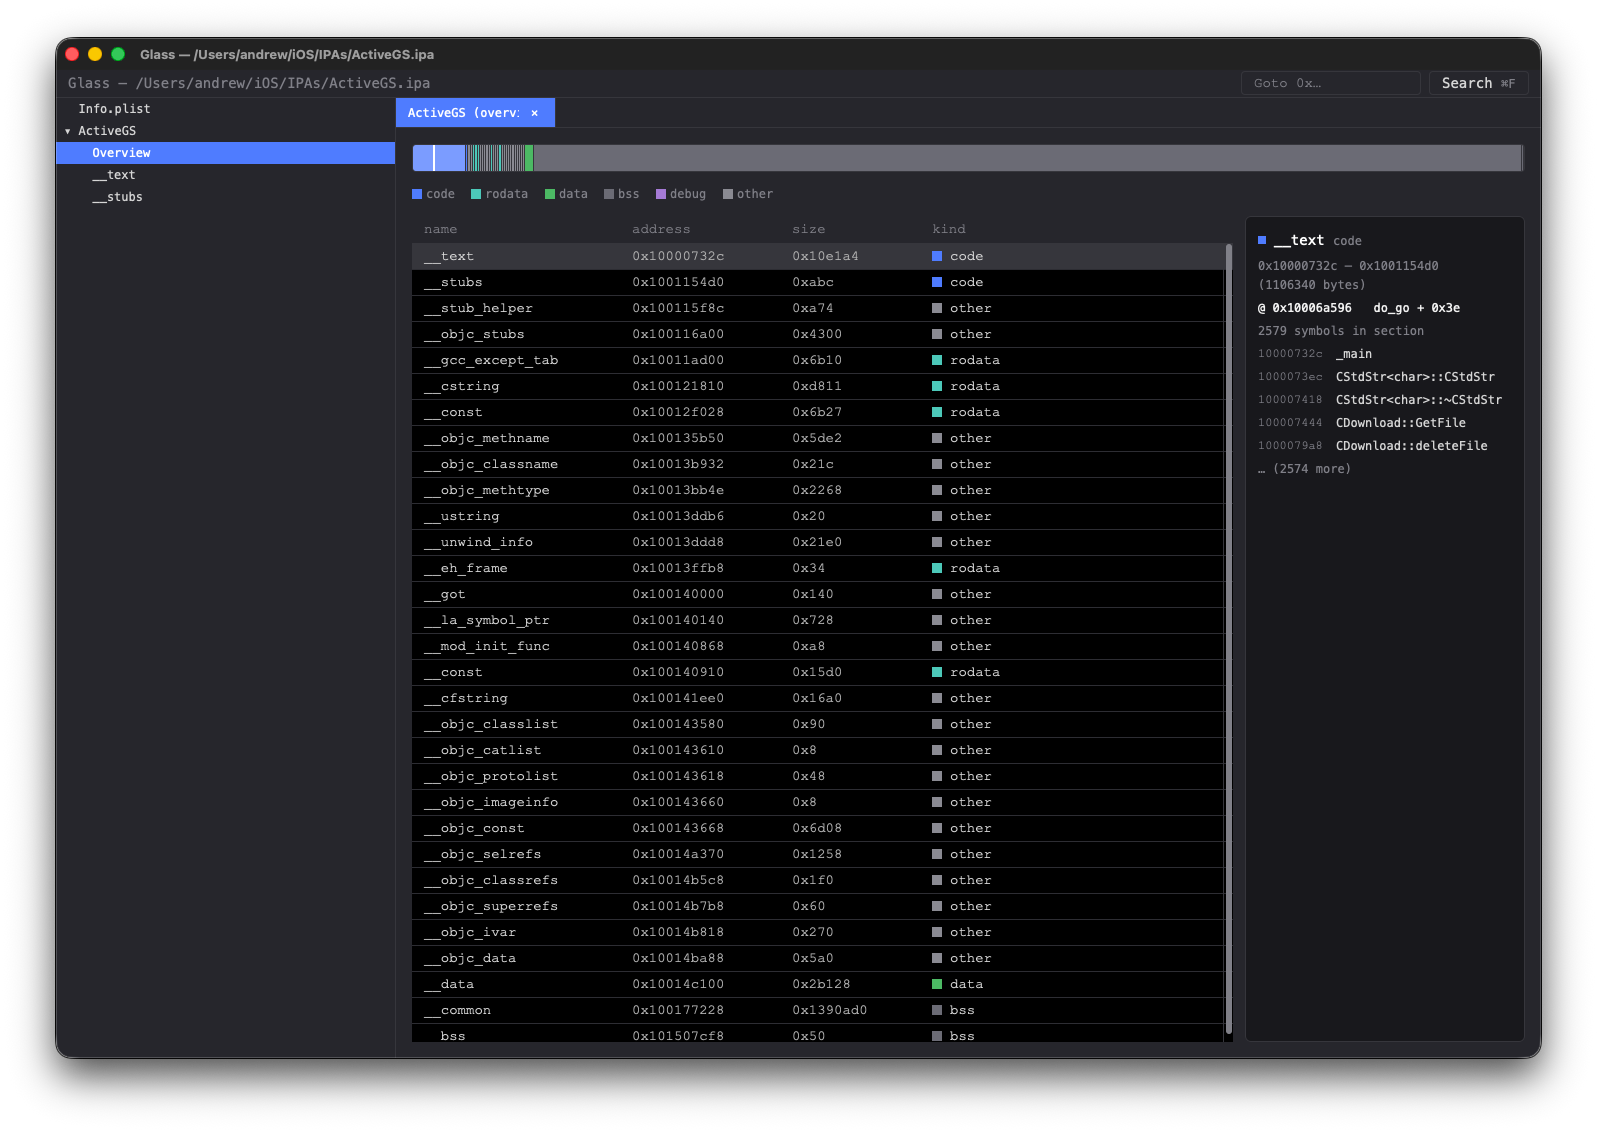 azw413/glass
Glass - a fast and free IDA Pro alternative
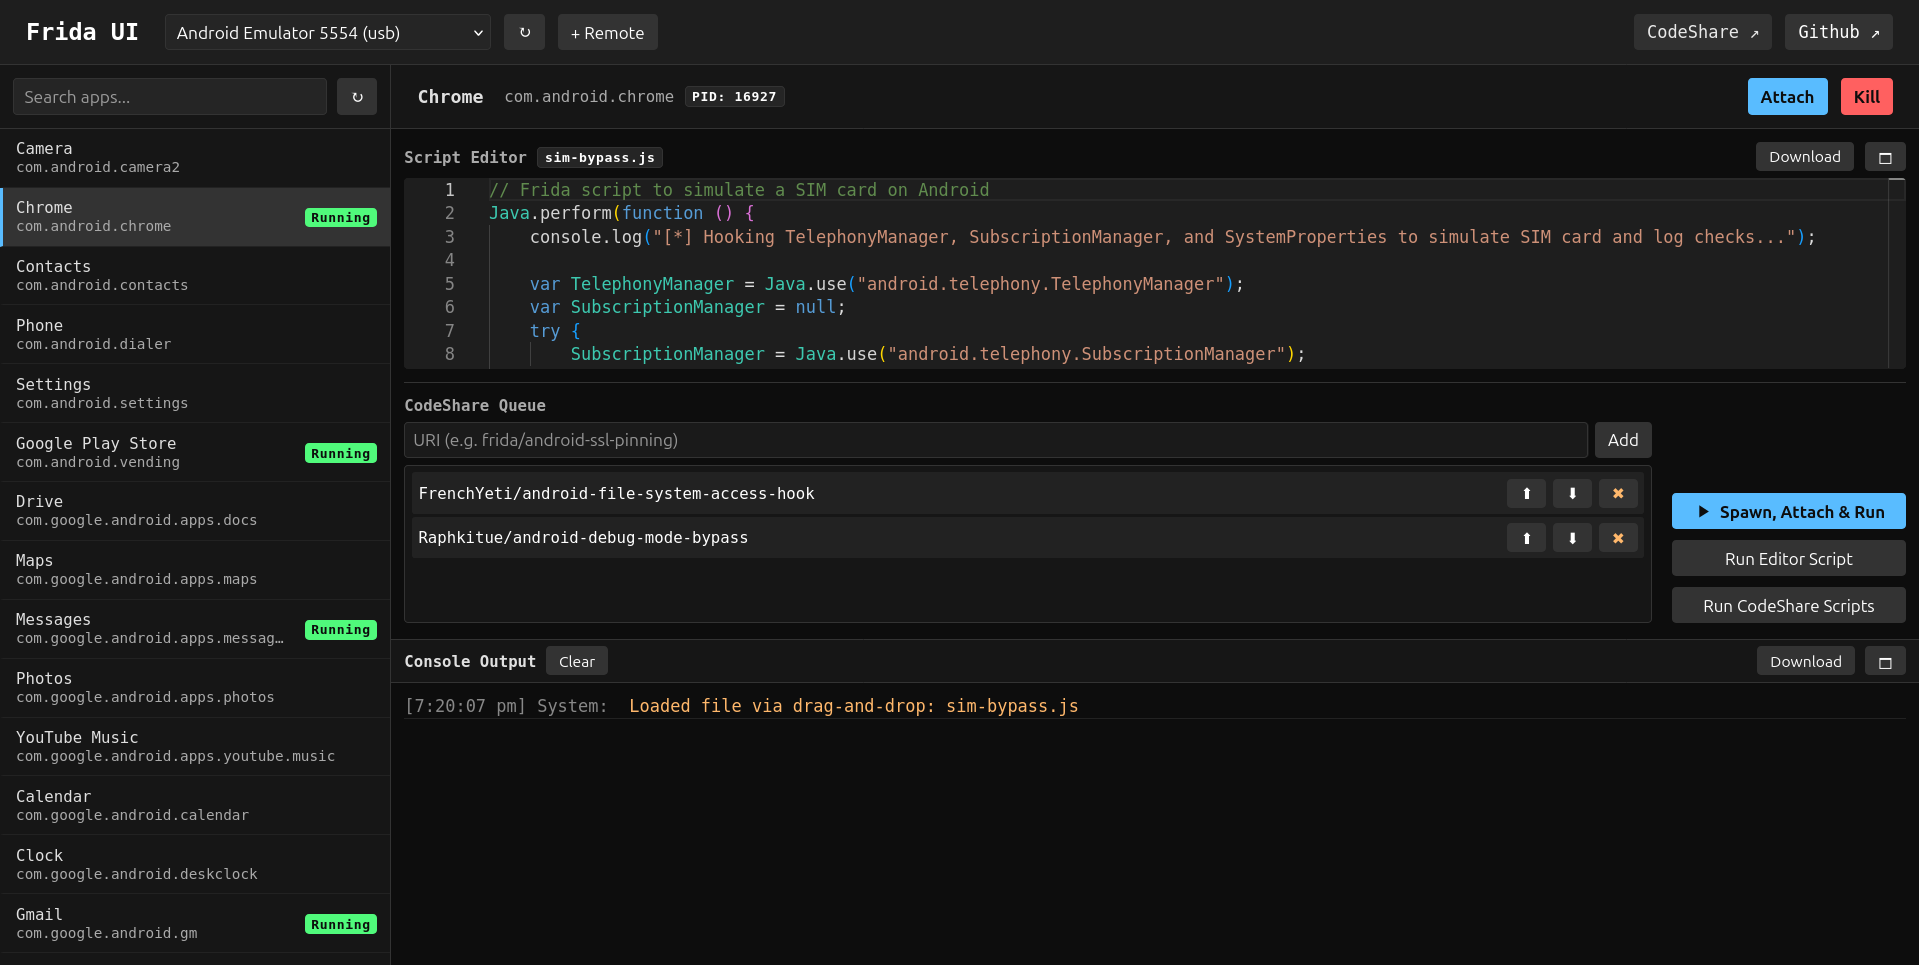 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
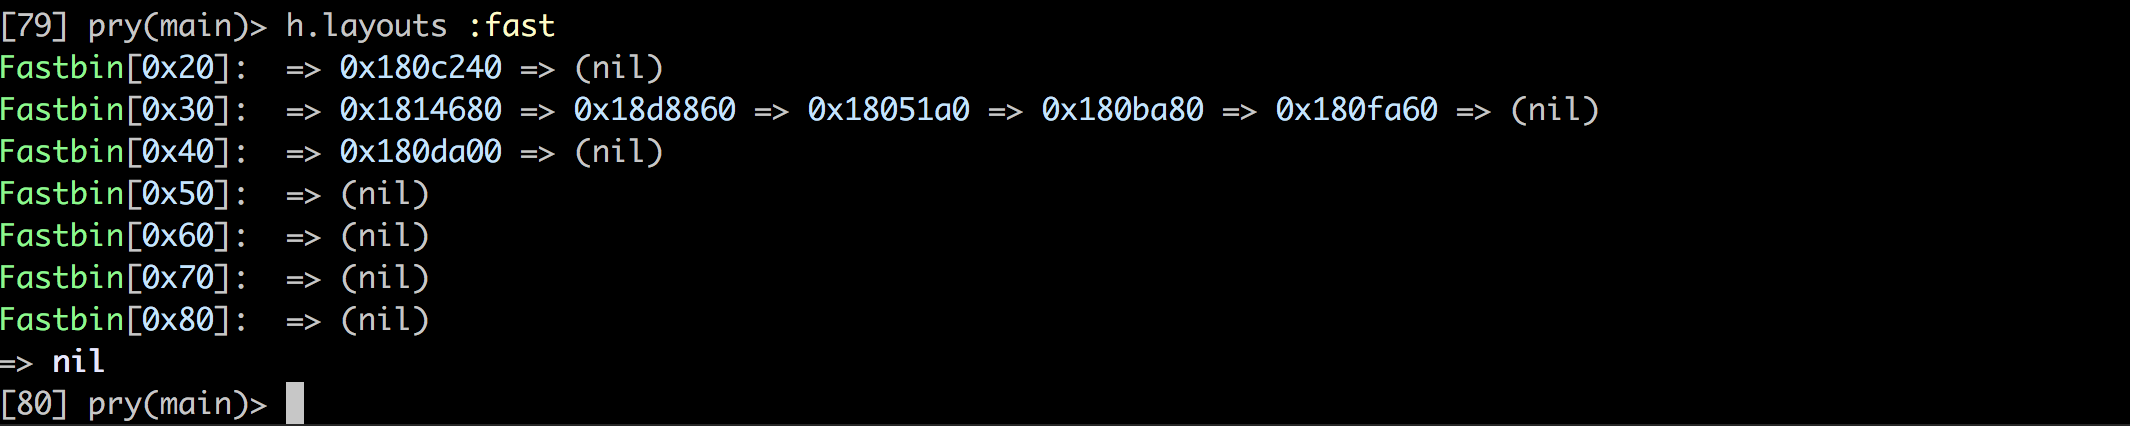 david942j/heapinfo
An interactive memory info for pwning / exploiting
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 axlan/fatal_core_dump
A core dump debugging murder mystery.