

nginxpwn
 kitctf/nginxpwn
Exploitation Training -- CVE-2013-2028: Nginx Stack Based Buffer Overflow
binary-exploitationdebuggerseducation+3
5510 years ago
kitctf/nginxpwnExploitation Training -- CVE-2013-2028: Nginx Stack Based Buffer Overflow
 enkomio/sojobo
A binary analysis framework
 fail0verflow/ps5-umtxdbg
C++ exploit reliability experimentation for a PlayStation 5 FreeBSD kernel vulnerability, with VM kernel builds and GDB remote-debugging setup.
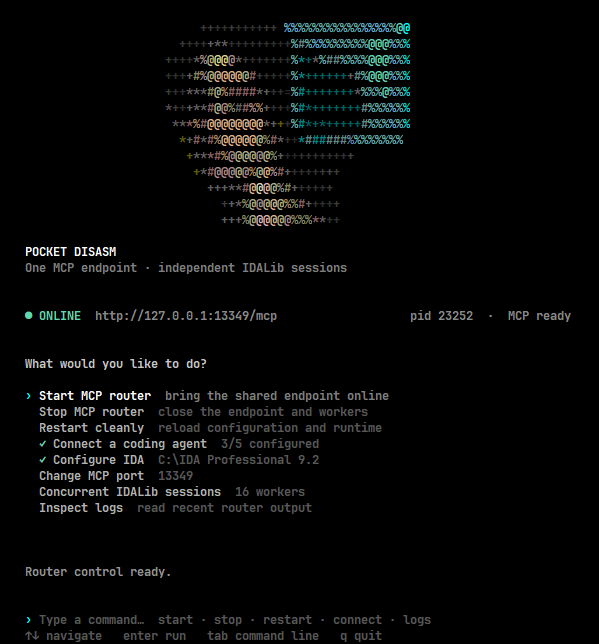 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
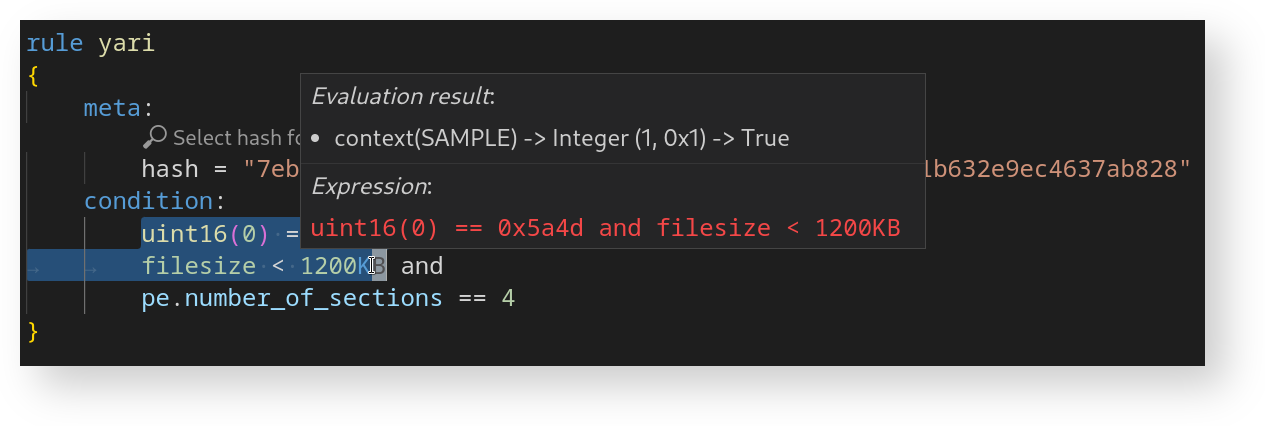 avast/yari
YARI is an interactive debugger for YARA Language.
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
 baiyibai/pico-usb-wifi
Firmware for Raspberry Pi Pico W that creates a driverless USB Wi-Fi adapter with transparent layer-2 bridging, WPA2/WPA3 authentication, and…
 kernelzeroday/cve-2021-3156-baron-samedit
1day research effort
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
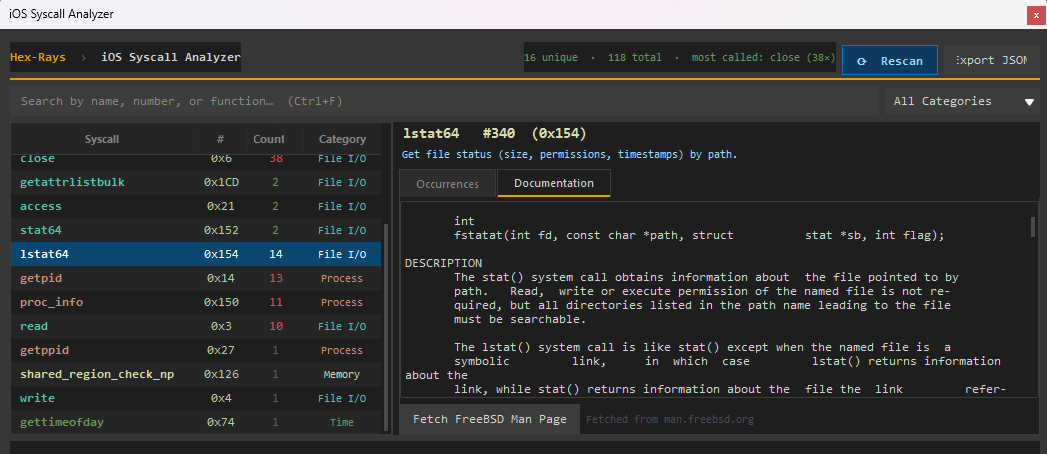 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
 jaydcarlson/c2-printf
Print trace messages over a Silicon Labs C2 debugger connection
 ypl6/heaplens
CMPT733 Cybersecurity Lab II Project: GDB plugin for heap exploits inspired by CVE-2021-3156
 alfa8sa/cve-2025-5548
Heap Buffer Overflow in CVE-2025-5548
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 calysteon/cve-2025-43504
Technical deep-dive into CVE-2025-43504, a remote pre-authentication global buffer overflow in LLDB's debugserver for iOS, with PoC code and…
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 hugsy/recon_2024_windbg_workshop
Workshop materials for mastering WinDbg debugging in kernel and user mode, with KdNet setup, demos, and a Time Travel Debugging challenge for binary…