

Jackalope
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
binary-analysisdebuggersdynamic-analysis-sandboxing+6
1.4k
googleprojectzero/jackalopeBinary, coverage-guided fuzzer for Windows, macOS, Linux and Android
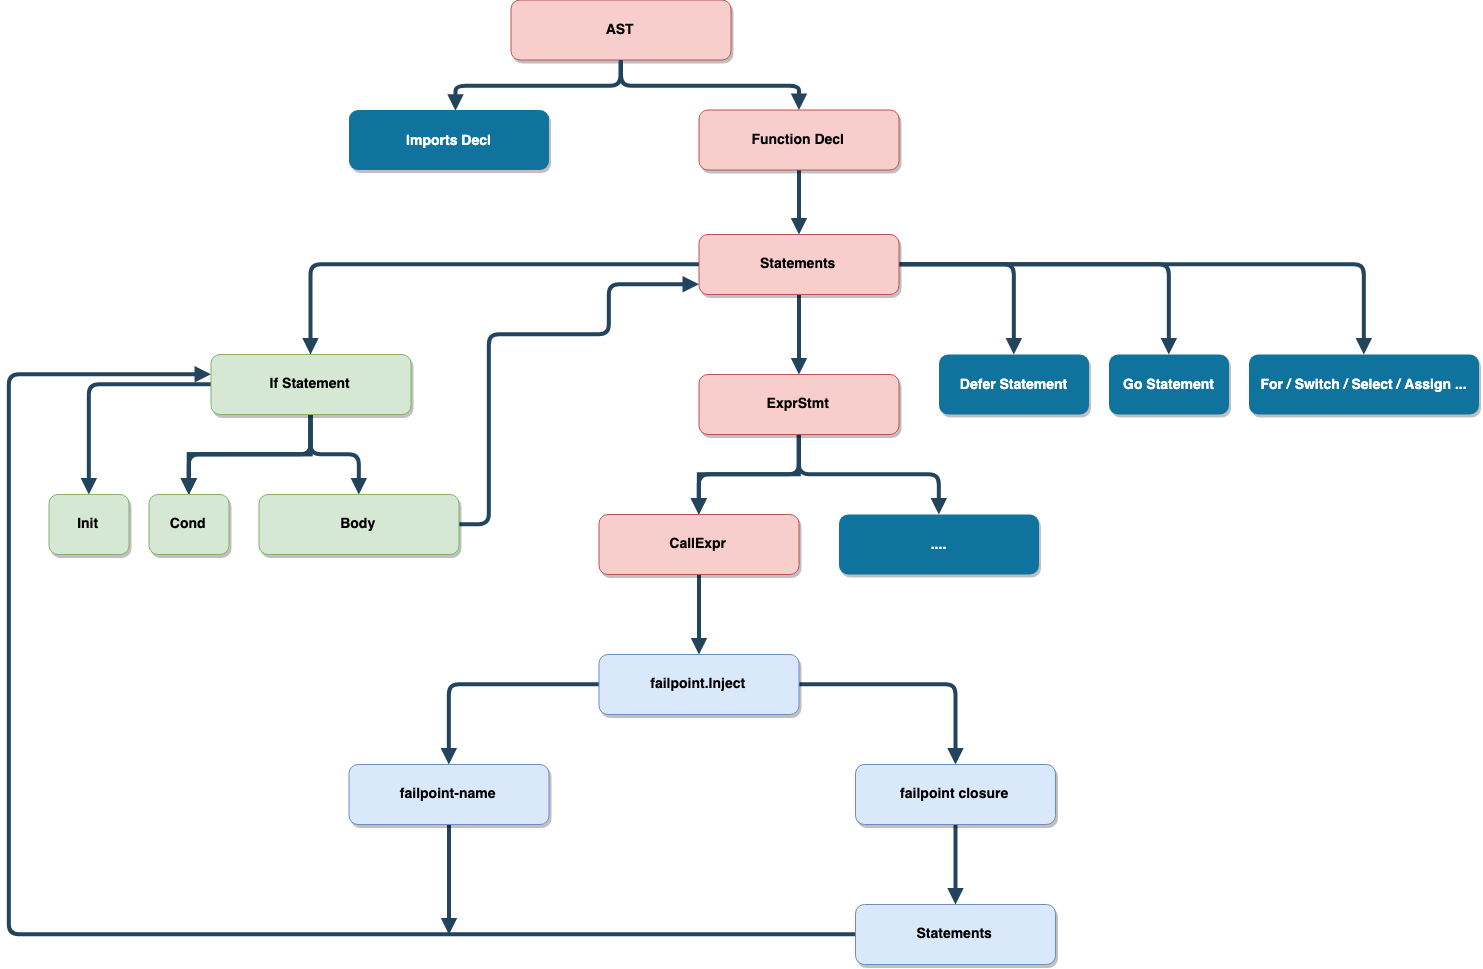 pingcap/failpoint
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
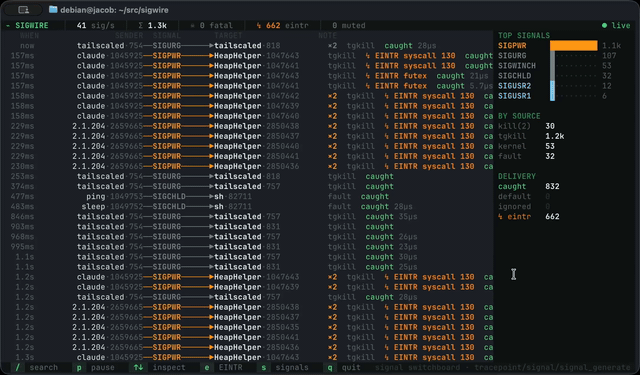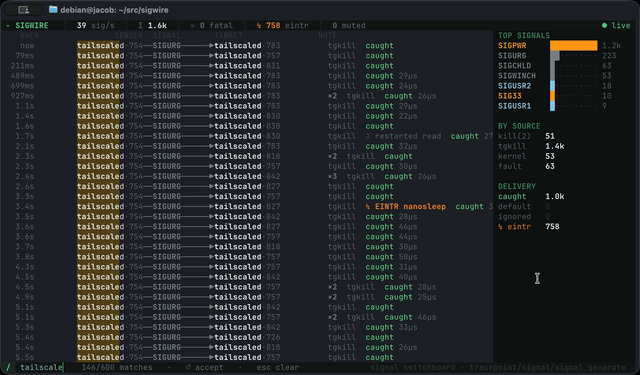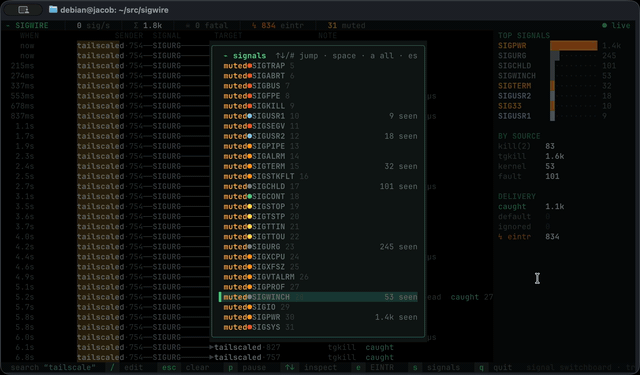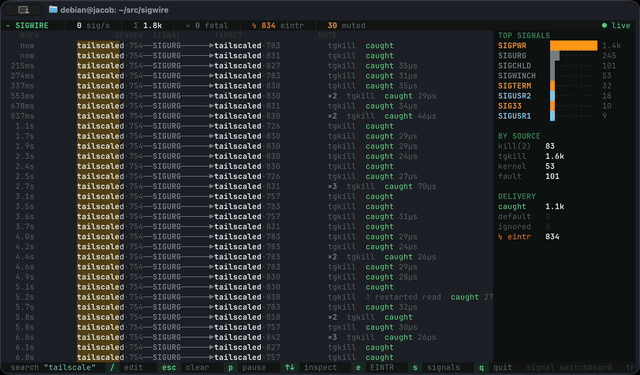 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
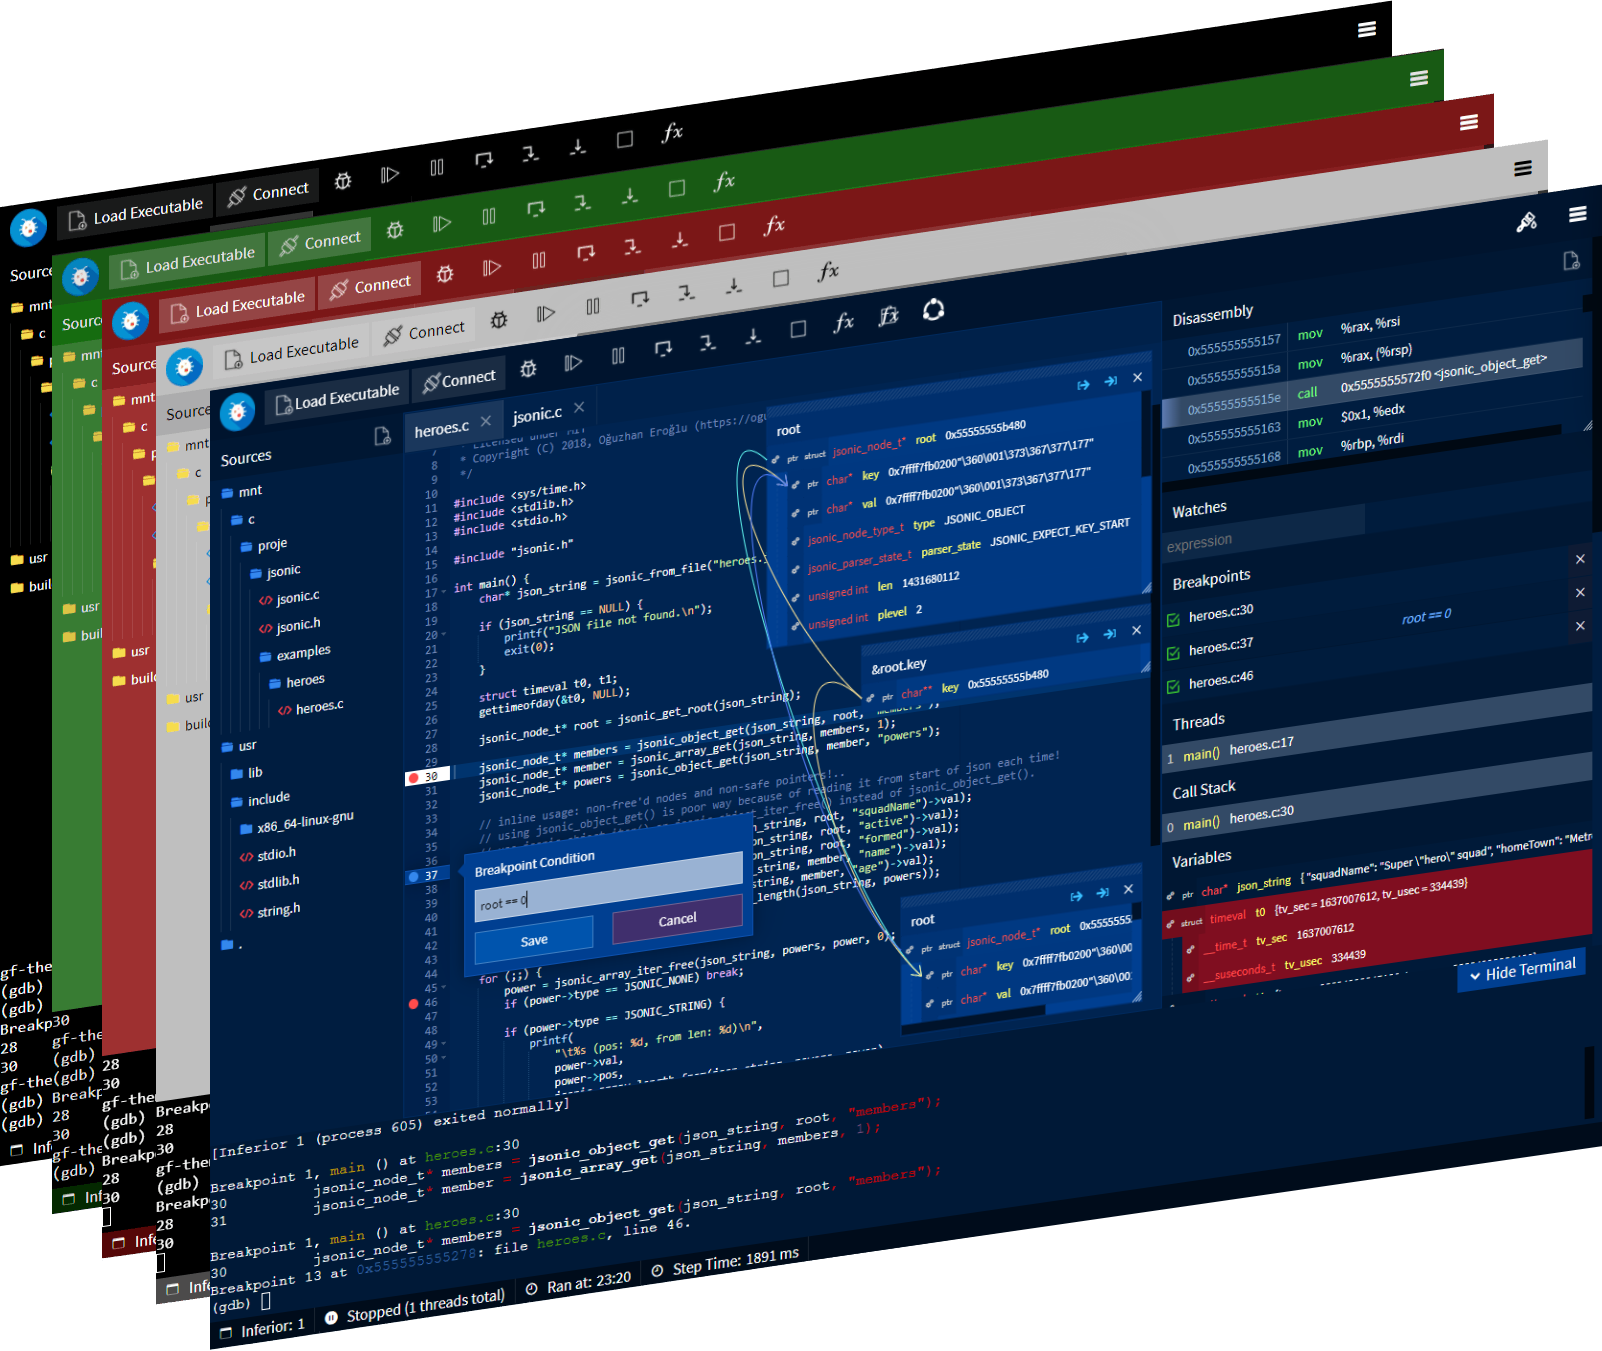 rohanrhu/gdb-frontend
☕ GDBFrontend is an easy, flexible and extensible gui debugger.

 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
 shaikusaf/linux-4.19.72_cve-2020-14356
Linux kernel source tree modified for CVE-2020-14356, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…
 fuzzysecurity/powershell-suite
My musings with PowerShell
 deputation/instrumentation_callbacks
A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
 amossys/memitm
Tool to make in memory man in the middle