

rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
3.9k
rizinorg/rizinUNIX-like reverse engineering framework and command-line toolset.
 angr/angr
A powerful and user-friendly binary analysis platform!
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through the Remote Debugging…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
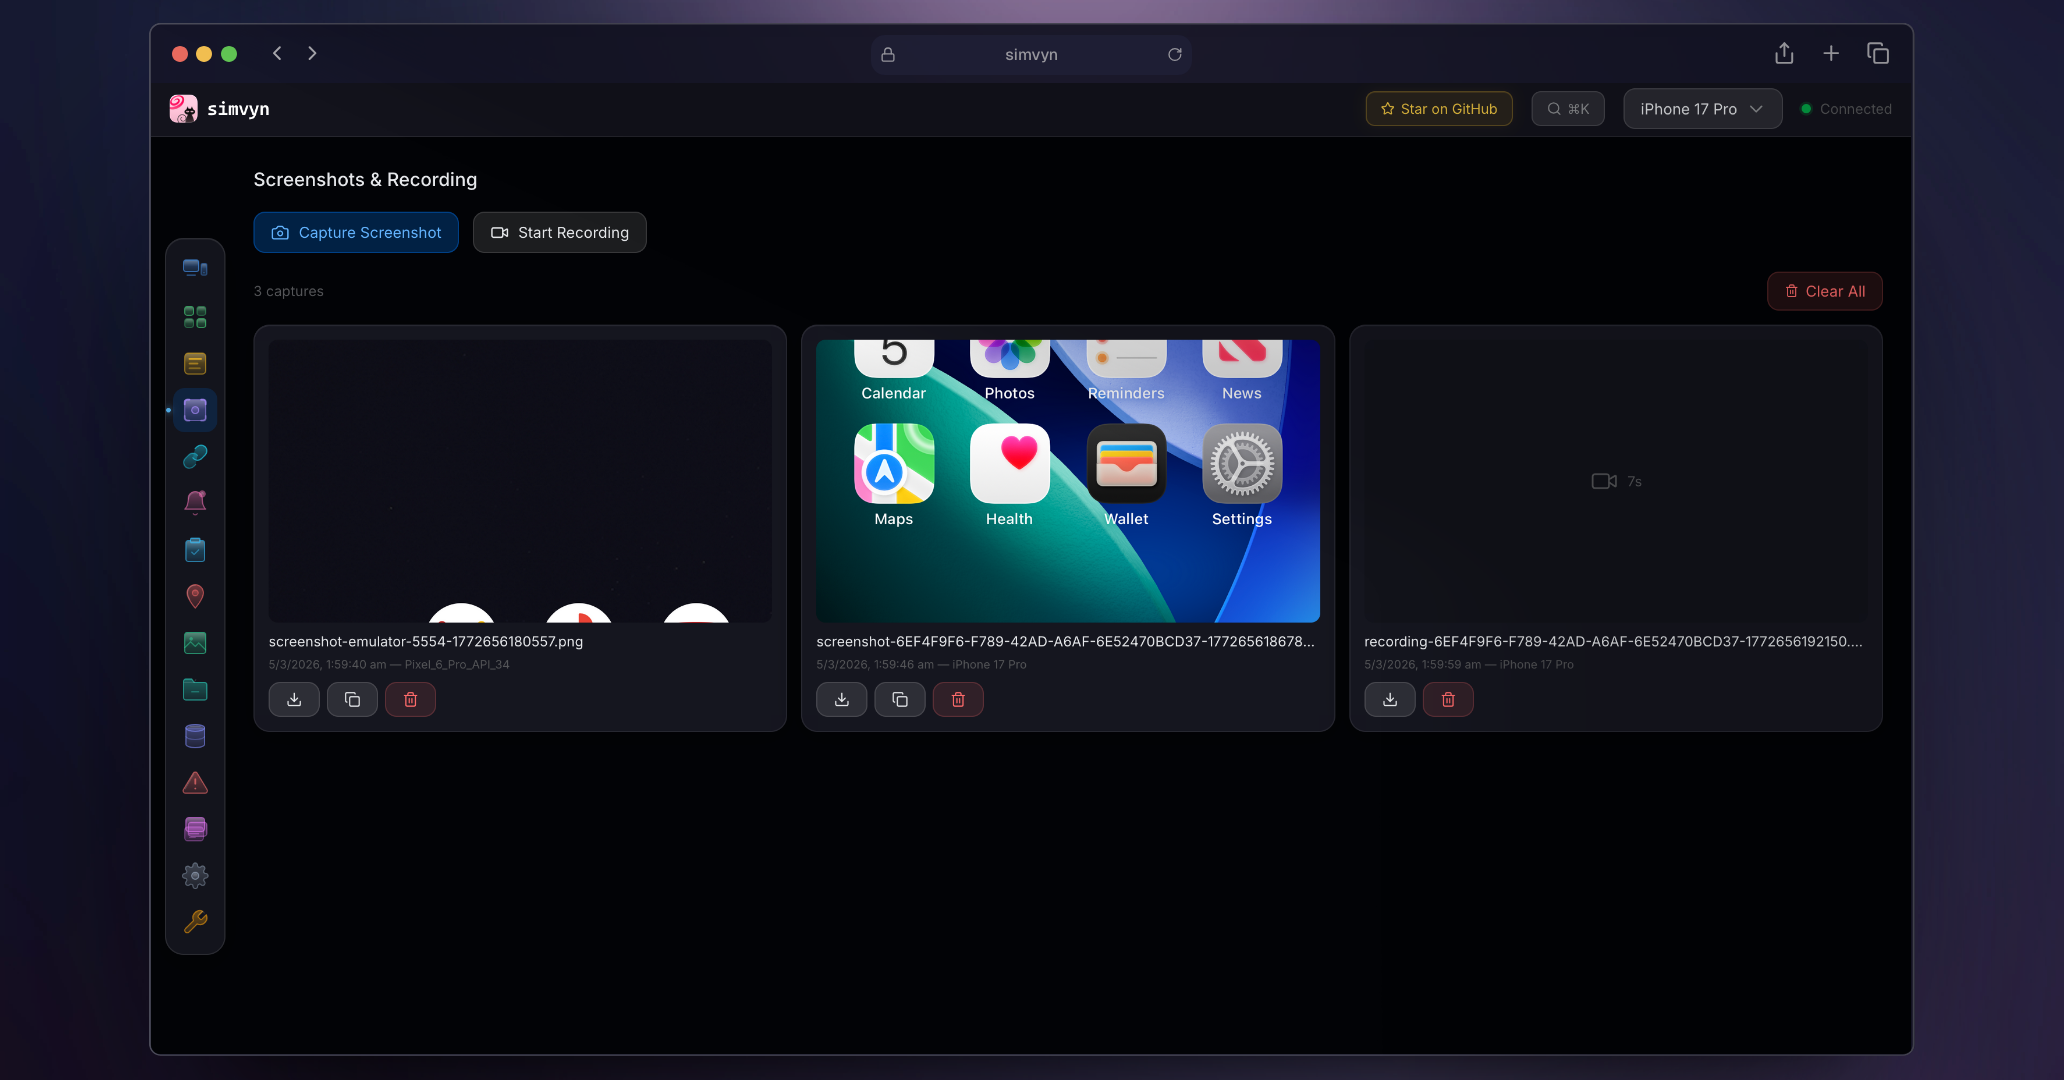 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
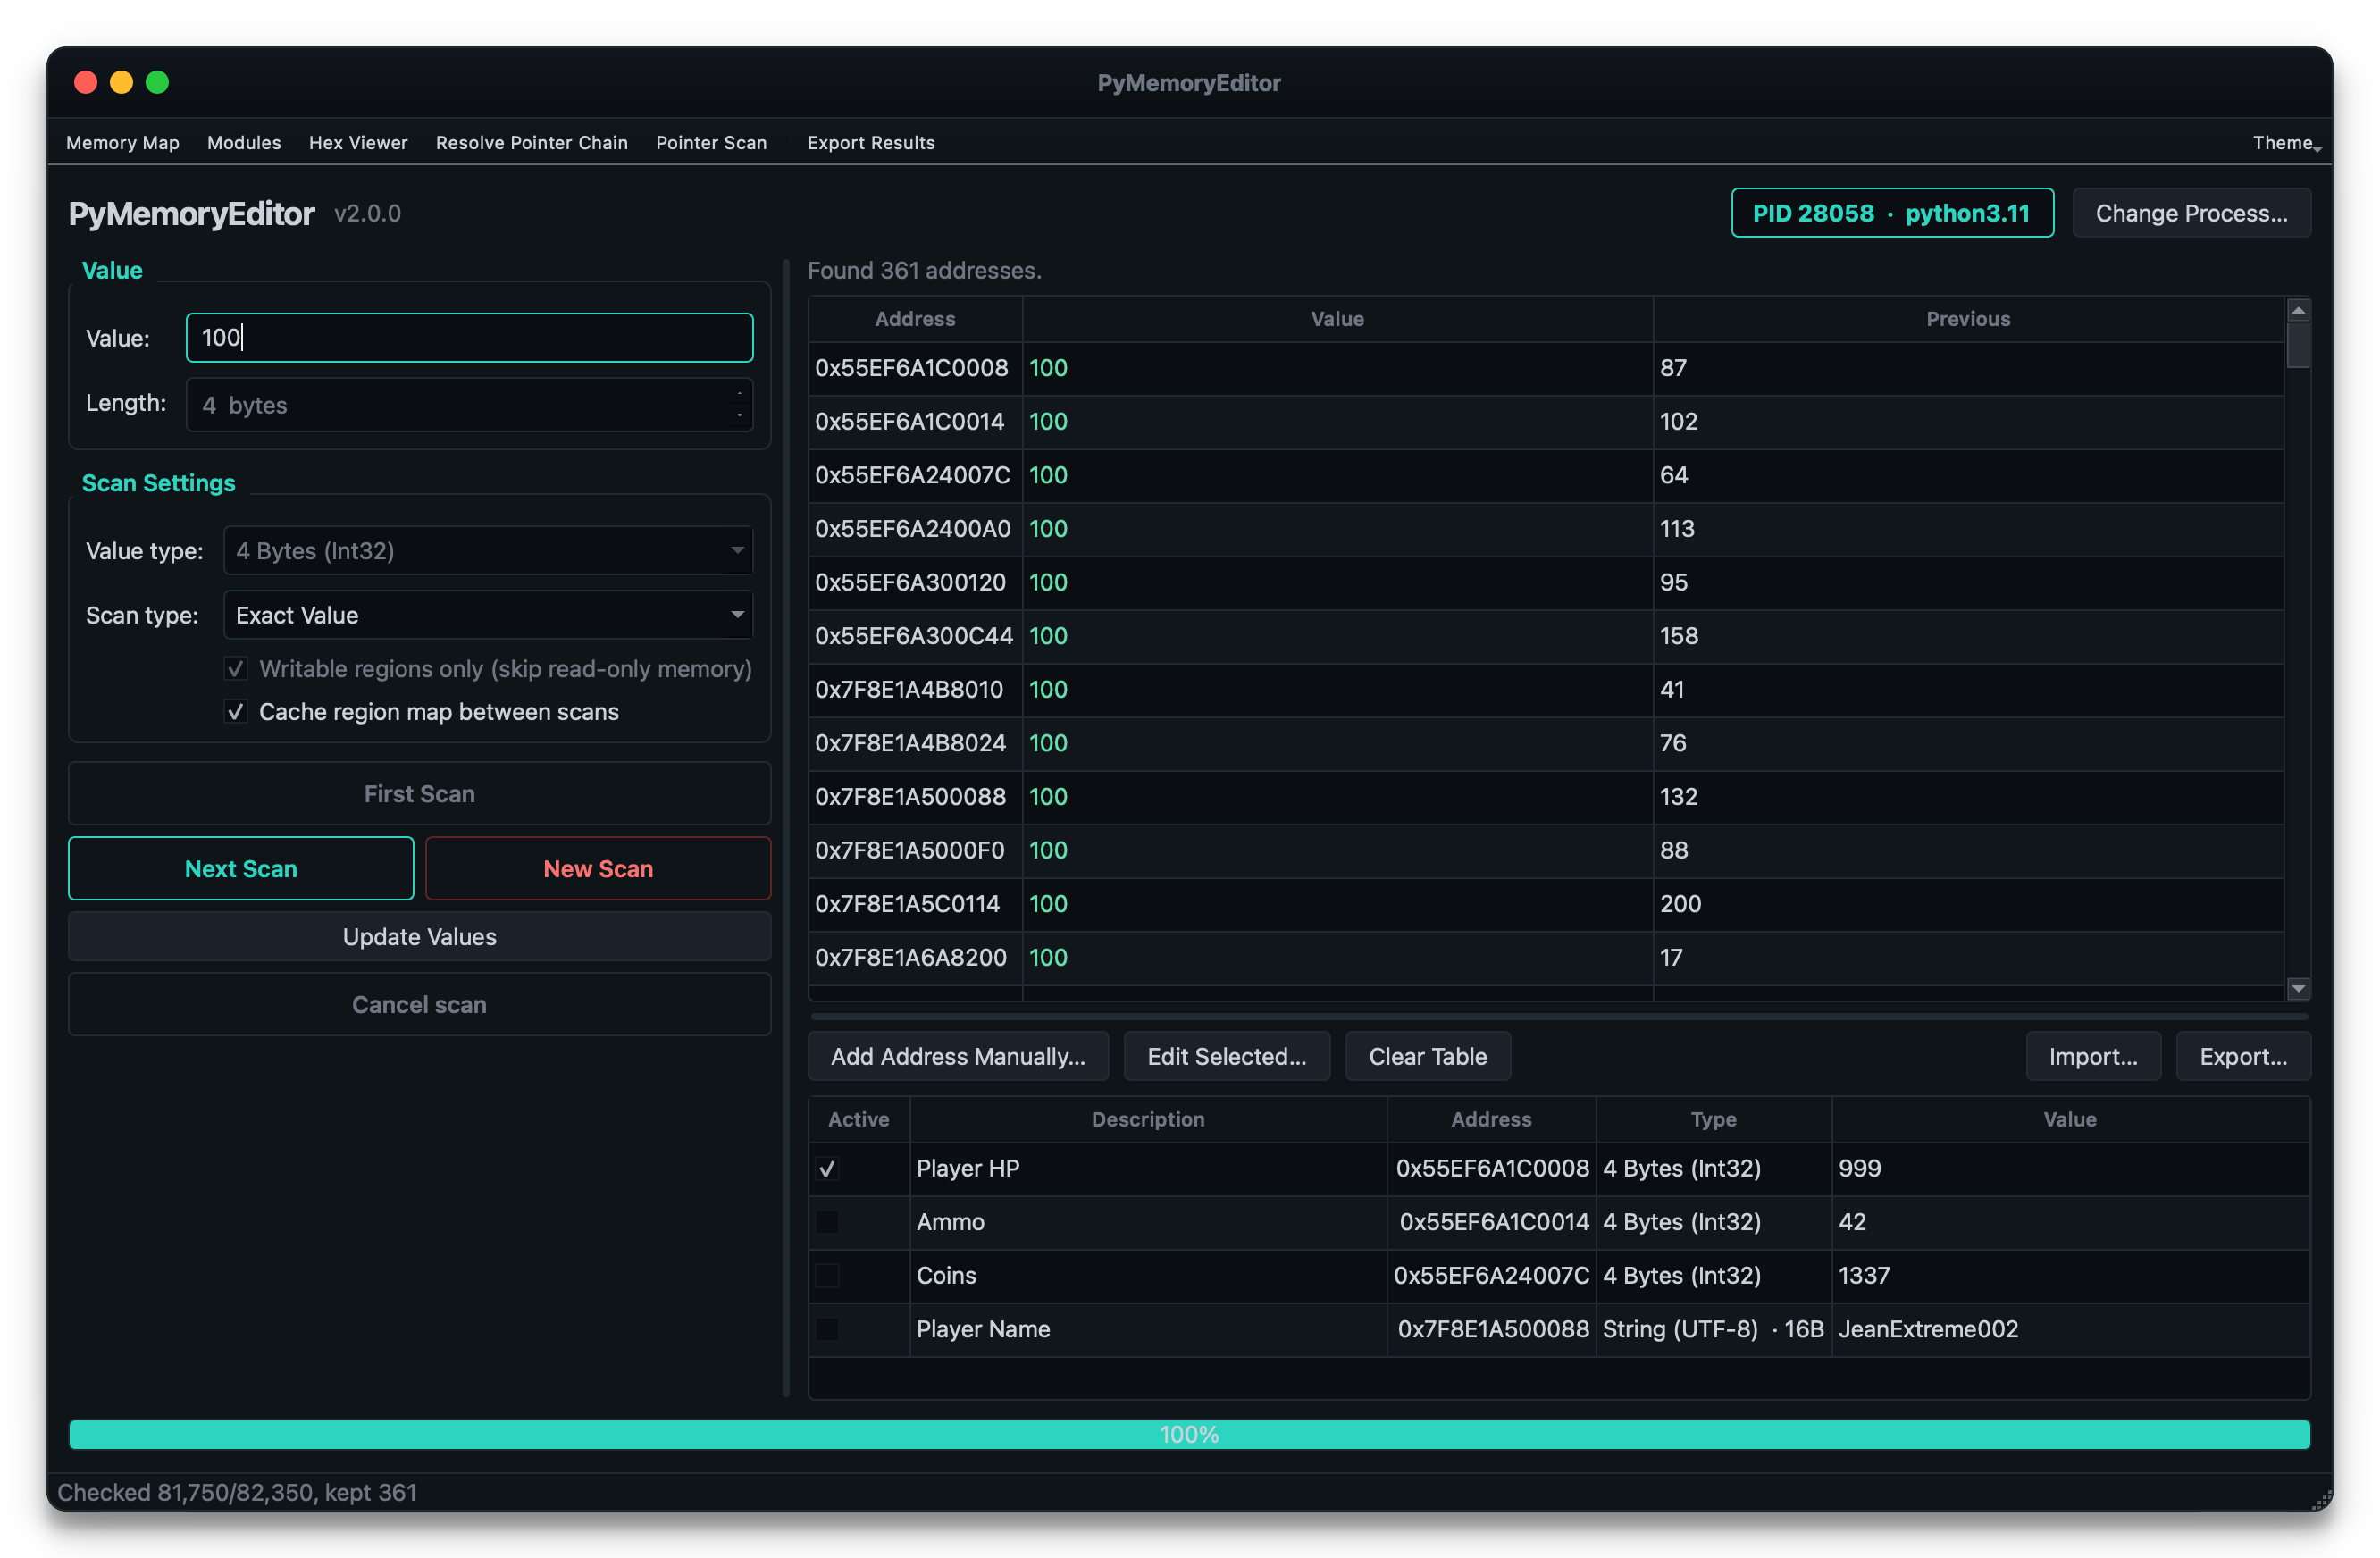 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .