
simvyn
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
android-securitydatabase-securitydebuggers+9
438
pranshuchittora/simvynUniversal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 daniellmcguire/xboxseries
Personal research into the Xbox Series Architecture
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
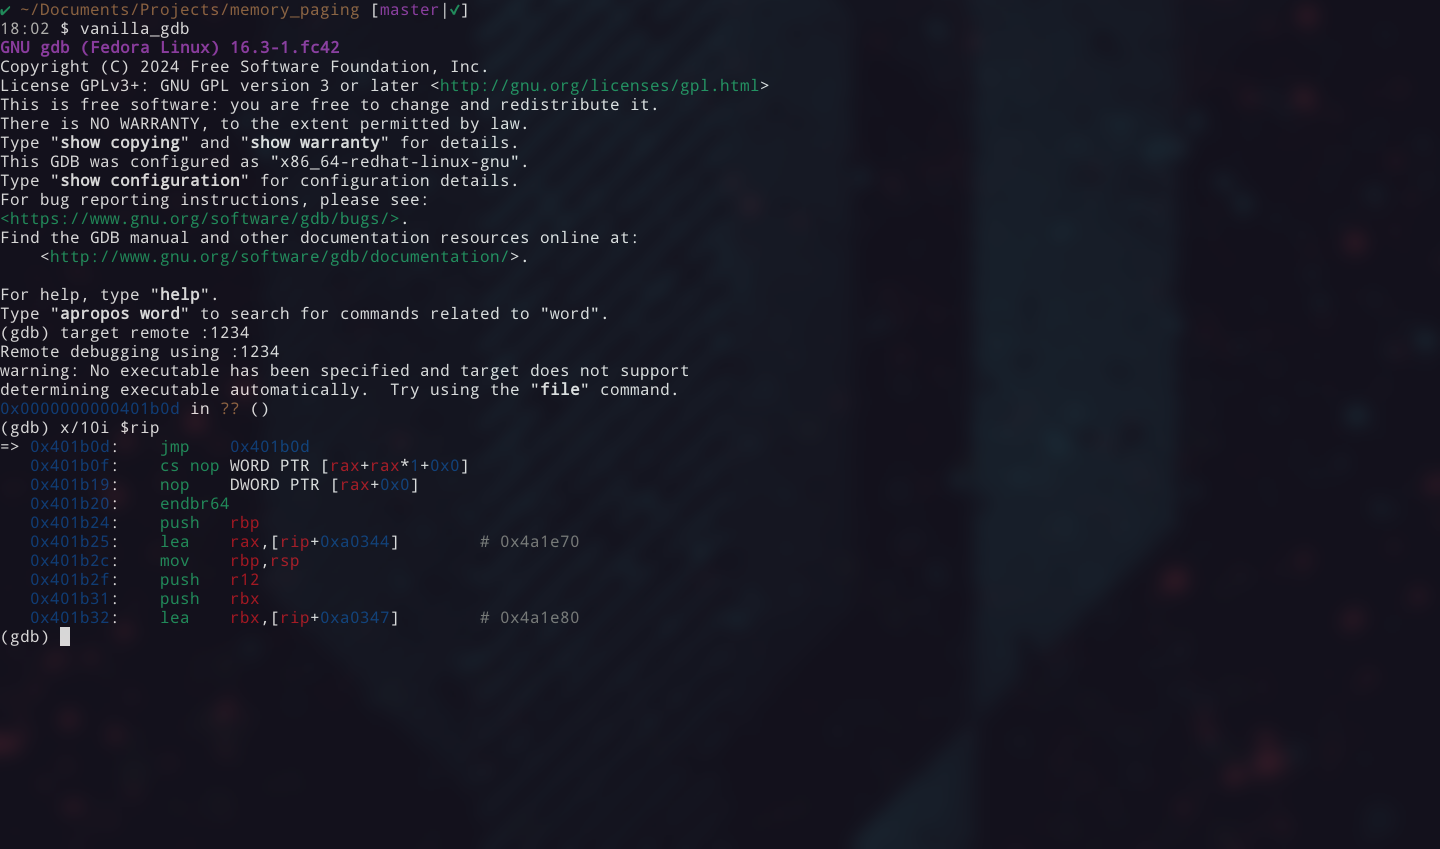 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
 cdacesec/cve-2022-31902
Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.