

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
34 results
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.3k
1 day ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
28 days ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
22610 days ago
CVE-2026-85048-the-gpu-died preview

CVE-2026-85048-the-gpu-died

GitHubsneakynachos/cve-2026-85048-the-gpu-died

Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…

binary-exploitationdebuggersexploitation+4
11 month ago
RESim preview

RESim

GitHubmfthomps/resim

Reverse engineering software using a full system simulator
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1951 month ago
TinyInst preview

TinyInst

GitHubgoogleprojectzero/tinyinst

A lightweight dynamic instrumentation library
binary-analysiscode-analysisdebuggers+3
1.4k1 month ago
cve-2026-62737-lab preview

cve-2026-62737-lab

GitHubdavidcarliez/cve-2026-62737-lab

Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
binary-exploitationdebuggersexploitation+2
22 months ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k3 months ago
ptrace preview

ptrace

GitHubwhatswrongandwhy/ptrace

Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.

binary-analysisdebuggersdynamic-code-analysis+2
3 months ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
253 months ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
204 months ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools

binary-analysisdebuggersgeneral-purpose-utilities+1
1.5k4 months ago
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

Dump cookies and credentials directly from Chrome/Edge process memory
data-exfiltrationdebuggersmemory-forensics+3
1.5k6 months ago
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

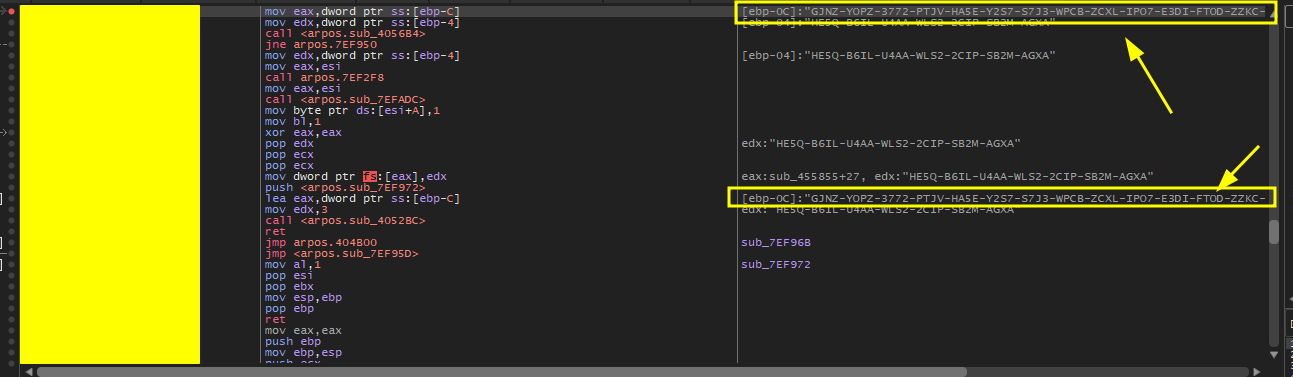
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
binary-analysisdebuggersexploitation+3
27 months ago
processhacker-mcp preview

processhacker-mcp

GitHubillegal-instruction-co/processhacker-mcp

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
debuggersdynamic-analysis-sandboxingexploitation+7
518 months ago
machscope preview

machscope

GitHubsadopc/machscope

All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.

binary-analysiscode-analysisctf+8
1038 months ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques

adversarial-attackdebuggersids-ips-evasion+6
9608 months ago
ComfyEngine preview

ComfyEngine

GitHubkashithecomfy/comfyengine

ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.

binary-analysisdebuggersdynamic-code-analysis+5
6110 months ago
Previous12Next