

r2frida
 nowsecure/r2frida
Radare2 and Frida better together.
android-securitybinary-analysisdebuggers+8
nowsecure/r2fridaRadare2 and Frida better together.

 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
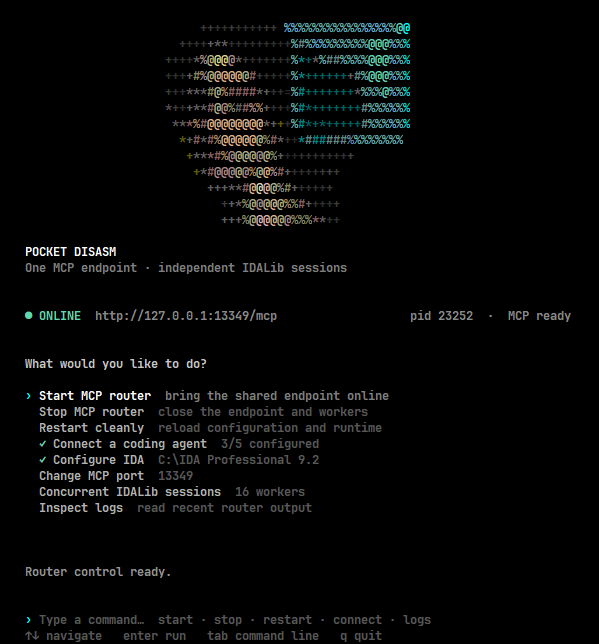 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
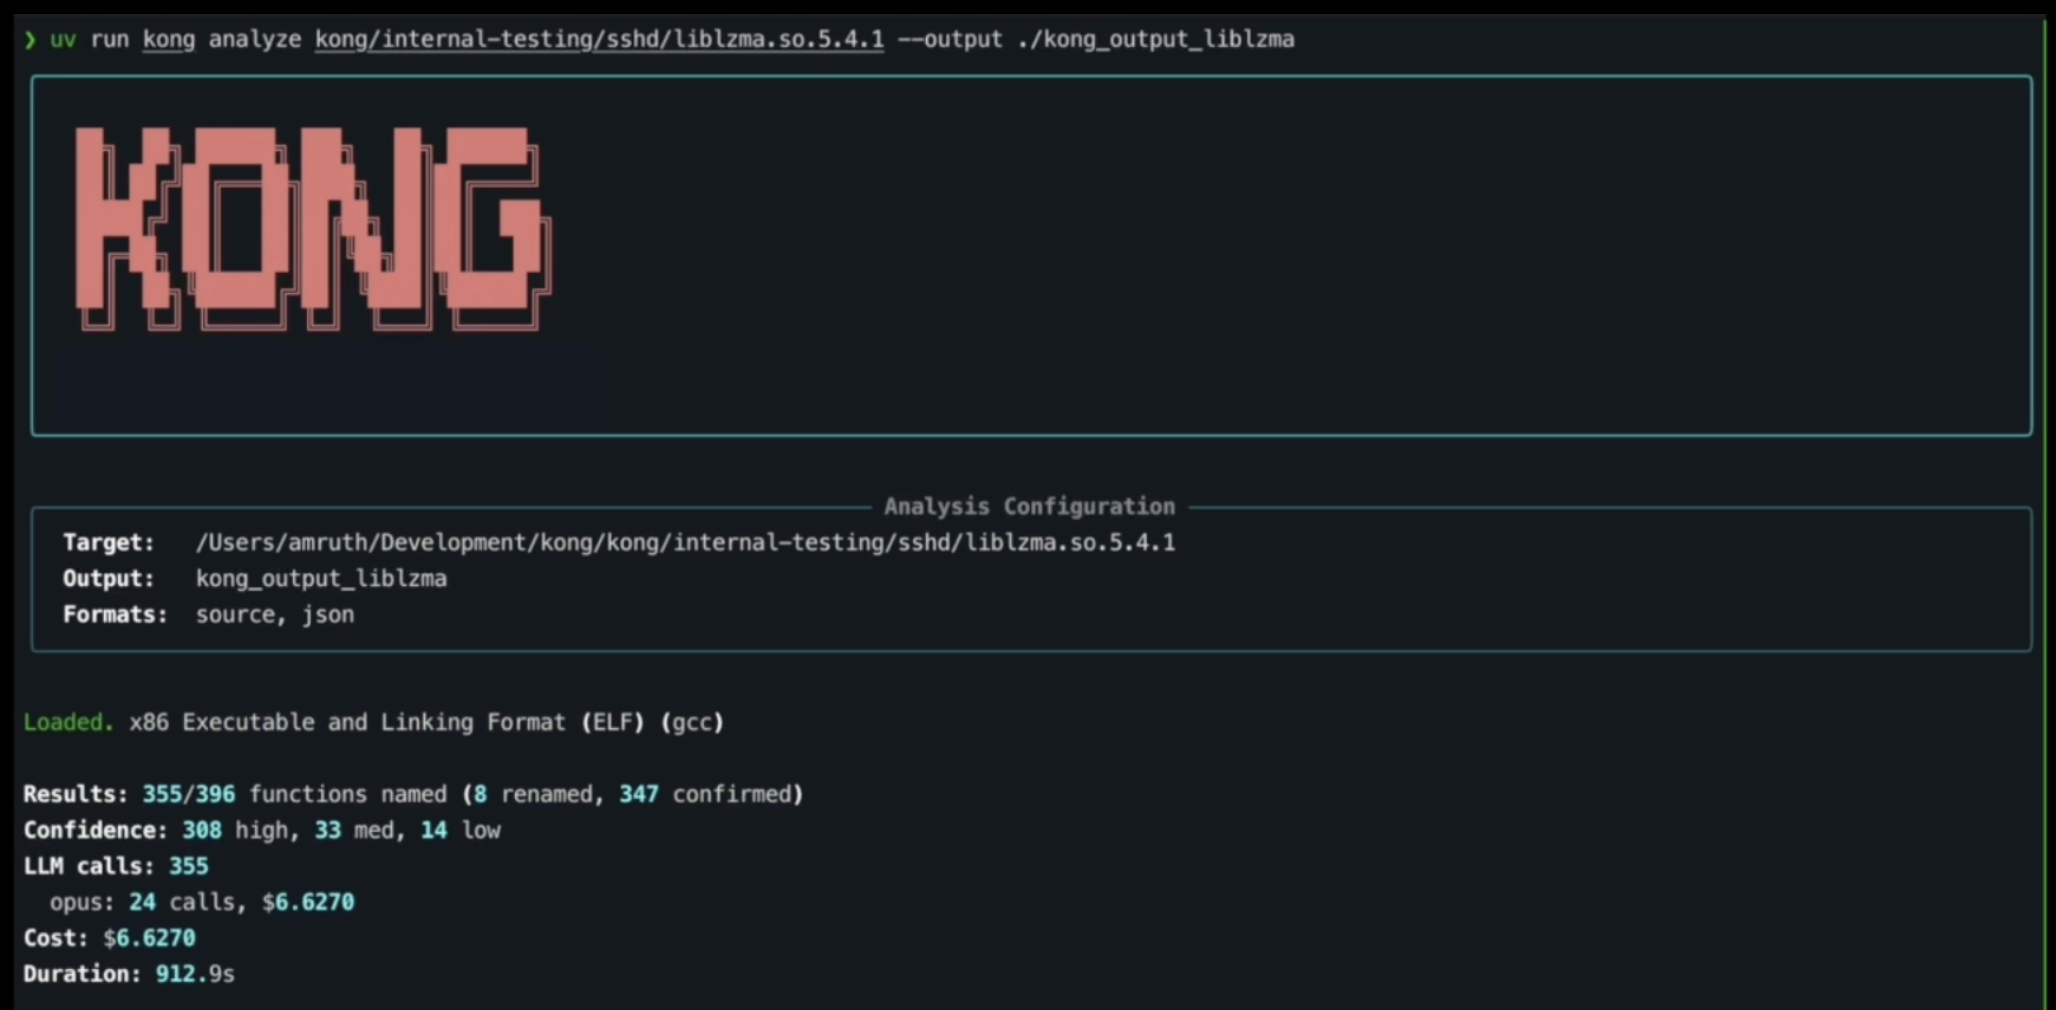 amruth-sn/kong
The world's first agentic reverse engineer.
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.