
CVE-2023-52356-libtiff-analysis
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
binary-analysisdebuggerseducation+2
yardenbenita/cve-2023-52356-libtiff-analysisRoot-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
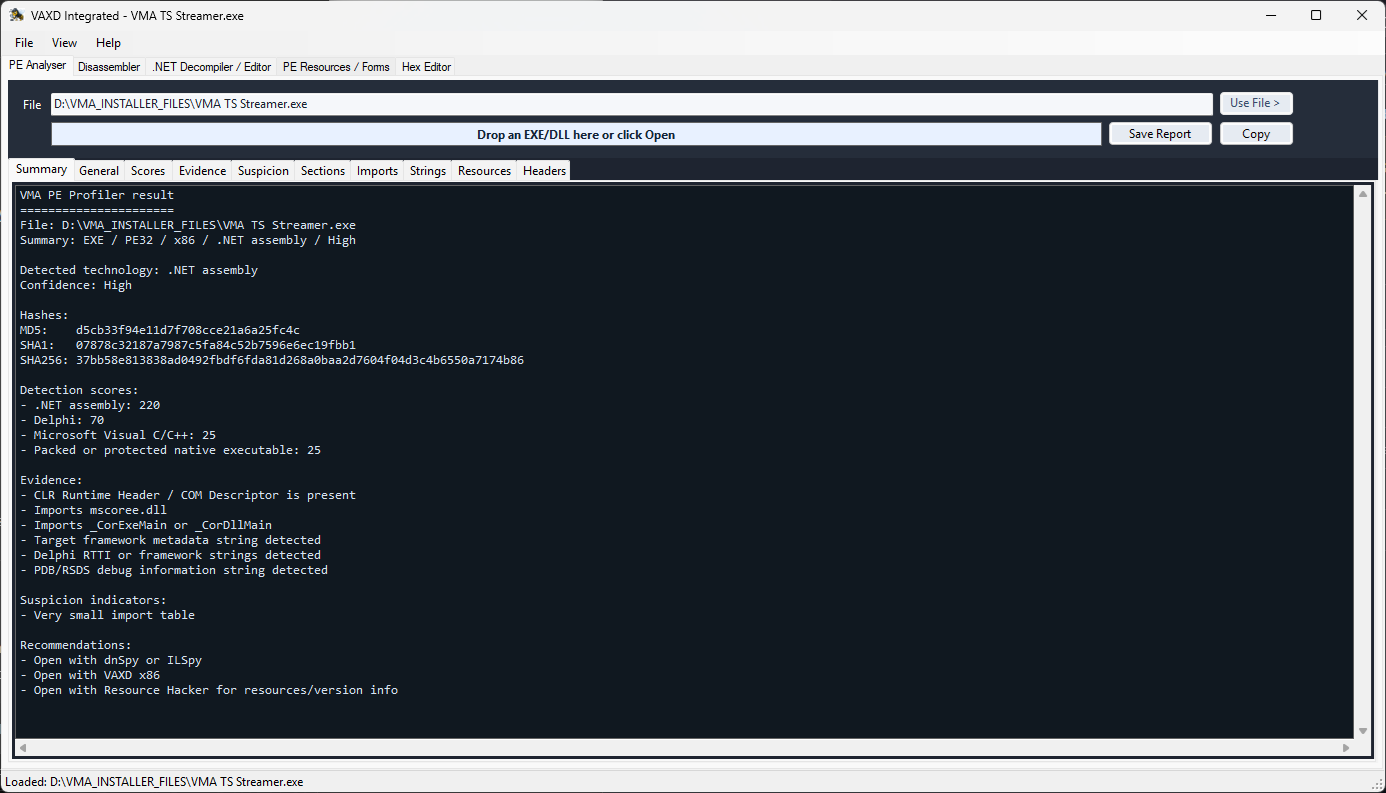 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
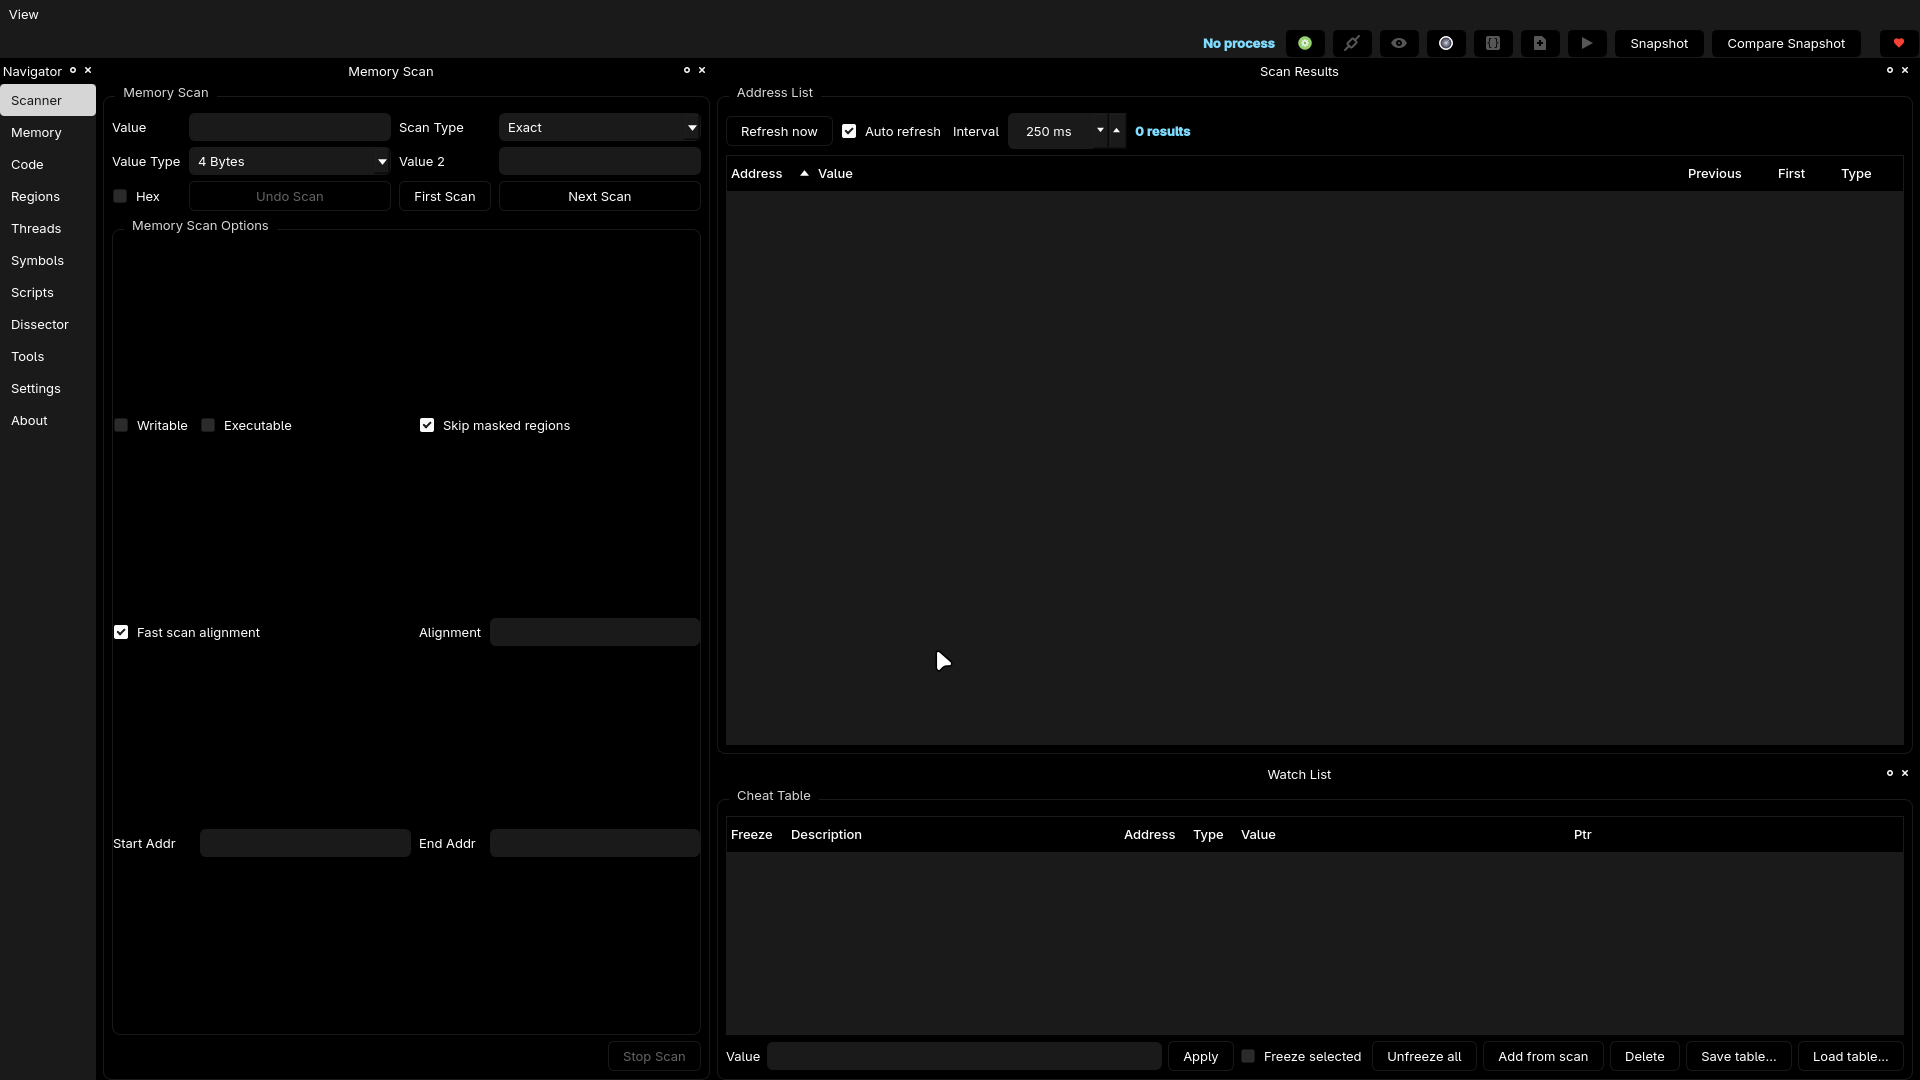 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…