

TangledWinExec
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
daem0nc0re/tangledwinexecPoCs and tools for investigation of Windows process execution techniques
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
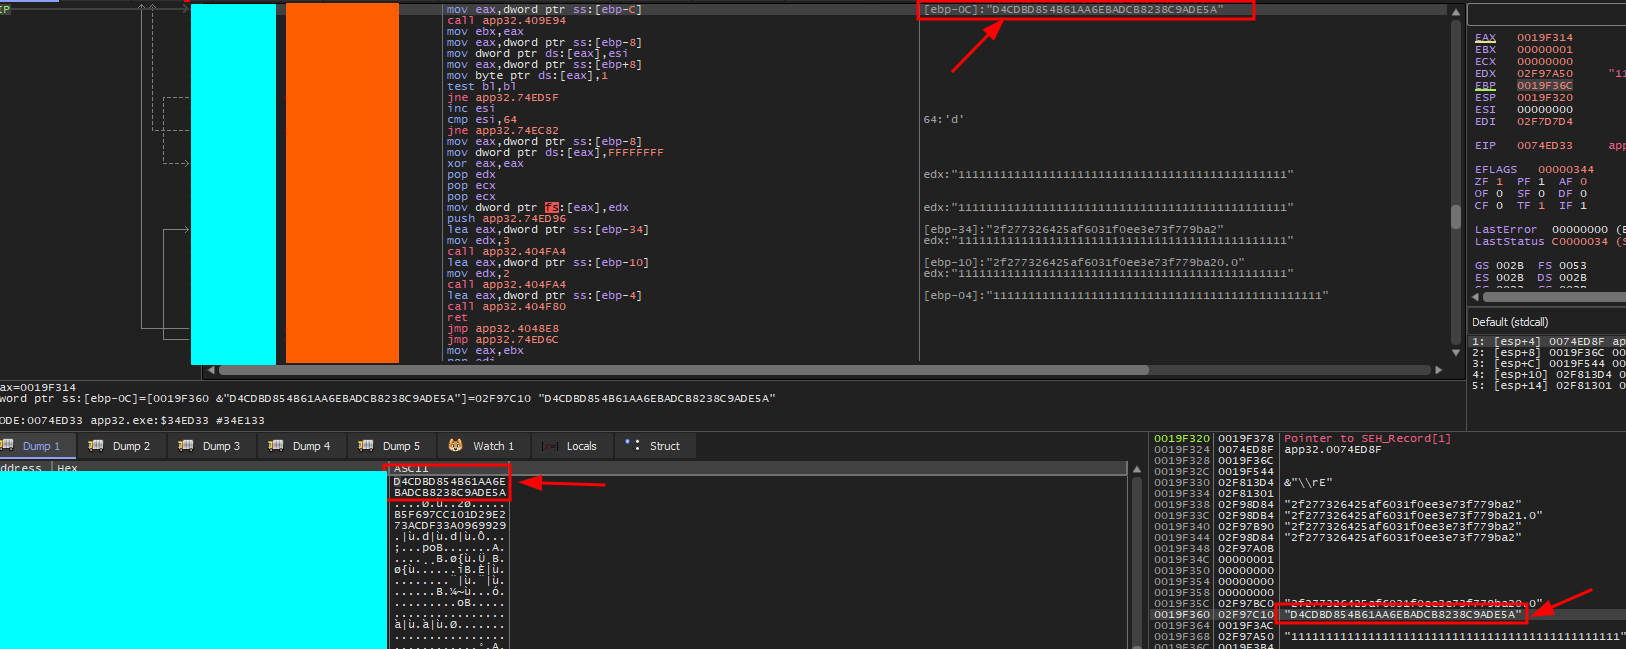 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
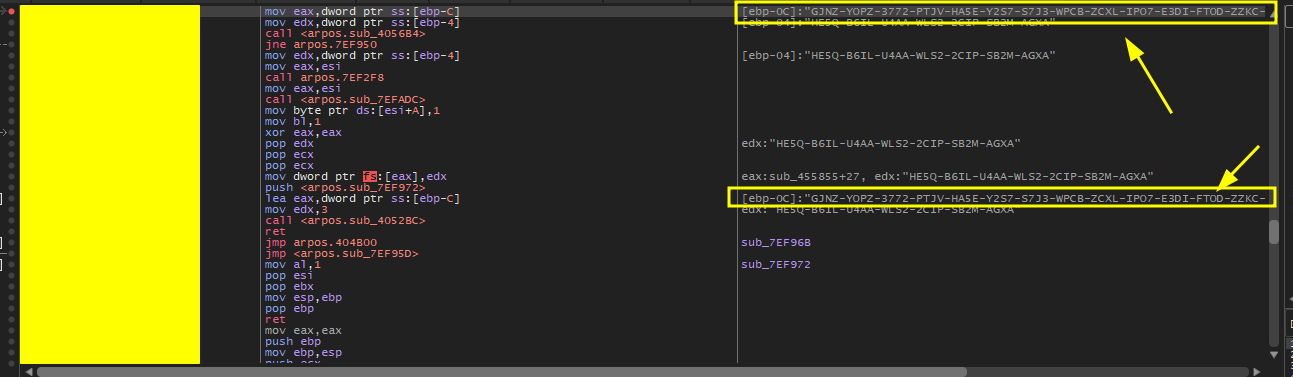 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
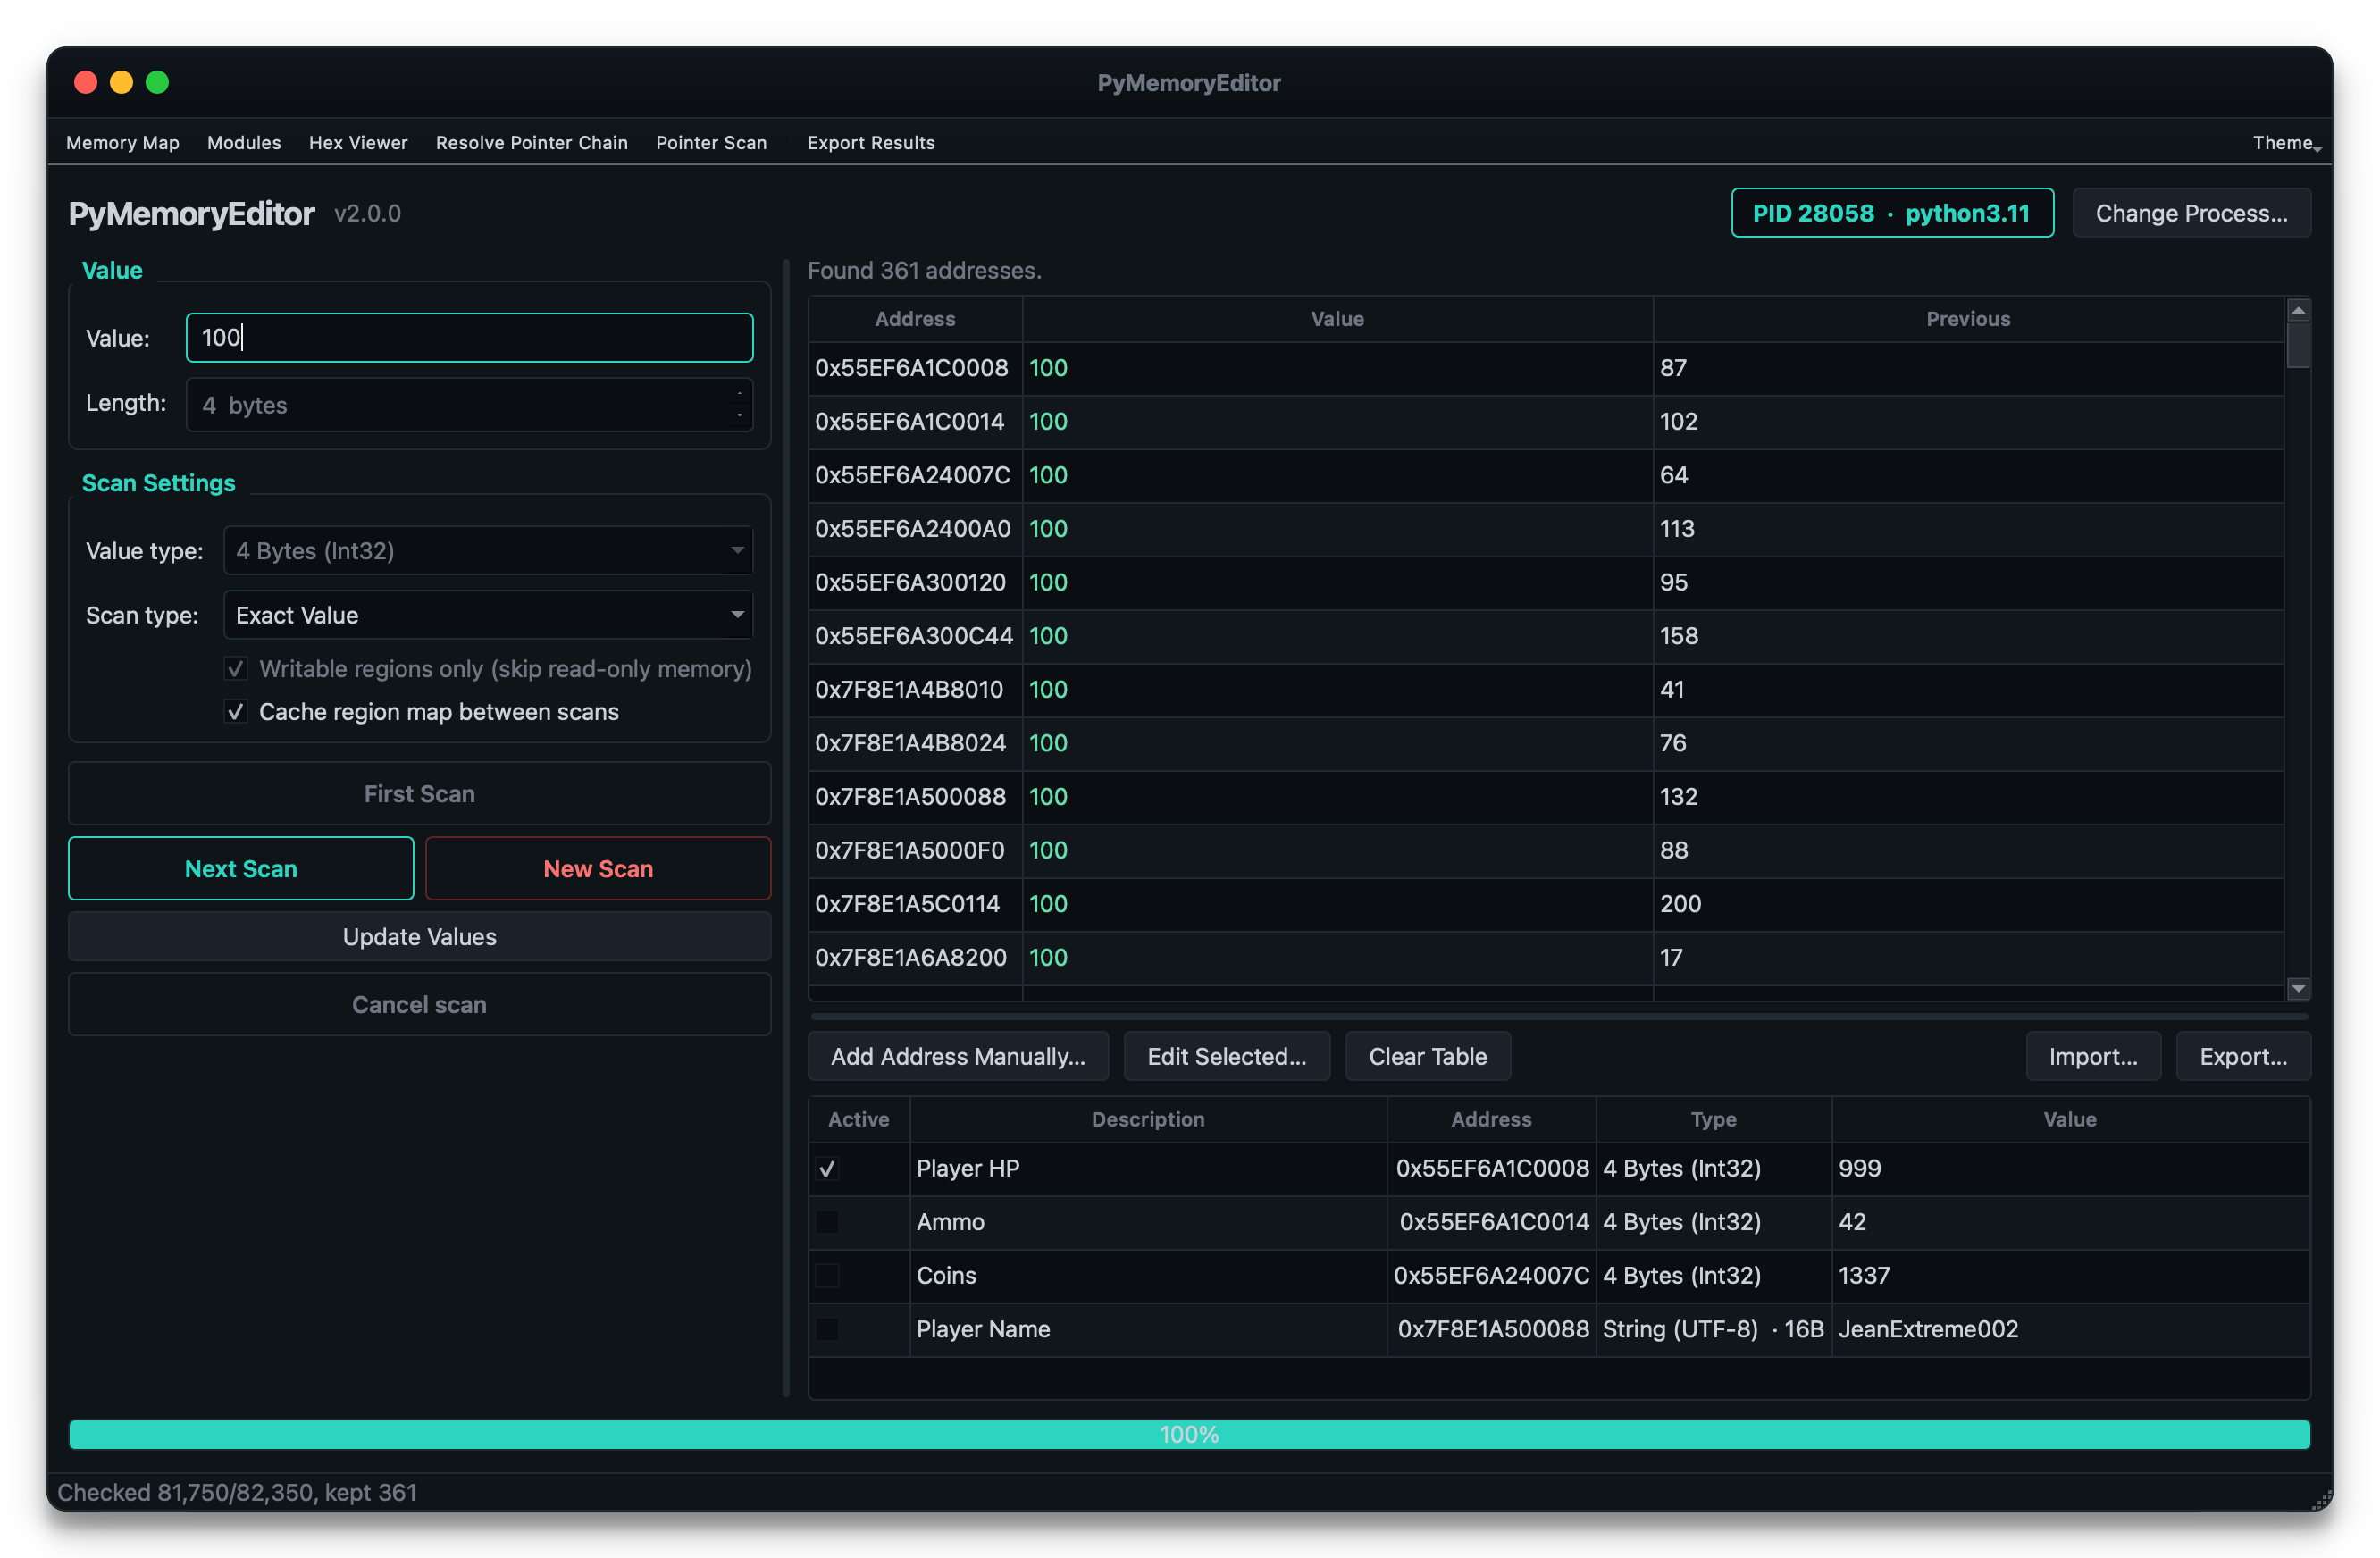 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
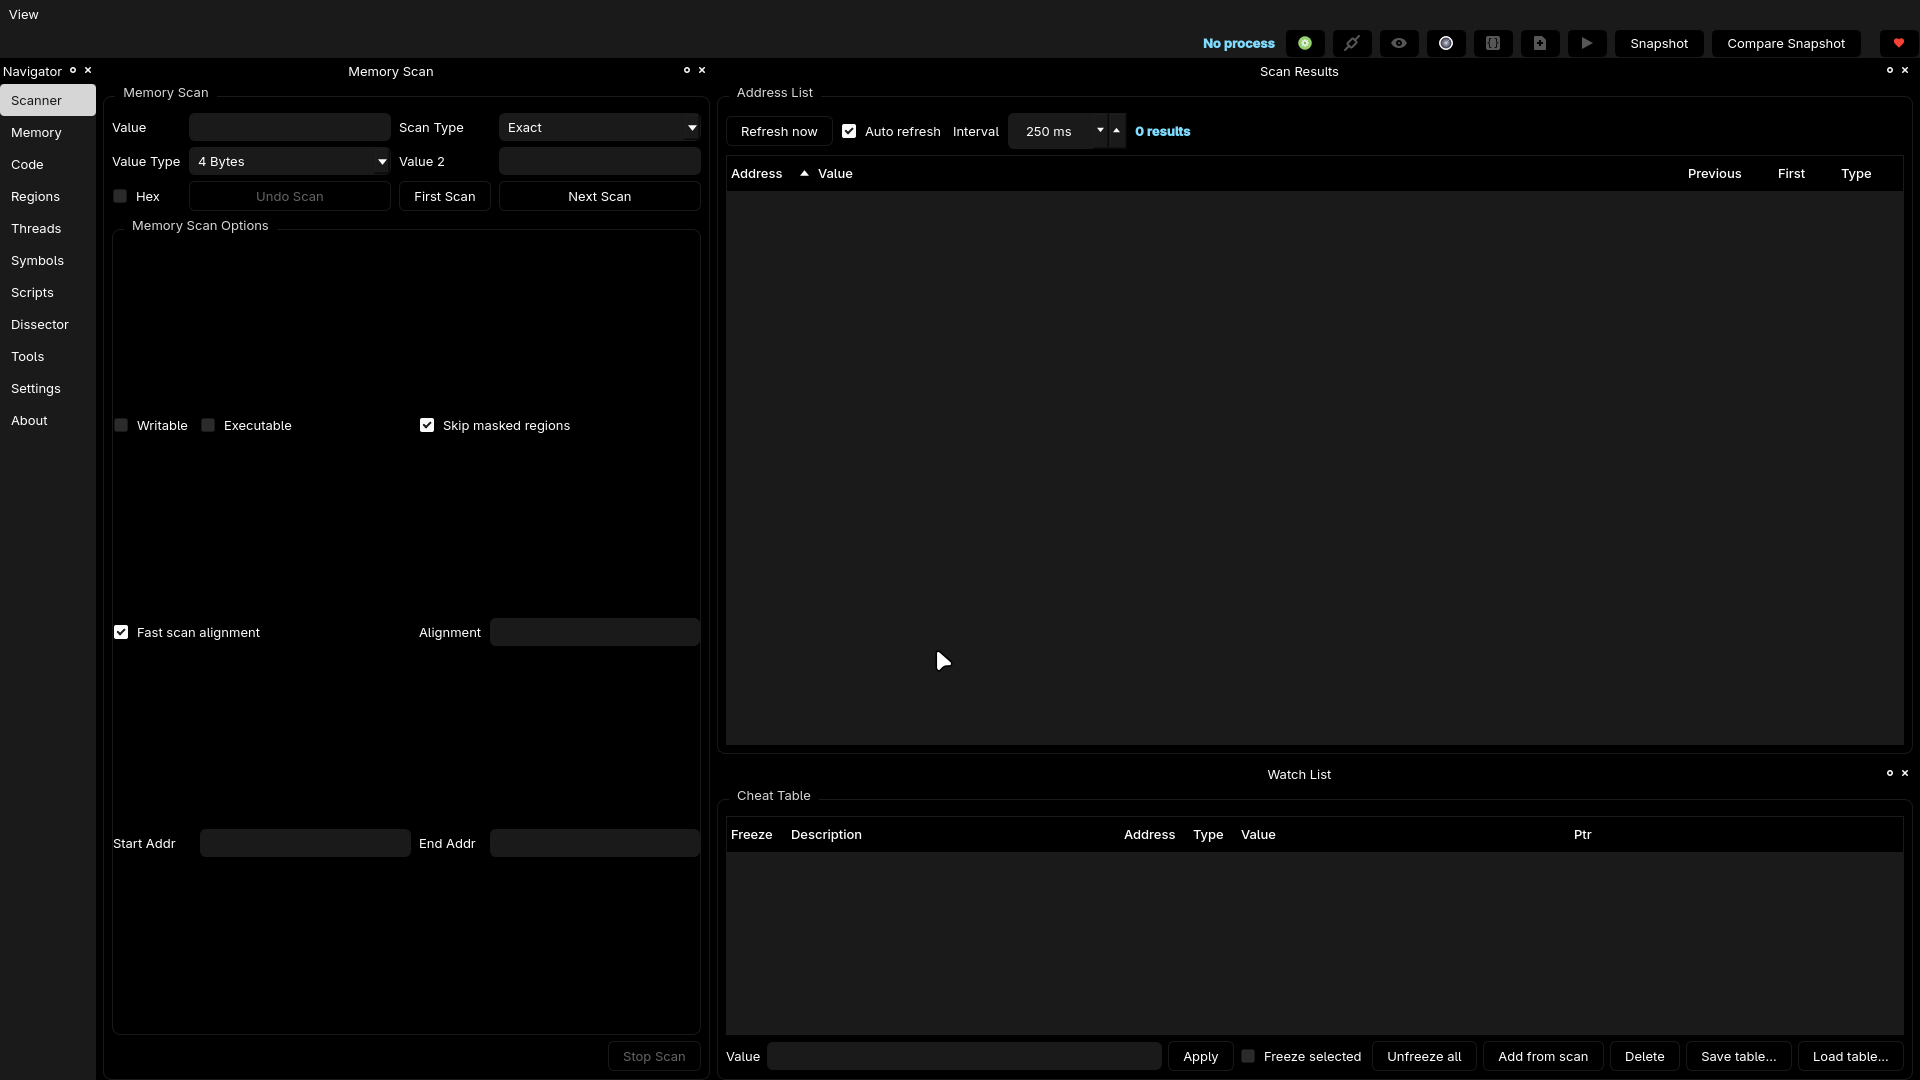 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 zodiacon/alltools
All reasonably stable tools
 0xnobody/vmpdump
A dynamic VMP dumper and import fixer, powered by VTIL.