
JADXecute
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
android-securitycode-analysisdebuggers+6
lauriewired/jadxecuteJADX-gui scripting plugin for dynamic decompiler manipulation
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
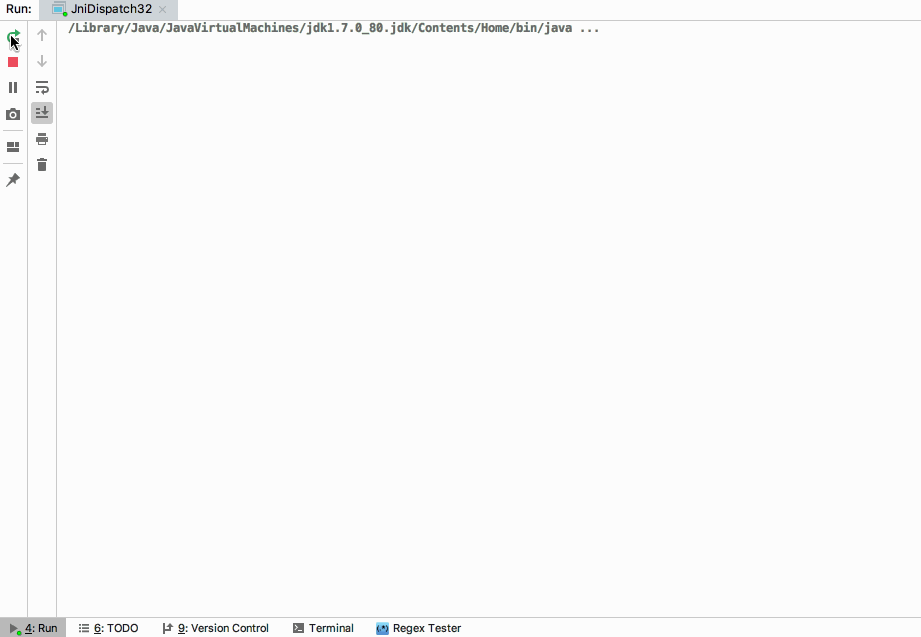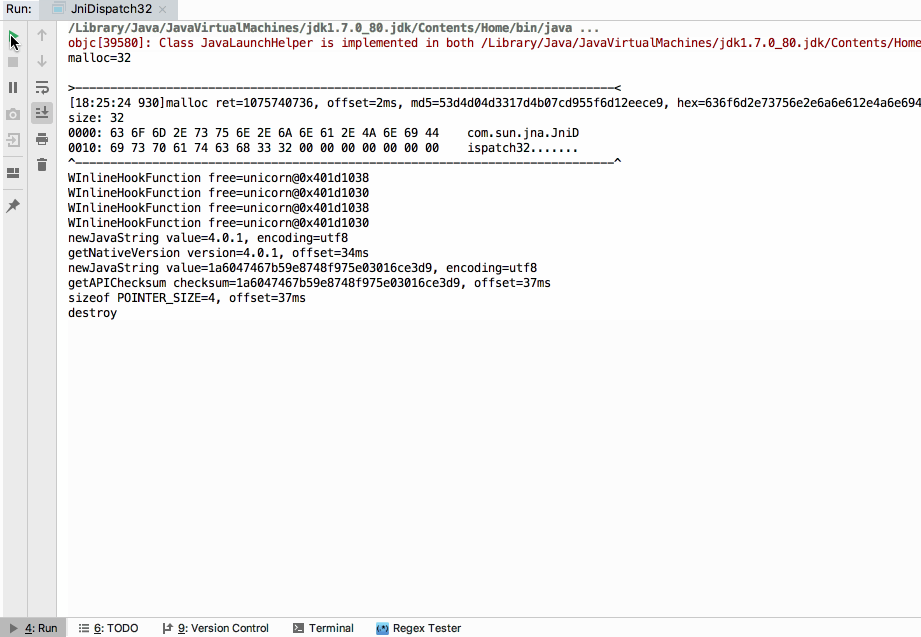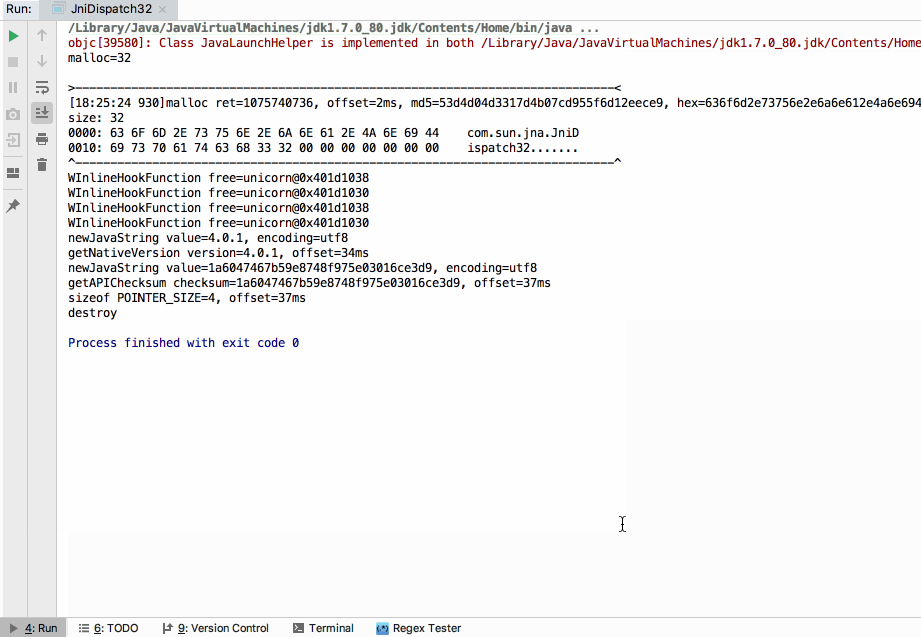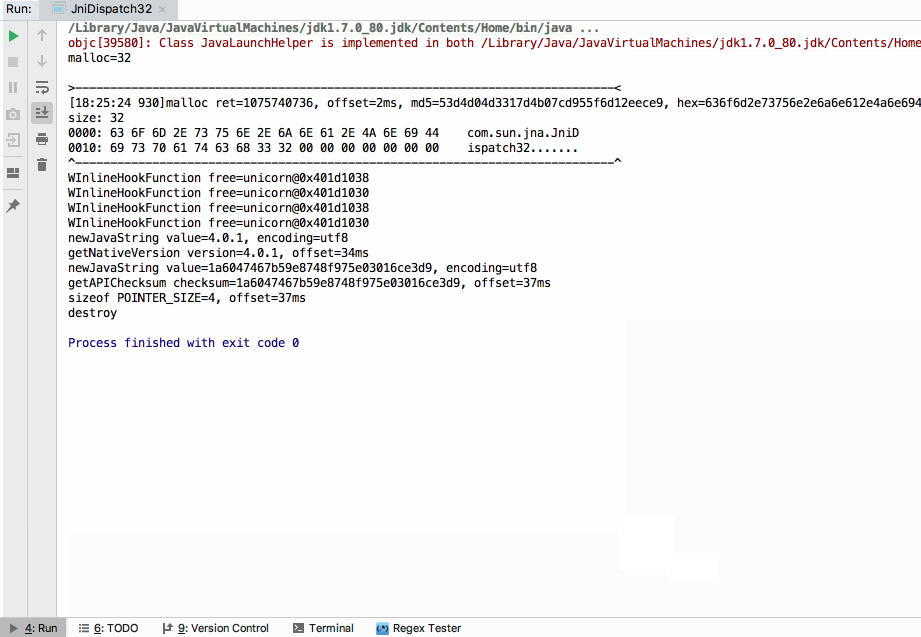 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
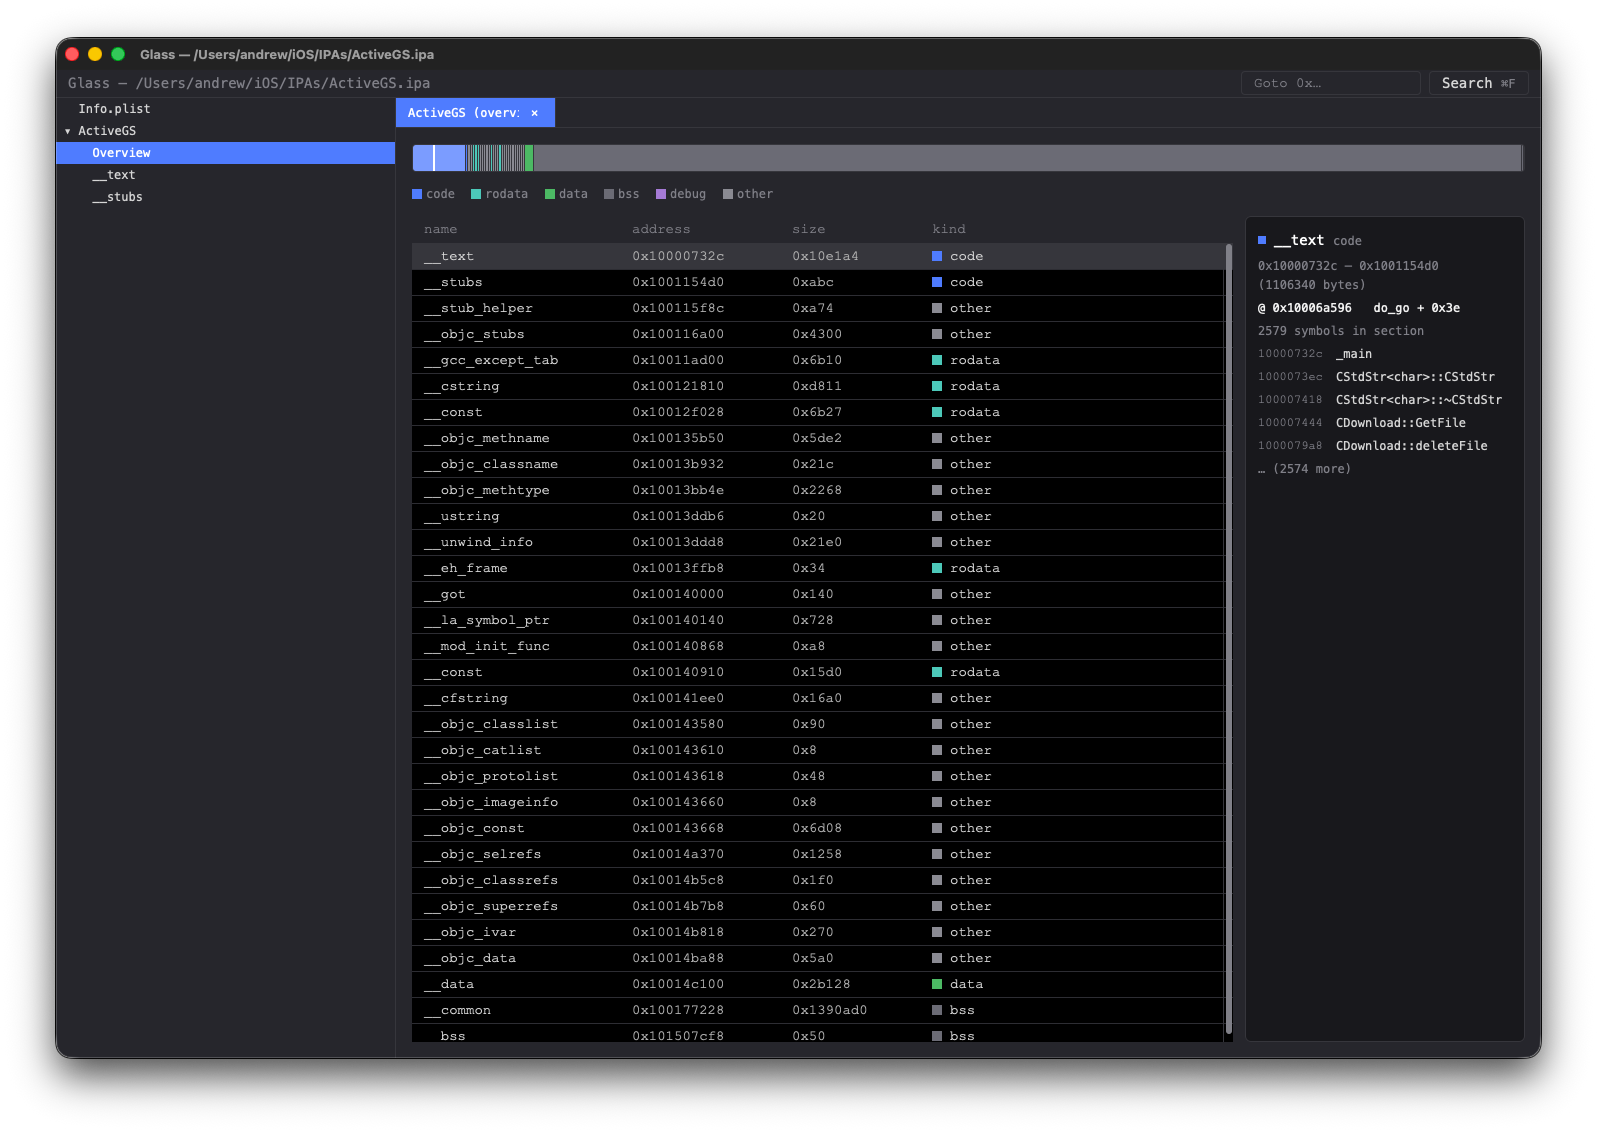 azw413/glass
Glass - a fast and free IDA Pro alternative
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 ilgobbo00/cve-2023-6241-pixel7_adaptation
Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…