
super-trouper
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
android-securitybinary-analysisdebuggers+5
4
crissyfield/super-trouperMCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
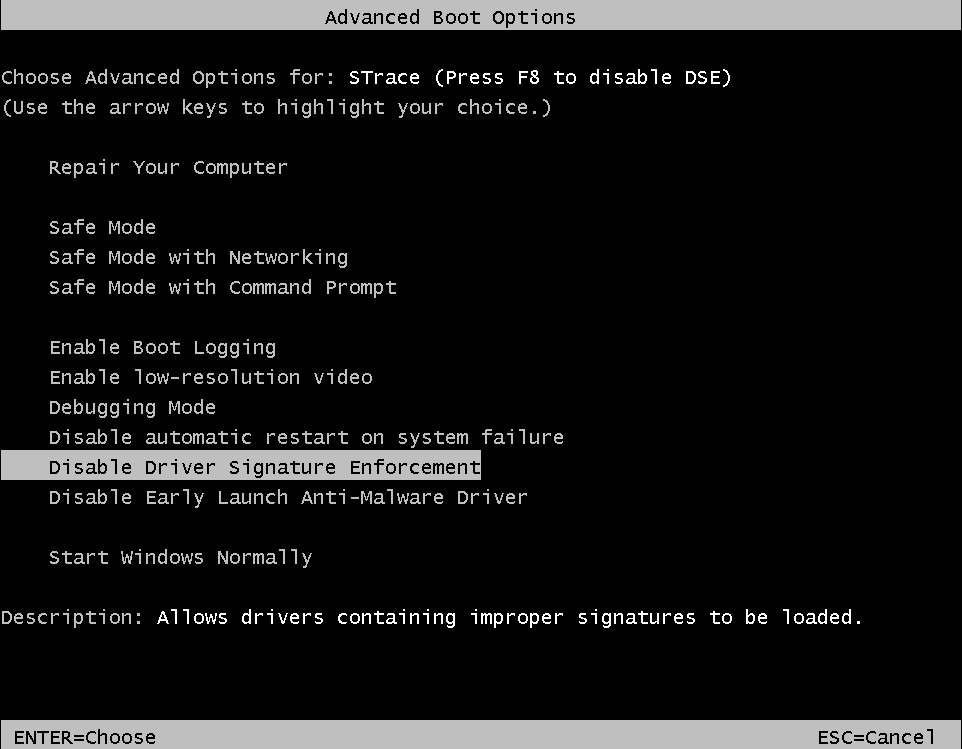 mandiant/strace
A DTrace on Windows Reimplementation
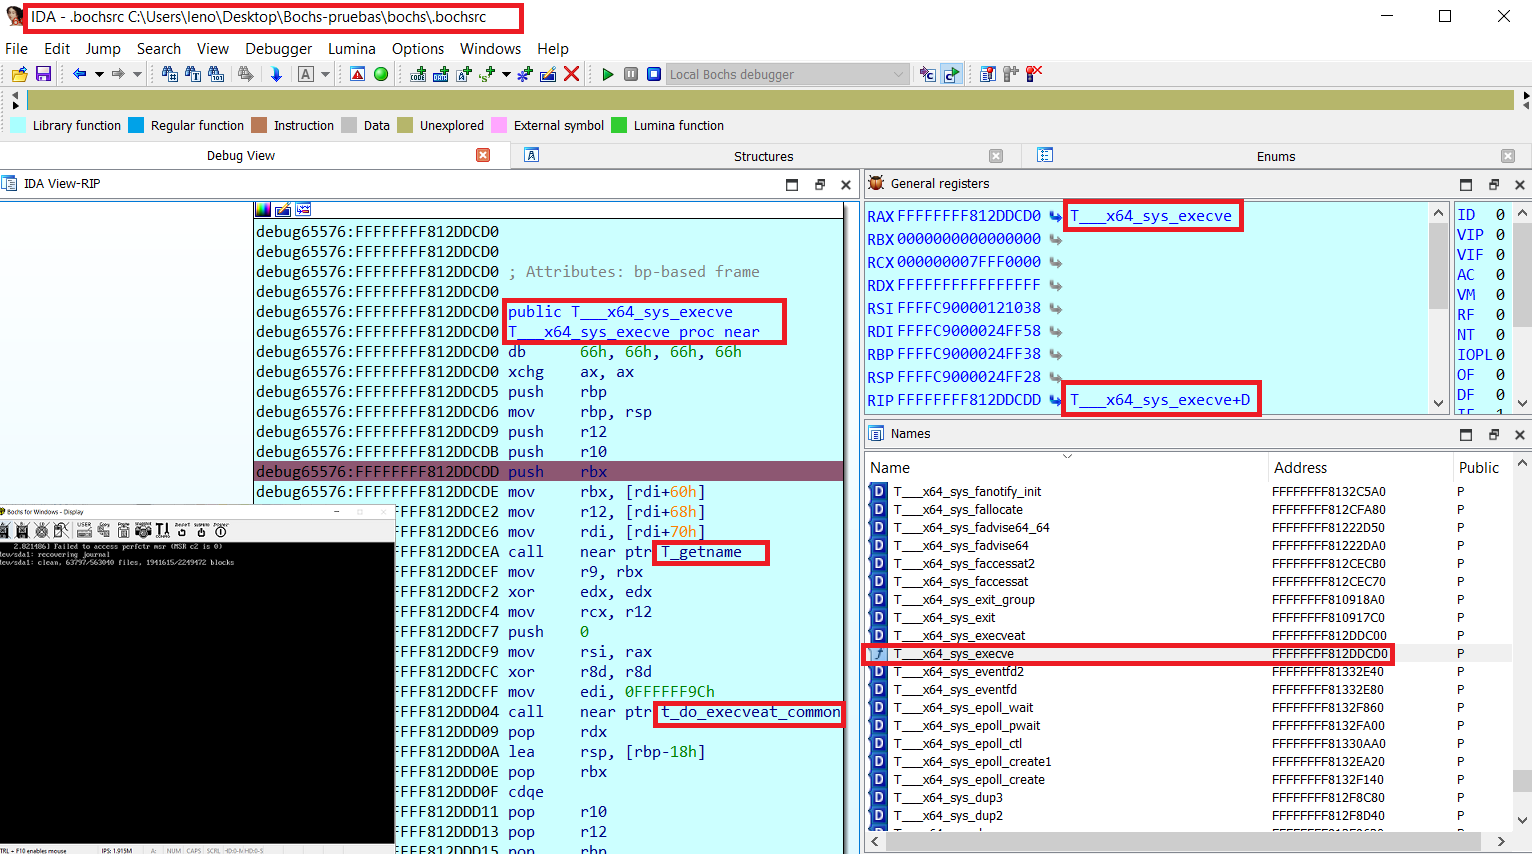 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 chichou/vscode-frida
Unofficial frida extension for VSCode
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation


 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
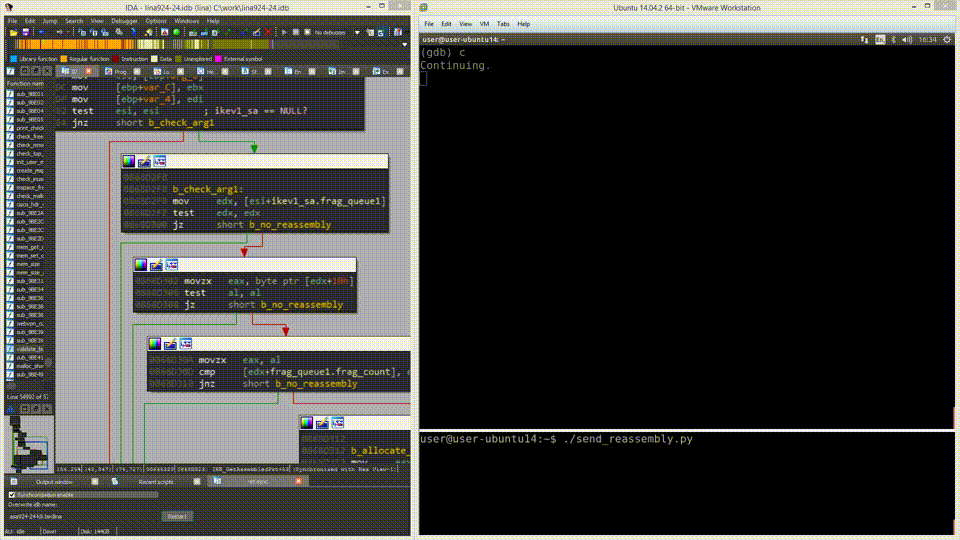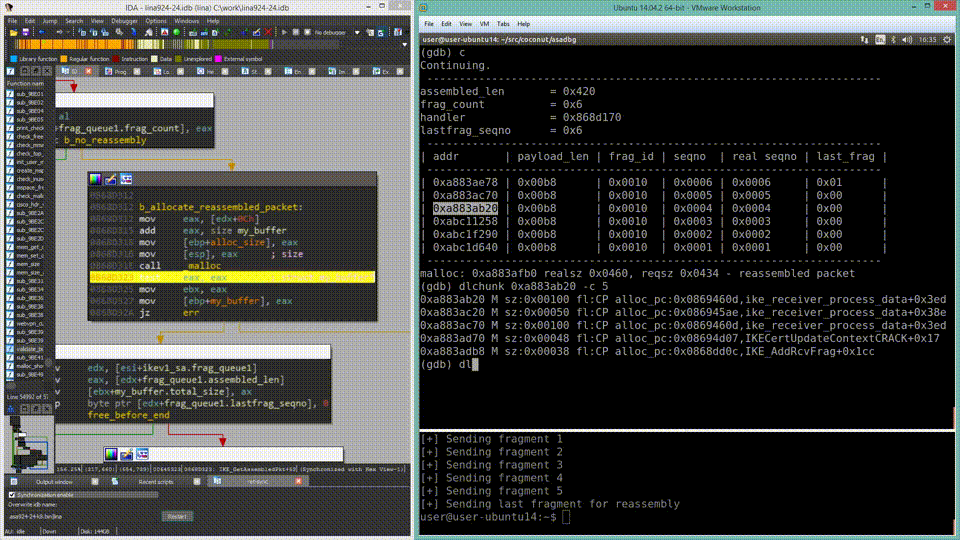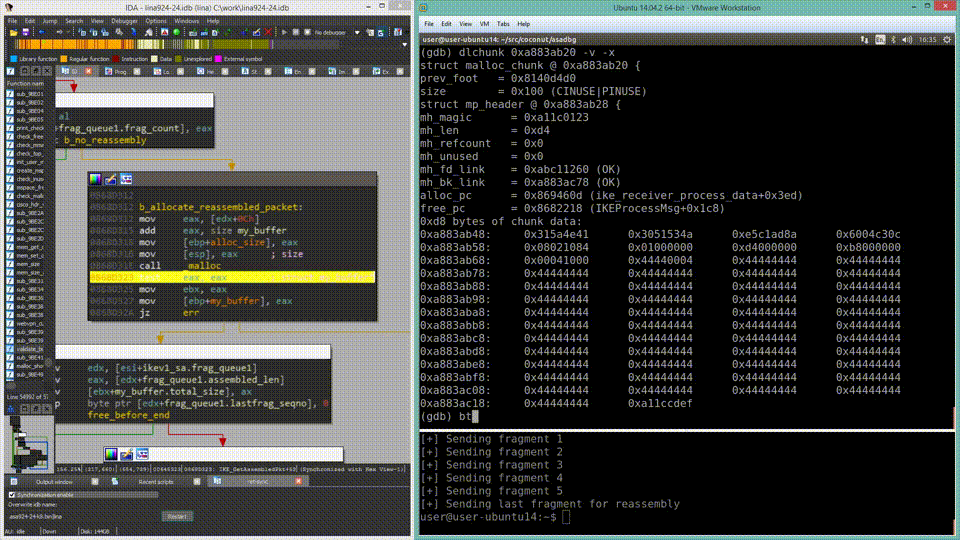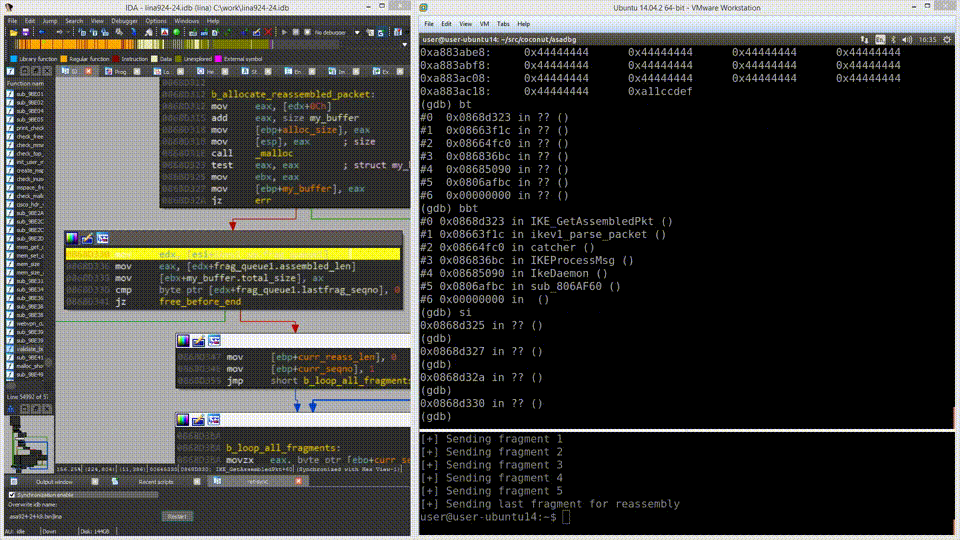 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.