

bba
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
android-securitybinary-analysisdebuggers+7
28
openbba0/bbaAndroid app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
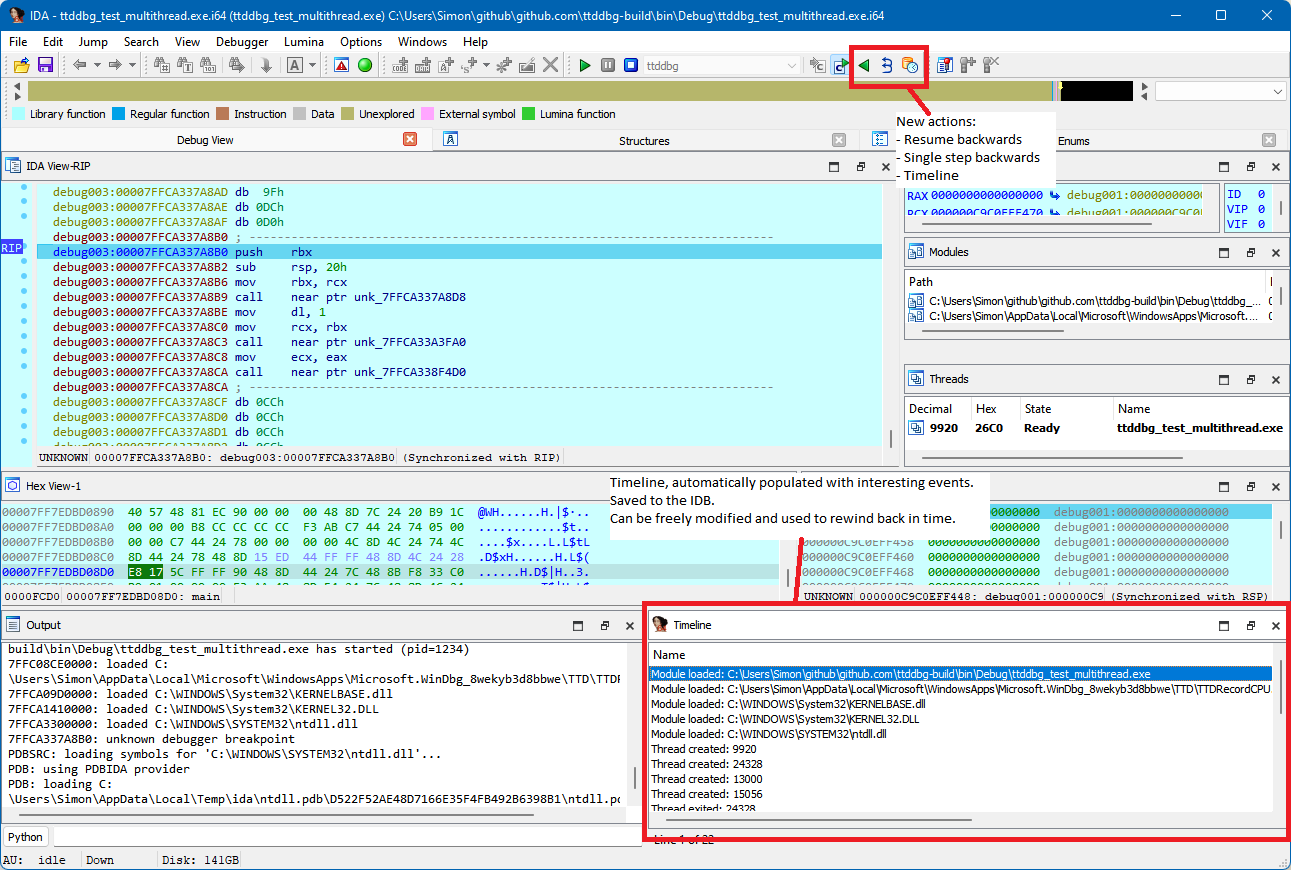 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 xalicex/kernel-debug-lab-for-virtual-box
How to set up 2 VirtualBox VM to debug kernel driver using windbg
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 malwaretech/basichook
x86 Inline hooking engine (using trampolines)
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 jackdoe/pico2-swd-riscv
SWD debug probe library for RP2350 RISC-V cores. Provides halt/resume/step, register and memory access, code execution, and instruction tracing over…
 k3vinlusec/whatsapp-double-free-vulnerability_cve-2019-11932
Step-by-step exploit analysis of WhatsApp's CVE-2019-11932 double-free vulnerability using GEF-GDB debugger for dynamic debugging and arbitrary code…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…