
jdwp-shellifier
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
debuggersexploitationmisconfiguration+1
919
ioactive/jdwp-shellifierExploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
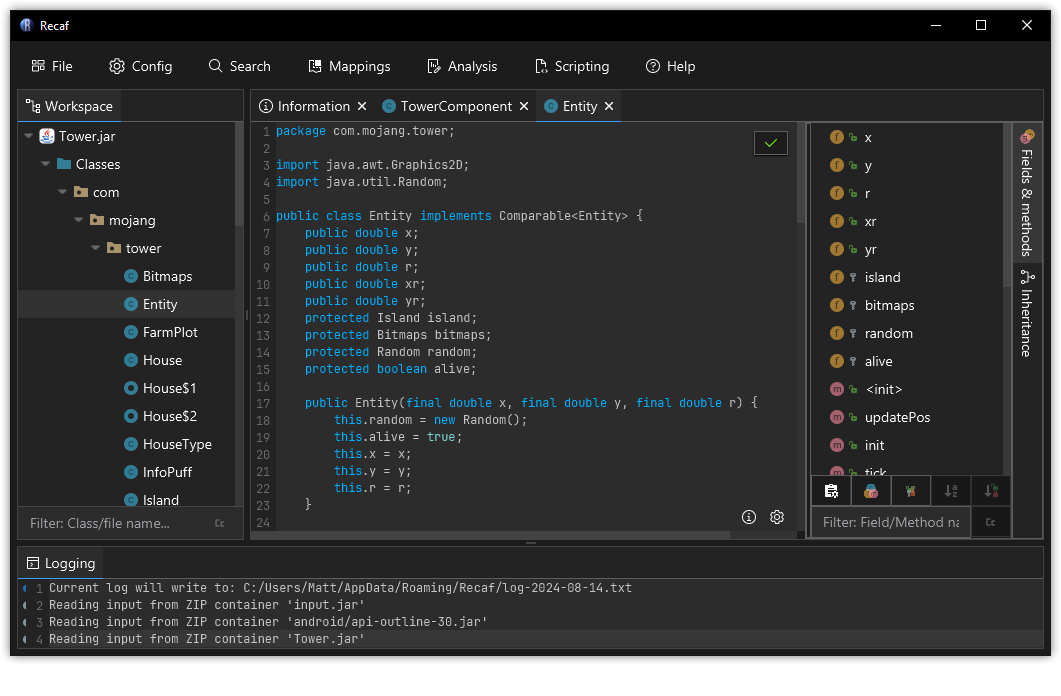
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
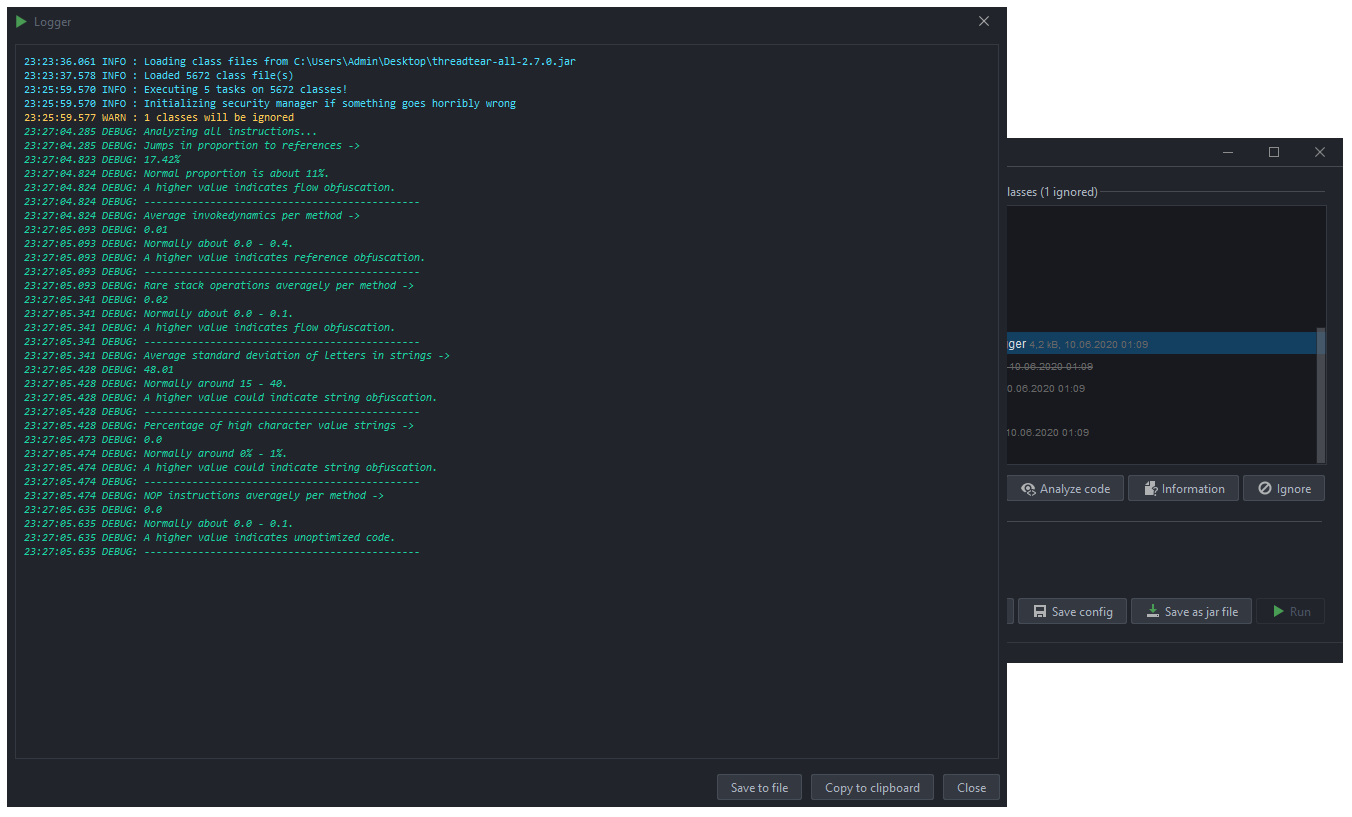 loerting/threadtear
Multifunctional java deobfuscation tool suite
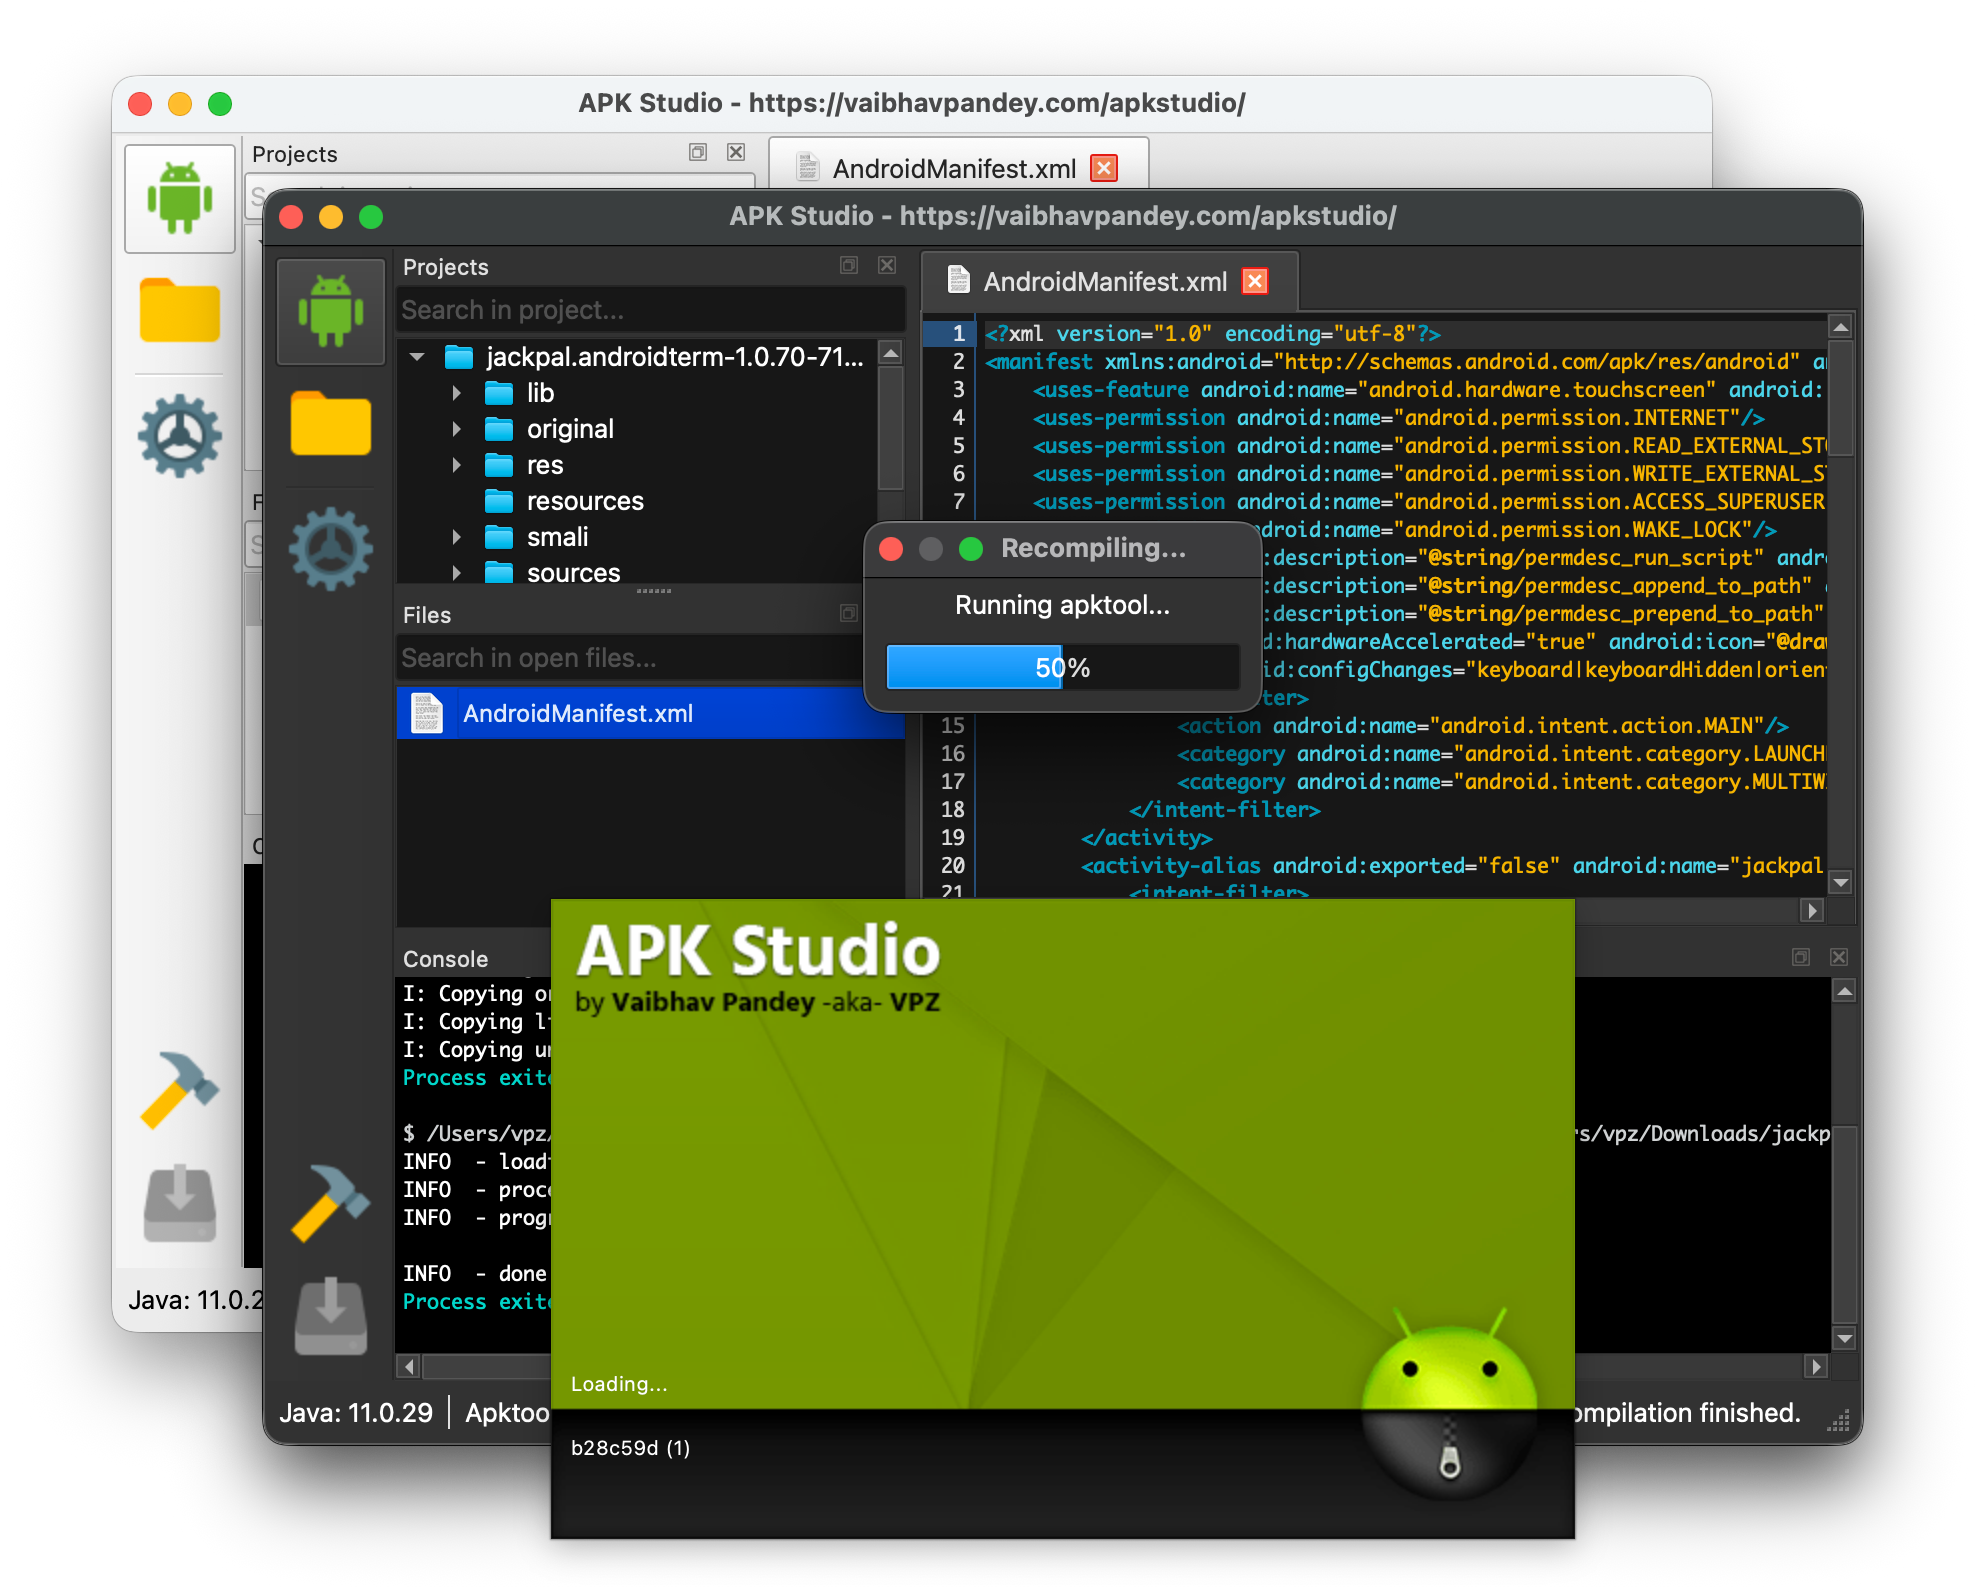 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
