
gemma_crackme_tutorial
 markoglasgow/gemma_crackme_tutorial
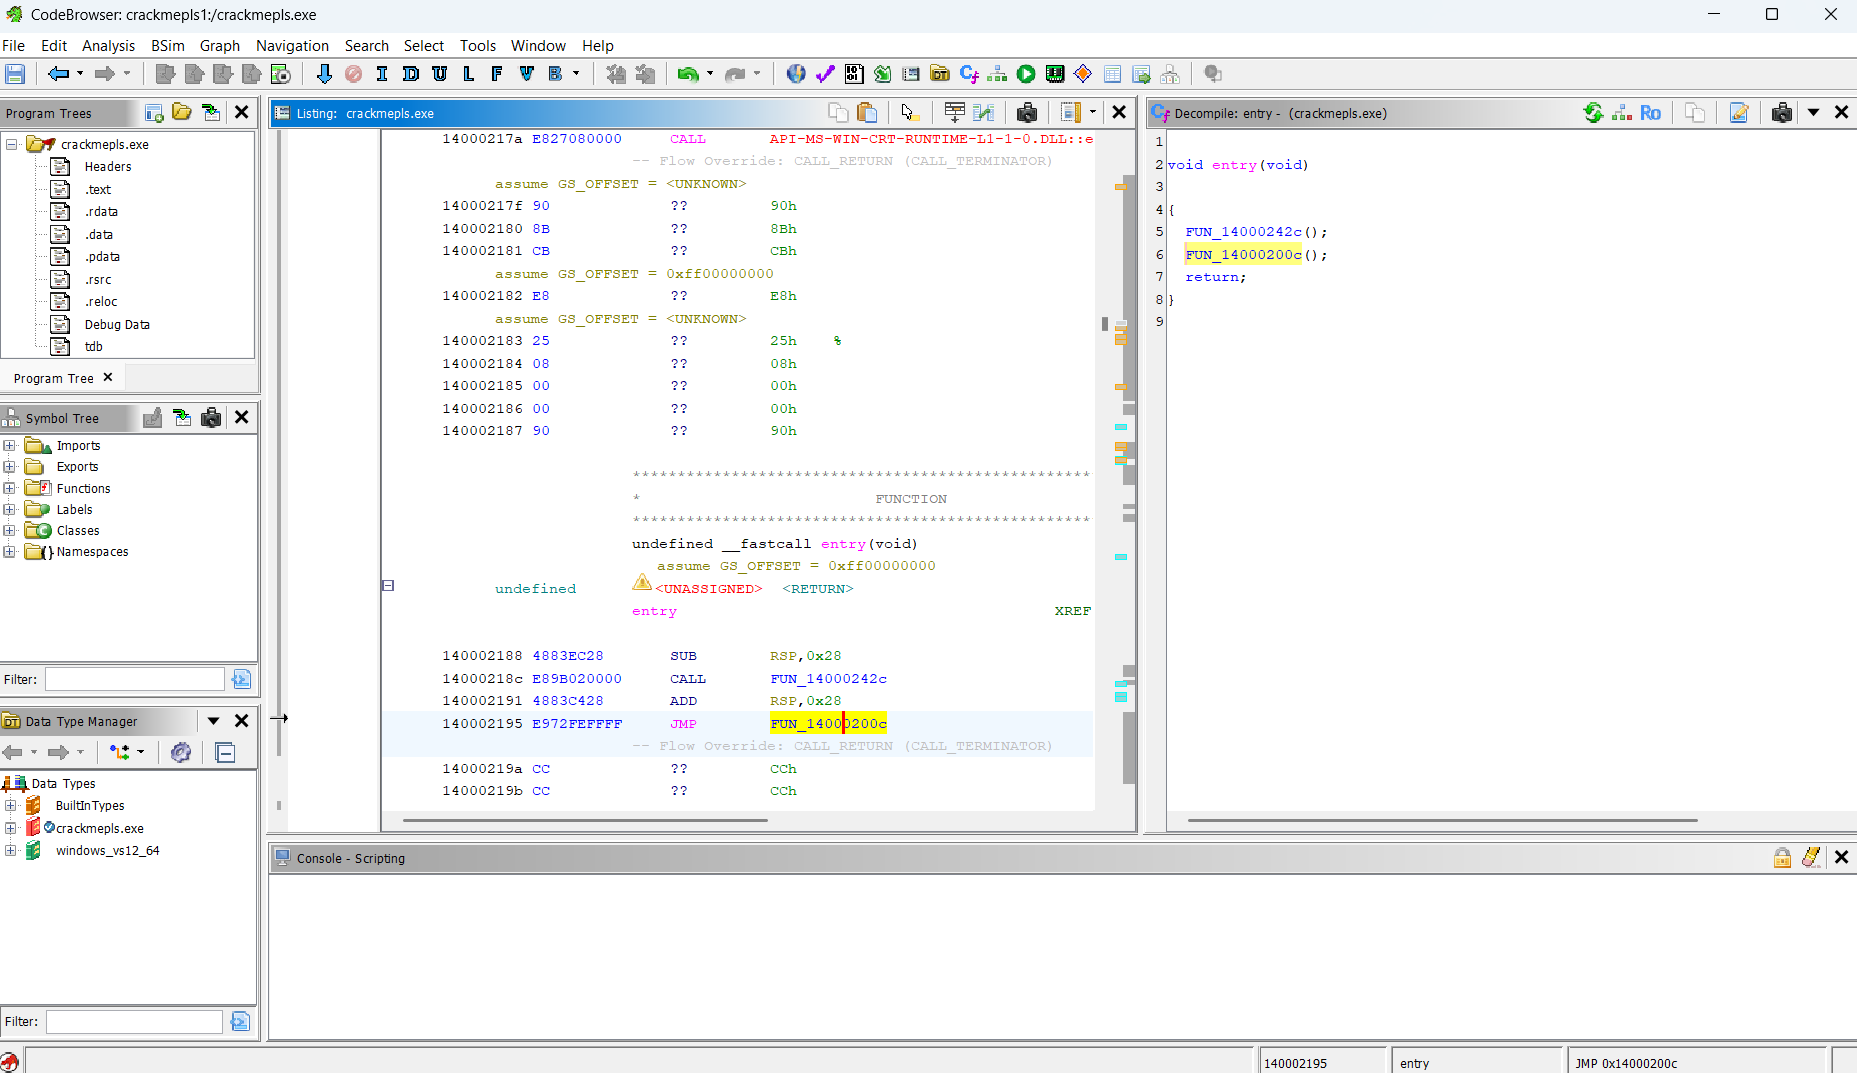
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
ai-assisted-reversingbinary-analysisdebuggers+3
35
