
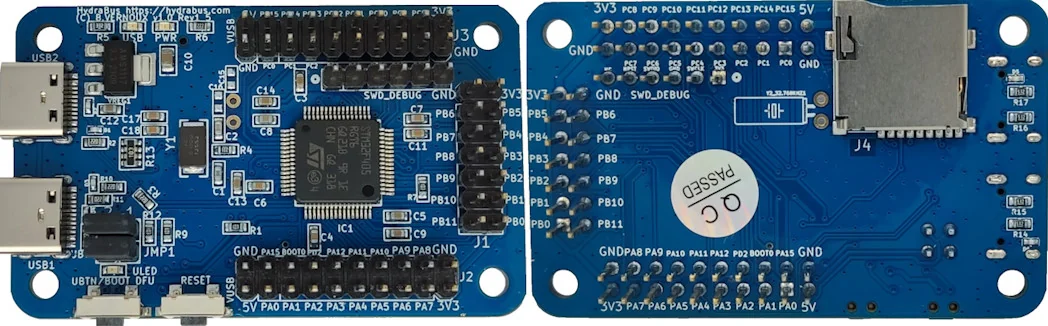
hydrafw
 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
debuggerseducationembedded-systems-security+6
448
hydrabus/hydrafwOpen-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 allthingsida/idasql
Vibe Reverse Engineer with IDA SQL: An interface for IDA in SQL via live virtual tables
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
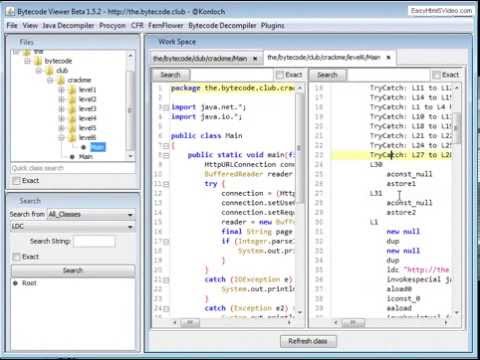 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 illera88/ponce
IDA 2016 plugin contest winner! Symbolic Execution just one-click away!

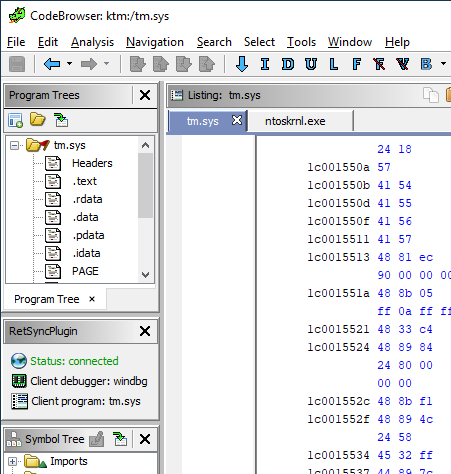 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
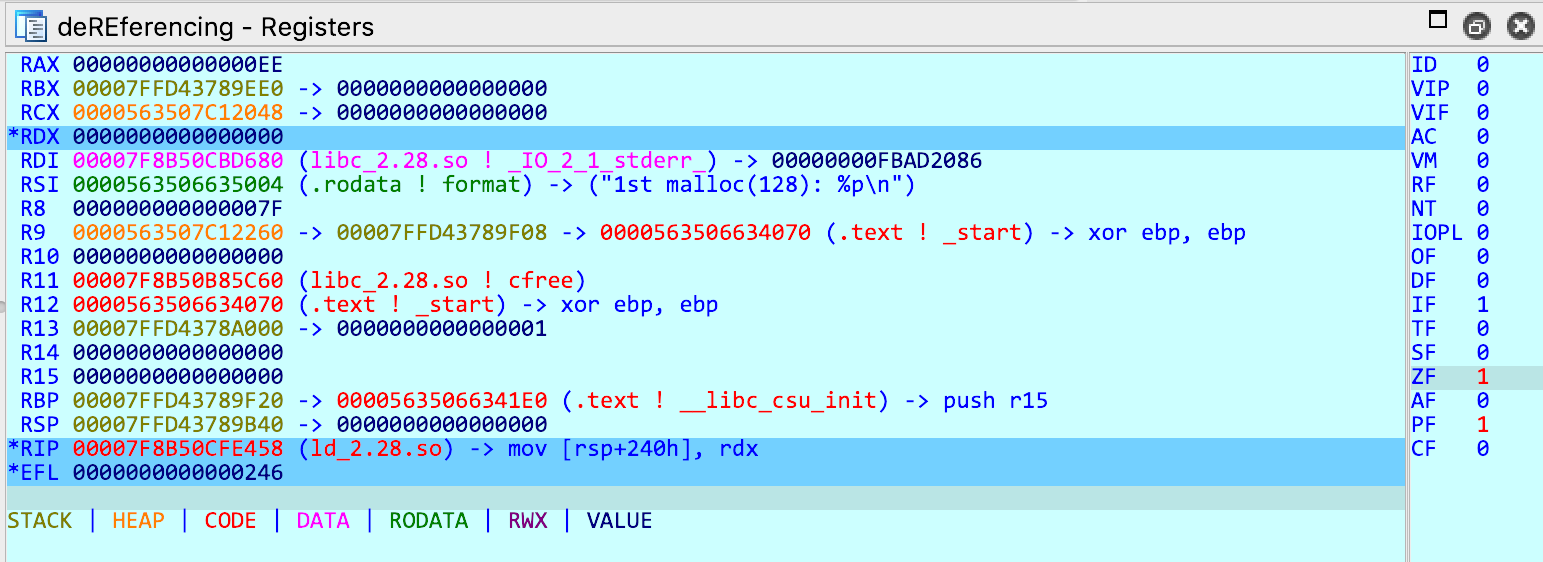 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views