

ceasta
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
178
ngwg/ceastaDisassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
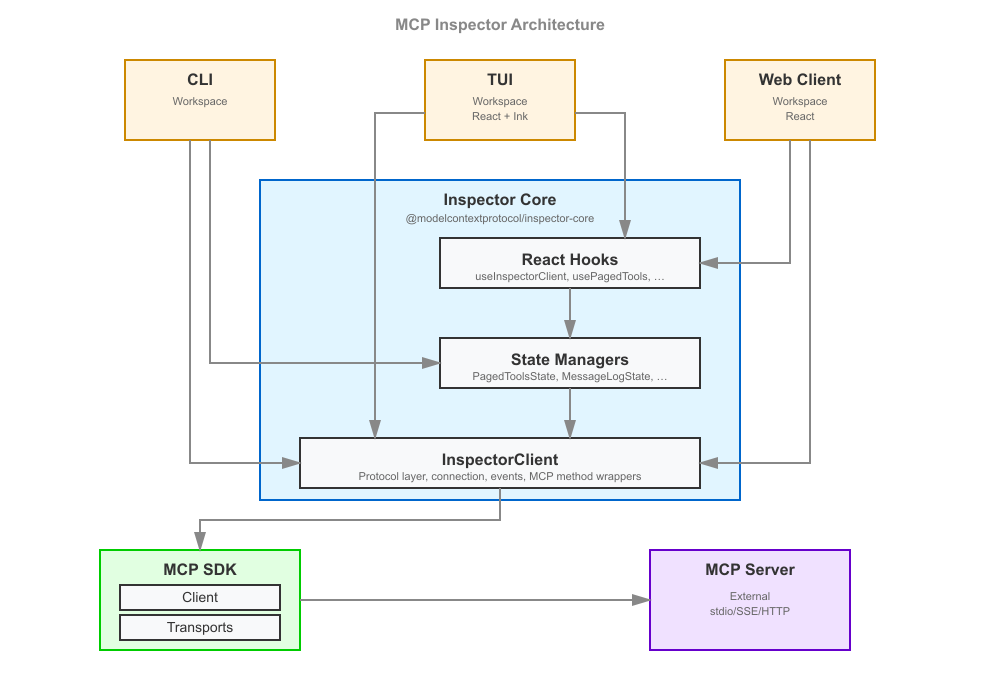 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…

 zrax/pycdc
C++ python bytecode disassembler and decompiler
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 takahiroharuyama/ida_haru
scripts/plugins for IDA Pro
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
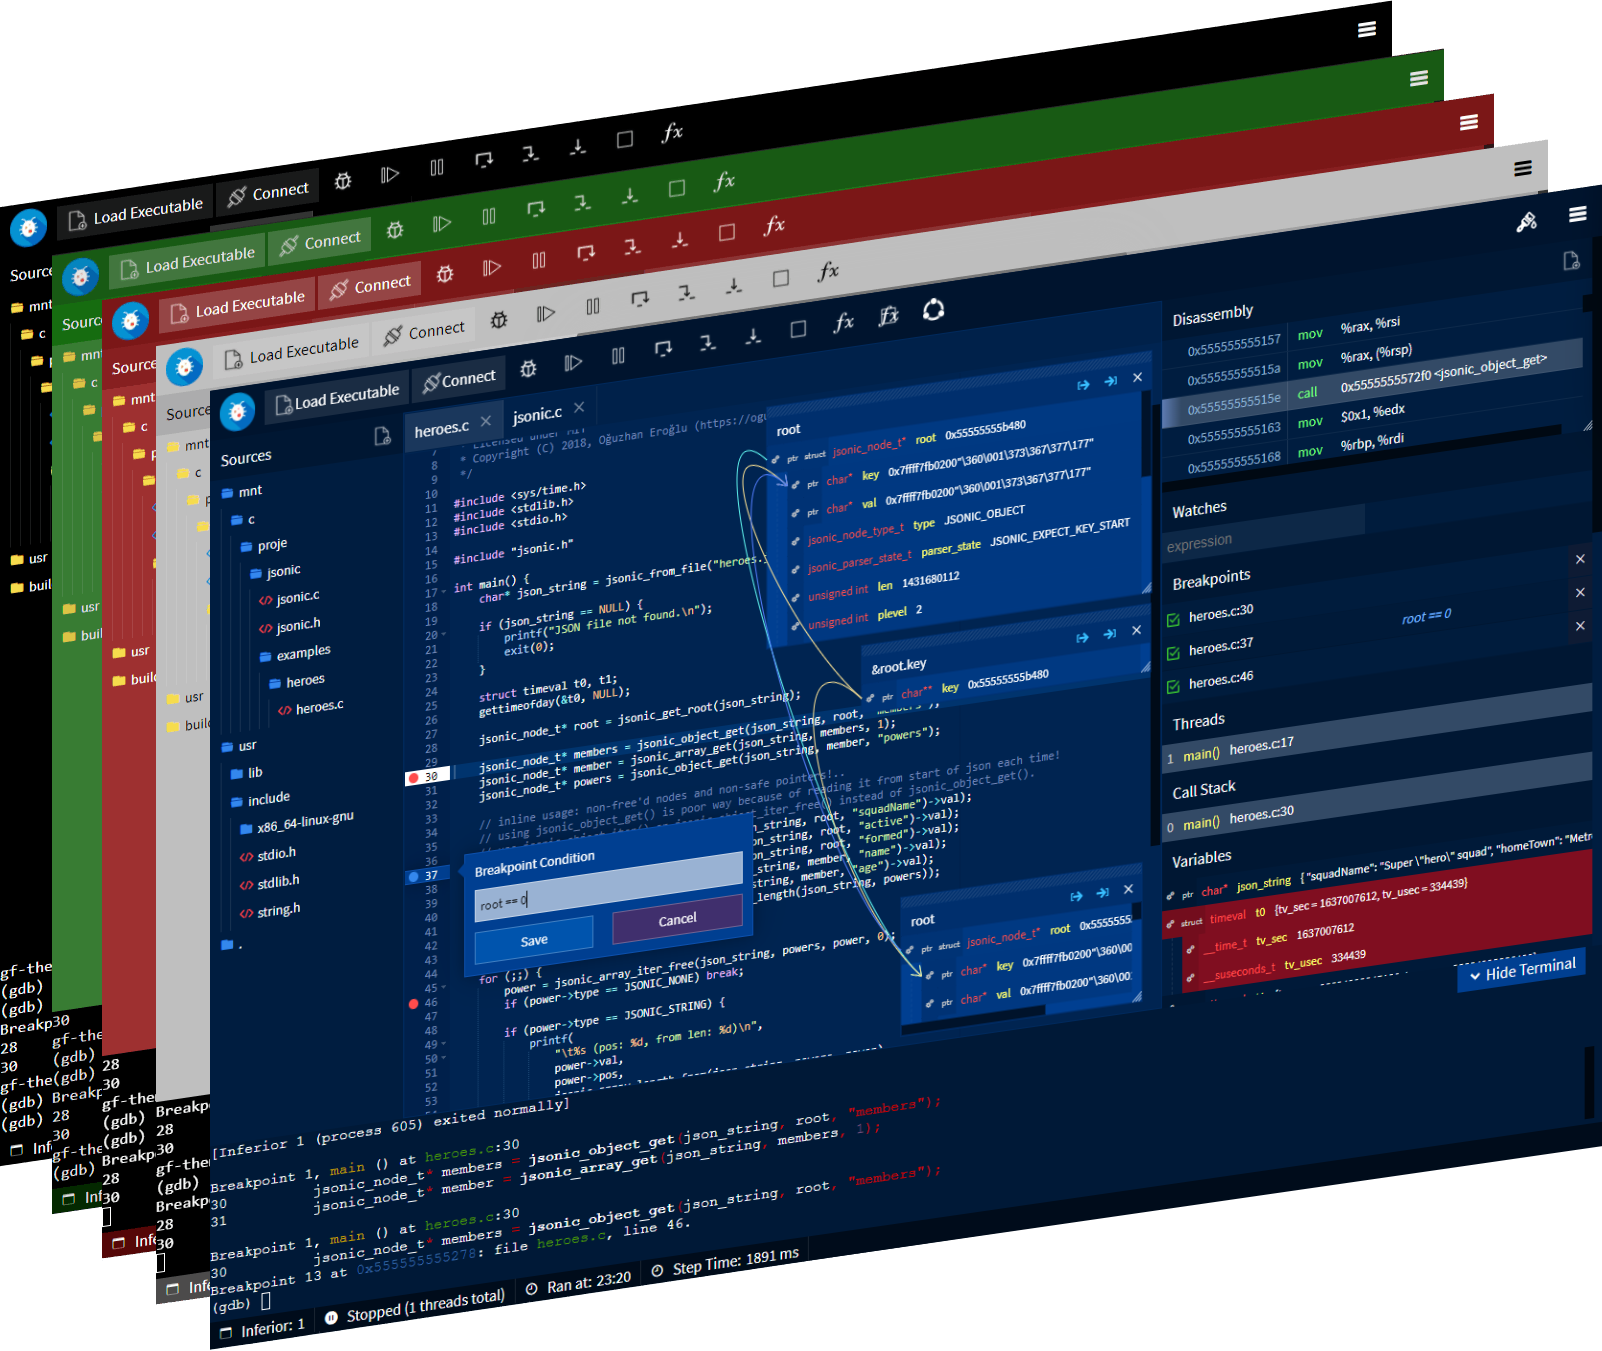 rohanrhu/gdb-frontend
☕ GDBFrontend is an easy, flexible and extensible gui debugger.