

ILSpy
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
binary-analysiscode-analysisdebuggers+2
icsharpcode/ilspy.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
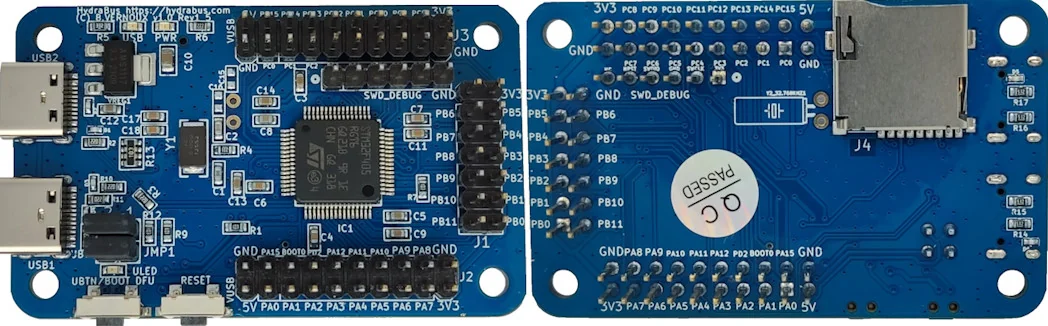 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 cea-sec/miasm
Reverse engineering framework in Python
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 nccgroup/iodide
The Cisco IOS Debugger and Integrated Disassembler Environment
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 nickcano/xenoscan
Open source memory scanner written in C++