

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
51.4k22h 21m ago
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
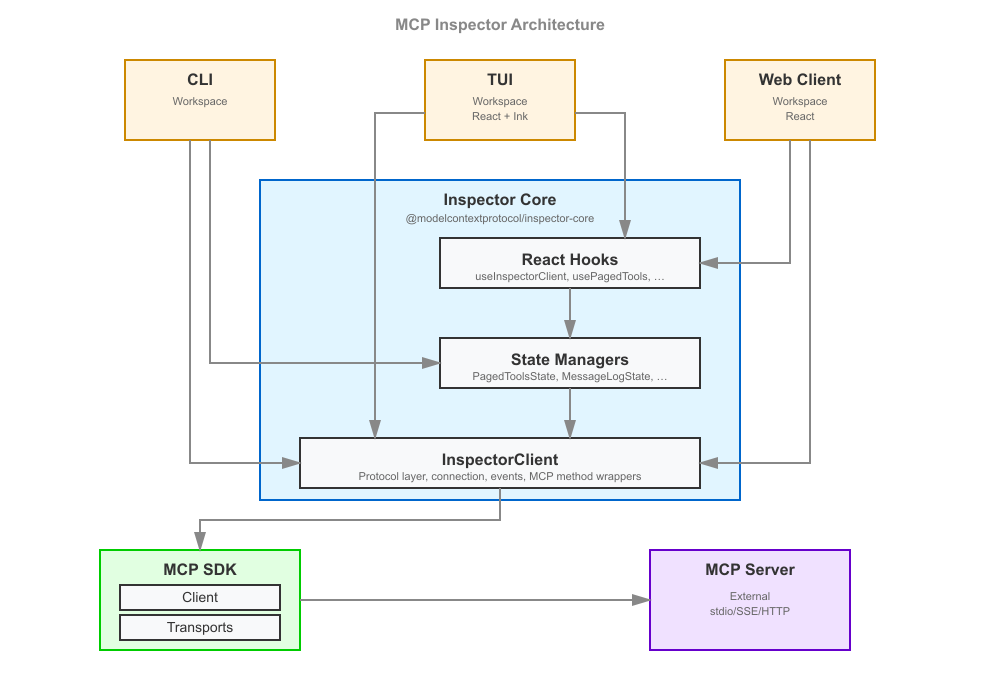 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
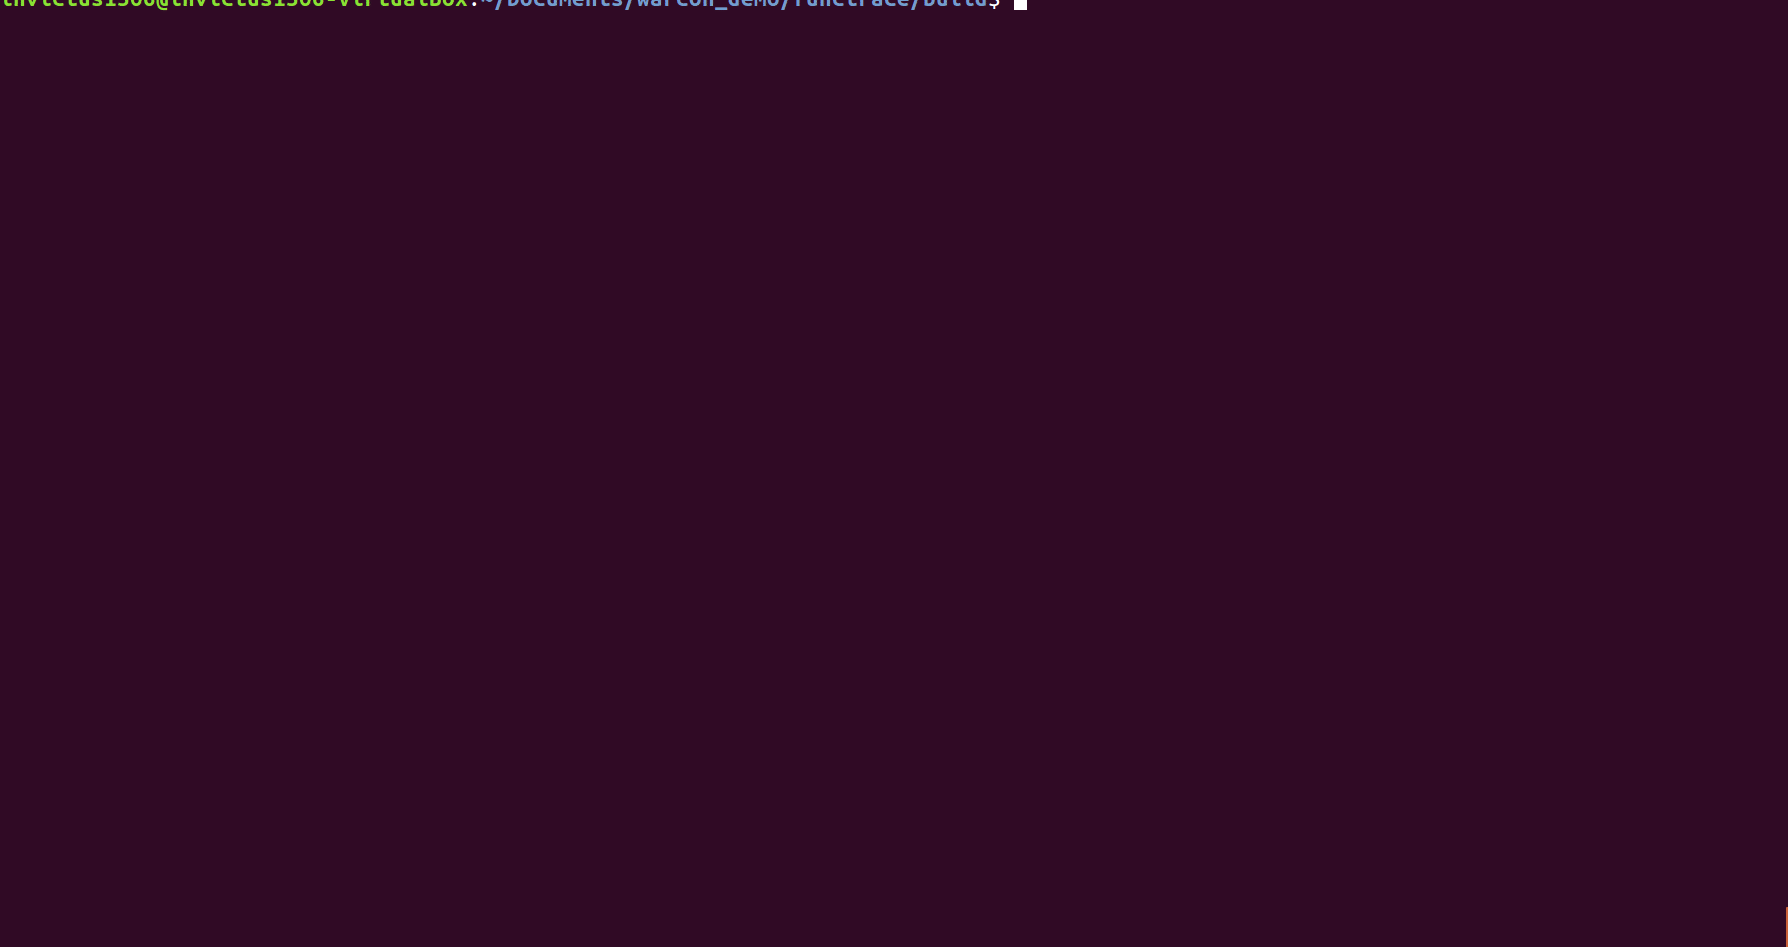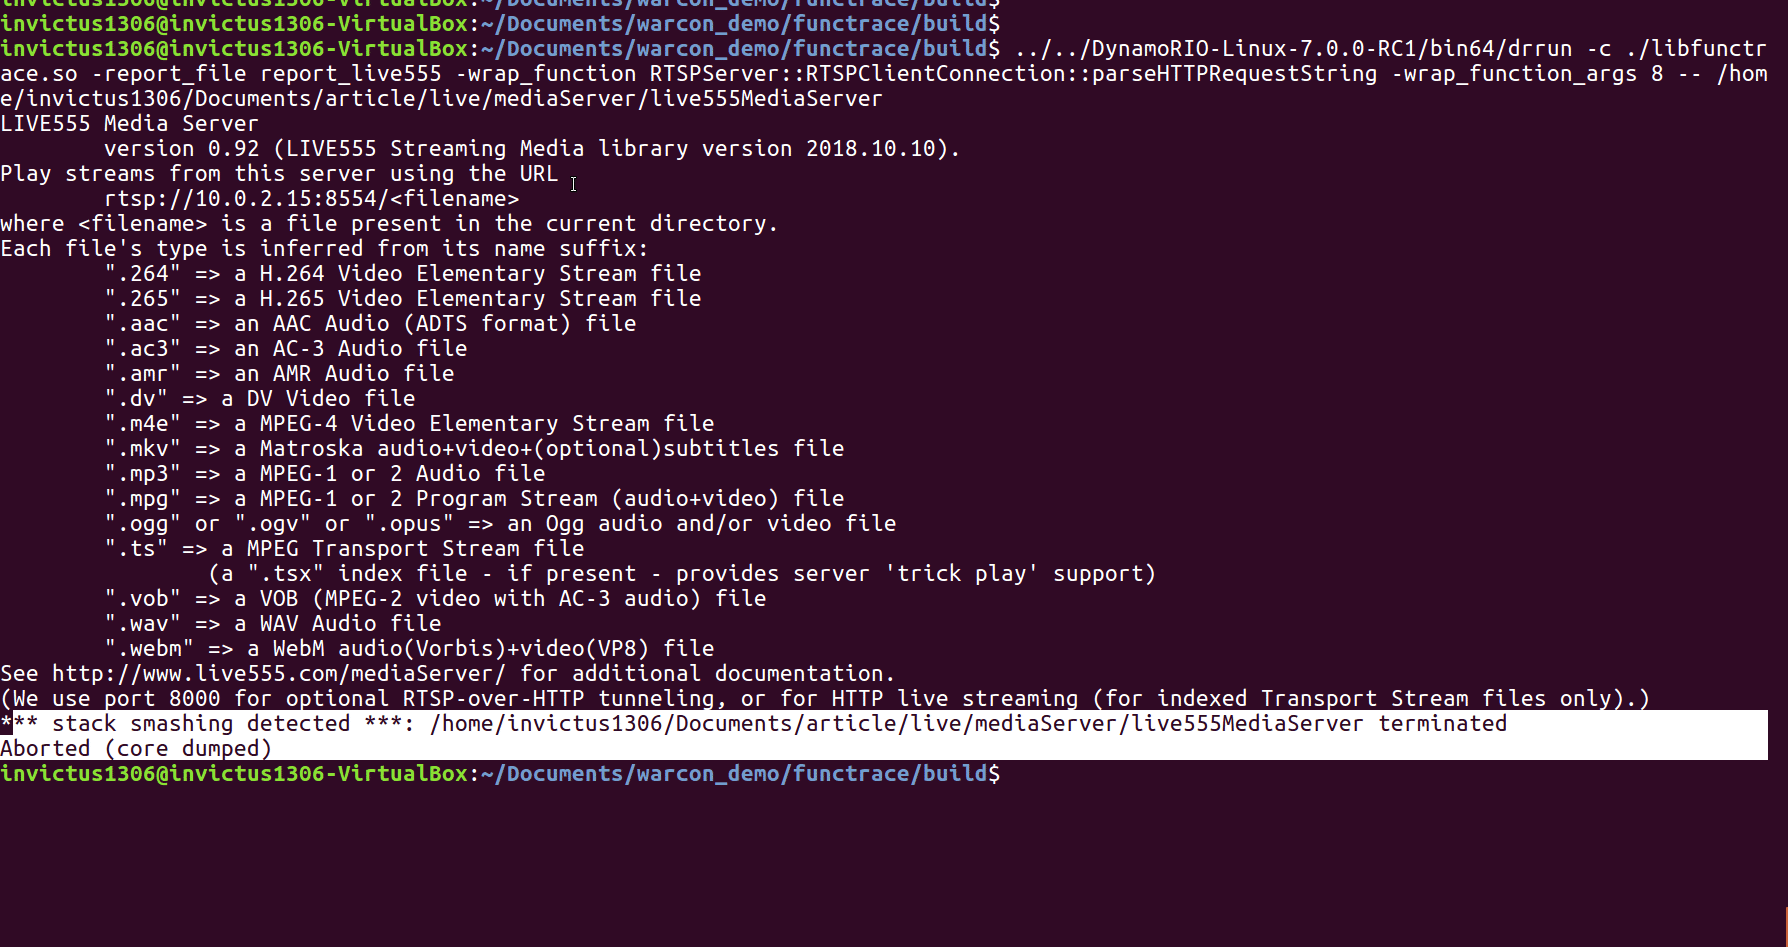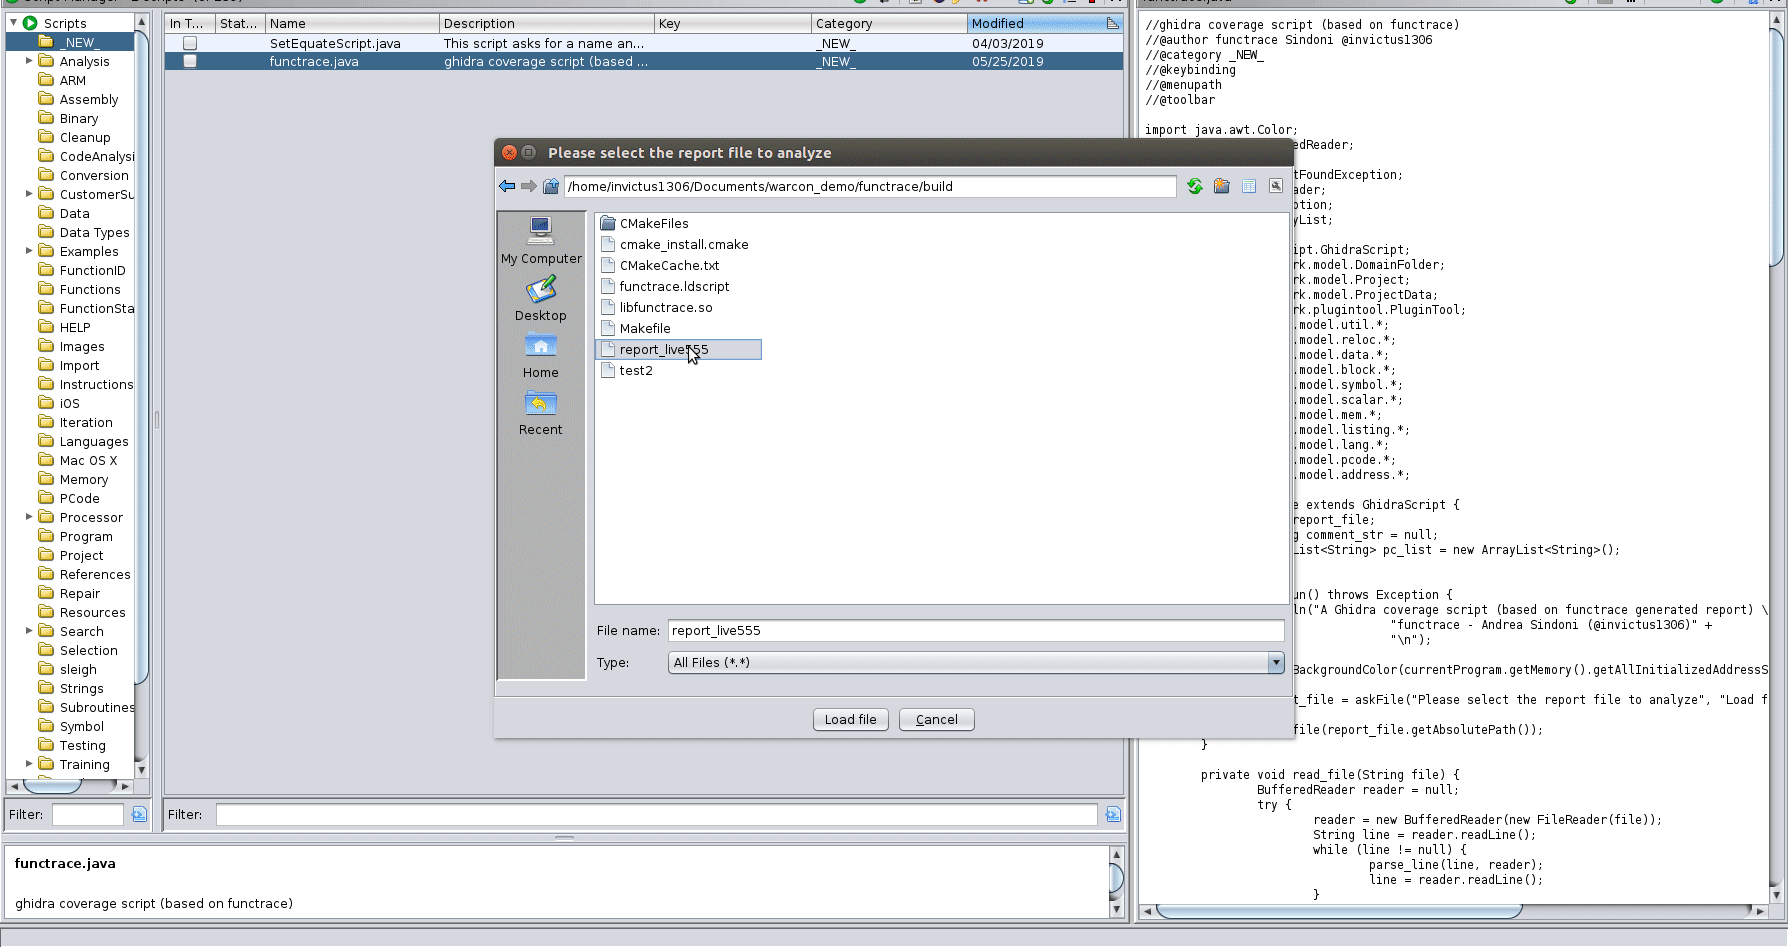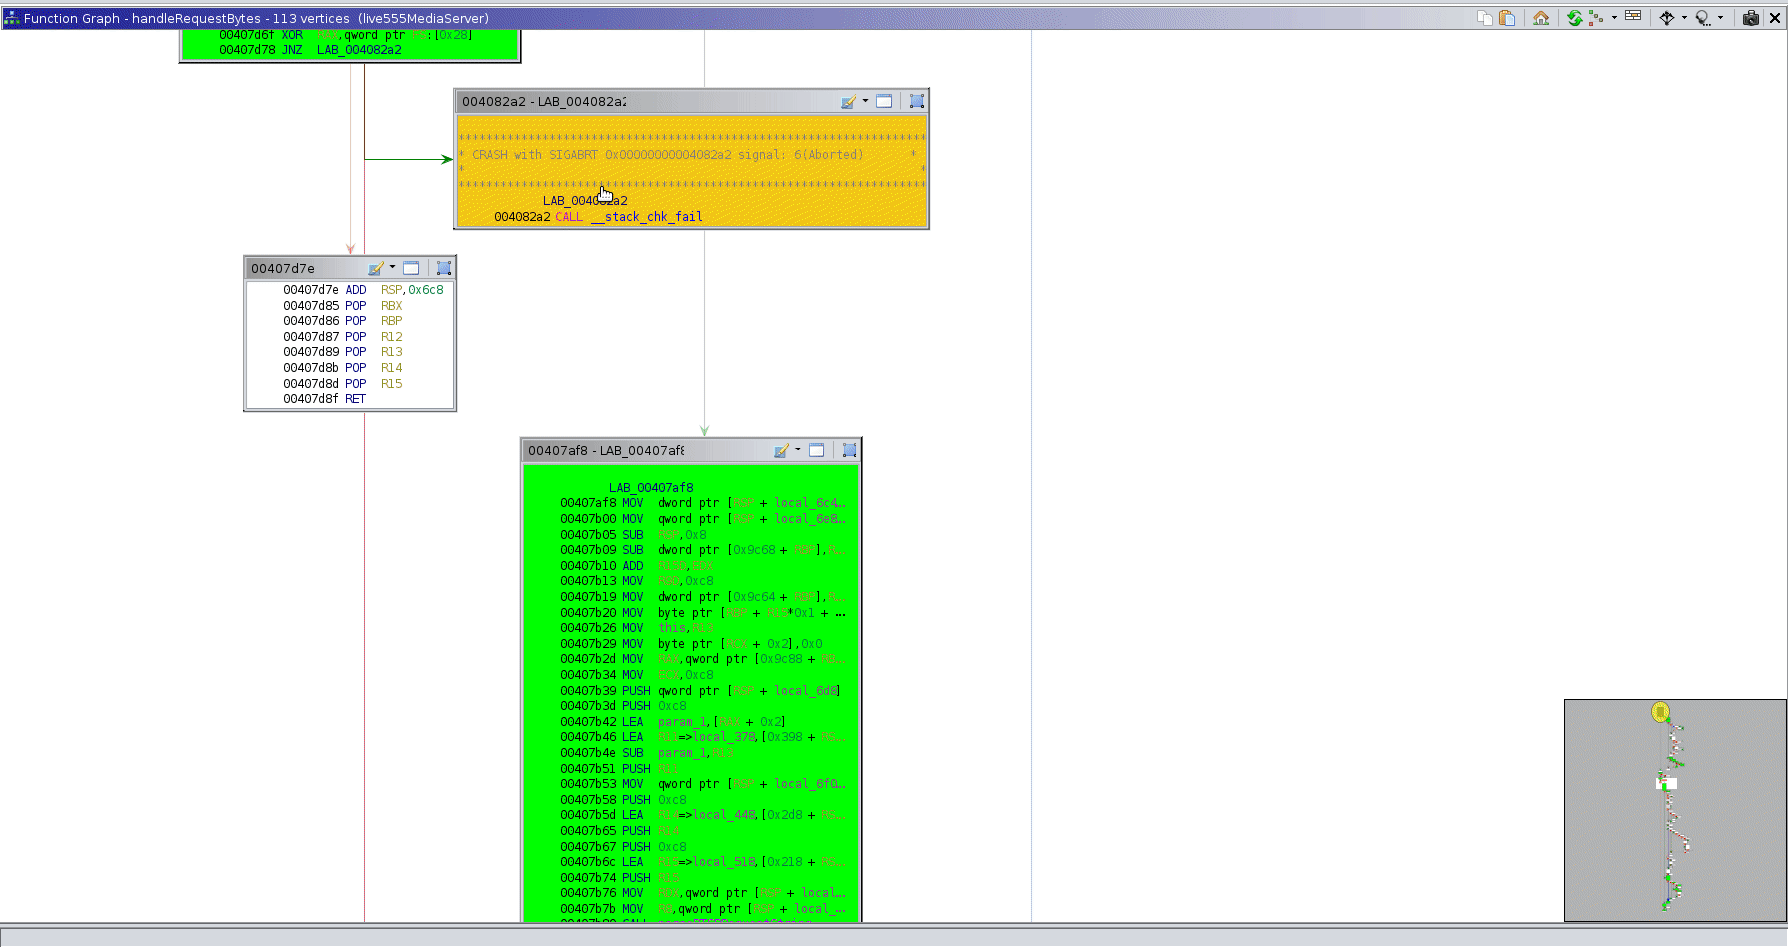 invictus1306/functrace
A function tracer
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
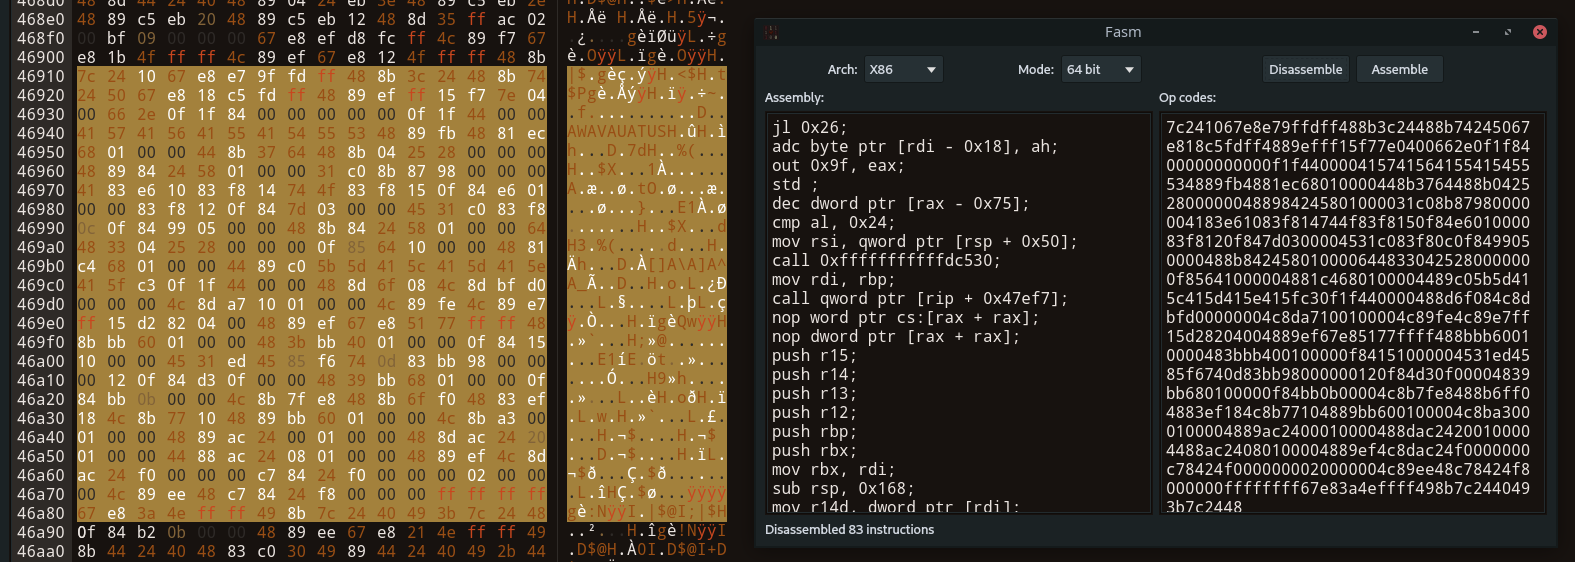 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
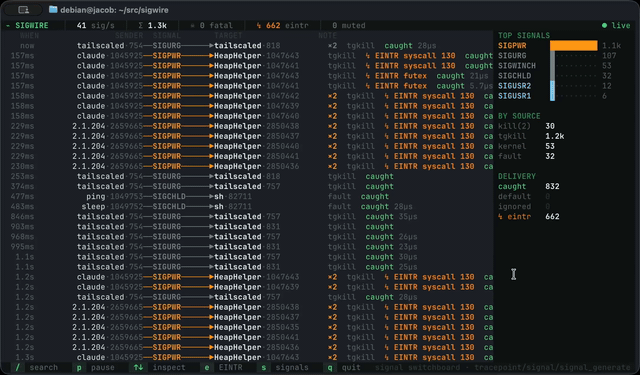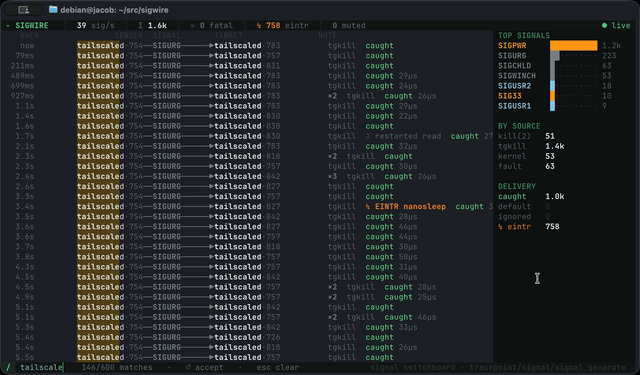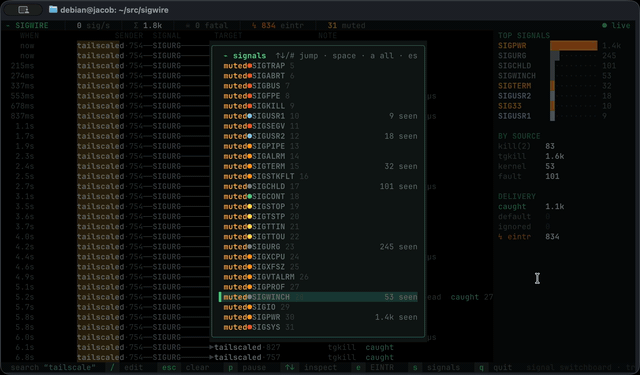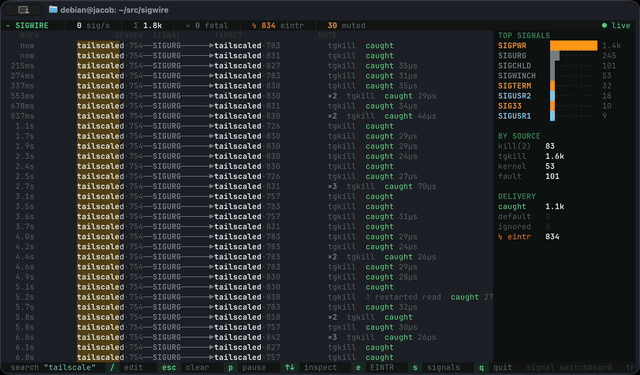 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
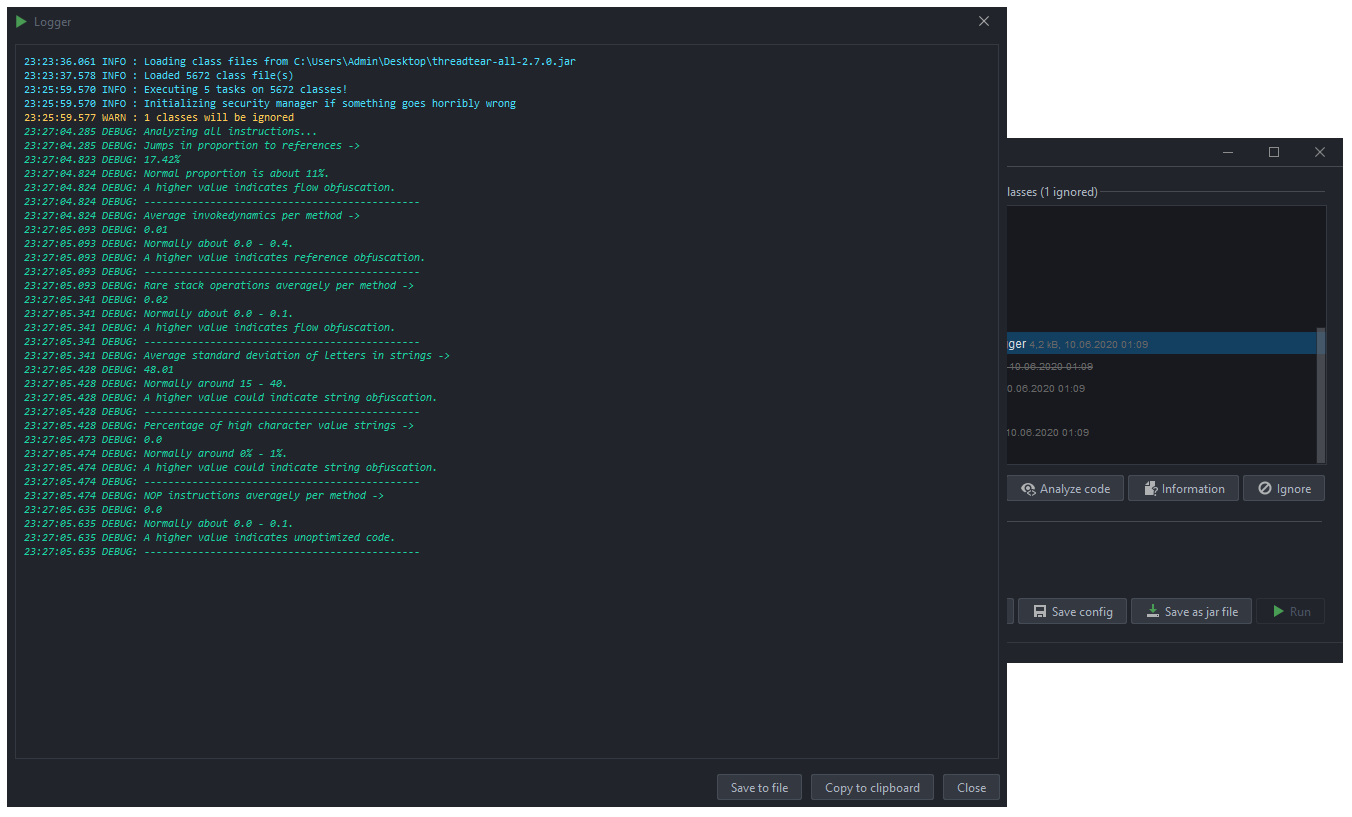 loerting/threadtear
Multifunctional java deobfuscation tool suite
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
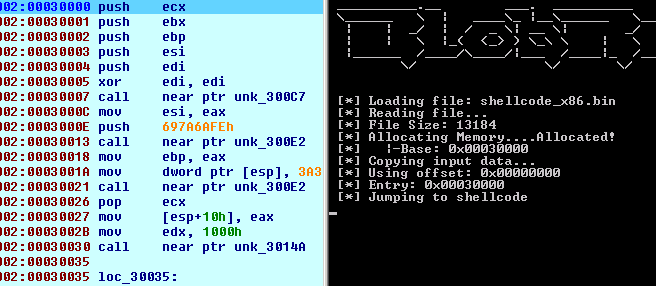 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 amossys/memitm
Tool to make in memory man in the middle
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android