
salt
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
paolomonti42/saltSALT - SLUB ALlocator Tracer for the Linux kernel
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 zodiacon/alltools
All reasonably stable tools
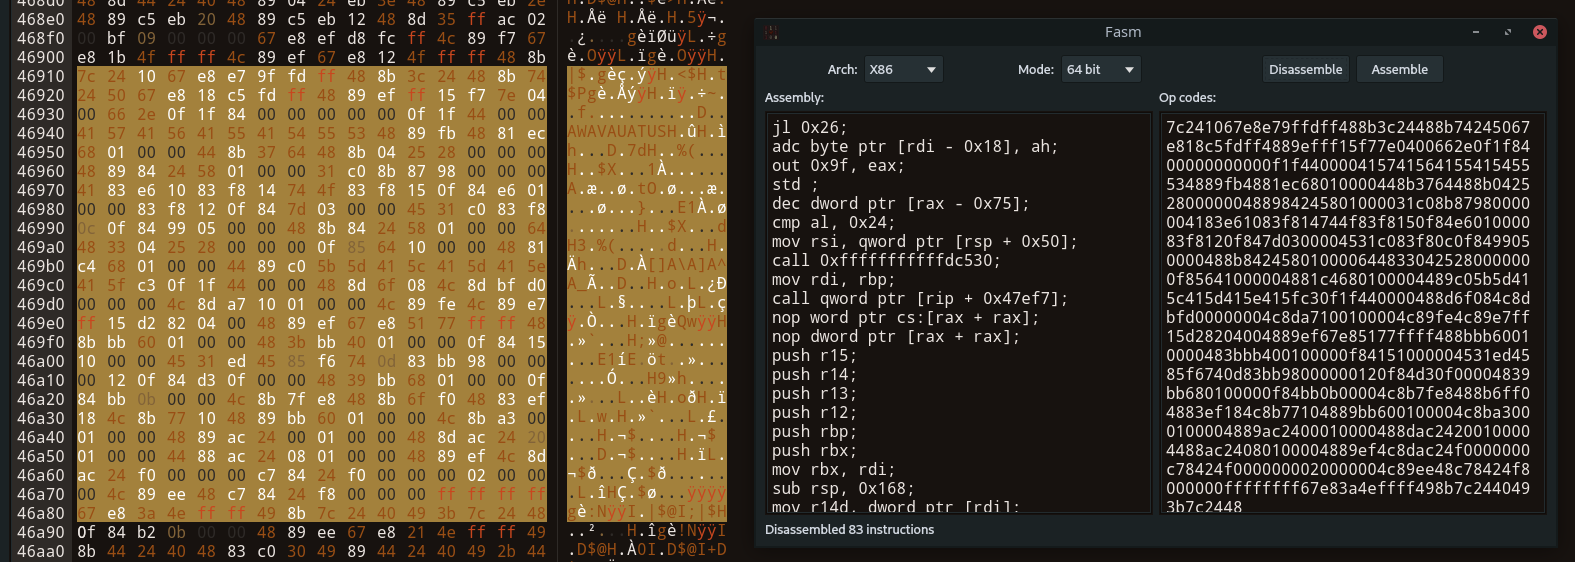 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
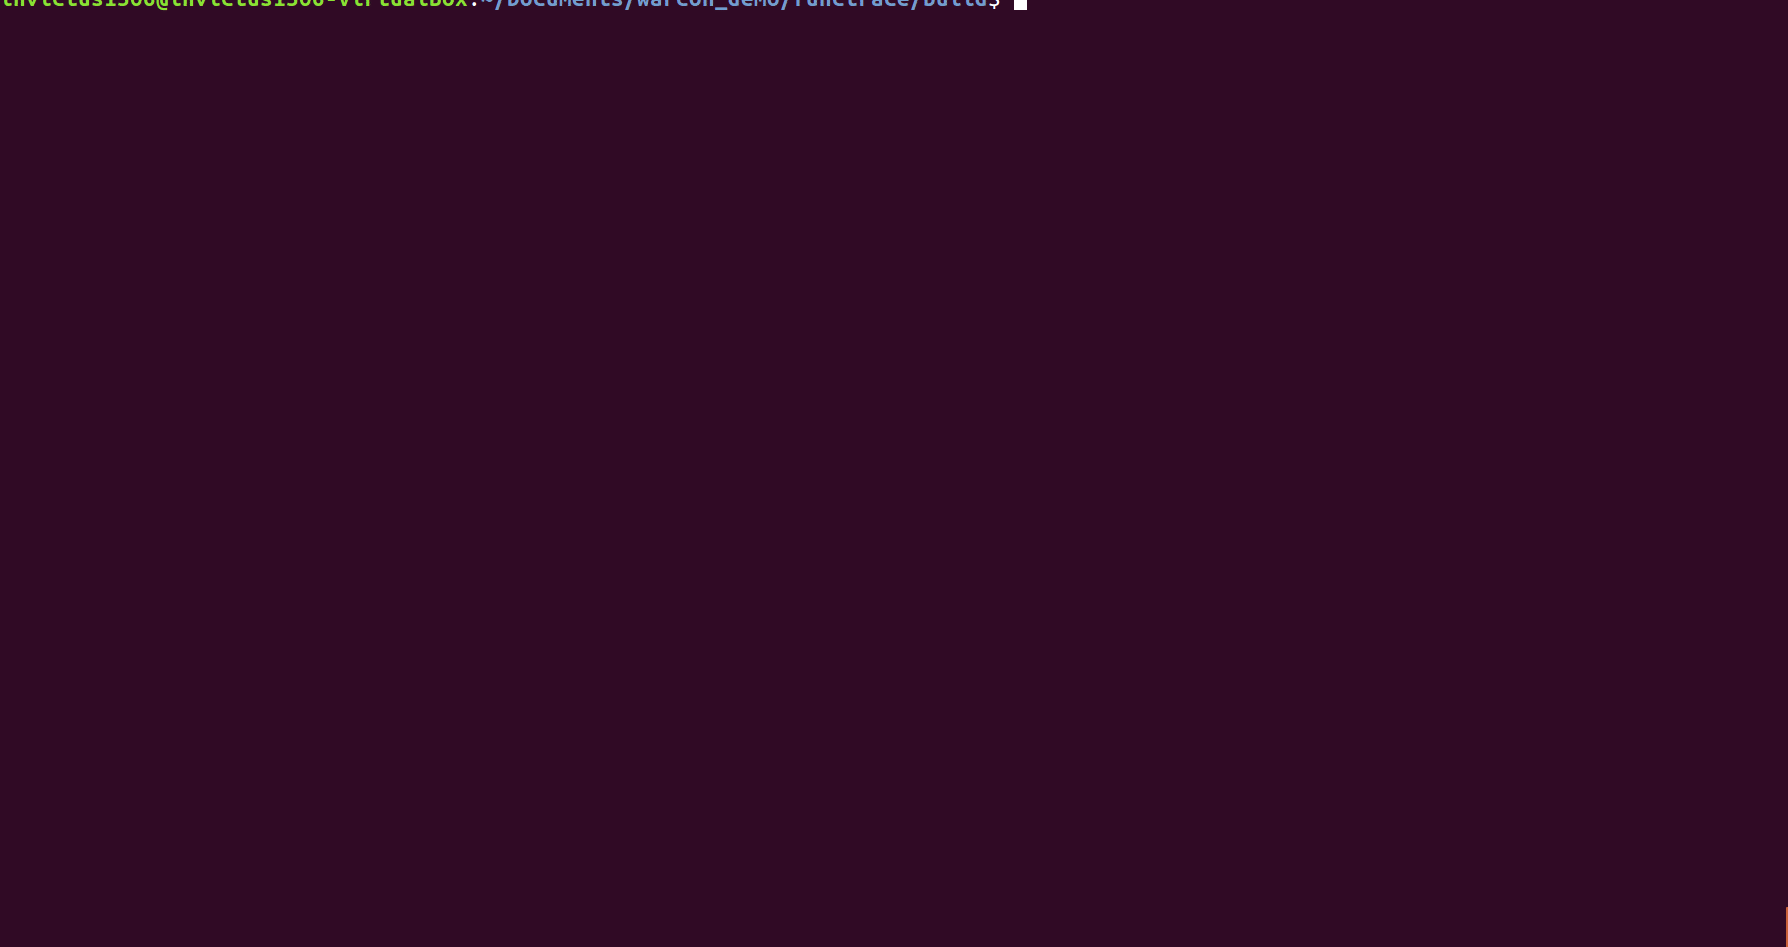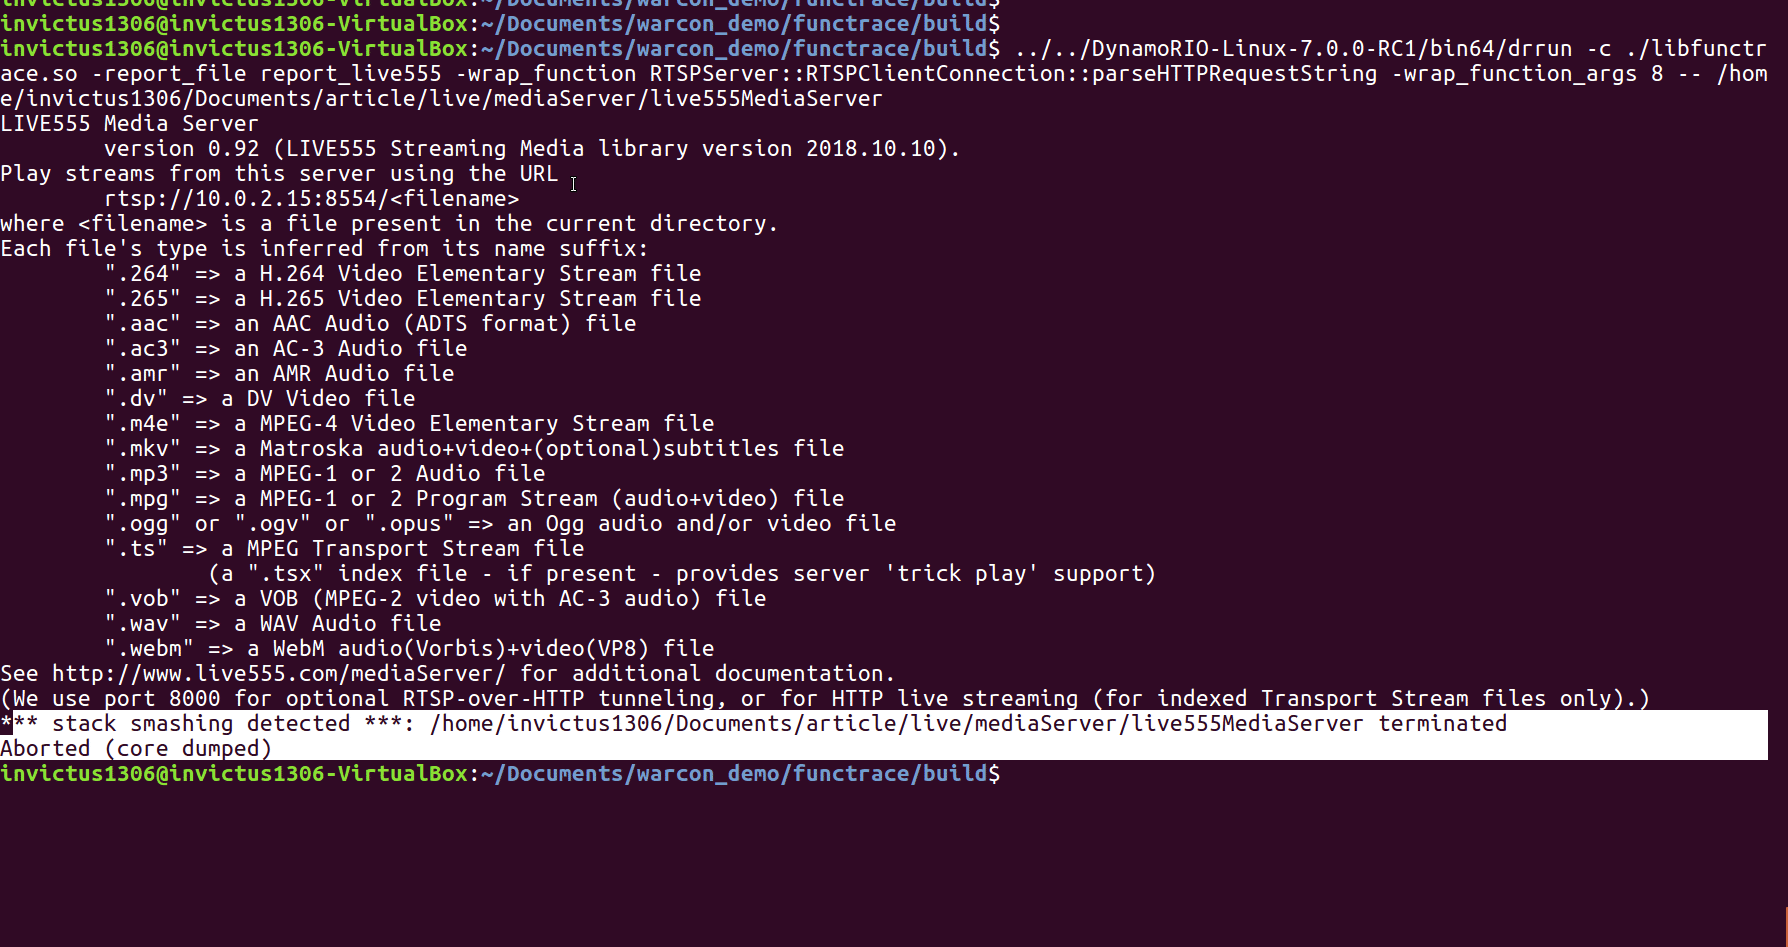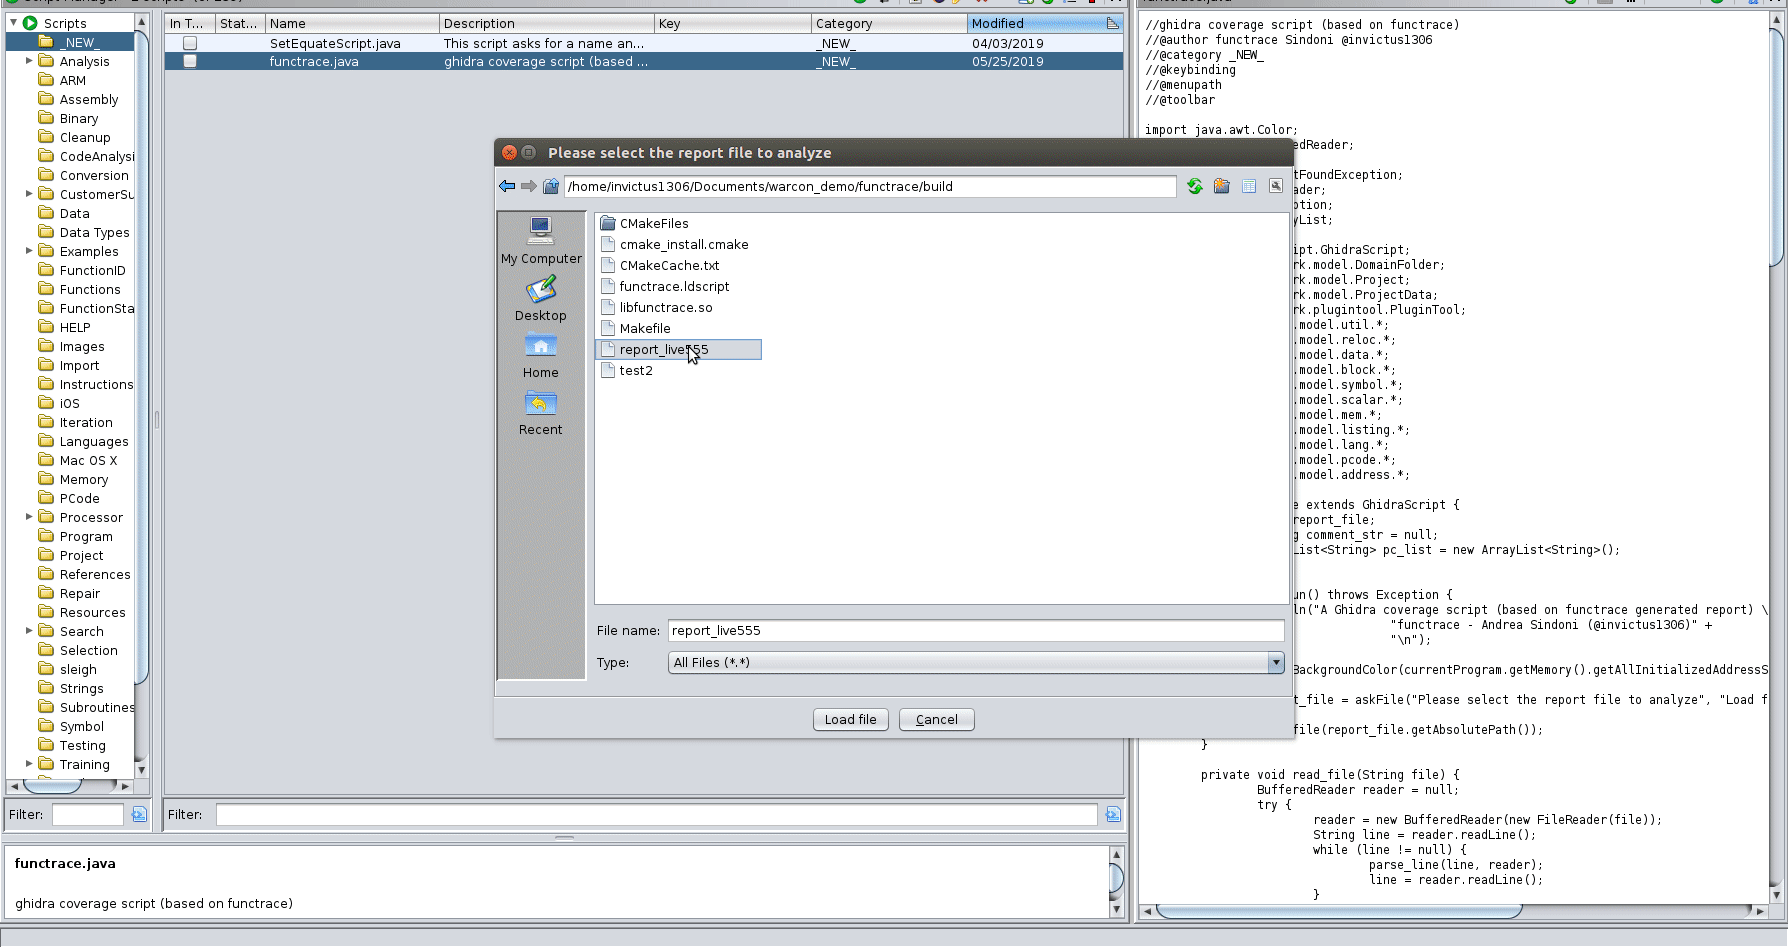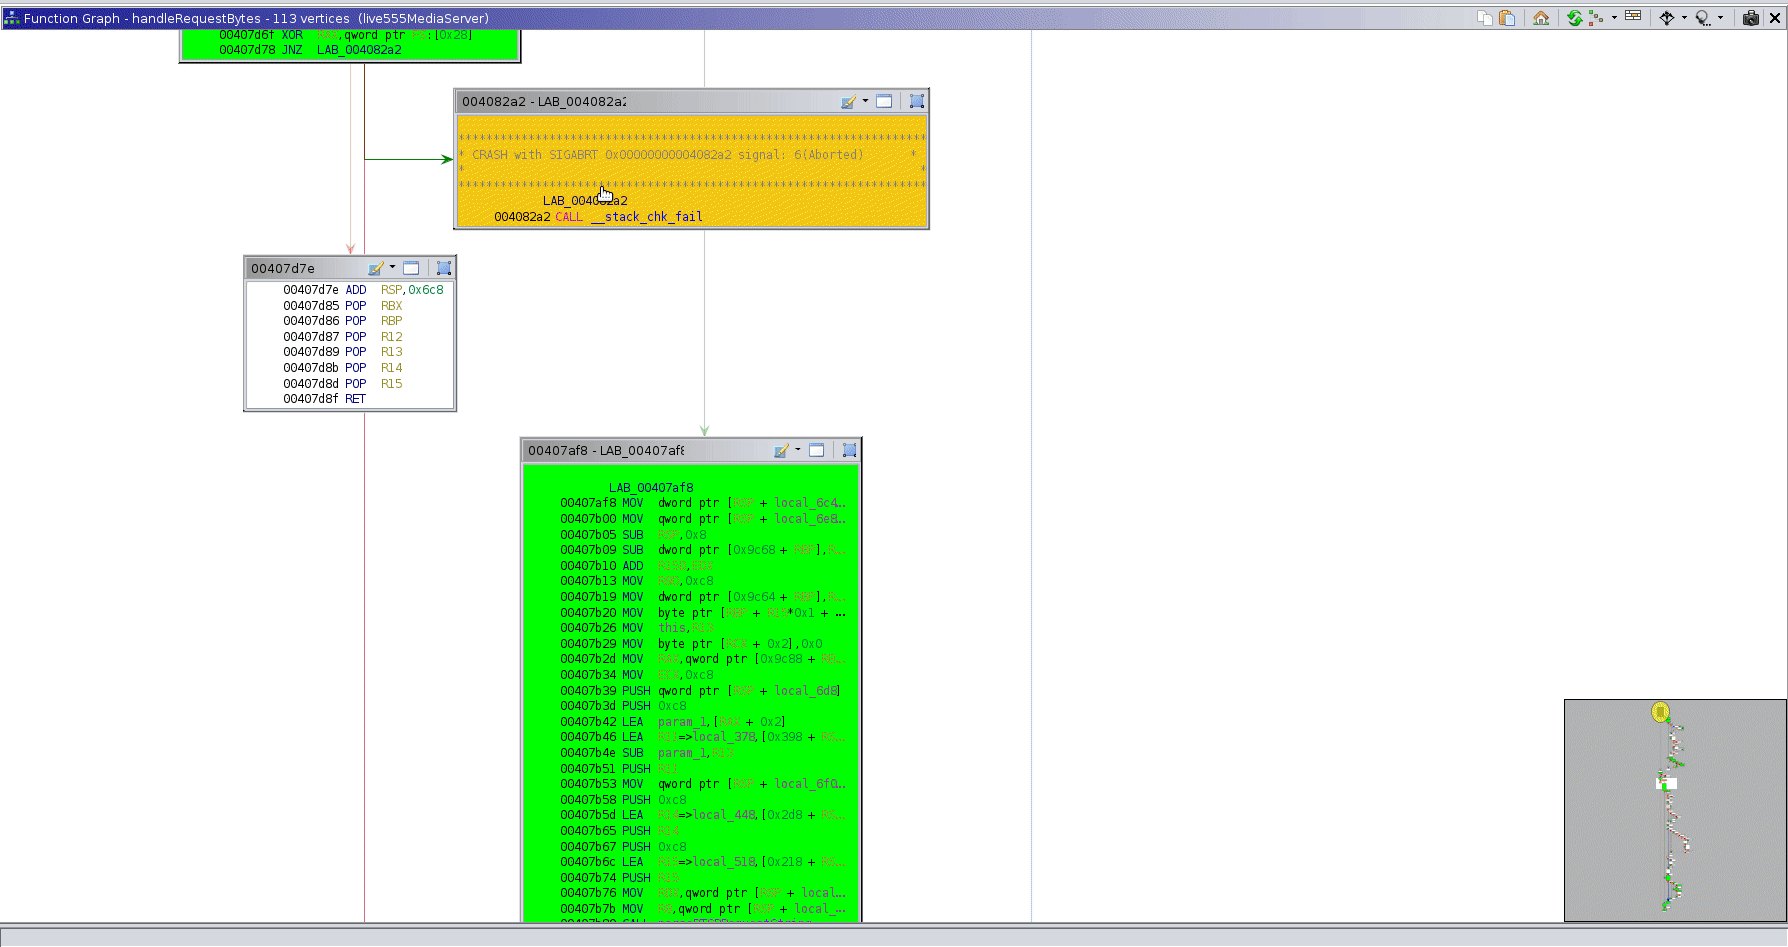 invictus1306/functrace
A function tracer
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
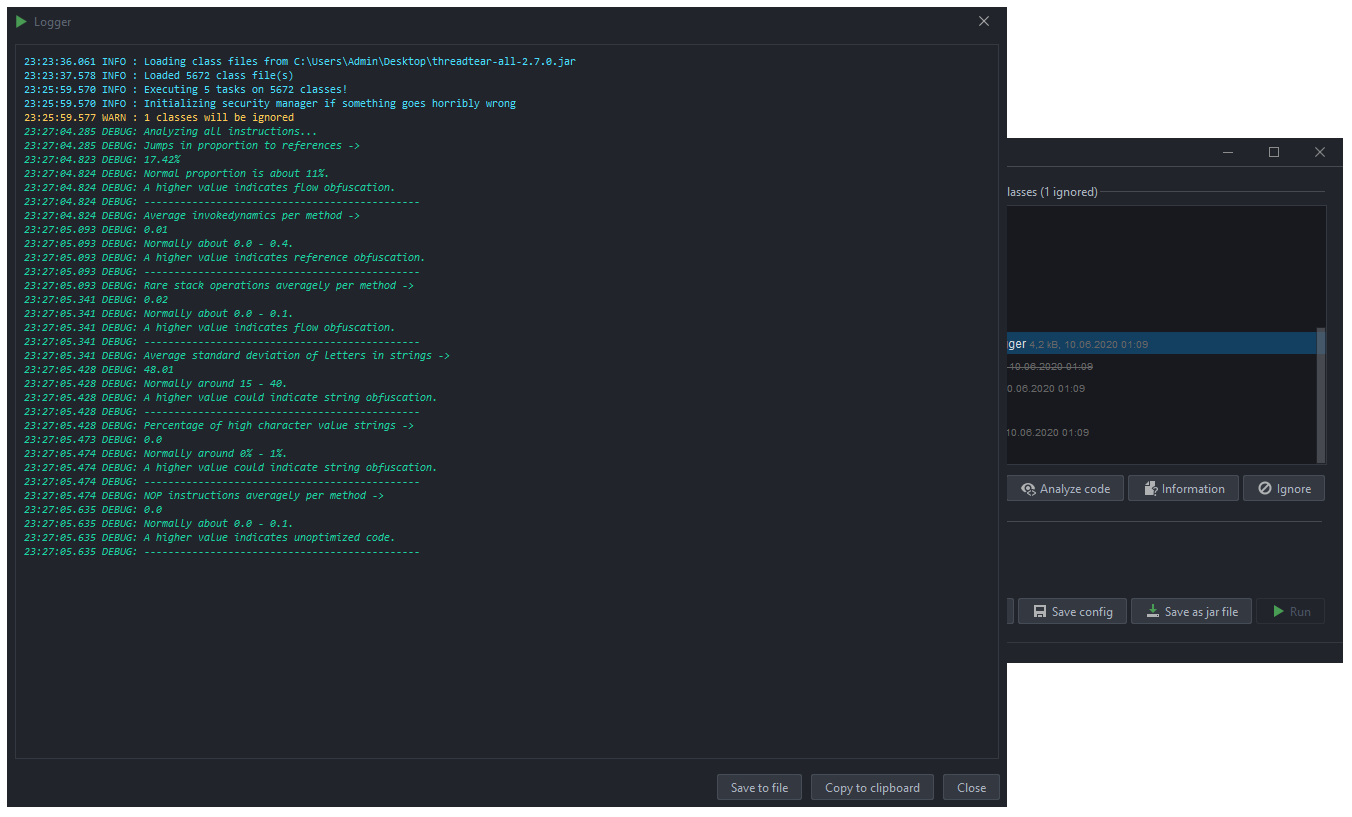 loerting/threadtear
Multifunctional java deobfuscation tool suite
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
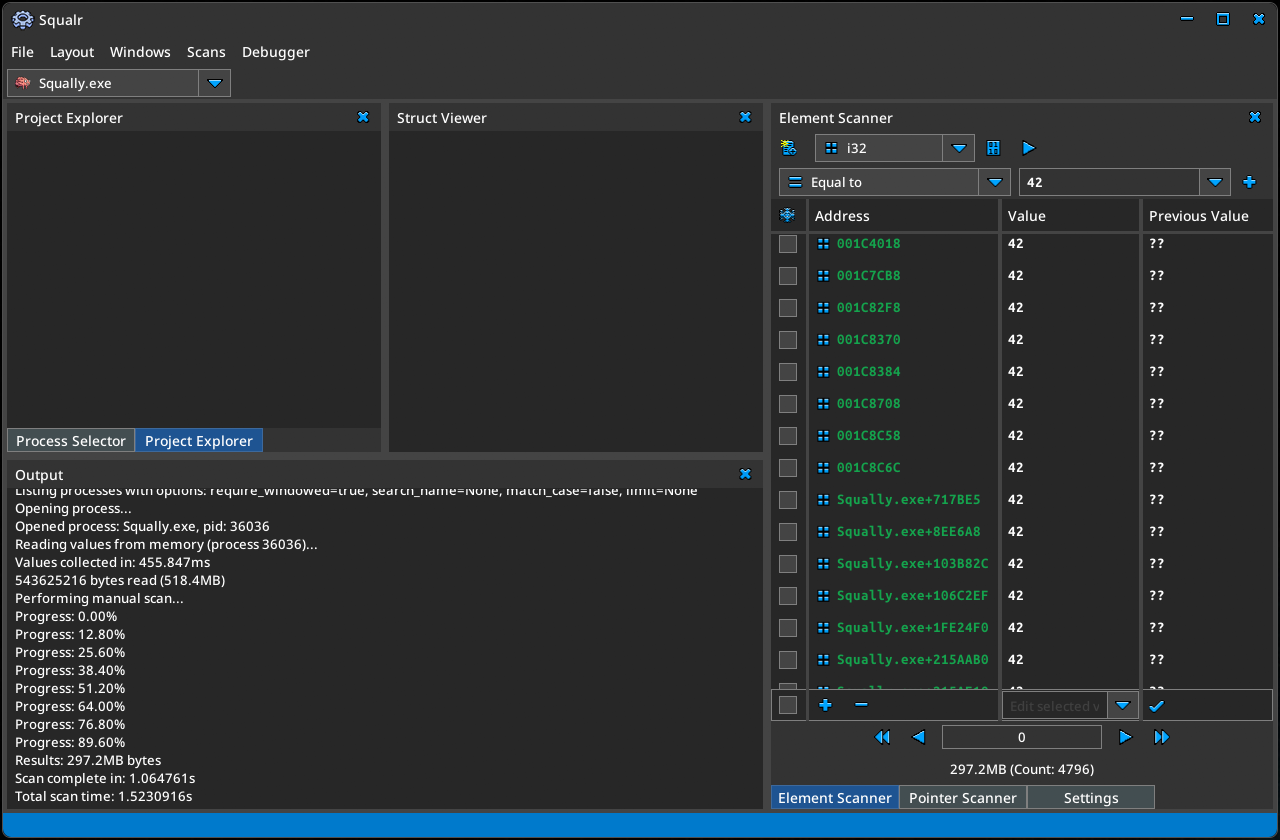 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 isecpartners/introspy-ios
Security profiling for blackbox iOS