

Rogue-Framework
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
21
thisistfs/rogue-frameworkDesktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…

 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
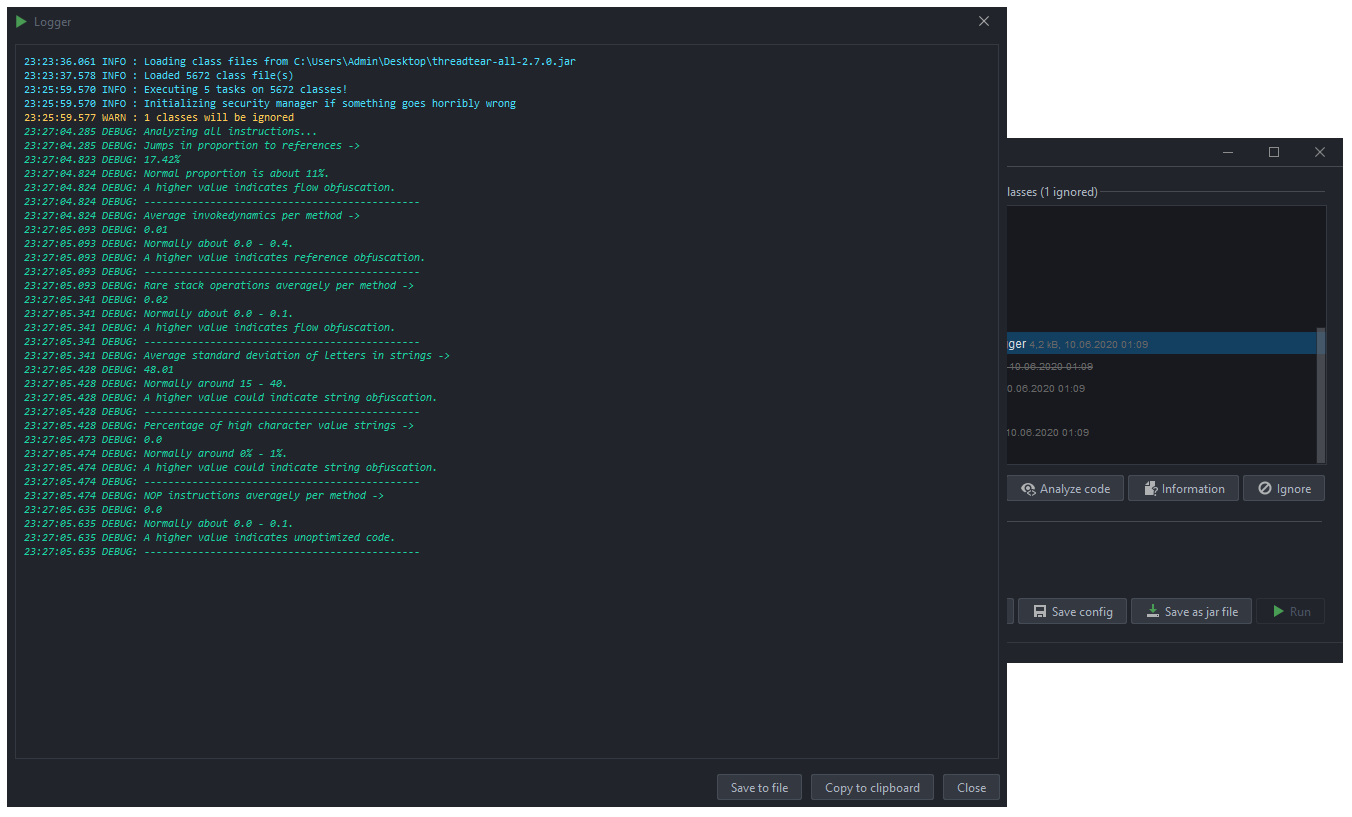 loerting/threadtear
Multifunctional java deobfuscation tool suite
 ctxis/cape
Malware Configuration And Payload Extraction