
slater
 hikari-systems/slater
Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
authentication-authorizationcloud-securitydatabase-security+3
103
hikari-systems/slaterLow-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…
 sysdream/pysqli
Python SQL injection framework
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
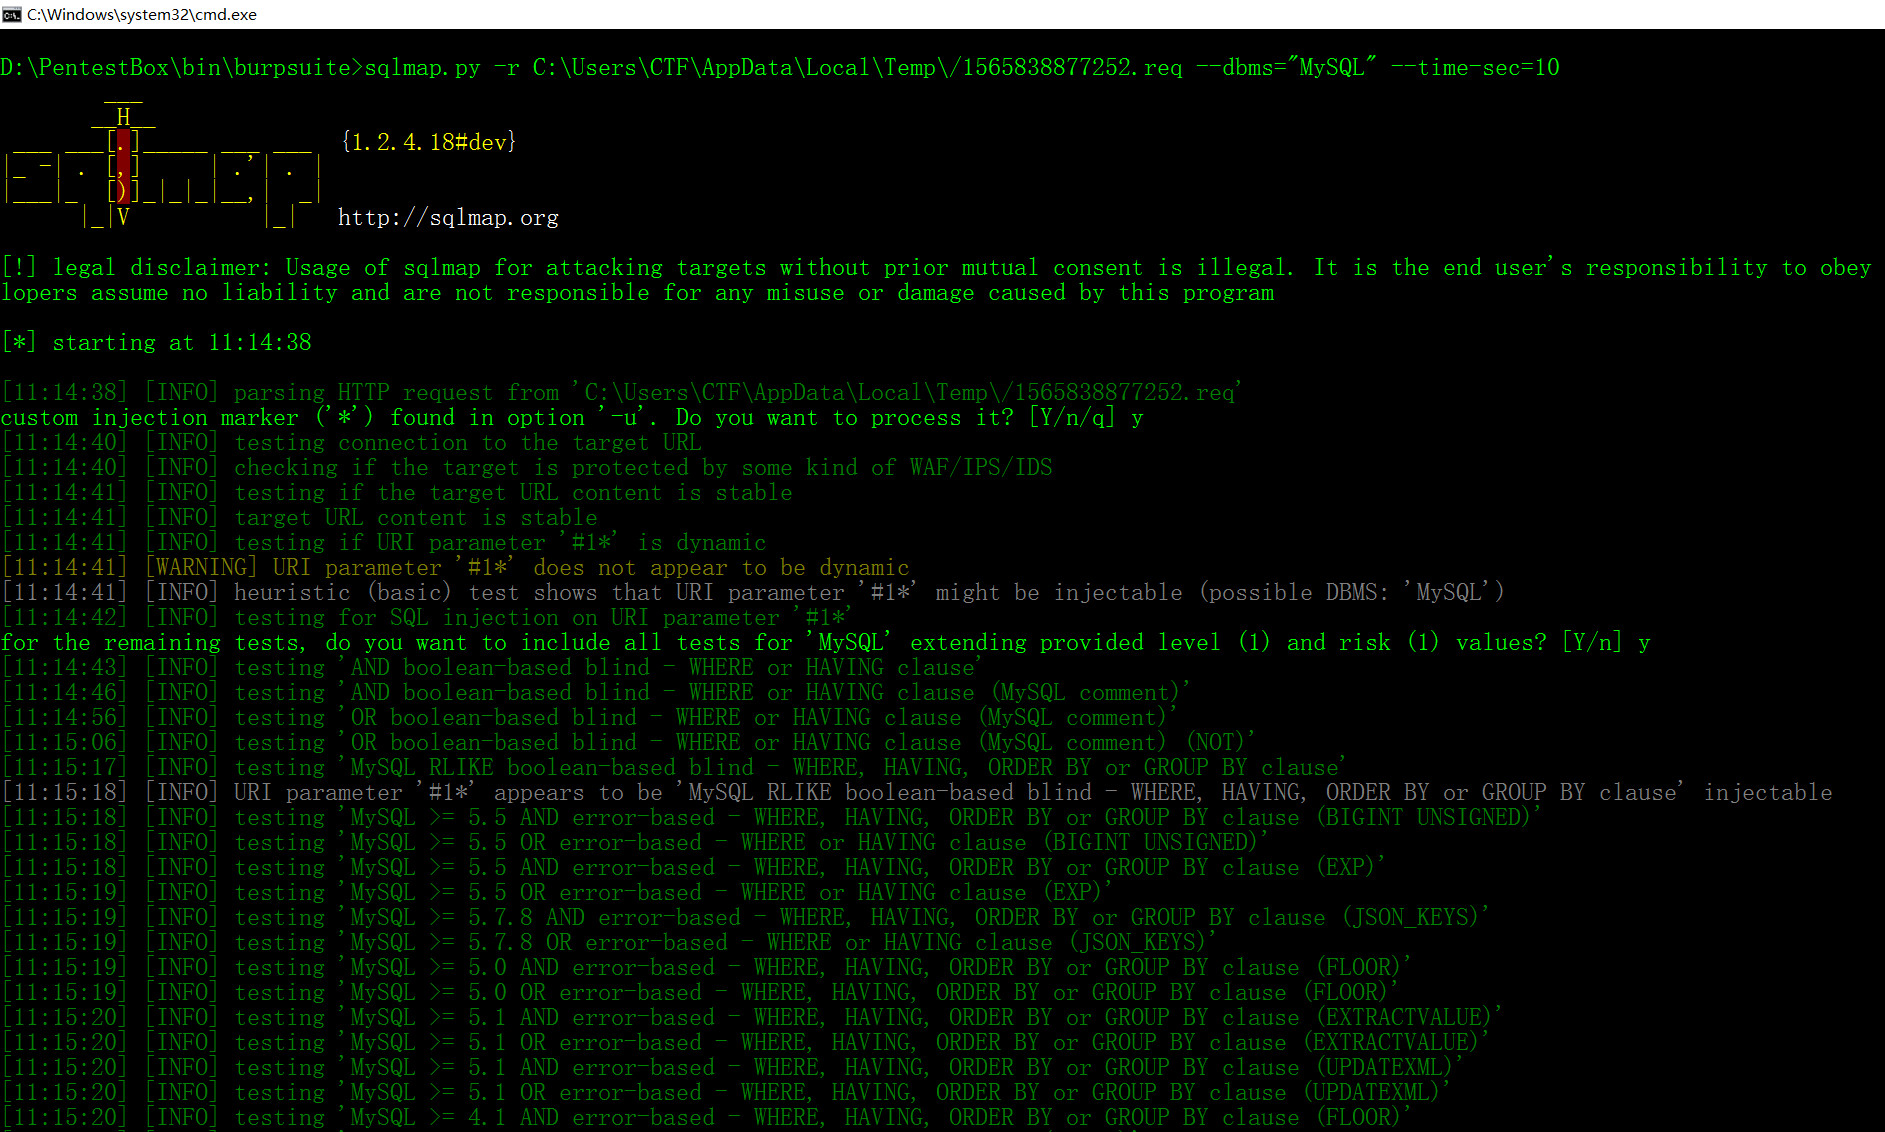 jas502n/sqlmap_burpsuite
SqlMap_BurpSuite
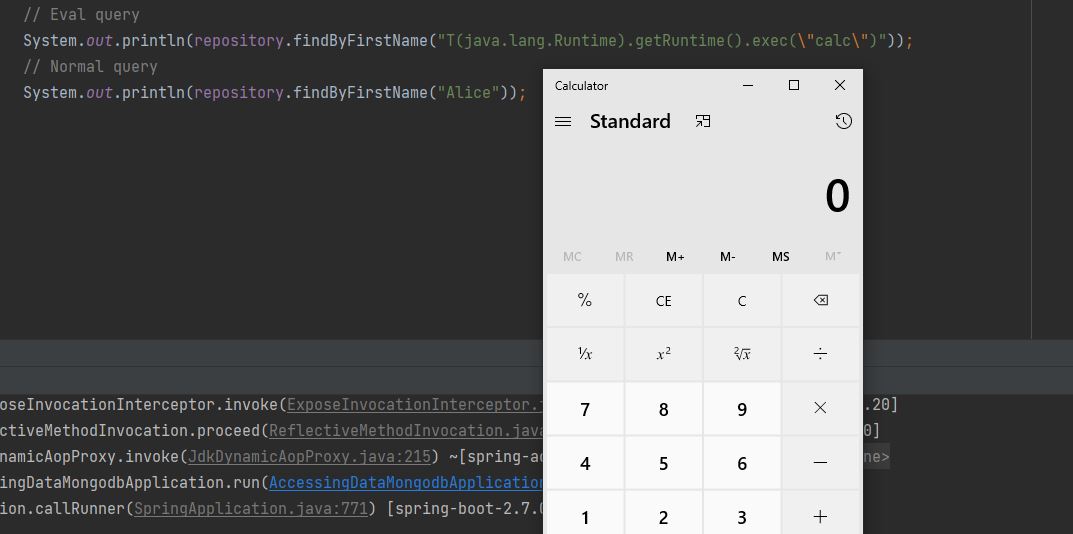 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 infobyte/isr-sqlget
ISR-sqlget It's a blind SQL injection tool developed in Perl.
 laitrungminhduc/cve-2010-3600-pythonhackoracle11gr2
This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).
 padayali-jd/cve-2025-22964
Proof-of-concept exploit for CVE-2025-22964, a time-based blind SQL injection vulnerability in DDSN Interactive cm3 Acora CMS 10.1.1, enabling…
 knqyf263/cve-2018-6376
Proof-of-concept exploit for CVE-2018-6376, a second-order SQL injection vulnerability in Joomla! CMS, with Docker-based test environment.
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 jimywork/stretcher
Tool designed to help identify open Elasticsearch servers that are exposing sensitive information
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…