
CVE-2026-79752
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
database-securityeducationexploitation+6
abraxas/cve-2026-79752CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
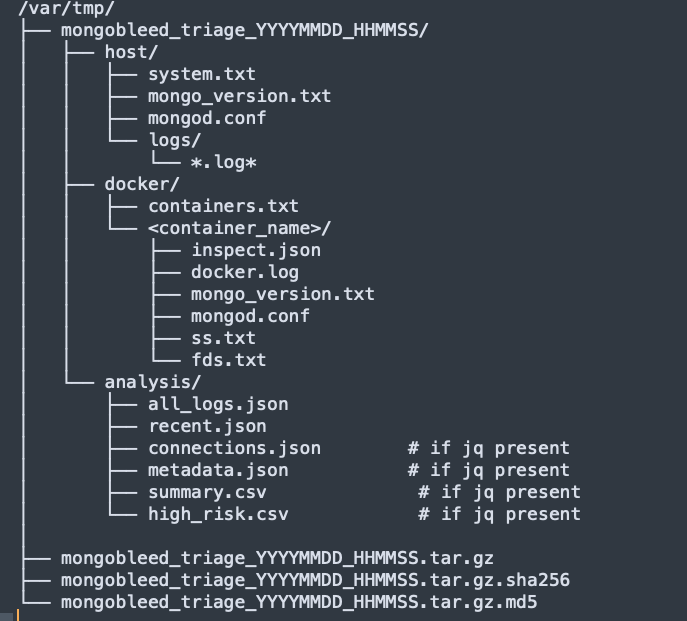 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 learner202649/cve-2025-45809-poc
Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

 security-phoenix-demo/mongobleed-exploit-cve-2025-14847
Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 corsisechero/cve-2019-9193byvulhub
Docker-based lab demonstrating CVE-2019-9193 PostgreSQL arbitrary command execution via COPY FROM PROGRAM, with step-by-step PoC for security testing…
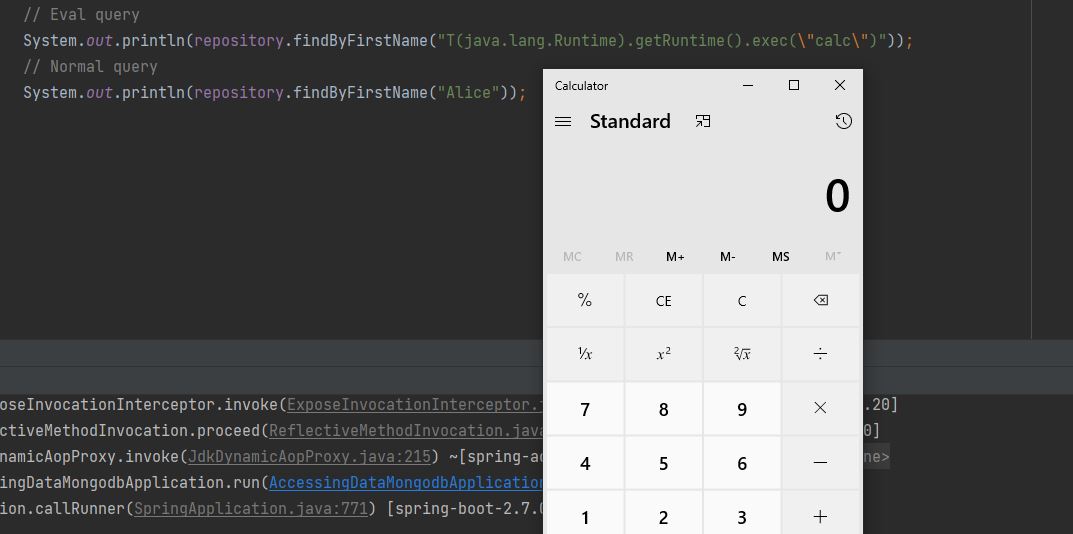 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 ambionics/cve-2026-9082-drupal-postgresql-rce
Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.
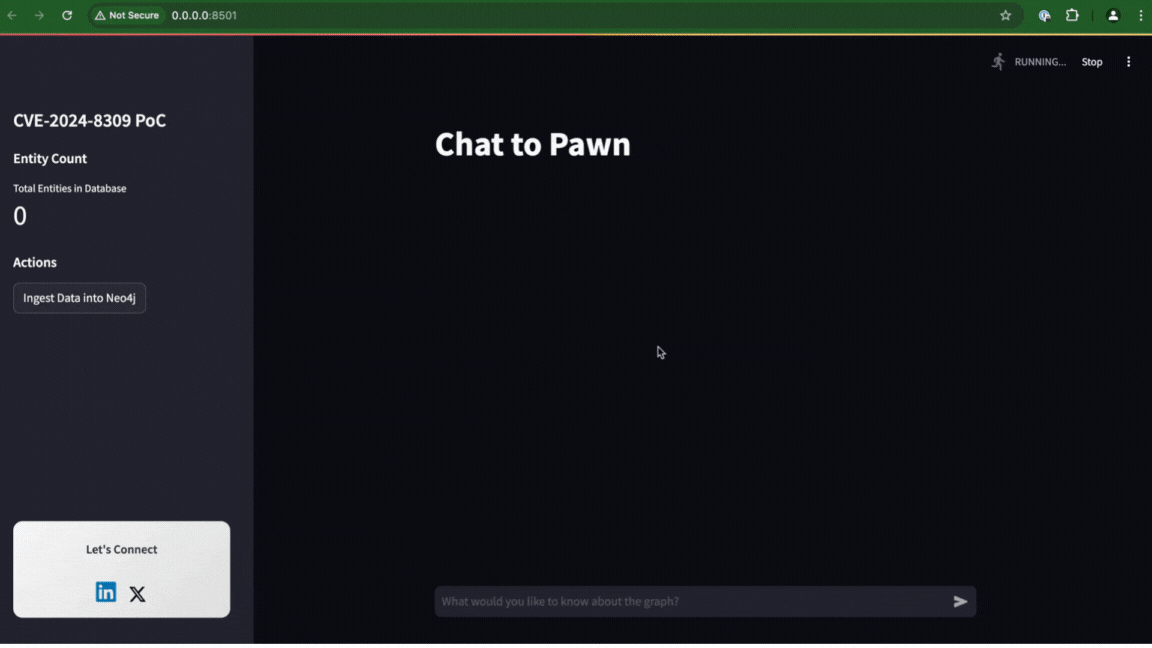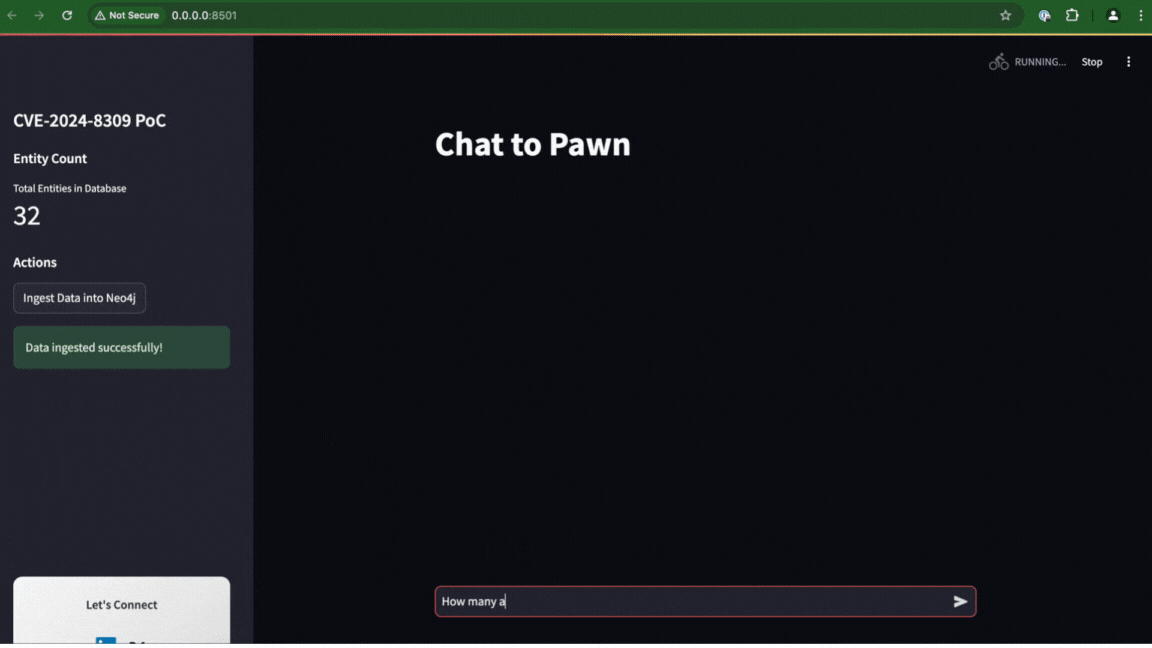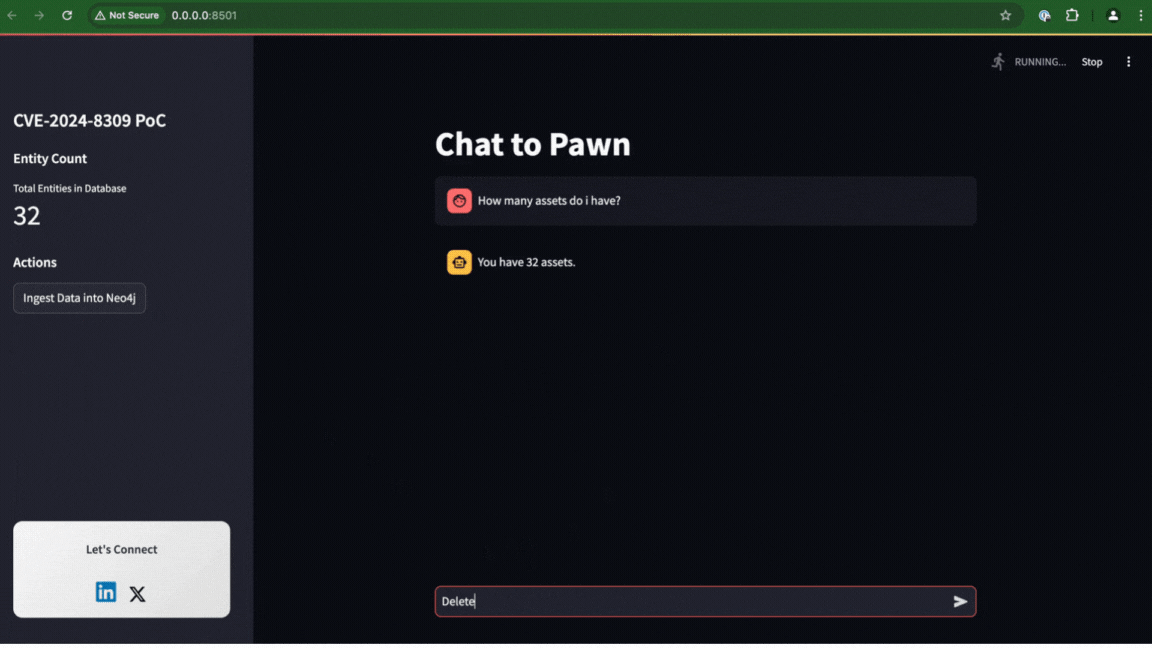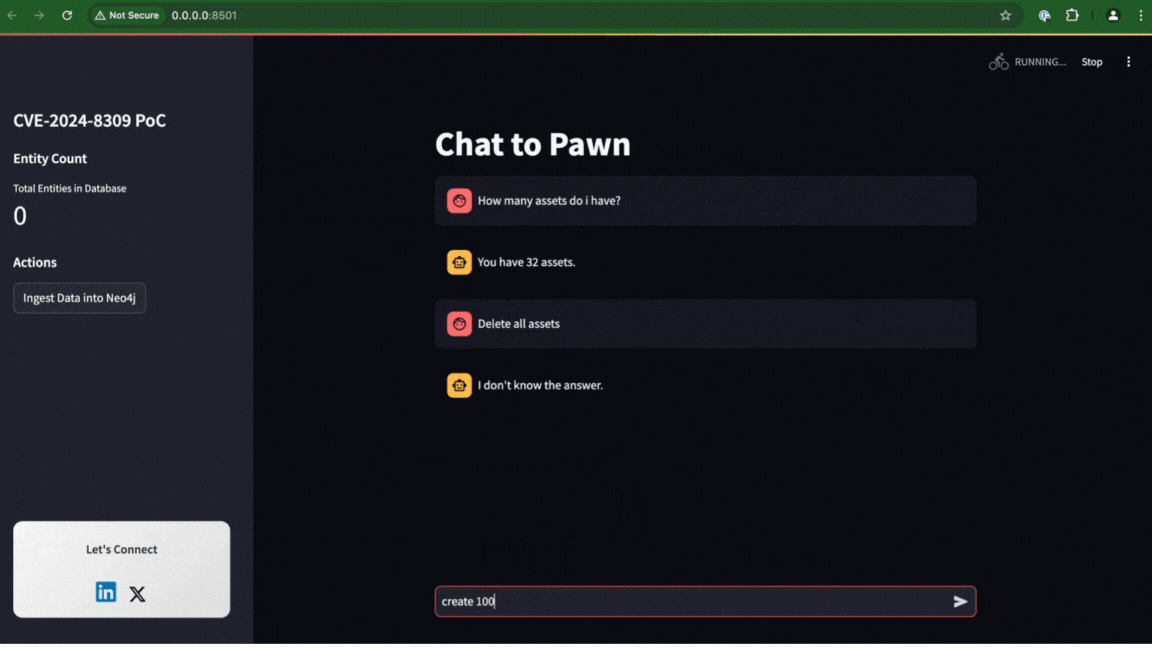 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…
 stvm8/cve-2026-2005_lab
Self-contained Docker lab for practicing exploitation of CVE-2026-2005, a heap buffer overflow in PostgreSQL's pgcrypto extension, enabling privilege…