CVE-2026-78804_Dolibarr_authenticated_SQL_injection

The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…

The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…

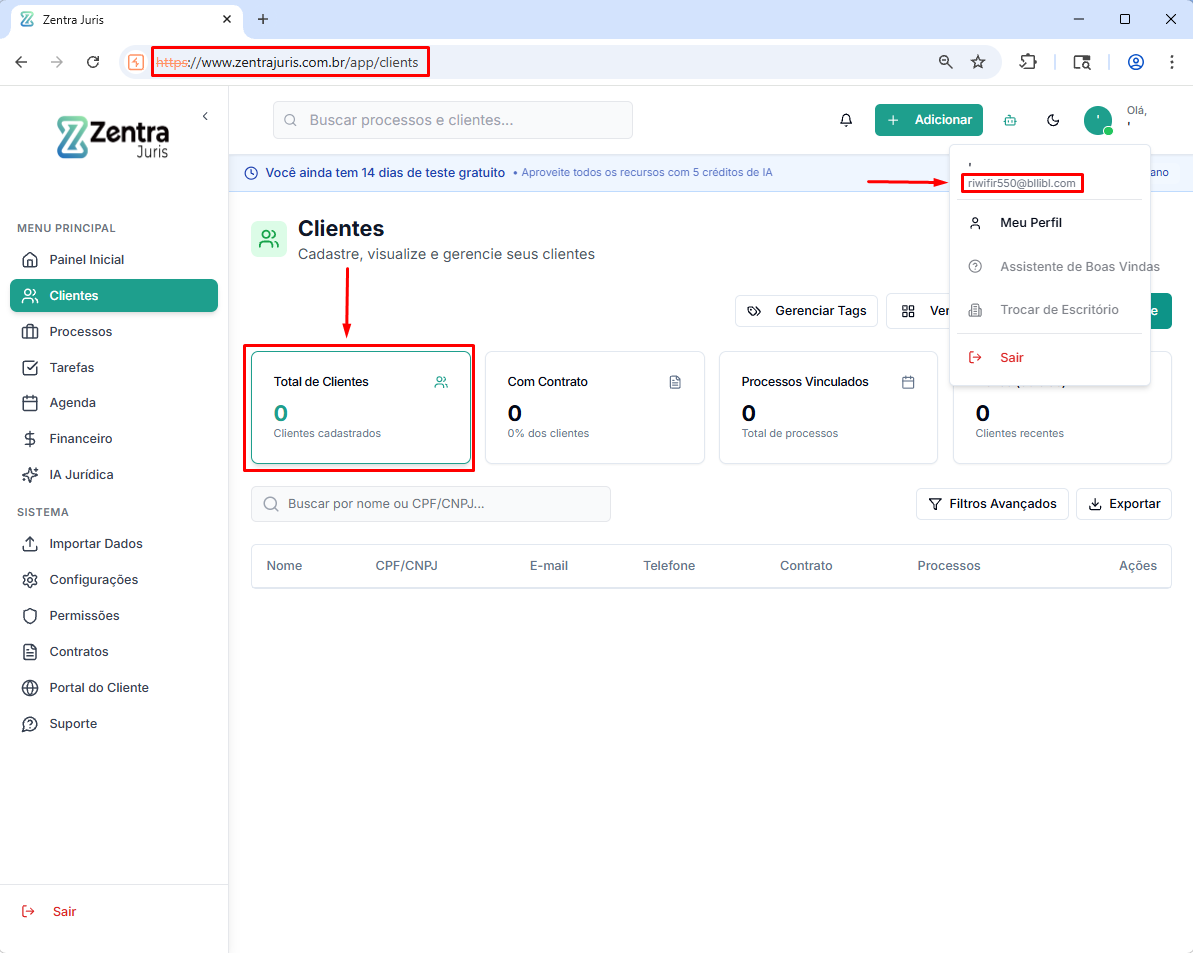
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…

Moodle 5.2.3 - High - Remote - SQLi - enrol_database concatenates course idnumber into SQL

CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL

POCs to demonstrate CVE-2026-42167 in ProFTPD

CVE-2026-72898

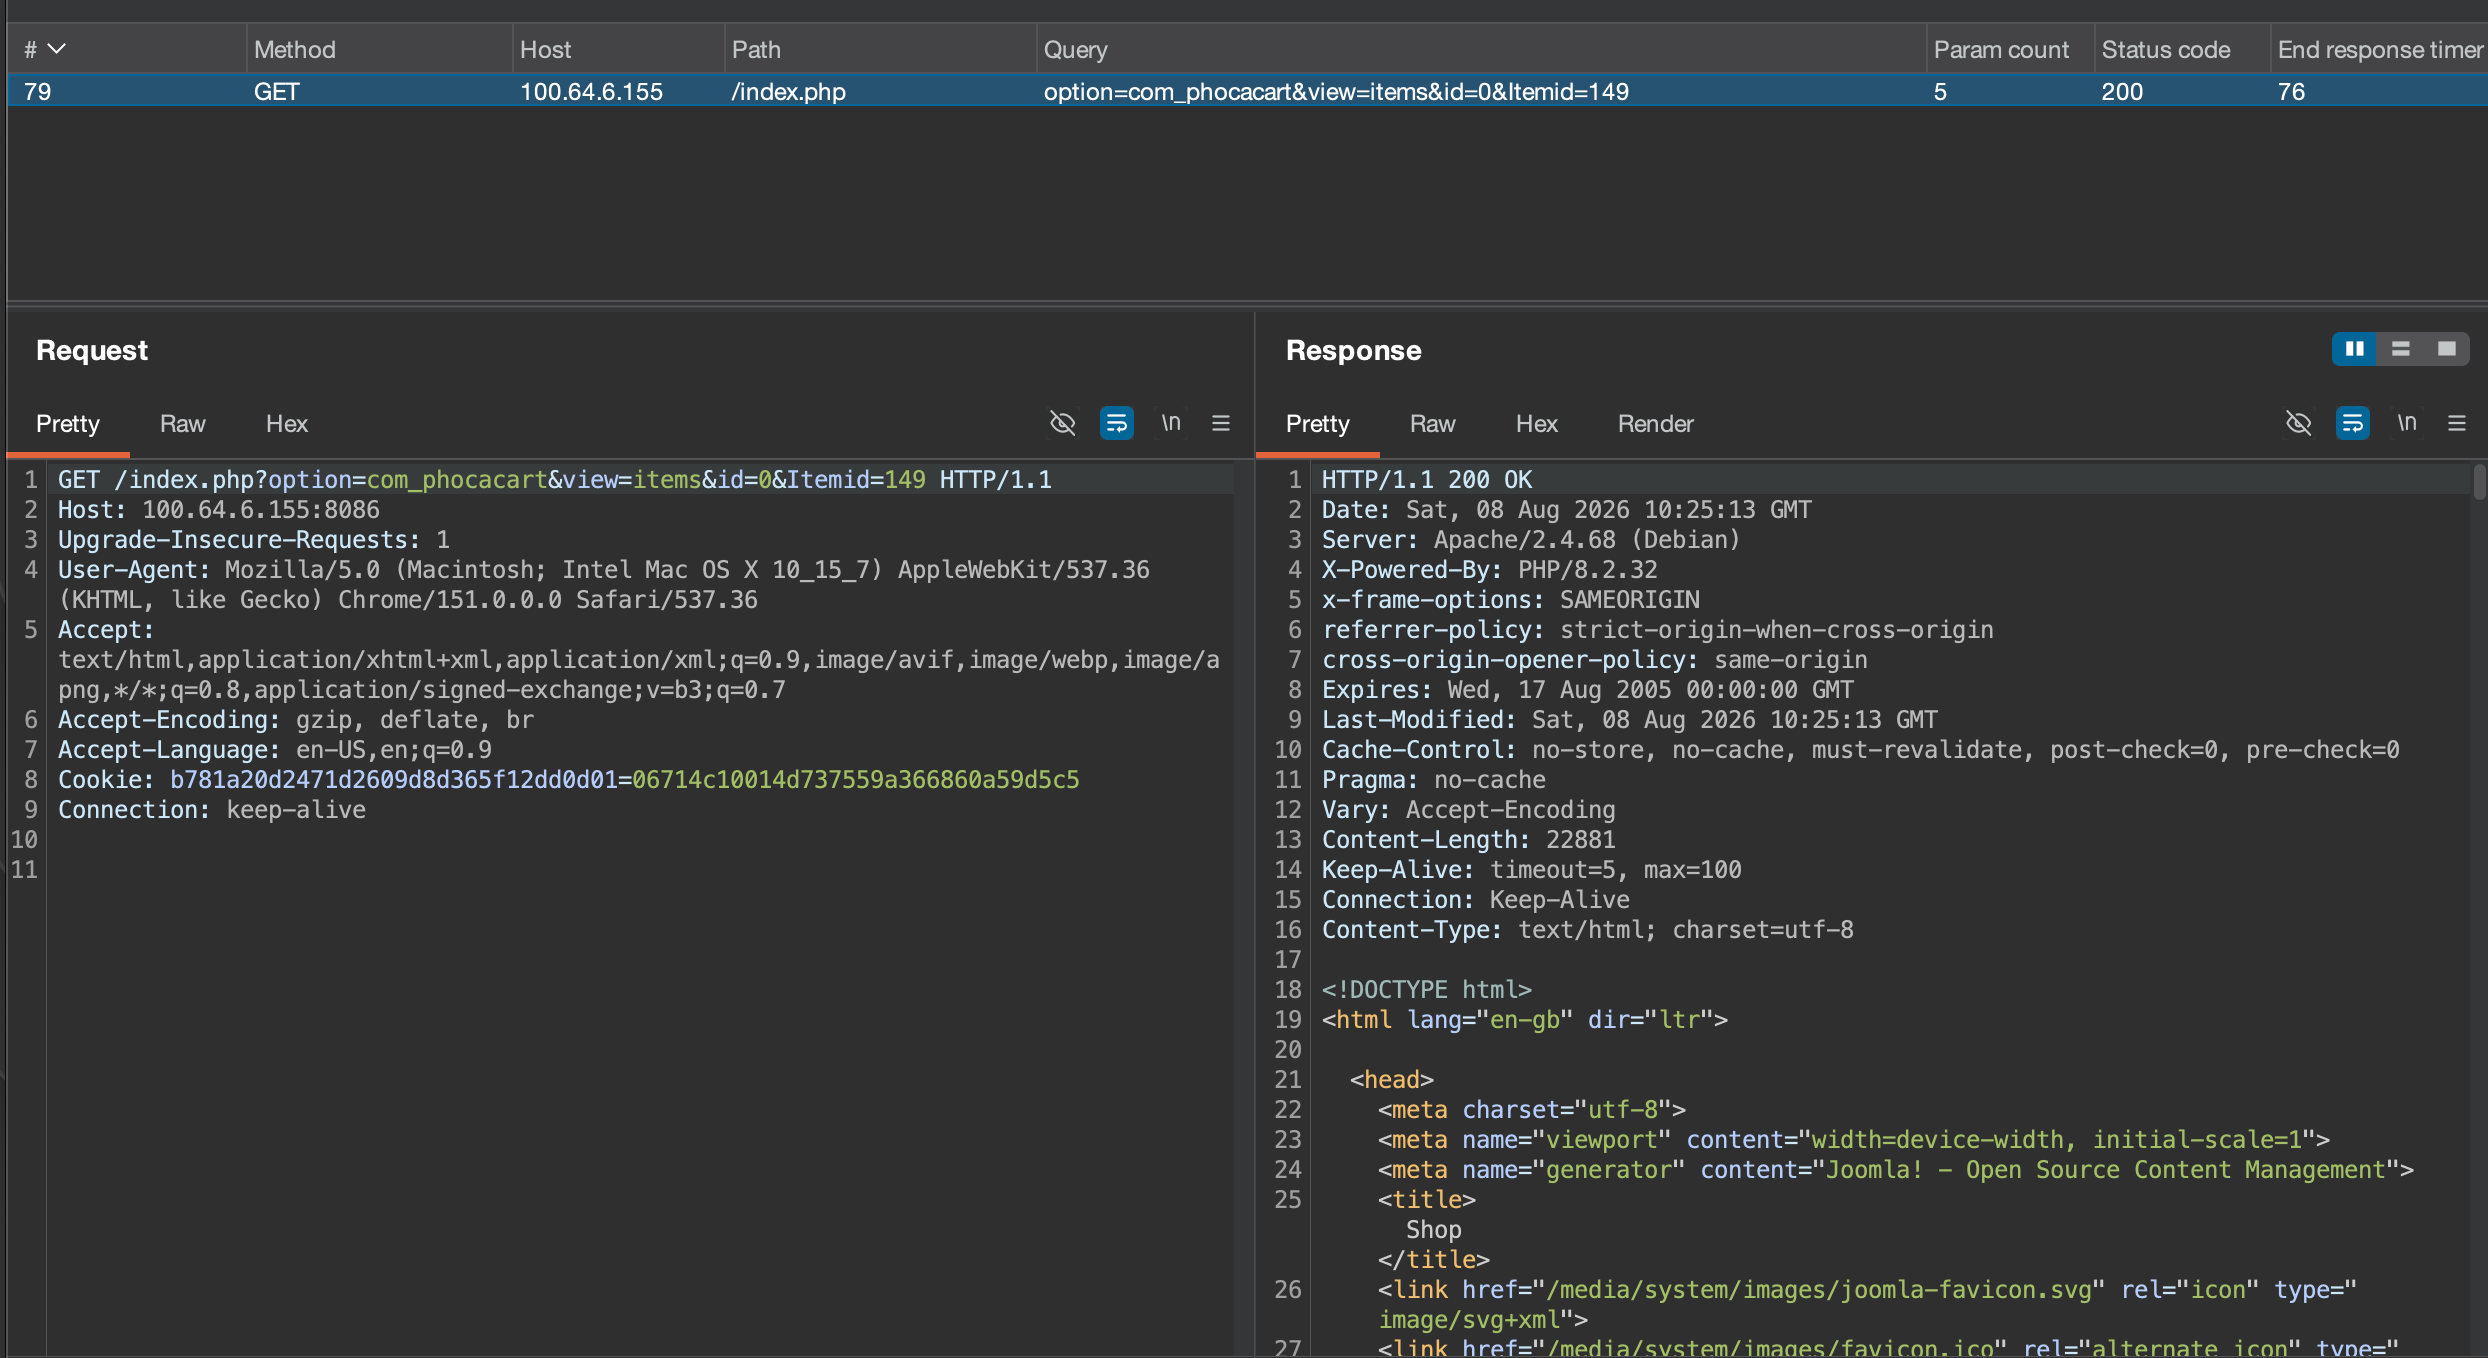
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3

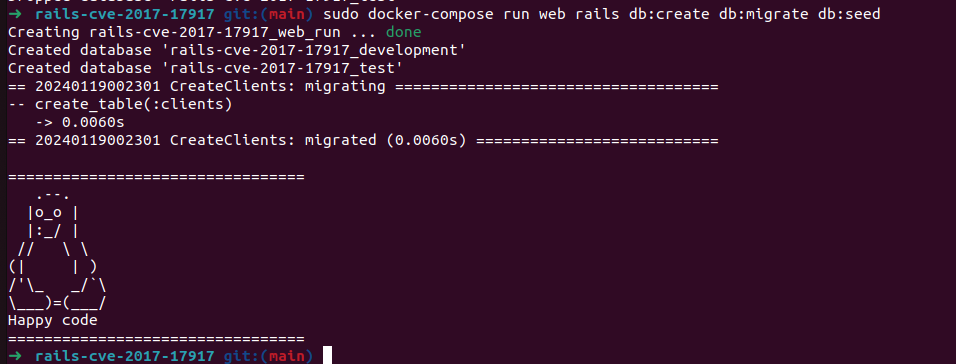
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…

Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…