
custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 secforce/cve-2008-1613
RedDot CMS versions 7.5 Build 7.5.0.48 and below full database enumeration exploit that takes advantage of a remote SQL injection vulnerability in…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
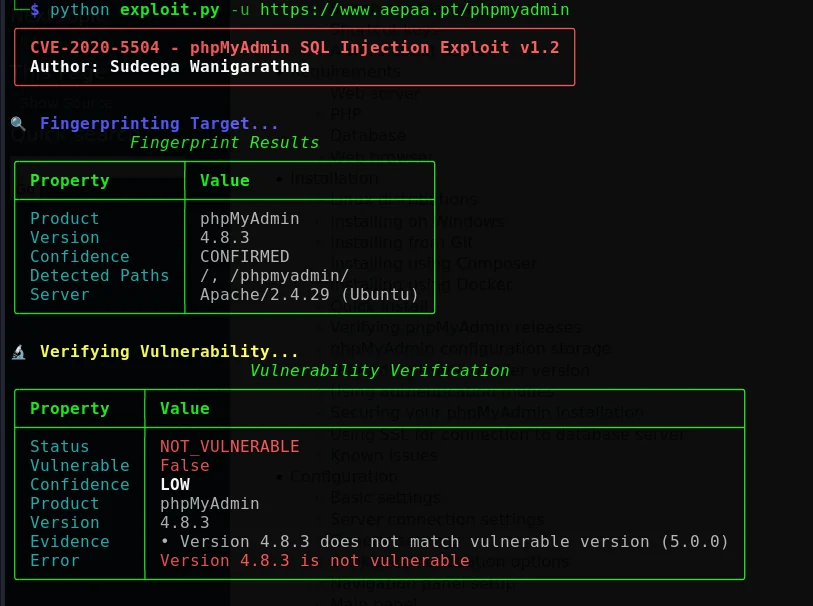 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 fantasy-fql/esapi-sqlinjection-cve-2025-5878-exploit
Exploit for CVE-2025-5878 targeting ESAPI's encodeForSQL() method with OracleCodec, enabling time-based blind SQL injection. Supports database…
 msd0pe-1/cve-2023-31714
Proof-of-concept exploit for CVE-2023-31714, a pre-authentication SQL injection in Chitor-CMS < 1.1.2. Automates database enumeration and credential…
 zsy107u/cve-2025-2011-poc
Proof-of-concept exploit for CVE-2025-2011, a SQL injection vulnerability in WordPress Depicter Plugin 3.6.1, enabling database enumeration and data…
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.