LDAP-Password-Hunter

Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…

Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…

Proof of Concept (PoC) for SQL Injection in Xhibiter NFT Marketplace 1.10.2 (Collections Endpoint). Discovered by Sohel Yousef.

Find open databases - Powered by Binaryedge.io

A Python Framework For NoSQL Scanning and Exploitation

Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.

SQLi ITC Multiplan v3.7.4.1002 (CVE-2025-29529)

The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.

A simple and quick way to check if your SQL Developer by Oracle is vulnerable to SQL Injection (CVE-2023-3163), most commonly occurs when SQL…

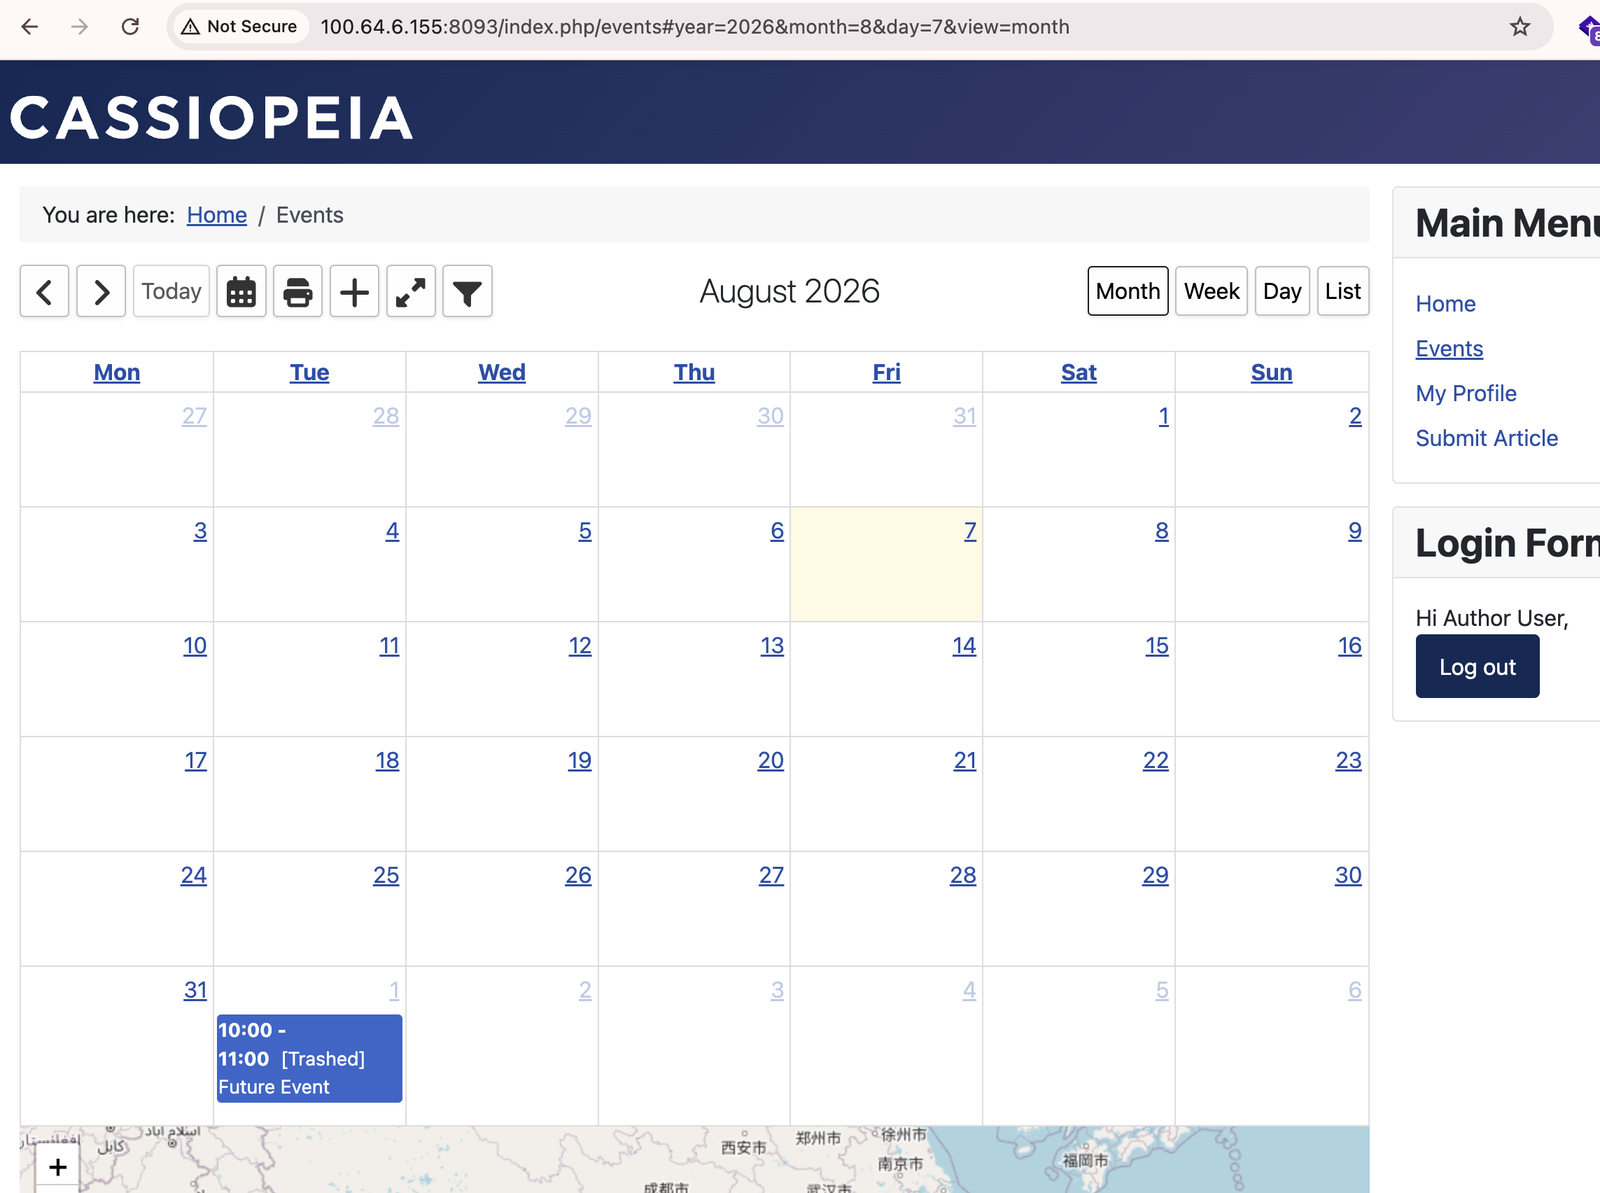
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2

Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…

Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…

Fixes unauthenticated SQL injection in a setup endpoint by replacing raw JDBC queries with ORM parameterization and constant-time token validation.

Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

Working POC of CVE-2026-6664 written by Sonnet 4.6

It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…

A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.

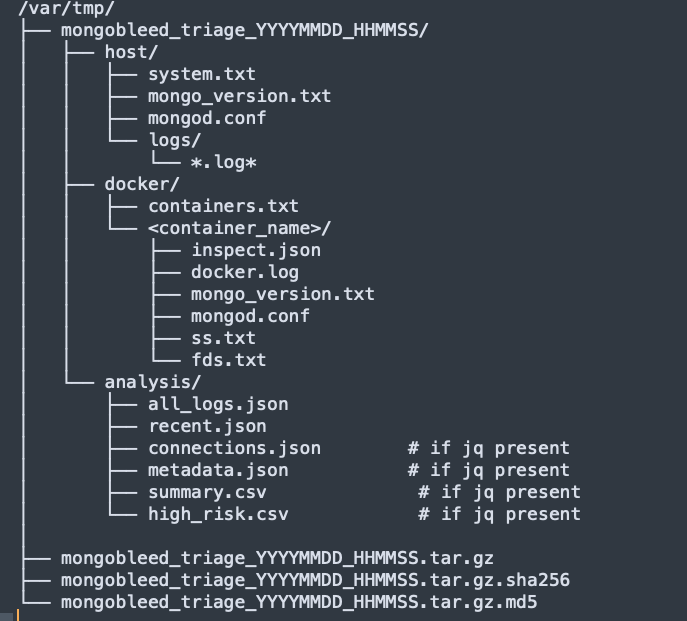
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…