
MySQL-Fu.rb
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
database-securityexploitationpayload-generation+3
3
hood3drob1n/mysql-fu.rbMySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 sadshade/cve-2022-24706-couchdb-exploit
Apache CouchDB 3.2.1 - Remote Code Execution (RCE)
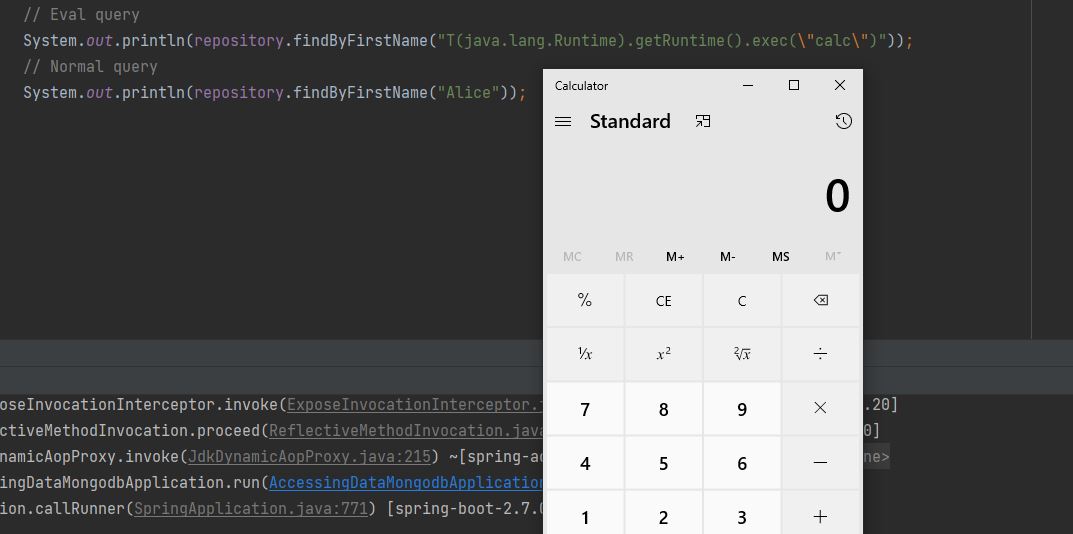 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 tw1sm/pysqlrecon
Offensive MSSQL toolkit written in Python, based off SQLRecon
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 aneeshanilkumar89/maximo_sql_injection-cve-2019-4650
MAximo SQL Injection Time Based - Oracle DB
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
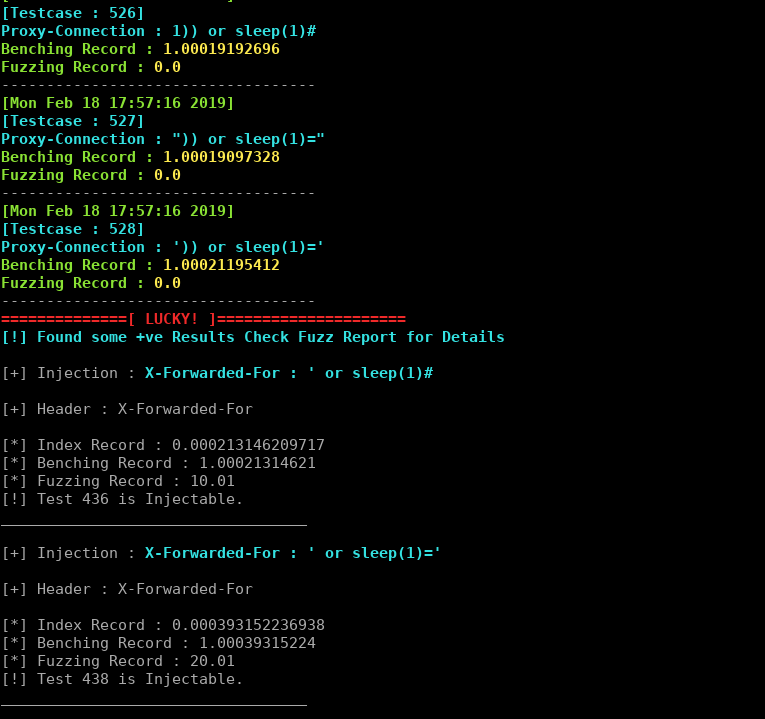 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 mhaskar/blinder
A python library to automate time-based blind SQL injection
 var77/cve-2026-2005
PoC for CVE-2026-2005
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC