

MongoBleed-CVE-2025-14847
 systemhaus-schulz/mongobleed-cve-2025-14847
MongoBleed CVE-2025-14847 Vulnerability Checker
database-securityexploitationinformation-gathering+3
systemhaus-schulz/mongobleed-cve-2025-14847MongoBleed CVE-2025-14847 Vulnerability Checker
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
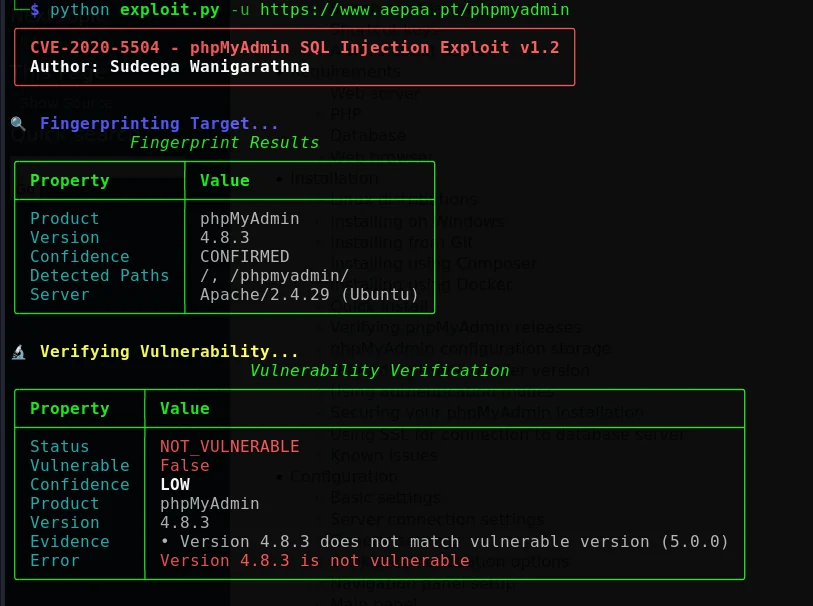 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
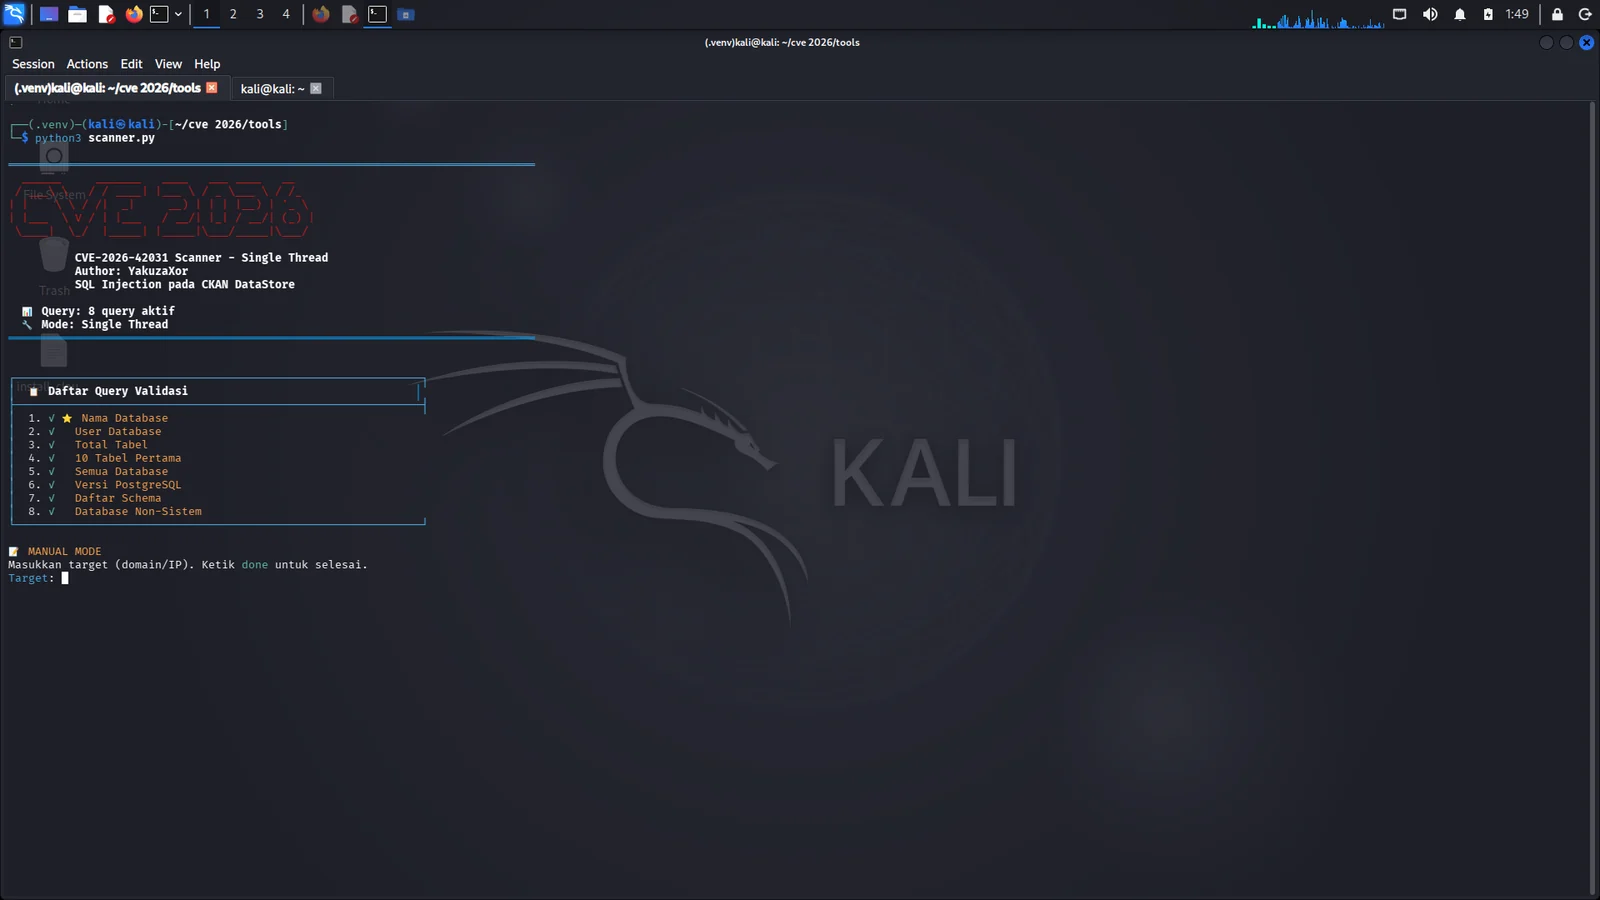 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 brynax/cve-2026-30655
Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…