

web2py-e94946d-CVE-2016-3957
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
authenticationcode-analysisdatabase-security+3
sj/web2py-e94946d-cve-2016-3957web2py/web2py @ e94946d
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 aneeshanilkumar89/maximo_sql_injection-cve-2019-4650
MAximo SQL Injection Time Based - Oracle DB
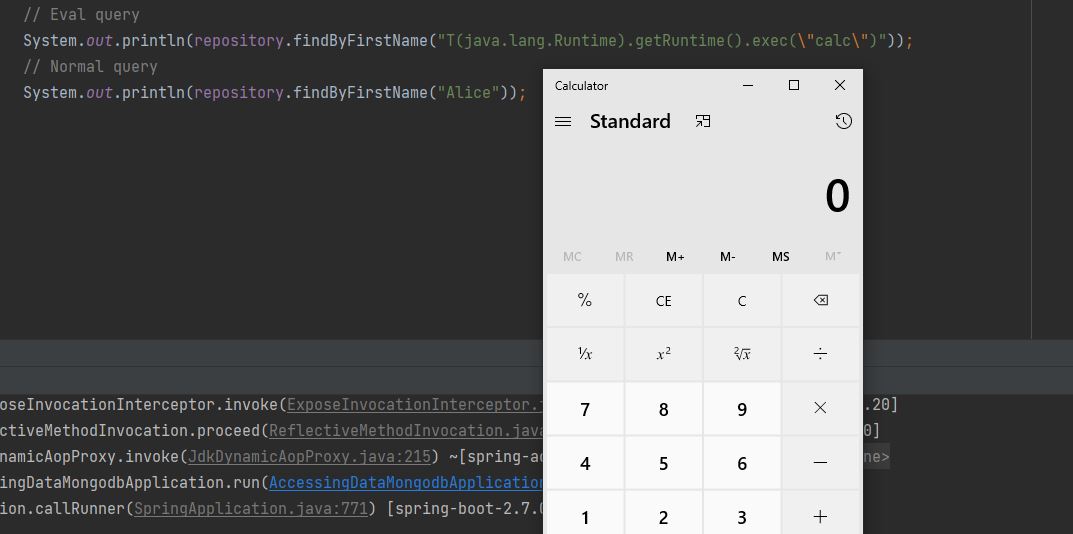 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 giangdurian/cve-2023-25157-geoserver-sqli-lab
Docker-based vulnerable lab and detailed PoC report for CVE-2023-25157/25158 SQL injection in GeoServer & GeoTools, with 4 verified attack vectors…
 padayali-jd/cve-2025-22964
Proof-of-concept exploit for CVE-2025-22964, a time-based blind SQL injection vulnerability in DDSN Interactive cm3 Acora CMS 10.1.1, enabling…
 shubham03007/cve-2025-28346
Code-projects Ticket Booking 1.0 is vulnerable to SQL Injection via the > Email parameter
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
 tkomlodi/cve-2022-23305_poc
CVE-2022-23305 Log4J JDBCAppender SQl injection POC
 kabir0104k/cve-2025-66947
Proof-of-concept for time-based blind SQL injection in a PHP admin panel. Demonstrates exploitation via unsanitized GET parameter, with mitigation…
 moritakaaz/cve-2025-11391
WordPress PPOM for WooCommerce Plugin <= 33.0.15 is vulnerable to SQL Injection