
Gopherus
 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
database-securityexploitationpayload-generation+3
3.4k4 years ago
tarunkant/gopherusThis tool generates gopher link for exploiting SSRF and gaining RCE in various servers
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
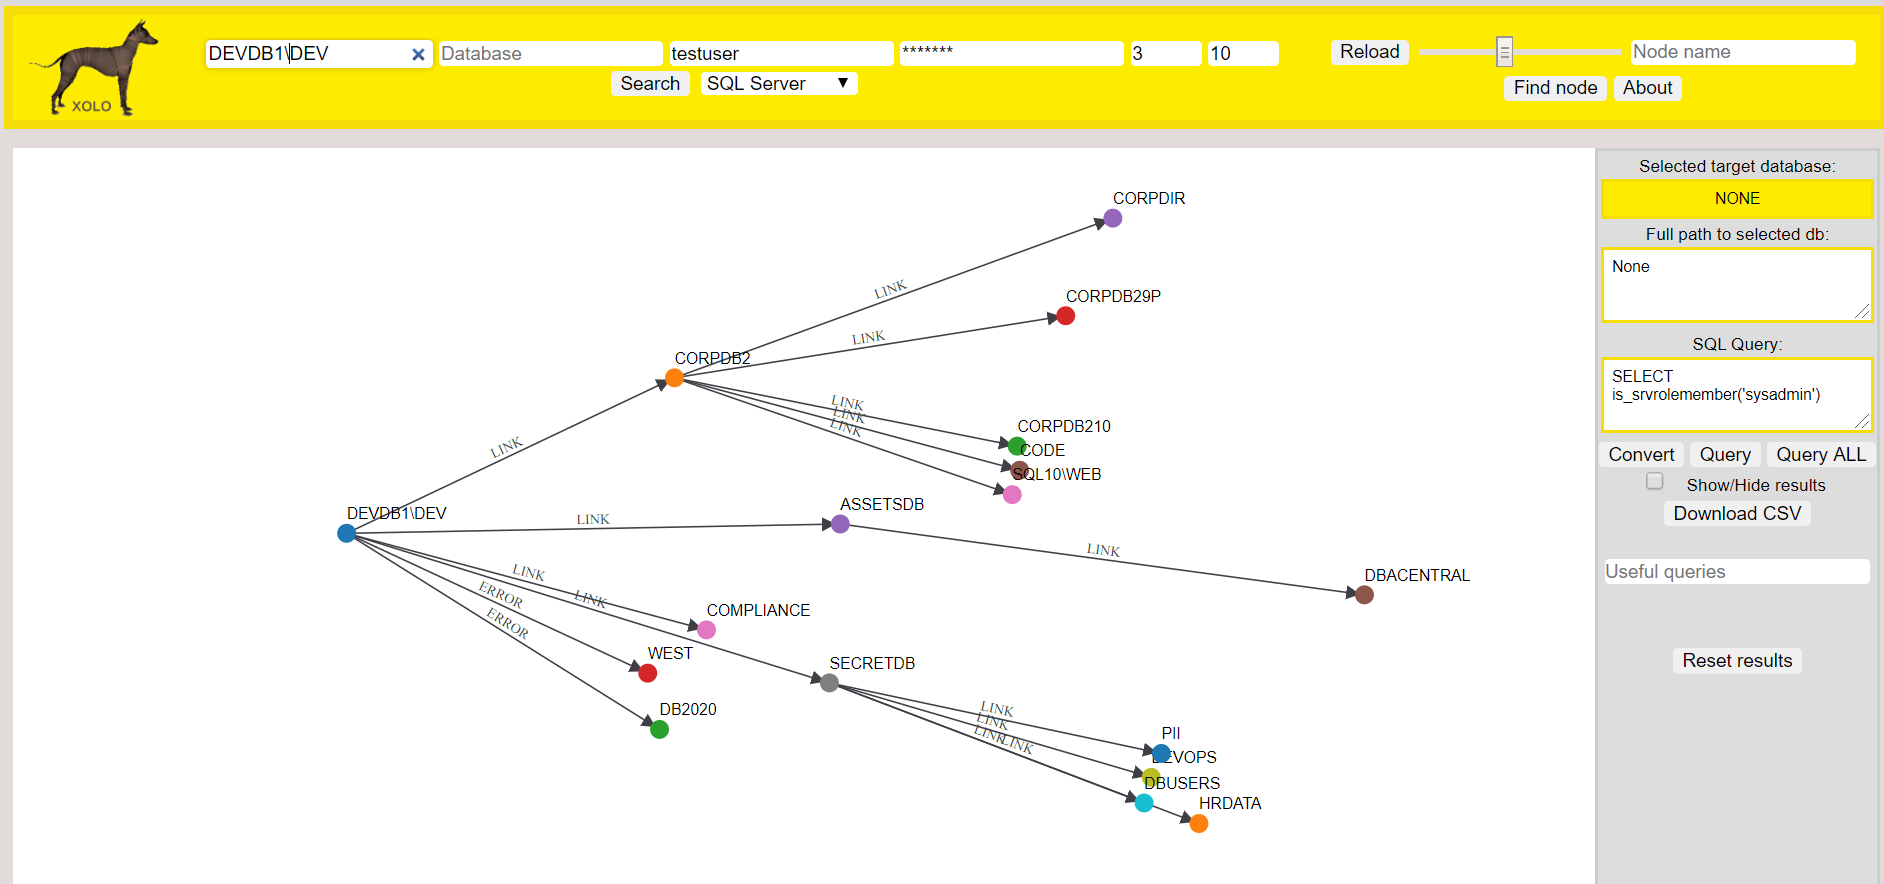 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 jimywork/stretcher
Tool designed to help identify open Elasticsearch servers that are exposing sensitive information
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
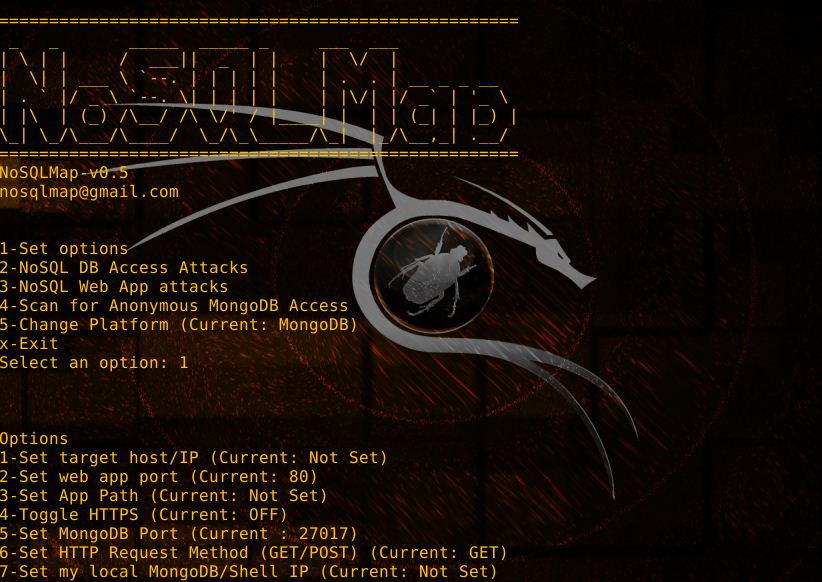 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 oldboy21/ldap-password-hunter
Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
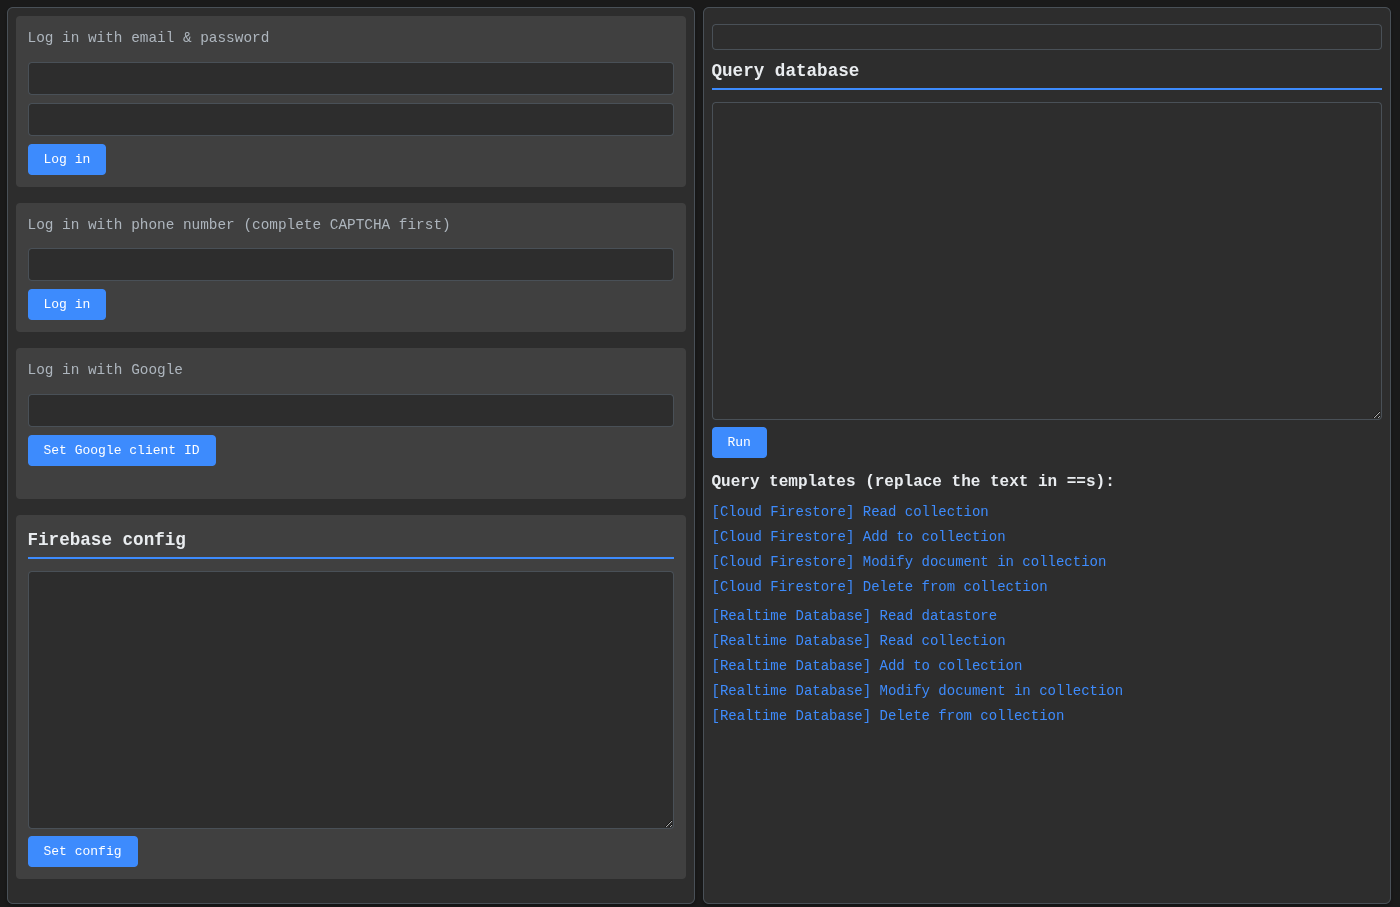 iosiro/baserunner
A tool for exploring Firebase datastores.
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137