

wp2shell-compromise-scanner-plugin
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
database-securitydigital-forensicsforensics+5
eyesecurity/wp2shell-compromise-scanner-pluginRead-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 konstantin-kelemen/mysqld_safe-cve-2016-6662-patch
Ansible playbook that applies the Percona patch for CVE-2016-6662 to the mysqld_safe file on CentOS and FreeBSD systems.
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
 randomrobbiebf/cve-2023-45657
Nexter <= 2.0.3 - Authenticated (Subscriber+) SQL Injection via 'to' and 'from'
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)

 al1ex/cve-2021-27928
CVE-2021-27928 MariaDB/MySQL-'wsrep provider' 命令注入漏洞
 vuxnx/cve-2026-72898
Proof-of-concept exploit for CVE-2026-72898, targeting Toucan2 behavior with malformed map options to reproduce the vulnerability and validate…
 kamal-marouane/cve-2022-28346
A flaw was found in the Django package, which leads to a SQL injection. This flaw allows an attacker using a crafted dictionary containing malicious…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 agarma/cve-2020-24913-poc
A Poc for CVE-2020-24913, a SQL injection vulnerability in qcubed (all versions including 3.1.1) in profile.php via the strQuery parameter allows an…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
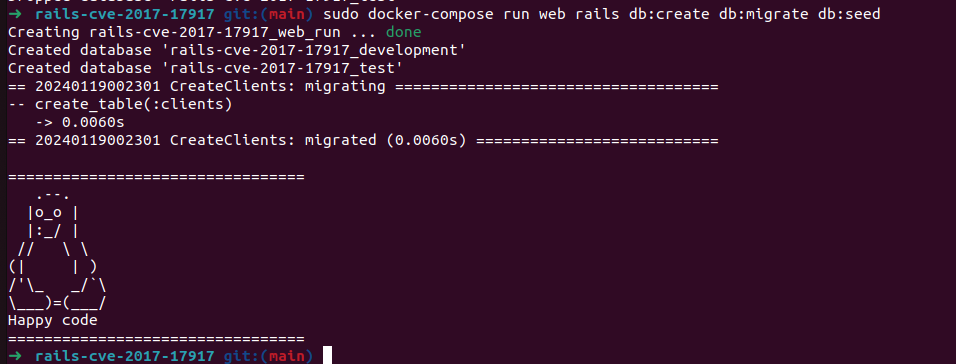 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 torque59/nosqlpot
The NoSQL Honeypot Framework