

CVE-2026-26980
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
database-securitydata-exfiltrationexploitation+4
10
vognik/cve-2026-26980Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 security-phoenix-demo/mongobleed-exploit-cve-2025-14847
Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 redfr0g/cve-2023-20110
PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
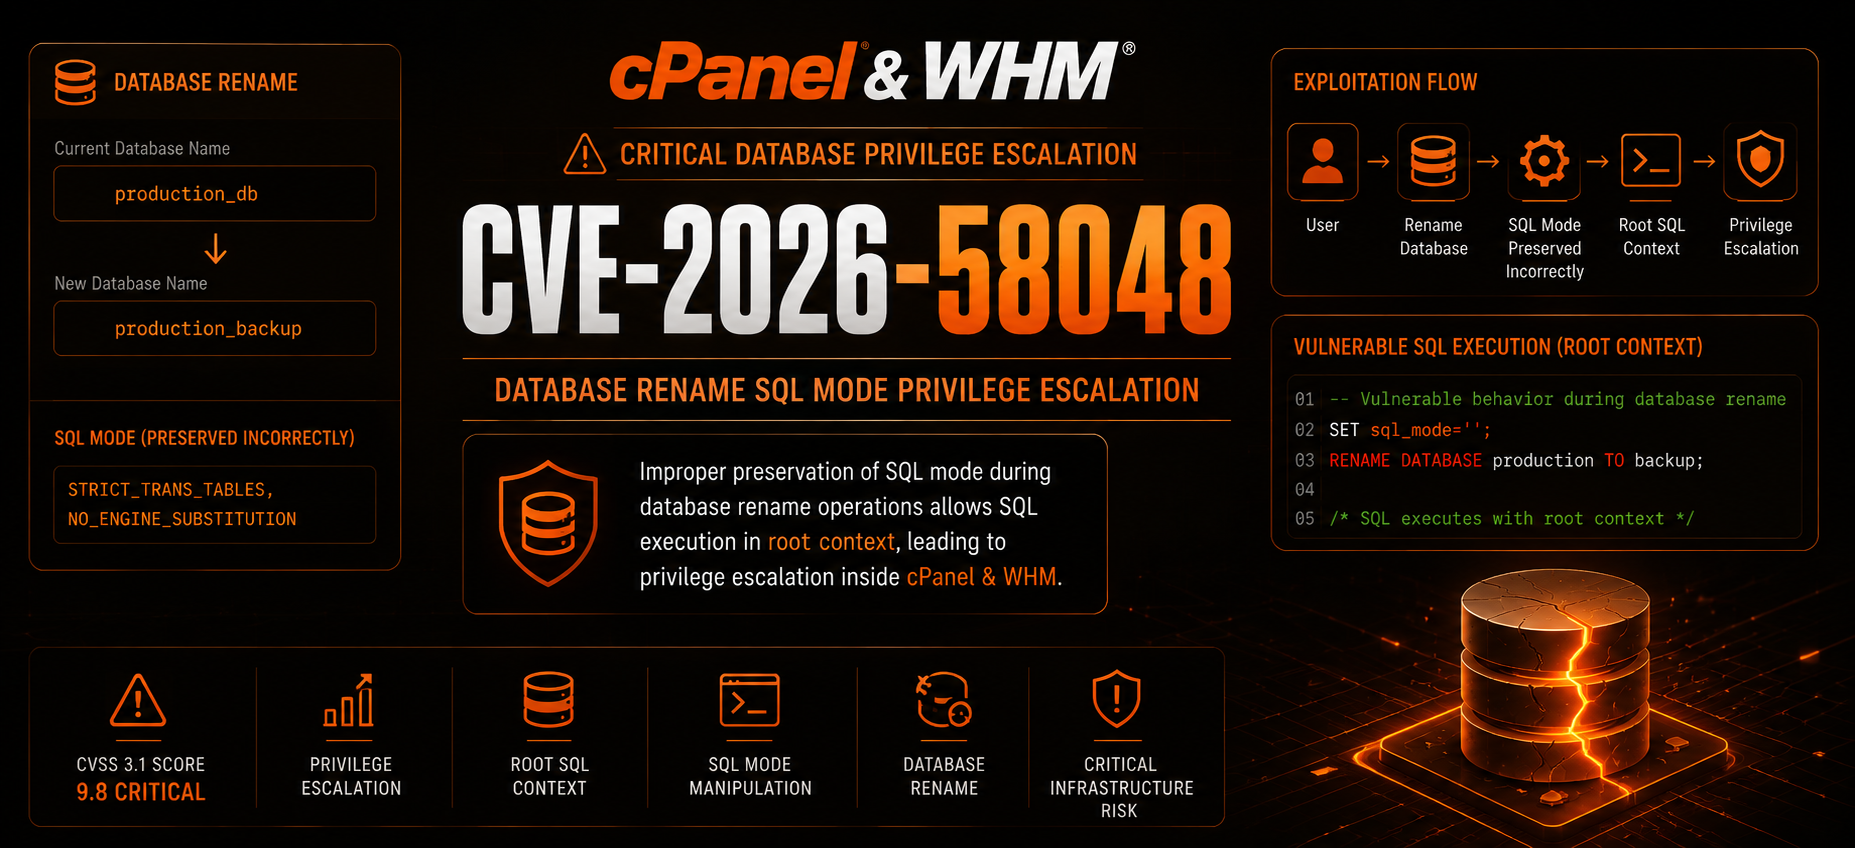 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
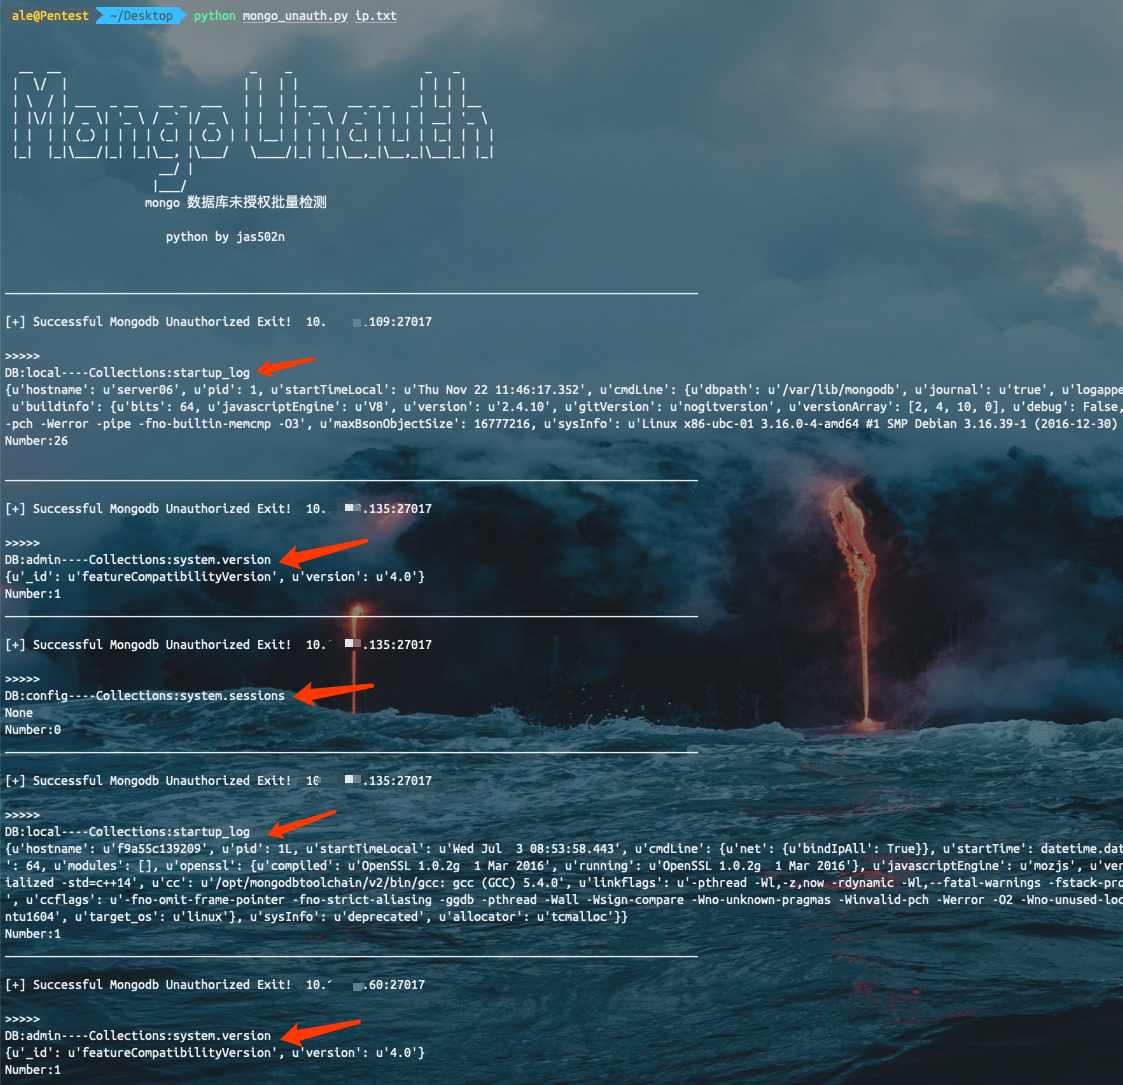 jas502n/unauthorized-tools
未授权批量检测脚本
 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
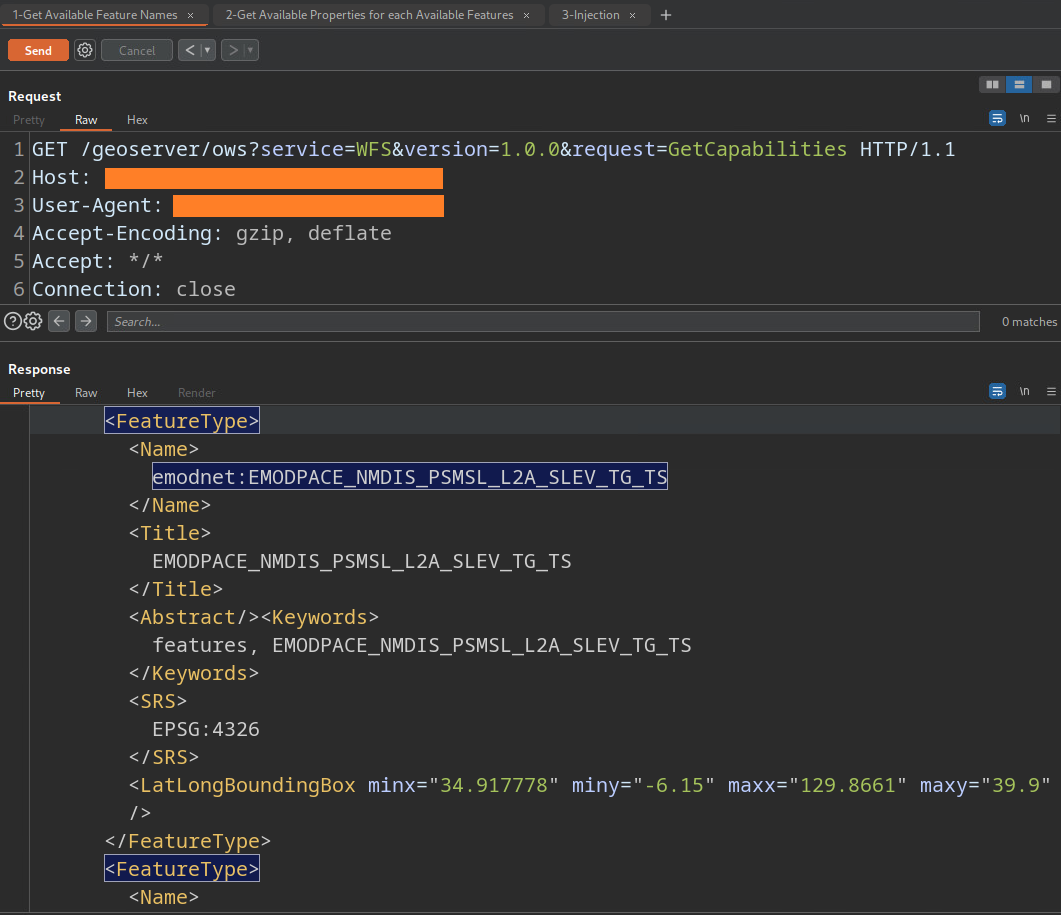 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 altelus1/cve-2022-24707
PoC of CVE-2022-24707
 0xblackash/cve-2026-72898
CVE-2026-72898
 bongbongco/cve-2012-1675
Oracle Database TNS Listener Poison Attack Vulnerability
 onewinner/cve-2025-14847
MongoDB 内存泄露漏洞 (CVE-2025-14847) 检测工具
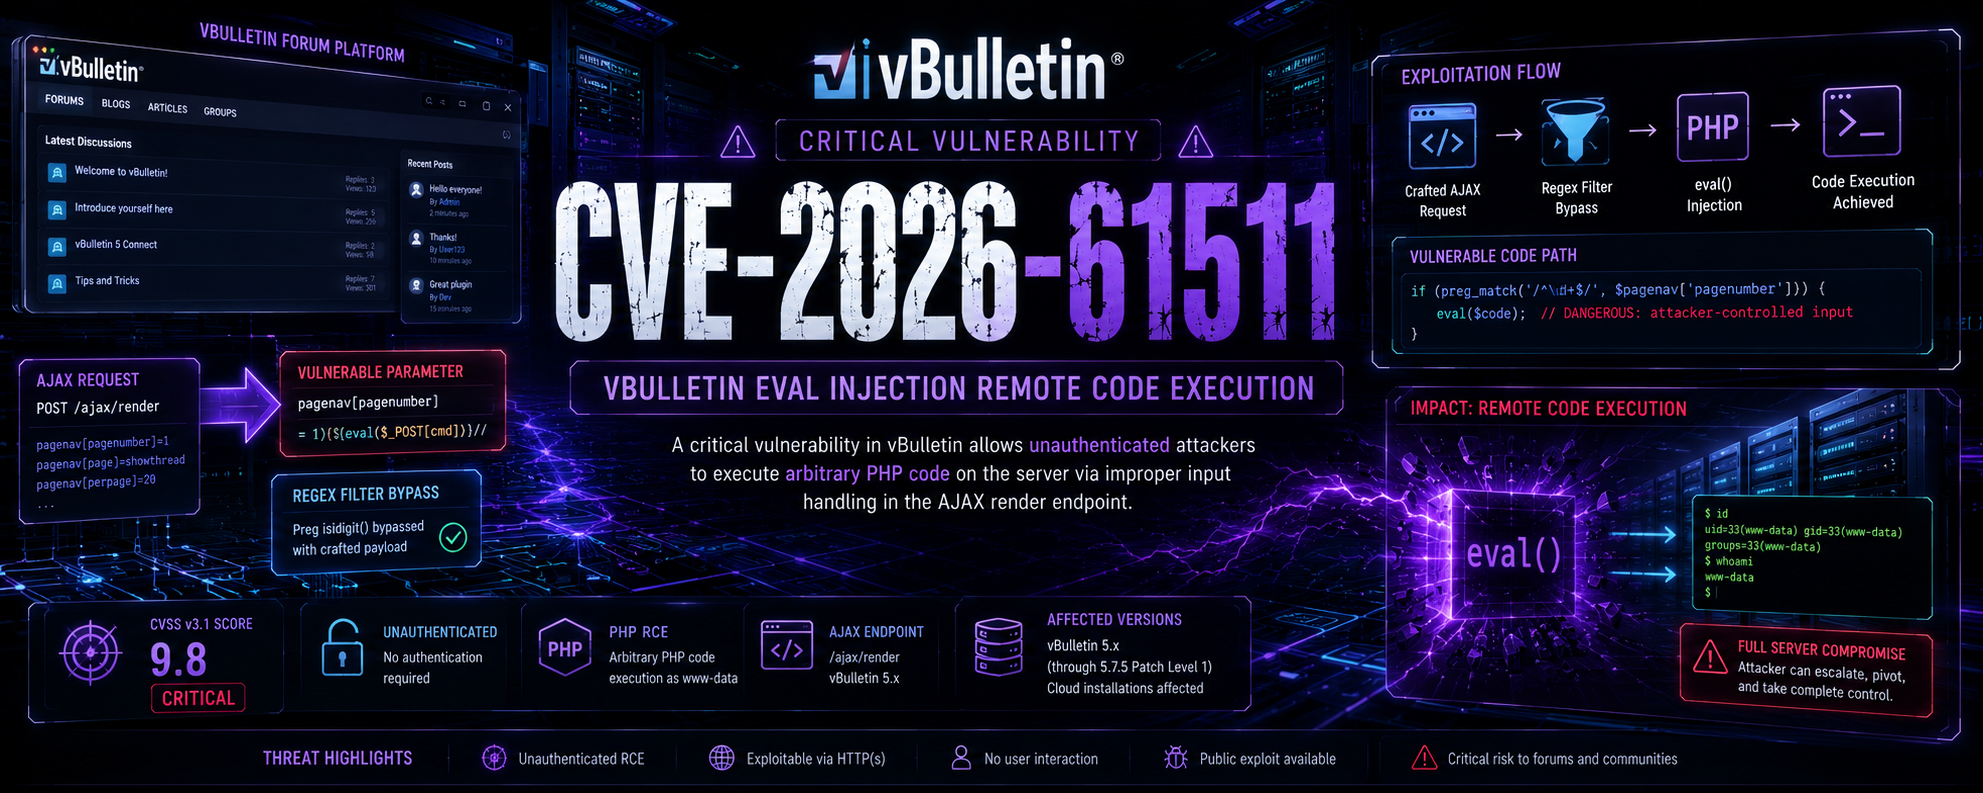 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 fsecurelabs/cisco-ucm-sqli-scripts
Scripts that can be used to exploit CVE-2019-15972 which was an Authenticated SQLi issue in Cisco Unified Call Manager (UCM).
 jas502n/sscms_decrypt
sscms database decrypt
 ambionics/cve-2026-9082-drupal-postgresql-rce
Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.