
Adminer-CVE-2021-43008
 daturasaturated/adminer-cve-2021-43008
Adminer CVE-2021-43008 PoC
database-securitydata-exfiltrationexploitation+3
daturasaturated/adminer-cve-2021-43008Adminer CVE-2021-43008 PoC
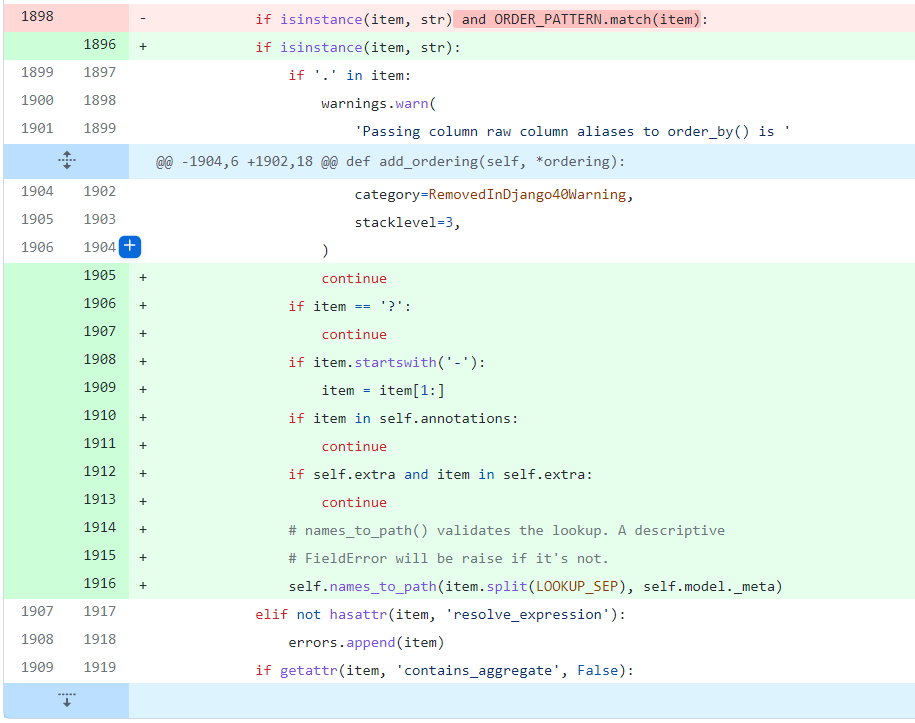 luuanhduc/cve-2021-35042
Django SQL injection vulnerability
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 rick2600/redis-stack-cve-2024-55656
Proof-of-concept exploit for CVE-2024-55656, an integer overflow in RedisBloom leading to heap-based OOB read/write and remote code execution in…
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io
 0xbug/sqliscanner
Automatic SQL injection with Charles and sqlmap api
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections