django_sqli_target_CVE-2025-64459

Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…

Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…

PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)

This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.

Open-source, cross-platform, multi-purpose security auditing tool

SolarWinds Orion Account Audit / Password Dumping Utility

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Automated testing to find logic and performance bugs in database systems

Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…

Windows Oracle Database Attack Toolkit

Detect security issues, large or small, in a CouchDB server

Detect security issues in an Apache CouchDB server

Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…

CVE-2025-14847 MongoDB Memory Leak Exploit

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

Proof-of-concept exploit for CVE-2025-14847, a MongoDB bleed vulnerability. Enables verification of vulnerable instances and understanding of attack…

The easiest, and most secure way to access and protect all of your infrastructure.

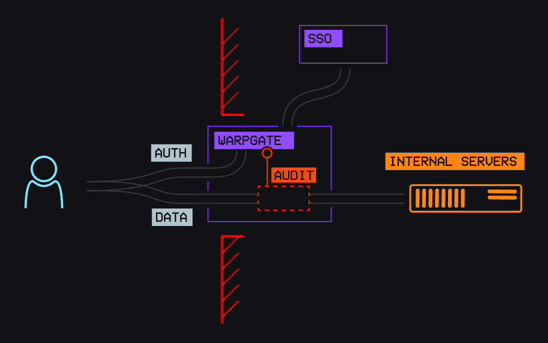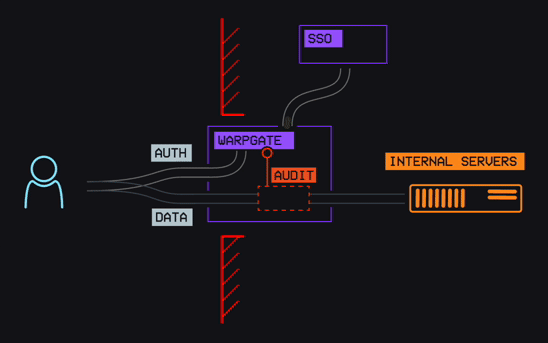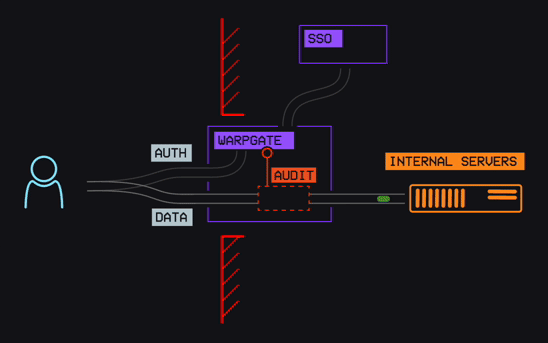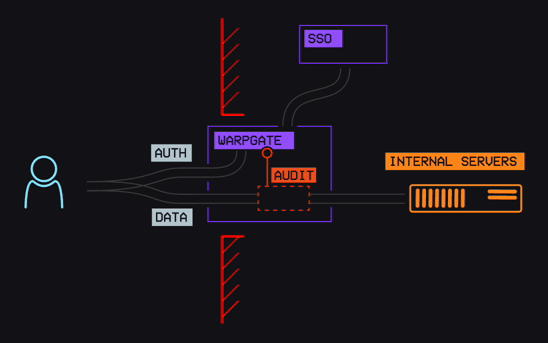
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software